
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2019-12189 — Proof-of-concept for a stored XSS vulnerability in Zoho ManageEngine ServiceDesk Plus 9.3, with a payload exploiting single quote and semicolon confusion in the query string. | Kitploit
Tools/GitHubGitHub/falconz/cve-2019-12189
Vulnerability AnalysisExploitationWeb Application ExploitationWeb SecurityPenetration Testing
GitHubfalconz/cve-2019-12189

CVE-2019-12189

Proof-of-concept for a stored XSS vulnerability in Zoho ManageEngine ServiceDesk Plus 9.3, with a payload exploiting single quote and semicolon confusion in the query string.

View Repository
277 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

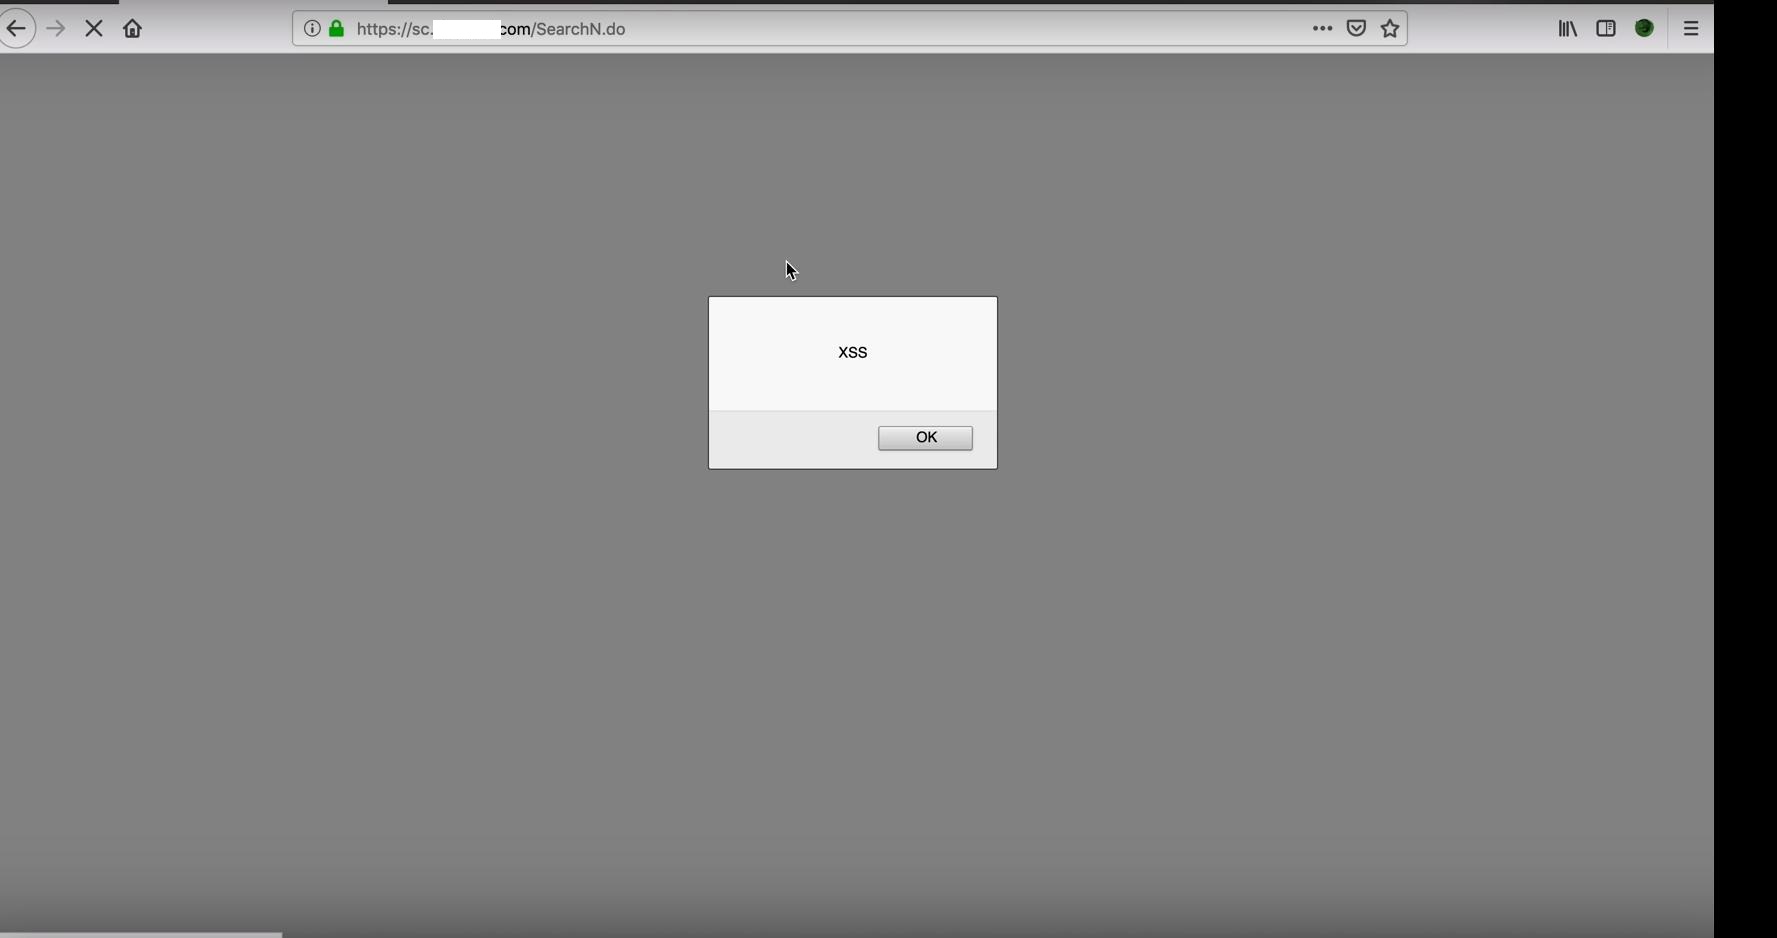
CVE-2019-12189 - Zoho ManageEngine ServiceDesk Plus 9.3 XSS vulnerability

Information Description:XSS was discovered in ManageEngine ServiceDesk Plus version Versions Affected: 9.3 Researcher: Dang The Tuyen

Proof-of-concept

The vulnerability stems from the confusion of both single quotes and semicolon in the query string of the URL.

payload: ';alert('XSS');' Attack vector: http:///SearchN.do
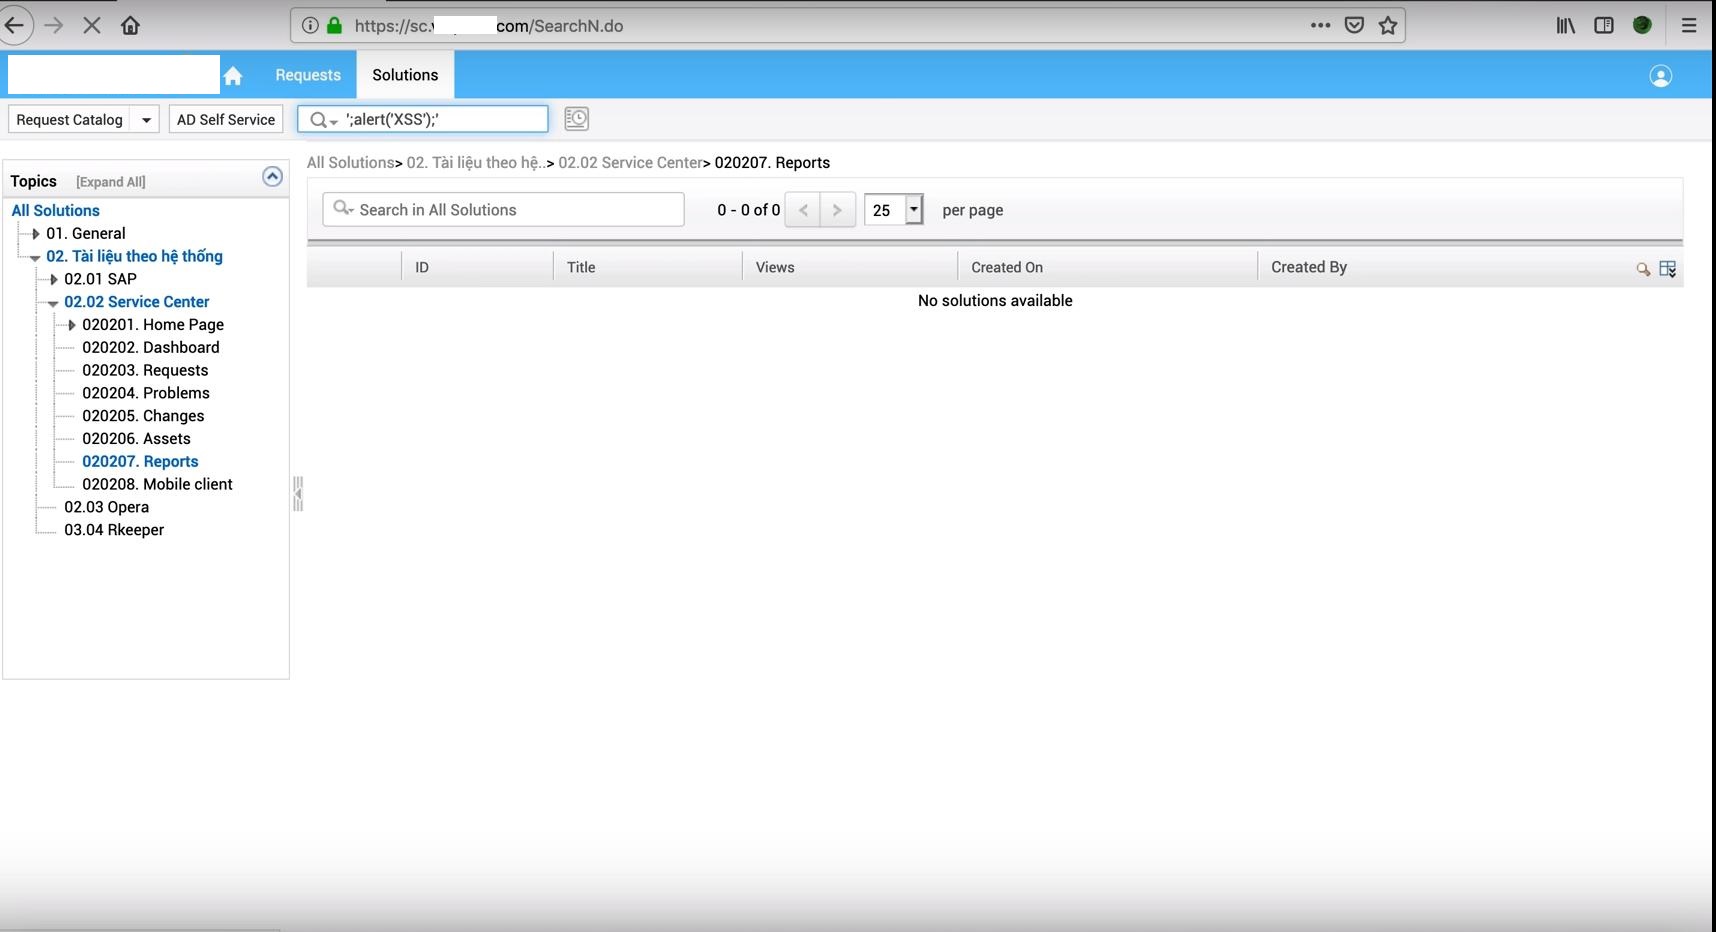
Screenshot

Alt text Alt text

Download Tool