
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-23998 — PoC for CVE-2024-23998 | Kitploit
Tools/GitHubGitHub/eqstlab/cve-2024-23998
Vulnerability AnalysisCode AnalysisExploitationWeb Application ExploitationPenetration Testing
GitHubeqstlab/cve-2024-23998

CVE-2024-23998

PoC for CVE-2024-23998

View Repository
262 years agoNot yet reviewed
Share

Another Redis Desktop Manager PoC

A Proof-Of-Concept for CVE-2024-23998 vulnerability.

1. Vunerability Overview:

  • Vulnerability Subject: Local Code Excution via XSS
  • Vulnerability Version: =< 1.6.6
  • Attack Type: Remote Code Execution
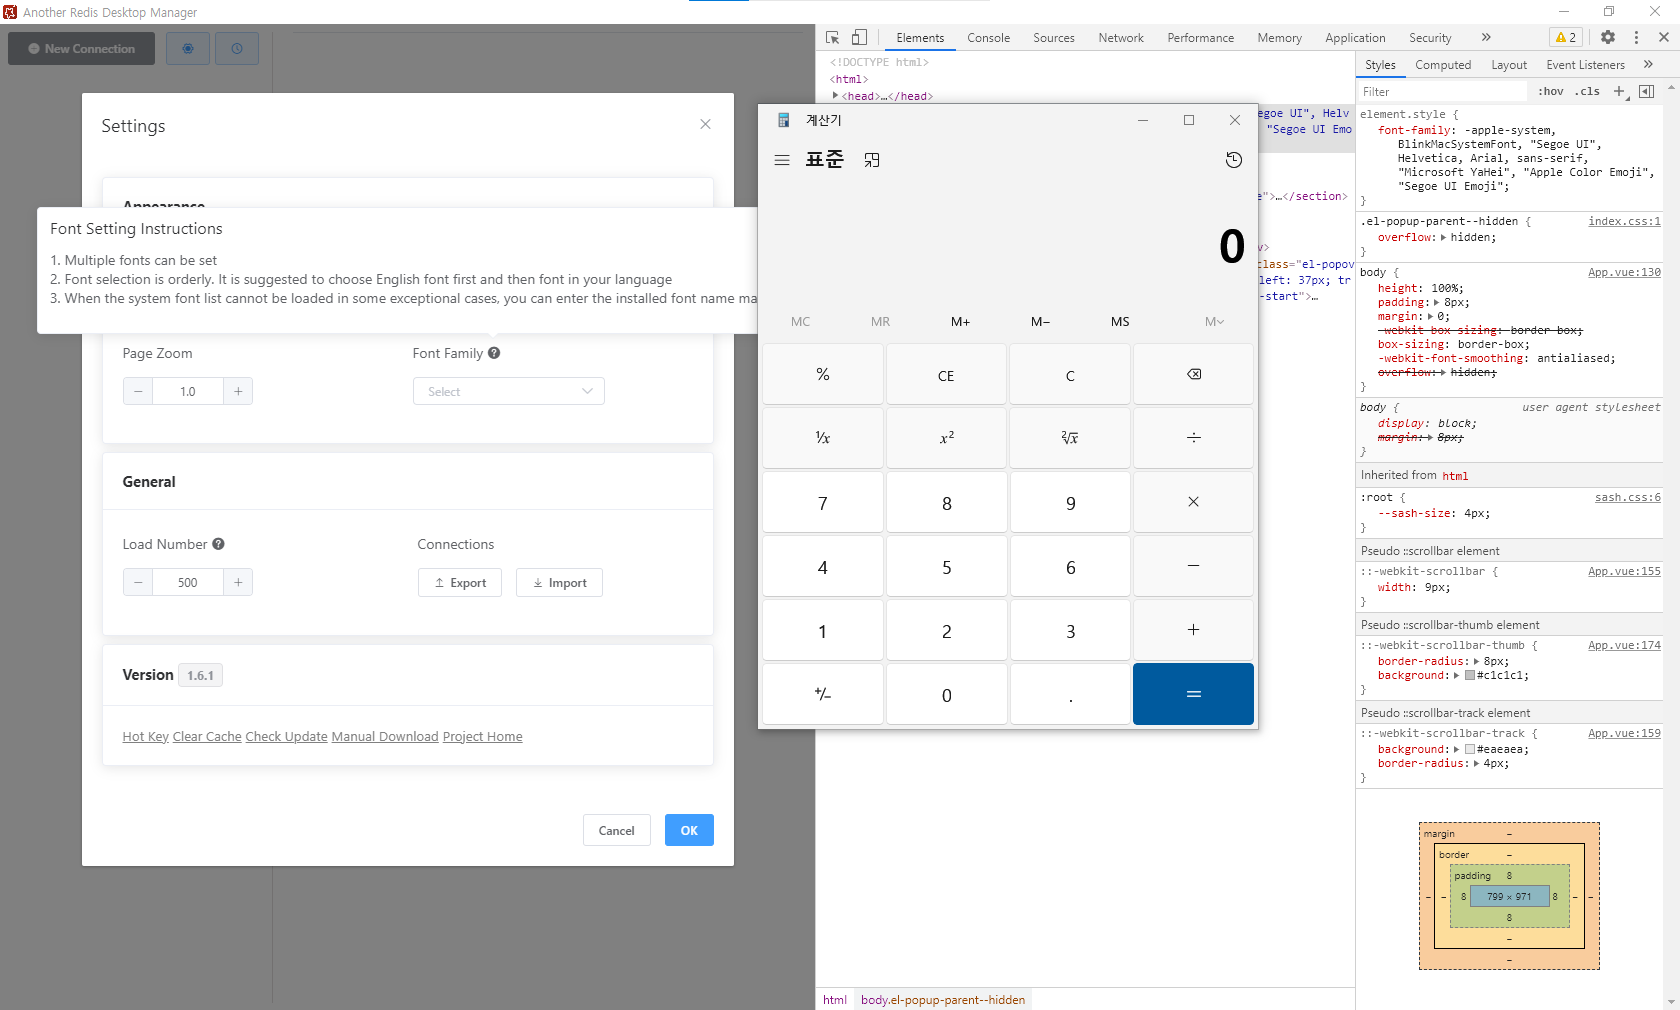
  • Attack Vectors: To exploit the vulnerability, we must patch font_faq html message for Setting function. When hovering the mouse over the font family help icon, malicious script in font_faq message execute and we can run OS command.
  • Reserved CVE Number: CVE-2024-23998

2. Vulnerability Cause:

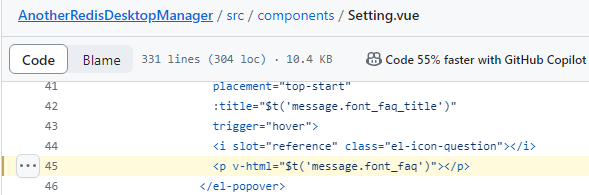
Step 1) In Setting.vue, there is v-html function, so malicious JS script can run through this fucntion.
alt text

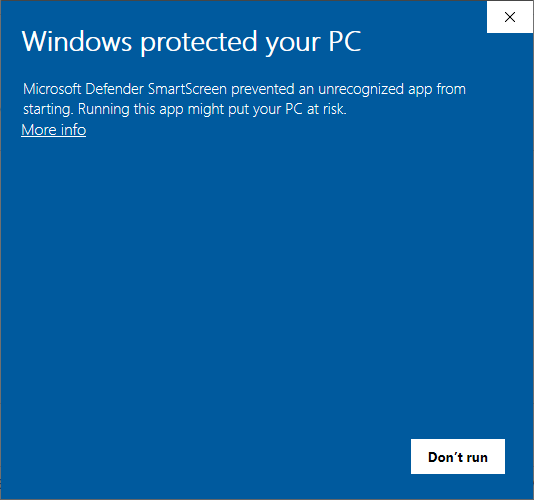
Step 2) When we install Another Redis Desktop Manager, Windows security blocks the installation. Because of that, if an attacker patches the installation file, the user won't know it has been patched.
alt text

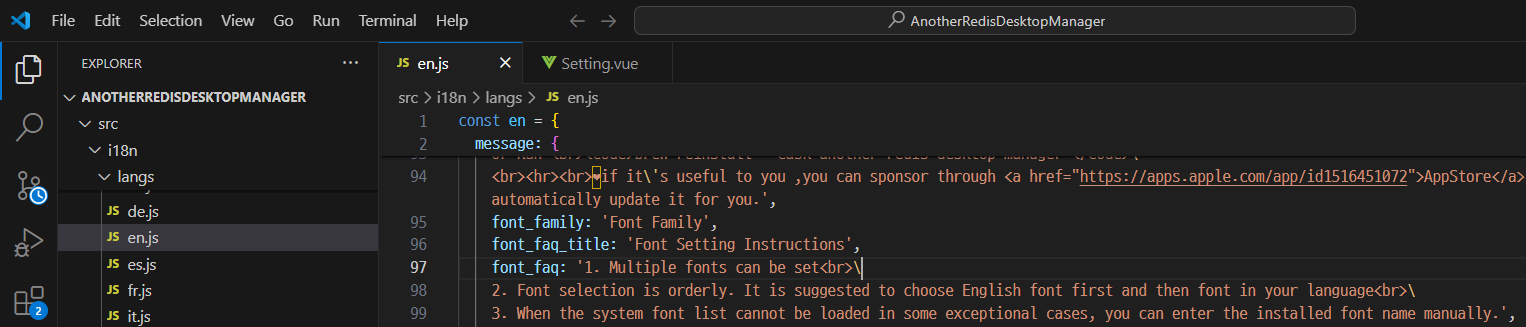
Step 3) We can find font faq message in en.js file
alt text

Step 4) Let's patch the message that execute calc.exe\

font_faq: '1. Multiple fonts can be set<br>\
    2. Font selection is orderly. It is suggested to choose English font first and then font in your language<br>\
    3. When the system font list cannot be loaded in some exceptional cases, you can enter the installed font name manually.\
    ',


Step 5) Build the program using npm.\

npm install --platform=win32
npm start
npm run electron


Step 6) When you hover mouse cursor on Font Famliy help icon, calculator is executed. alt text

AnotherRedisDesktopManager is a good target for attackers because it is used by many people, and it is easy to modify and redistribute files distributed as Electron applications. That's why many projects recommend not using v-html if possible. Additionally, because the nodeIntegration option is enabled, if it is maliciously modified and distributed, remote code execution is possible with the permissions of AnotherRedisDesktopManager.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.1k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    624
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    412
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH, RDP, Kubernetes, Database and RemoteApp endpoints through a web browser.

    333
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    328
  • 6

    Aliens_eye

    arxhr007/aliens_eye

    AI powered OSINT engine to discover and map 7,700+ social media identities across the web

    280

Explore all tools

Browse our collection of tools

View all tools →




