
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/brains93/cve-2024-24576-poc-python
Vulnerability AnalysisExploitationWeb Application ExploitationLearning & EducationPayload Development
GitHubbrains93/cve-2024-24576-poc-python

CVE-2024-24576-PoC-Python

Proof-of-concept demonstrating command injection via crafted arguments in Windows BAT file execution, exploiting CVE-2024-24576 to achieve arbitrary command execution.

View Repository
93172 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    916
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    707
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    430
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH, RDP, Kubernetes, Database and RemoteApp endpoints through a web browser.

    402
  • 5

    SafeLine

    chaitin/safeline

    Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic HTML/JS encryption.

    349
  • 6

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    341

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2024-24576-Poc-Python

A quick POC for the vulnerability disclosed here https://flatt.tech/research/posts/batbadbut-you-cant-securely-execute-commands-on-windows/

After you run the script it will ask for an arg to be passed to the BAT file. In the screenshot you can see that by adding " the underlying API that windows uses to call cmd can be escaped allowing for arbitrary command execution, in this case we opened calc.exe image
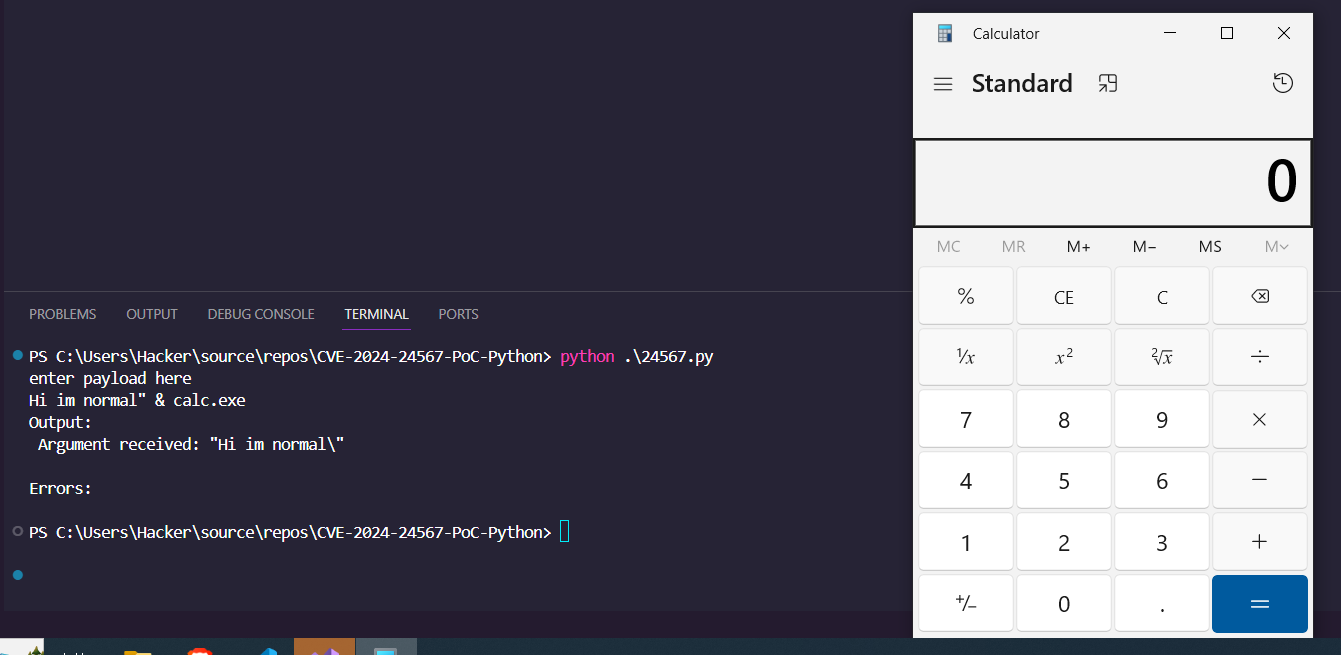
Obviously this code in itself is not malicious this is just to demonstrate that even sanitized input (unless you remove all "s) if it is calling a BAT file could be abused in this way possibly affecting public facing web applications

Video walkthrough https://youtu.be/xjL4pdf7pJ0

WIP There are other languages marked as having the same issues. I have tested Ruby but it seems unaffected I will be testing more to see where any issues lie

Golang code still to be tested. Ruby code seems unaffected by the same exploit path

Credit:

  • @Frostb1te for Rust POC https://github.com/frostb1ten/CVE-2024-24576-PoC
  • RyotaK Initial Disclosure
Download Tool



