
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Erlang-OTP-SSH-CVE-2025-32433 — CVE-2025-32433 – Erlang/OTP SSH vulnerability allowing pre-auth RCE | Kitploit

Tools/GitHubGitHub/bilalz5-github/erlang-otp-ssh-cve-2025-32433
Vulnerability AnalysisExploitationPenetration TestingLearning & EducationRemote Access Tool
GitHubbilalz5-github/erlang-otp-ssh-cve-2025-32433

Erlang-OTP-SSH-CVE-2025-32433

CVE-2025-32433 – Erlang/OTP SSH vulnerability allowing pre-auth RCE

View Repository
1231 year agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.0k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    627
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    416
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH, RDP, Kubernetes, Database and RemoteApp endpoints through a web browser.

    379
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    330
  • 6

    Aliens_eye

    arxhr007/aliens_eye

    AI powered OSINT engine to discover and map 7,700+ social media identities across the web

    288

Explore all tools

Browse our collection of tools

View all tools →
Share

✅ Result

The server responded to an SSH message ID 80 (0x50) — which is reserved for post-auth. This proves the server accepts invalid messages during the pre-auth phase, indicating vulnerable behavior as defined in CVE-2025-32433.
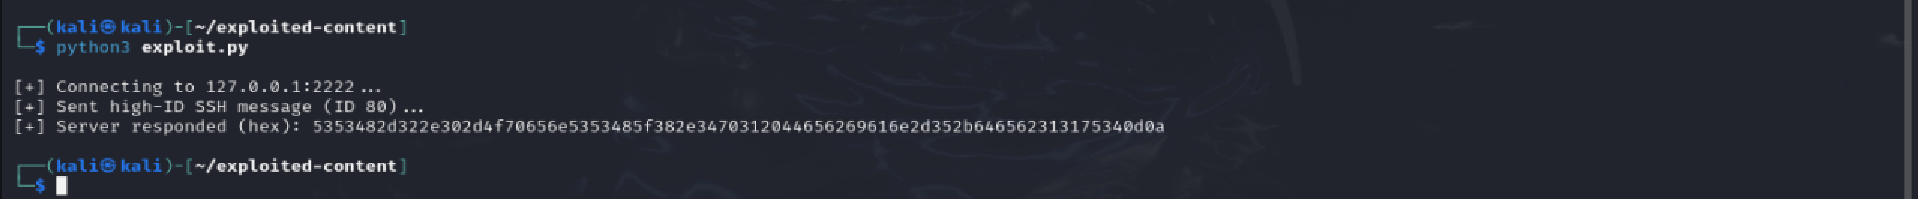
Python code is executed

📖 Research Summary

I built this lab after studying Erlang/OTP and the CVE from various trusted sources.

Erlang/OTP is a powerful environment originally developed by Ericsson to build scalable and fault-tolerant distributed systems. It includes its own SSH server implementation. The SSH module inside Erlang/OTP is vulnerable to unauthenticated remote code execution (RCE) due to incorrect handling of SSH message types ≥ 80 during the pre-auth phase.

Instead of rejecting these invalid messages, the server processes them — which allows an attacker to craft malicious messages and potentially gain unauthorized code execution access.


🔍 Key Things I Learned

  • Erlang/OTP SSH allows secure shell/file access within Erlang systems
  • Message ID 80+ is reserved for post-authentication but can be abused pre-auth
  • Detection: Suricata or NIDS can spot “SSH_MSG_CHANNEL_REQUEST” with “exec” commands
  • Affected Versions:
    • OTP-27.3.2 and below
    • OTP-26.2.5.10 and below
    • OTP-25.3.2.19 and below
  • Patched Versions:
    • OTP-27.3.3
    • OTP-26.2.5.11
    • OTP-25.3.2.20

📚 Credits & Reference

  • GitHub Security Advisory – GHSA-37cp-fgq5-7wc2
  • Research PoC and writeups by Matthew Keeley
  • Community detection insights via Suricata, Wireshark, and FortiGate
  • Official Erlang/OTP documentation and CVE pages

💬 Final Note

Not all content here is 100% original — I built the lab & PoC myself but studied from multiple sources to understand Erlang, OTP, SSH, and CVE-2025-32433 clearly. This README reflects my own summary and learning. 🤝


Download Tool



