
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-37742 — This repository contains a PoC for exploiting CVE-2024-37742, a vulnerability in Safe Exam Browser (SEB) ≤ 3.5.0 on Windows. The vulnerability enables unauthorized clipboard data sharing between SEB's kiosk mode and the underlying system, compromising the integrity of exams. | Kitploit
Tools/GitHubGitHub/aar0nd0m1n1c/cve-2024-37742
Vulnerability AnalysisExploitationPenetration TestingLearning & Education
GitHubaar0nd0m1n1c/cve-2024-37742

CVE-2024-37742

This repository contains a PoC for exploiting CVE-2024-37742, a vulnerability in Safe Exam Browser (SEB) ≤ 3.5.0 on Windows. The vulnerability enables unauthorized clipboard data sharing between SEB's kiosk mode and the underlying system, compromising the integrity of exams.

View Repository
8182 years agoNot yet reviewed
Share

CVE-2024-37742: Clipboard Exploit in SEB ≤ 3.5.0 (Windows)

This repository contains a proof-of-concept (PoC) for exploiting CVE-2024-37742, a vulnerability in Safe Exam Browser (SEB) ≤ 3.5.0 on Windows. The vulnerability allows an attacker to share clipboard data between the SEB kiosk mode and the underlying system, compromising exam integrity. By exploiting this flaw, an attacker can bypass exam controls and gain an unfair advantage during exams.

Disclaimer

This repository is for educational purposes only. The information provided here is intended to help developers understand the vulnerability and protect their systems. Do not use this exploit maliciously or without permission. Use of this PoC is at your own risk. The author is not responsible for any damages or legal issues that may arise from the use of this information.

Affected Versions

SEB ≤ 3.5.0 (Windows)

How It Works

  1. Incorrect access control allows clipboard data sharing between SEB kiosk and the underlying system.
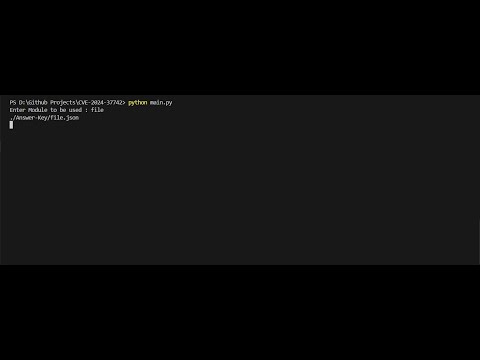
  2. The exploit utilizes the pyperclip Python module to copy answers from a JSON file in the 'Answer-Key' directory, containing questions and answers.
  3. In SEB kiosk mode:
    The user copies the question.
    The wmi Python module monitors system charge and discharge states to signal a Python script.
    The script accesses clipboard data, searches the JSON file for the answer, and pastes it into the clipboard.
  4. Finally, the user pastes the answer from the clipboard into the answer field.

Watch the video

Impact

This vulnerability allows authorized users to compromise the integrity of exams conducted using Safe Exam Browser (SEB). By exploiting incorrect access control, users can share clipboard data between the SEB kiosk mode and the underlying system. This enables them to copy exam questions, retrieve answers from an external source, and paste them back into the exam, undermining the security and fairness of the examination process.
Mitigation/Resolution

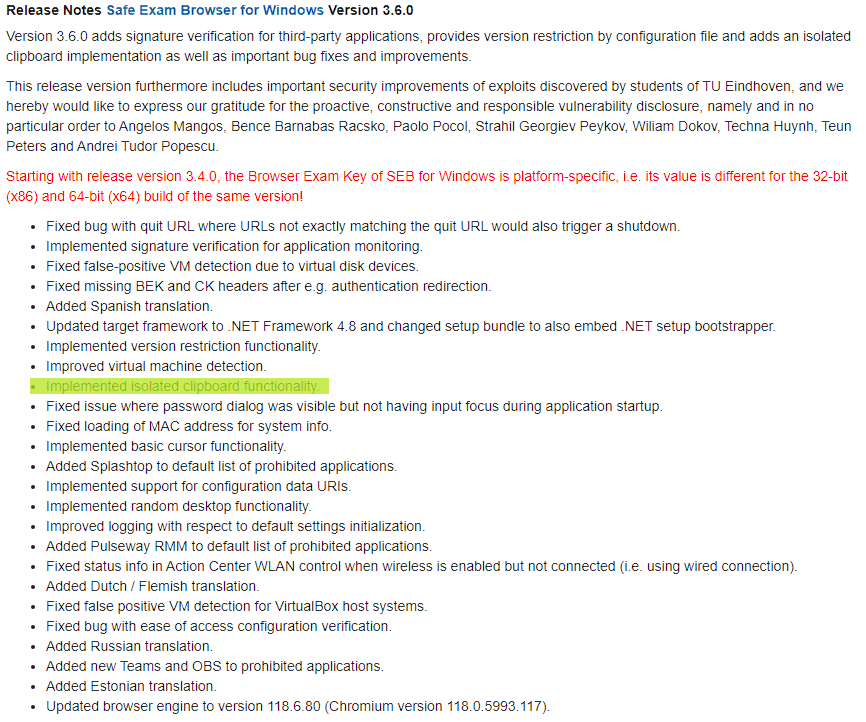
1. Upgrade to Safe Exam Browser (SEB) ≥ 3.6.0 for Windows, in the new version SEB has implemented an isolated clipboard

3 6 0 notes \

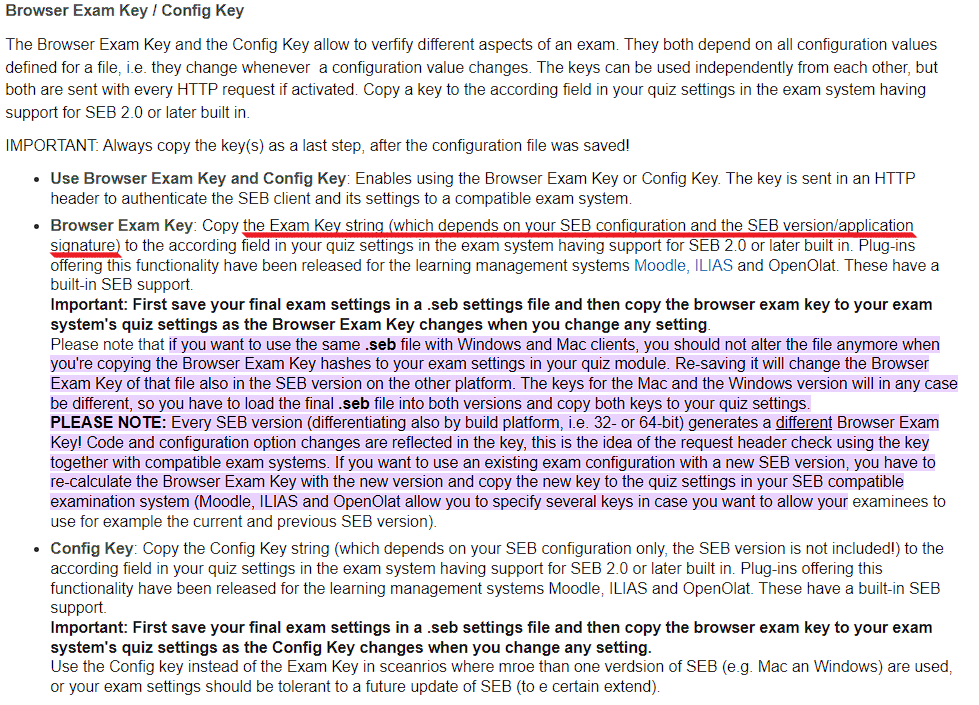
2. Configure Browser and Exam Key to use SEB 3.6.0

Browser Exam Key

References

[https://safeexambrowser.org/windows/win_usermanual_en.html]
[https://safeexambrowser.org/windows/win_release_notes_en.html]

License

This code is available under the MIT License. See the LICENSE file for details.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.0k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    647
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    421
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH, RDP, Kubernetes, Database and RemoteApp endpoints through a web browser.

    389
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    333
  • 6

    SafeLine

    chaitin/safeline

    Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic HTML/JS encryption.

    331

Explore all tools

Browse our collection of tools

View all tools →