
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2023-23752 — Python exploit for Joomla information disclosure CVE-2023-23752, abusing unauthenticated webservice endpoints to extract configuration data and database credentials. | Kitploit
Tools/GitHubGitHub/0xnahim/cve-2023-23752
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingLearning & EducationLabs & Practice
GitHub0xnahim/cve-2023-23752

CVE-2023-23752

Python exploit for Joomla information disclosure CVE-2023-23752, abusing unauthenticated webservice endpoints to extract configuration data and database credentials.

View Repository
5163 years agoNot yet reviewed
Share

Joomla! information disclosure - CVE-2023-23752 exploit

Exploit for CVE-2023-23752 (4.0.0 <= Joomla <= 4.2.7).

Usage

Before using the project we need to install the required packages (I recommend creating a virtual environment first)

pip install -r requierements.txt
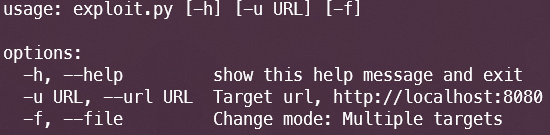
example of exploitation

Proof of Concept

To create a vulnerable environment we need to have docker installed

  1. Build image:
docker-compose up --build
  1. Once the image is created and running, go to http://127.0.0.1:4242/installation/index.php

  2. Fill in the data:

Database type: Mysqli
Host: mysql
Db User: root
Db Password: holamundo

References

This is an exploit for the vulnerability CVE-2023-23752 found by Zewei Zhang of NSFOCUS TIANJI Lab.

Resources about the vulnerability:

  • Discoverer advisory
  • Joomla Advisory
  • AttackerKB topic
  • Vulnerability analysis
  • Nuclei template
  • Acceis POC

Warning

The content of this repository does not promote or encourage any illegal activity. All material provided here is solely for research and educational purposes.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    509
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    469
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    343
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    310
  • 5

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    306
  • 6

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    301

Explore all tools

Browse our collection of tools

View all tools →




