Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-46817 — CVE-2026-46817 | Kitploit
Tools/GitHubGitHub/0xblackash/cve-2026-46817
ReconnaissanceVulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration Testing
GitHub0xblackash/cve-2026-46817

CVE-2026-46817

CVE-2026-46817

View Repository
11274 months agoNot yet reviewed
Share

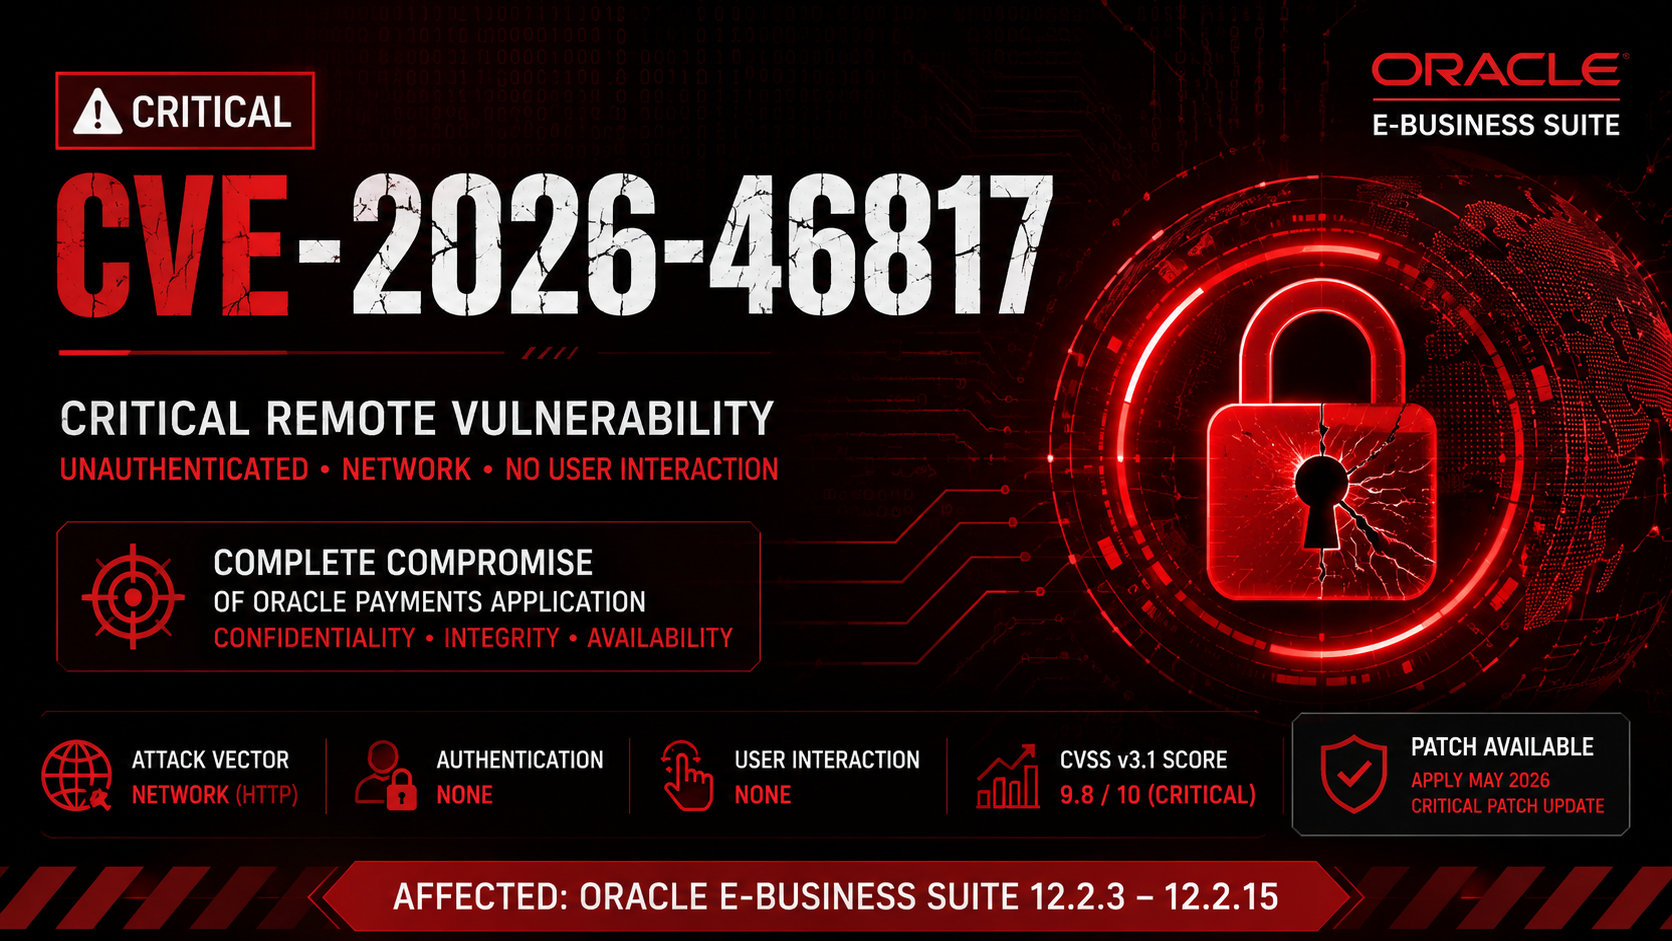
🚨 CVE-2026-46817 - Critical Remote Code Execution

ChatGPT Image Jun 30, 2026, 12_56_18 AM

Oracle E-Business Suite – Oracle Payments (File Transmission)

CVE CVSS Vendor Product Status

Critical unauthenticated remote vulnerability affecting Oracle Payments (File Transmission) that may allow complete compromise of the application over HTTP.


📌 Overview

CVE-2026-46817 is a critical vulnerability in the Oracle Payments component of Oracle E-Business Suite. The flaw affects the File Transmission functionality and can be exploited remotely over HTTP without authentication.

A successful attack may allow an attacker to fully compromise the vulnerable Oracle Payments application, resulting in complete loss of:

  • 🔓 Confidentiality
  • ✏️ Integrity
  • 🚫 Availability

📊 Severity

MetricValue
CVE IDCVE-2026-46817
CVSS v3.19.8 (Critical)
Attack VectorNetwork
Attack ComplexityLow
Privileges RequiredNone
User InteractionNone
ScopeUnchanged

CVSS Vector

CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H

🎯 Affected Products

ProductAffected Versions
Oracle E-Business Suite12.2.3 – 12.2.15
ComponentOracle Payments – File Transmission

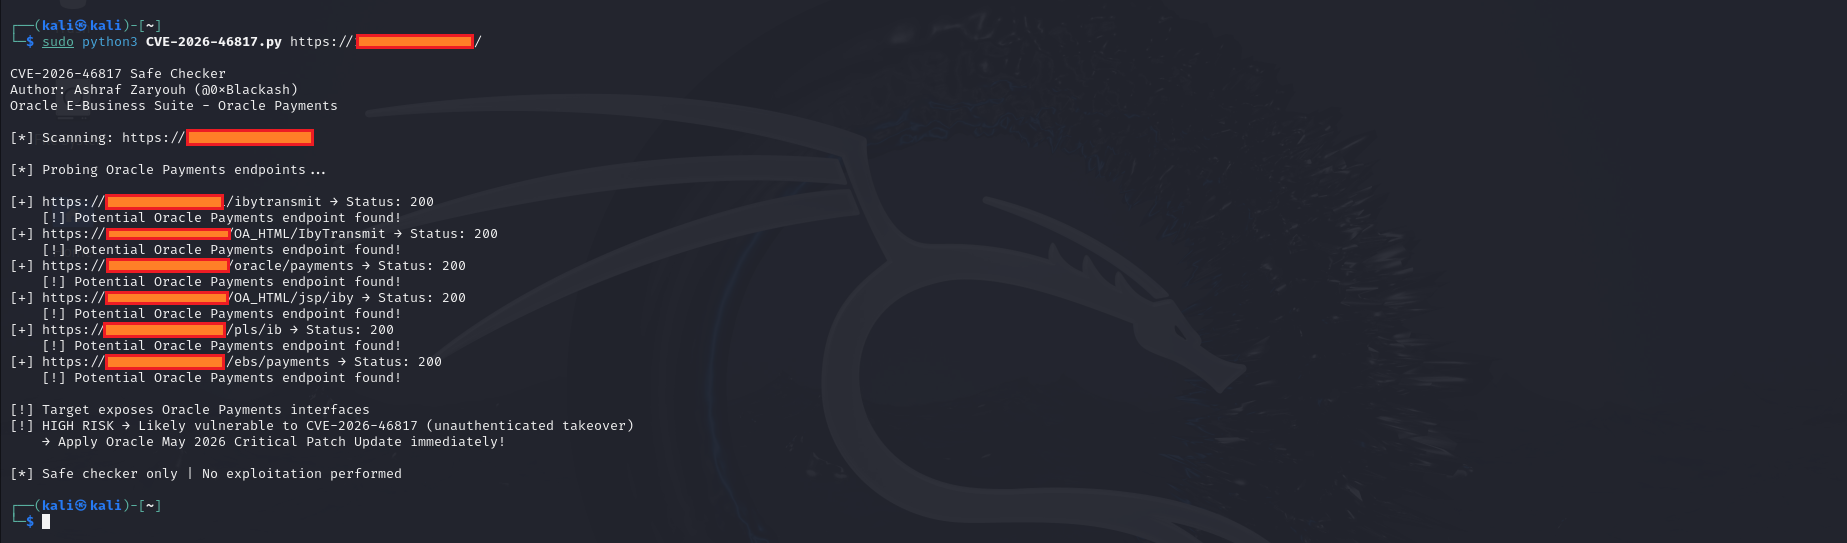
📸 Demo

CVE-2026-46817

⚠️ Potential Impact

Successful exploitation could allow an attacker to:

  • Execute unauthorized operations
  • Access sensitive payment-related information
  • Modify application data
  • Disrupt payment services
  • Completely compromise the Oracle Payments application

🛡️ Mitigation

Oracle recommends applying the latest Critical Patch Update (CPU) immediately.

Additional defensive measures include:

  • Restrict external HTTP access
  • Limit access using VPN or trusted networks
  • Monitor web server and application logs
  • Deploy a Web Application Firewall (WAF)
  • Enable continuous security monitoring
  • Follow the principle of least privilege

🔍 Detection

Security teams should monitor for:

  • Unexpected HTTP requests targeting Oracle Payments
  • Suspicious file transmission activity
  • Authentication bypass attempts
  • Unusual application errors
  • Unexpected administrative actions

📖 References

  • Oracle Critical Patch Update (May 2026)
  • National Vulnerability Database (NVD)

⚡ Key Takeaways

ItemStatus
Severity🔴 Critical
CVSS9.8
Remote✅ Yes
Authentication Required❌ No
User Interaction❌ No
Patch Available✅ Yes

⭐ Stay Updated • Patch Early • Monitor Continuously

Security is a process, not a product.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    916
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    707
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    430
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH, RDP, Kubernetes, Database and RemoteApp endpoints through a web browser.

    402
  • 5

    SafeLine

    chaitin/safeline

    Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic HTML/JS encryption.

    349
  • 6

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    341

Explore all tools

Browse our collection of tools

View all tools →