#1
Tools for intercepting, analyzing, and modifying web traffic for security testing.
Kitploit recommended
 simplerhacking/evilginx3-phishlets
This repository provides penetration testers and red teams with an extensive collection of dynamic phishing templates designed specifically for use…
 diegovargasj/cve-2025-32407
Proof-of-concept exploit for CVE-2025-32407: TLS certificate validation bypass in Samsung Internet for Galaxy Watch, enabling Man-in-the-Middle…
 caido-community/burp2caido
A tool to migrate Burpsuite HTTP history to Caido
 xepor/xepor
Flask-like routing framework for mitmproxy to intercept, modify, and spoof HTTP requests/responses. Enables rapid development of MITM scripts for…
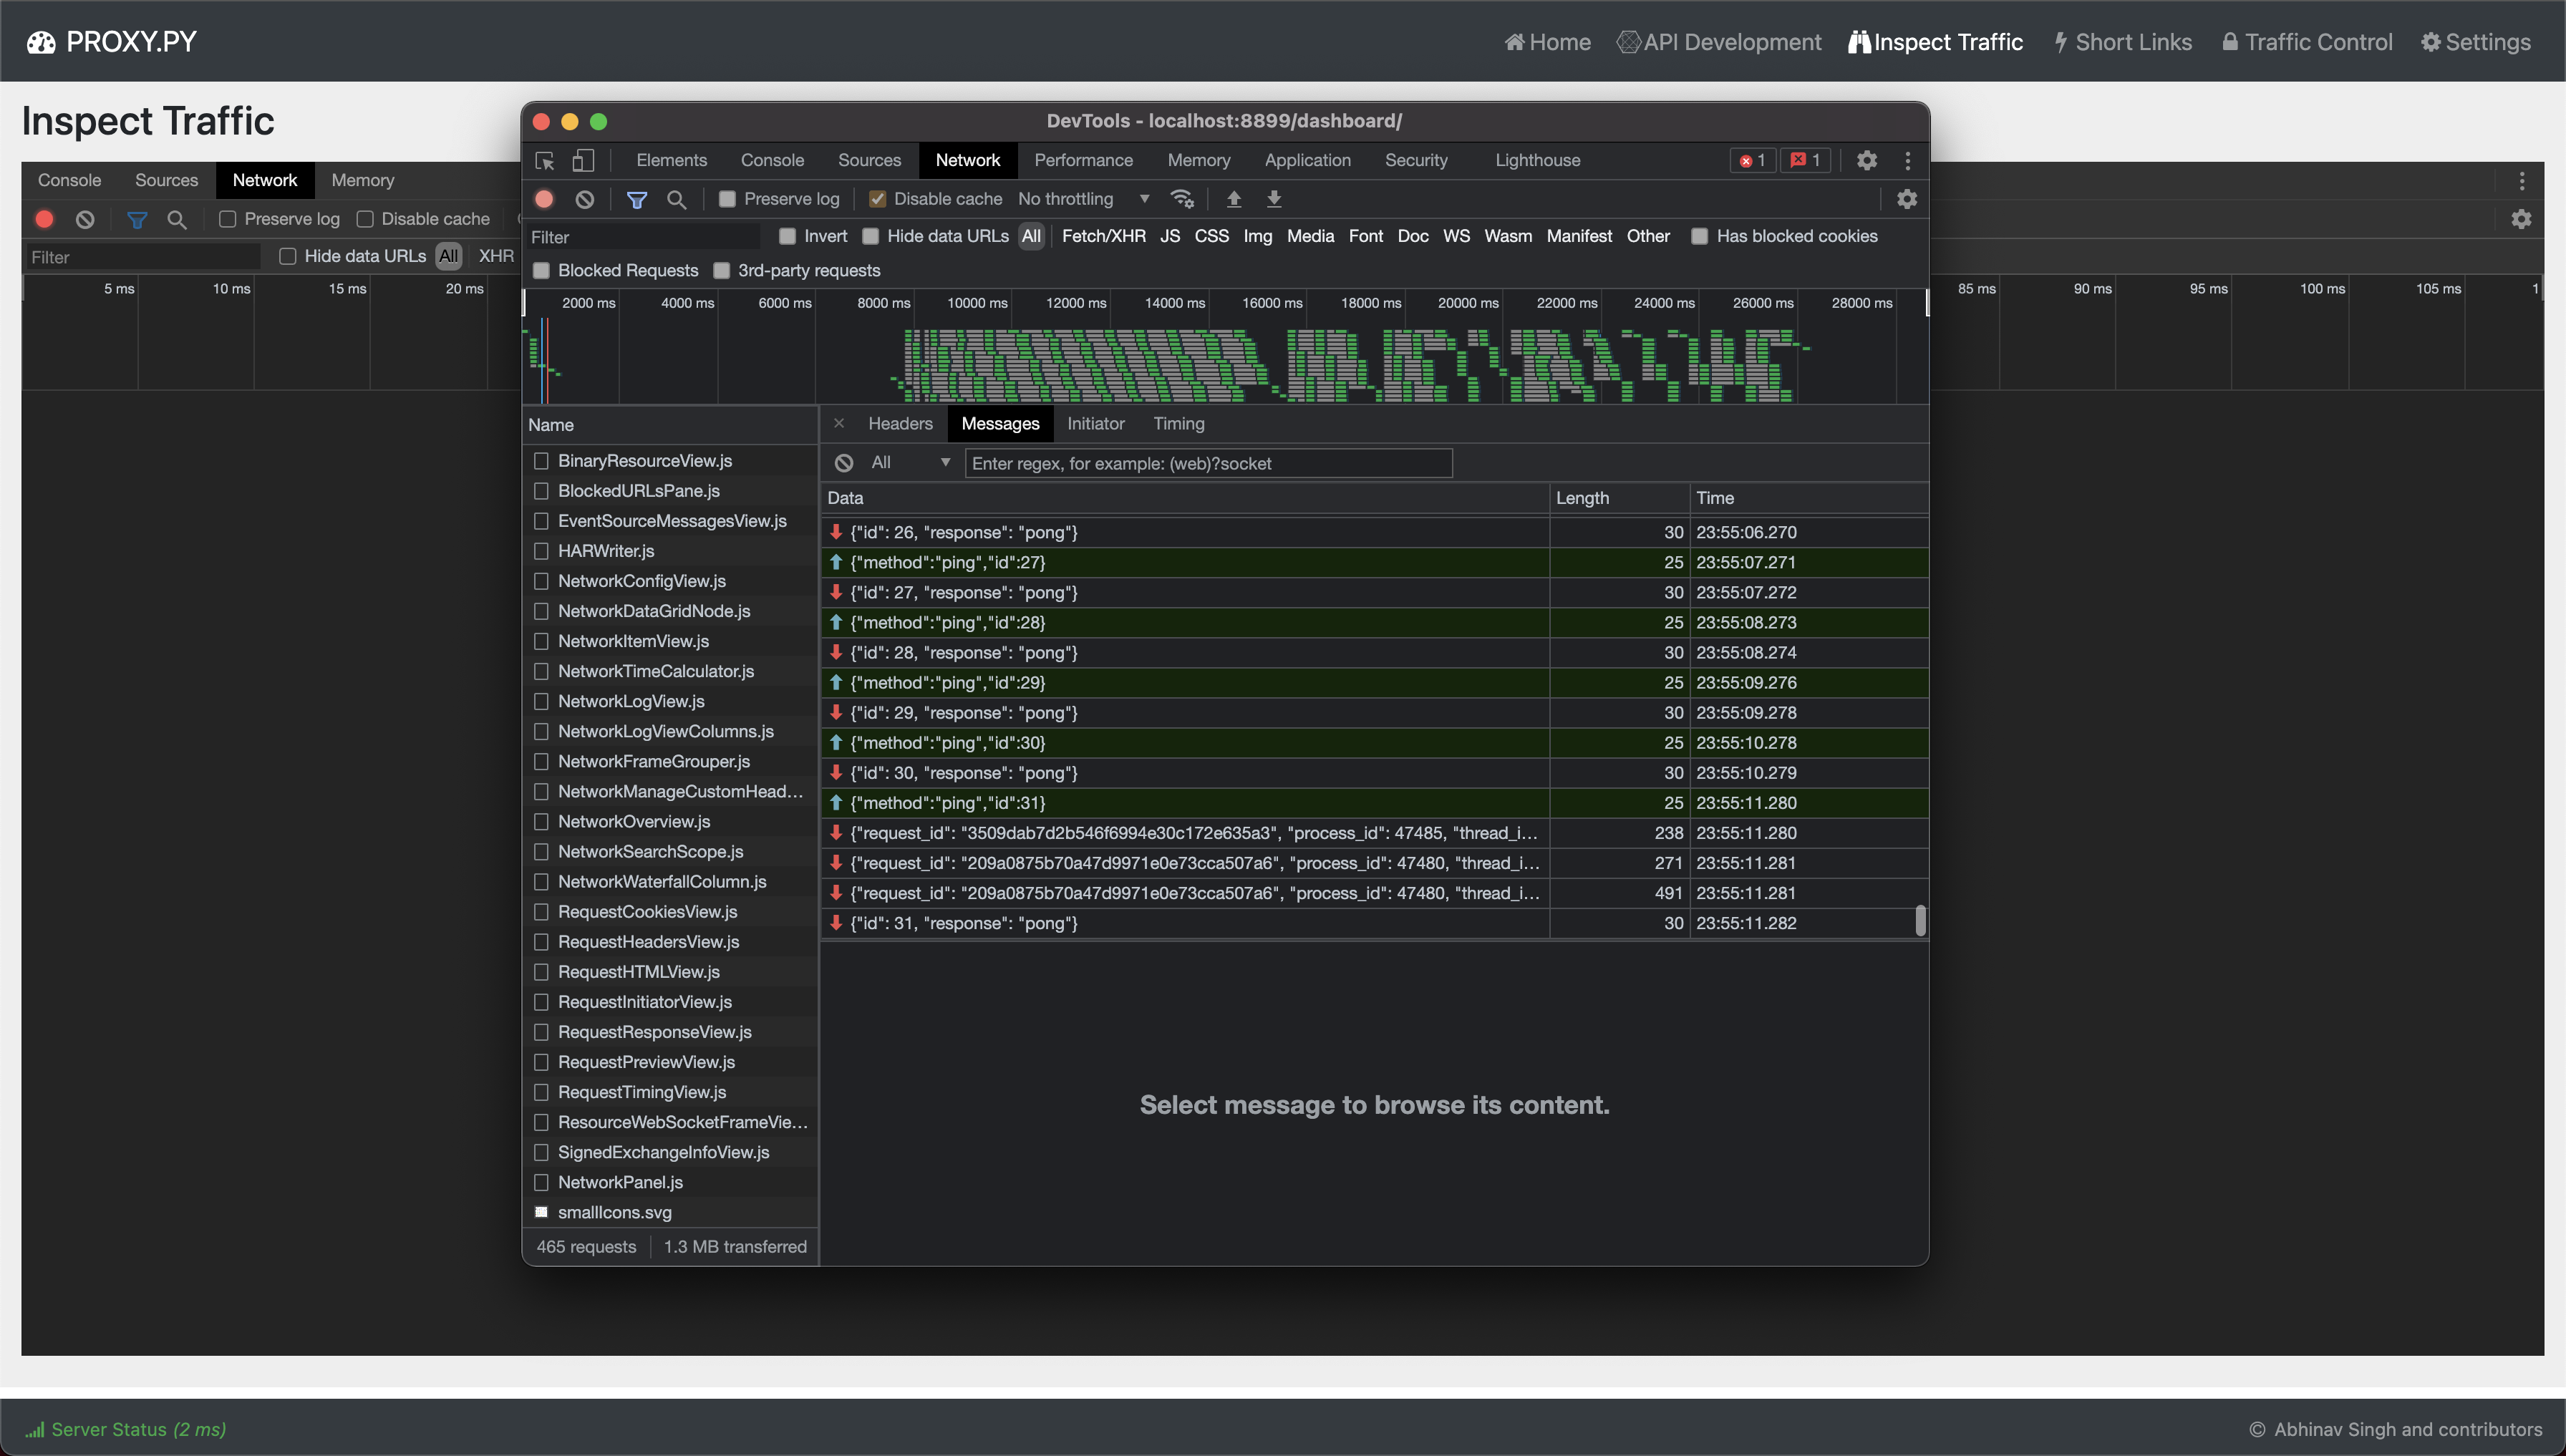 abhinavsingh/proxy.py
💫 Ngrok FRP Alternative • ⚡ Fast • 🪶 Lightweight • 0️⃣ Dependency • 🔌 Pluggable • 😈 TLS interception • 🔒 DNS-over-HTTPS • 🔥 Poor Man's VPN • ⏪…
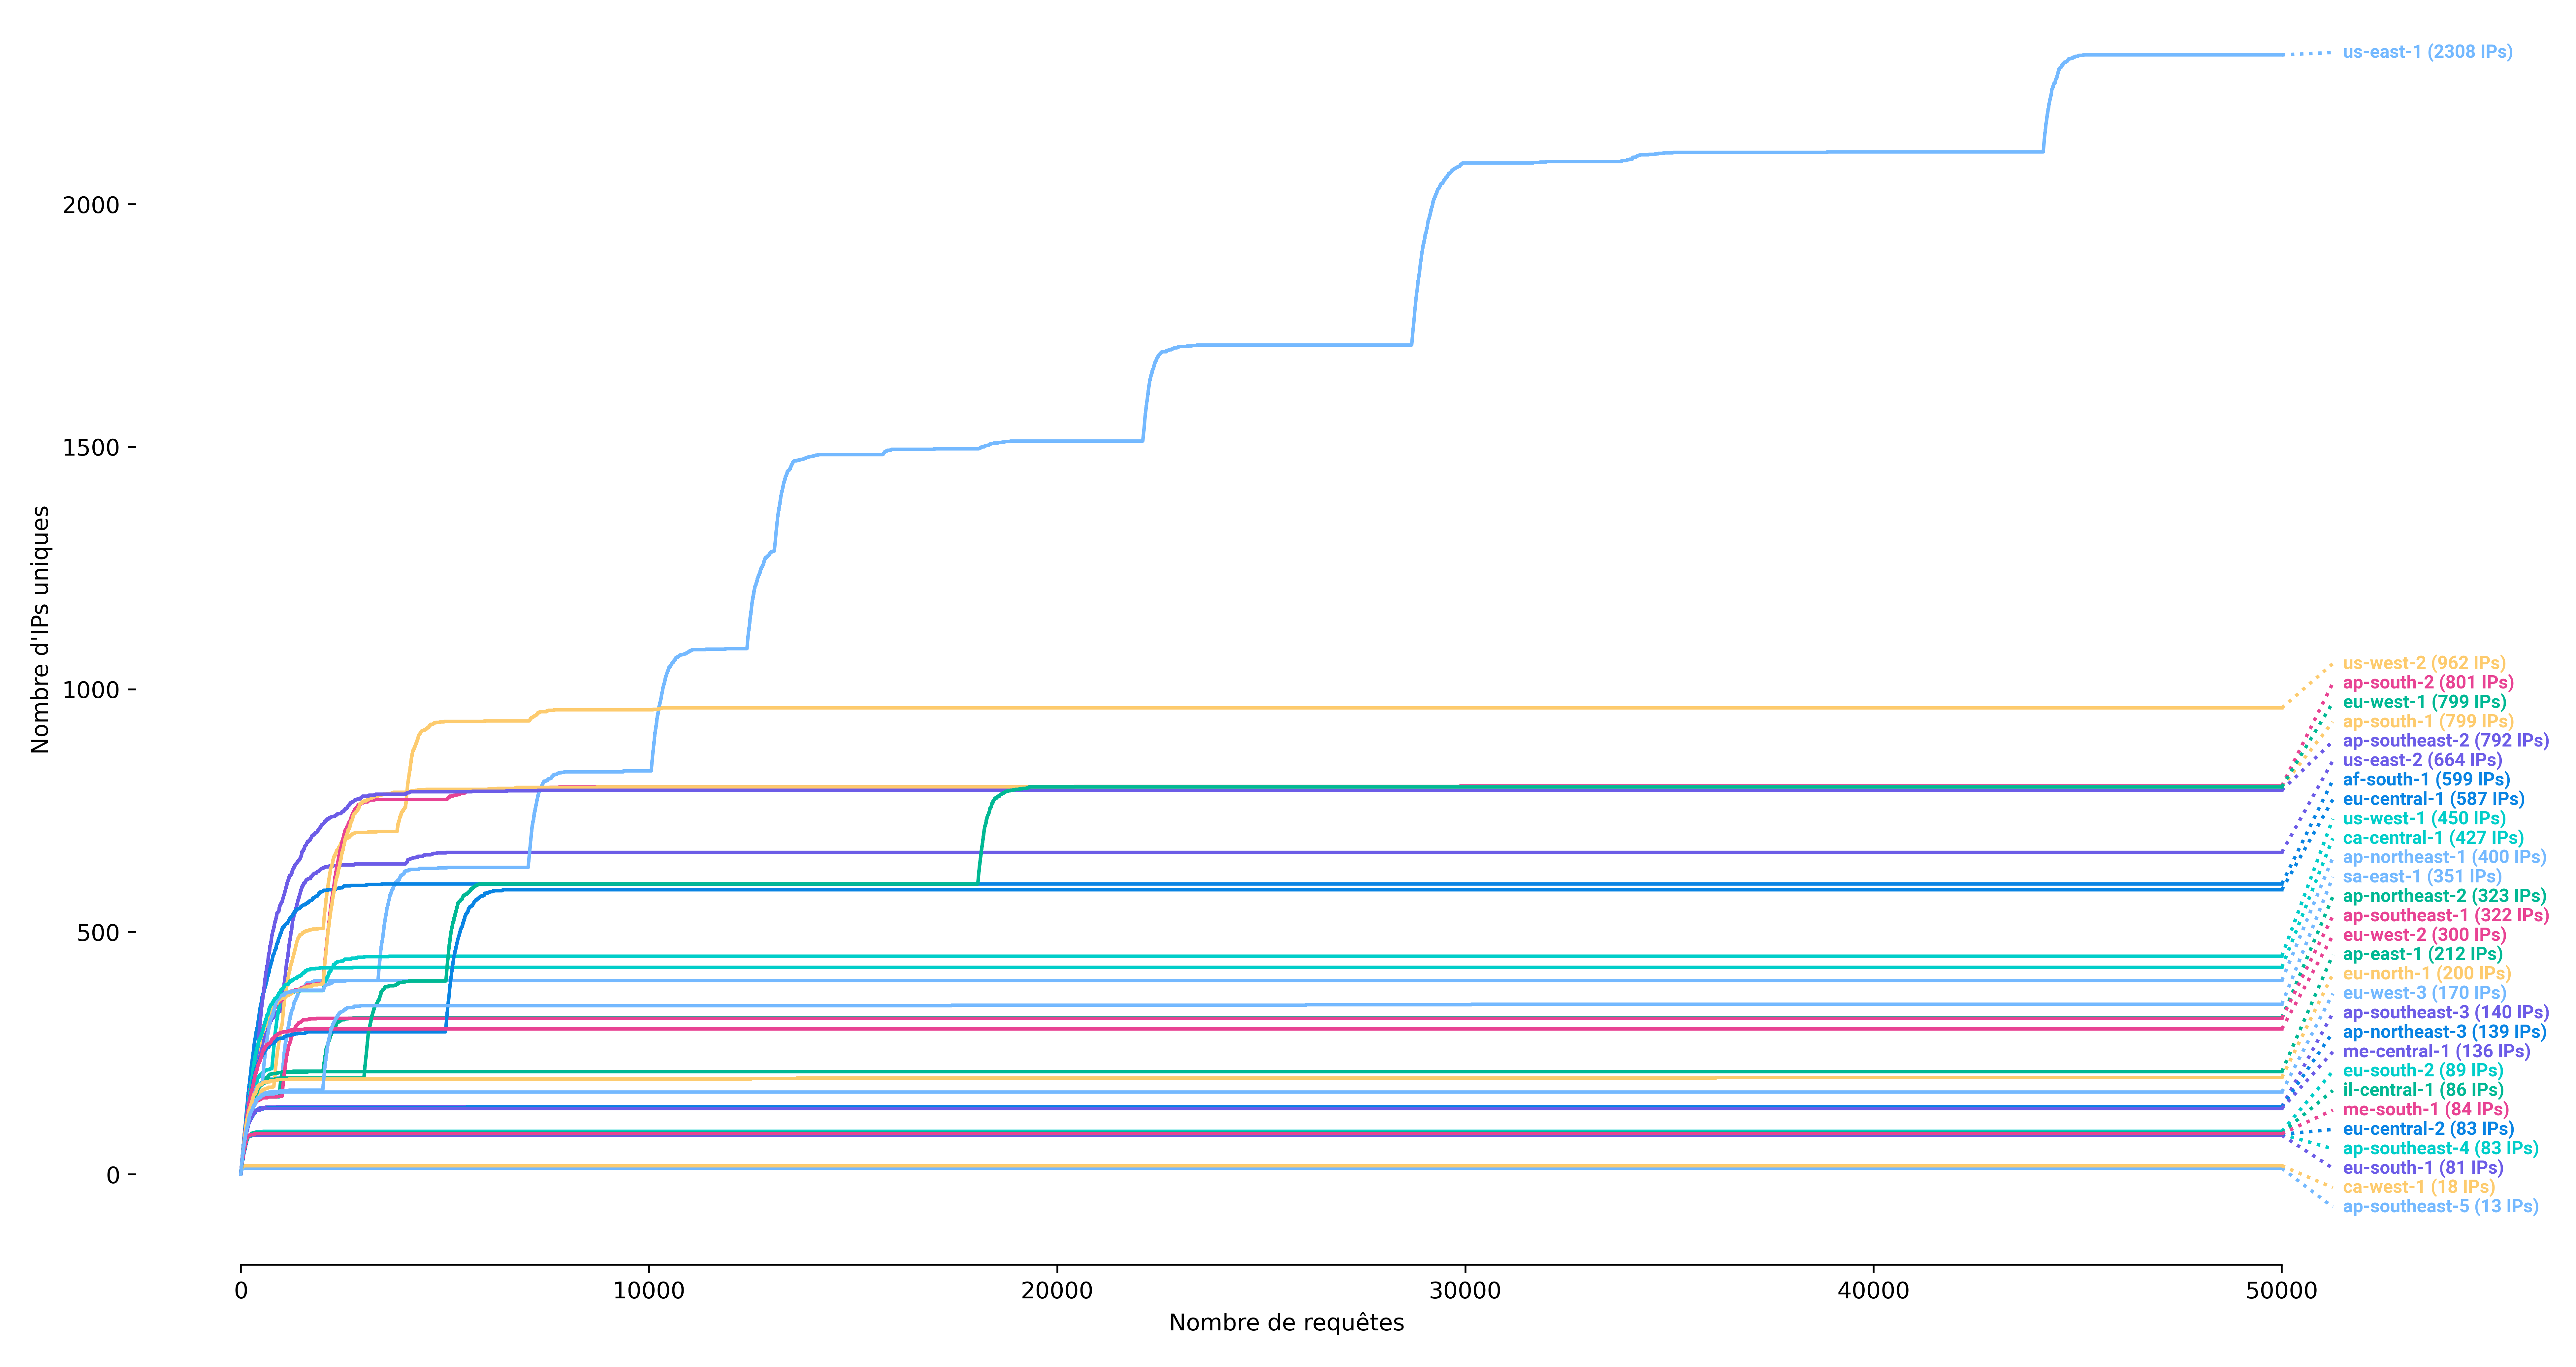 synacktiv/ipspinner
IPSpinner works as a local proxy that redirects requests through external services.
 nccgroup/blackboxprotobuf
Blackbox Protobuf is a set of tools for working with encoded Protocol Buffers (protobuf) without the matching protobuf definition.
 infobyte/faraday_burp
Burp Extension for collaboration in Faraday
 google/martian
Martian is a library for building custom HTTP/S proxies
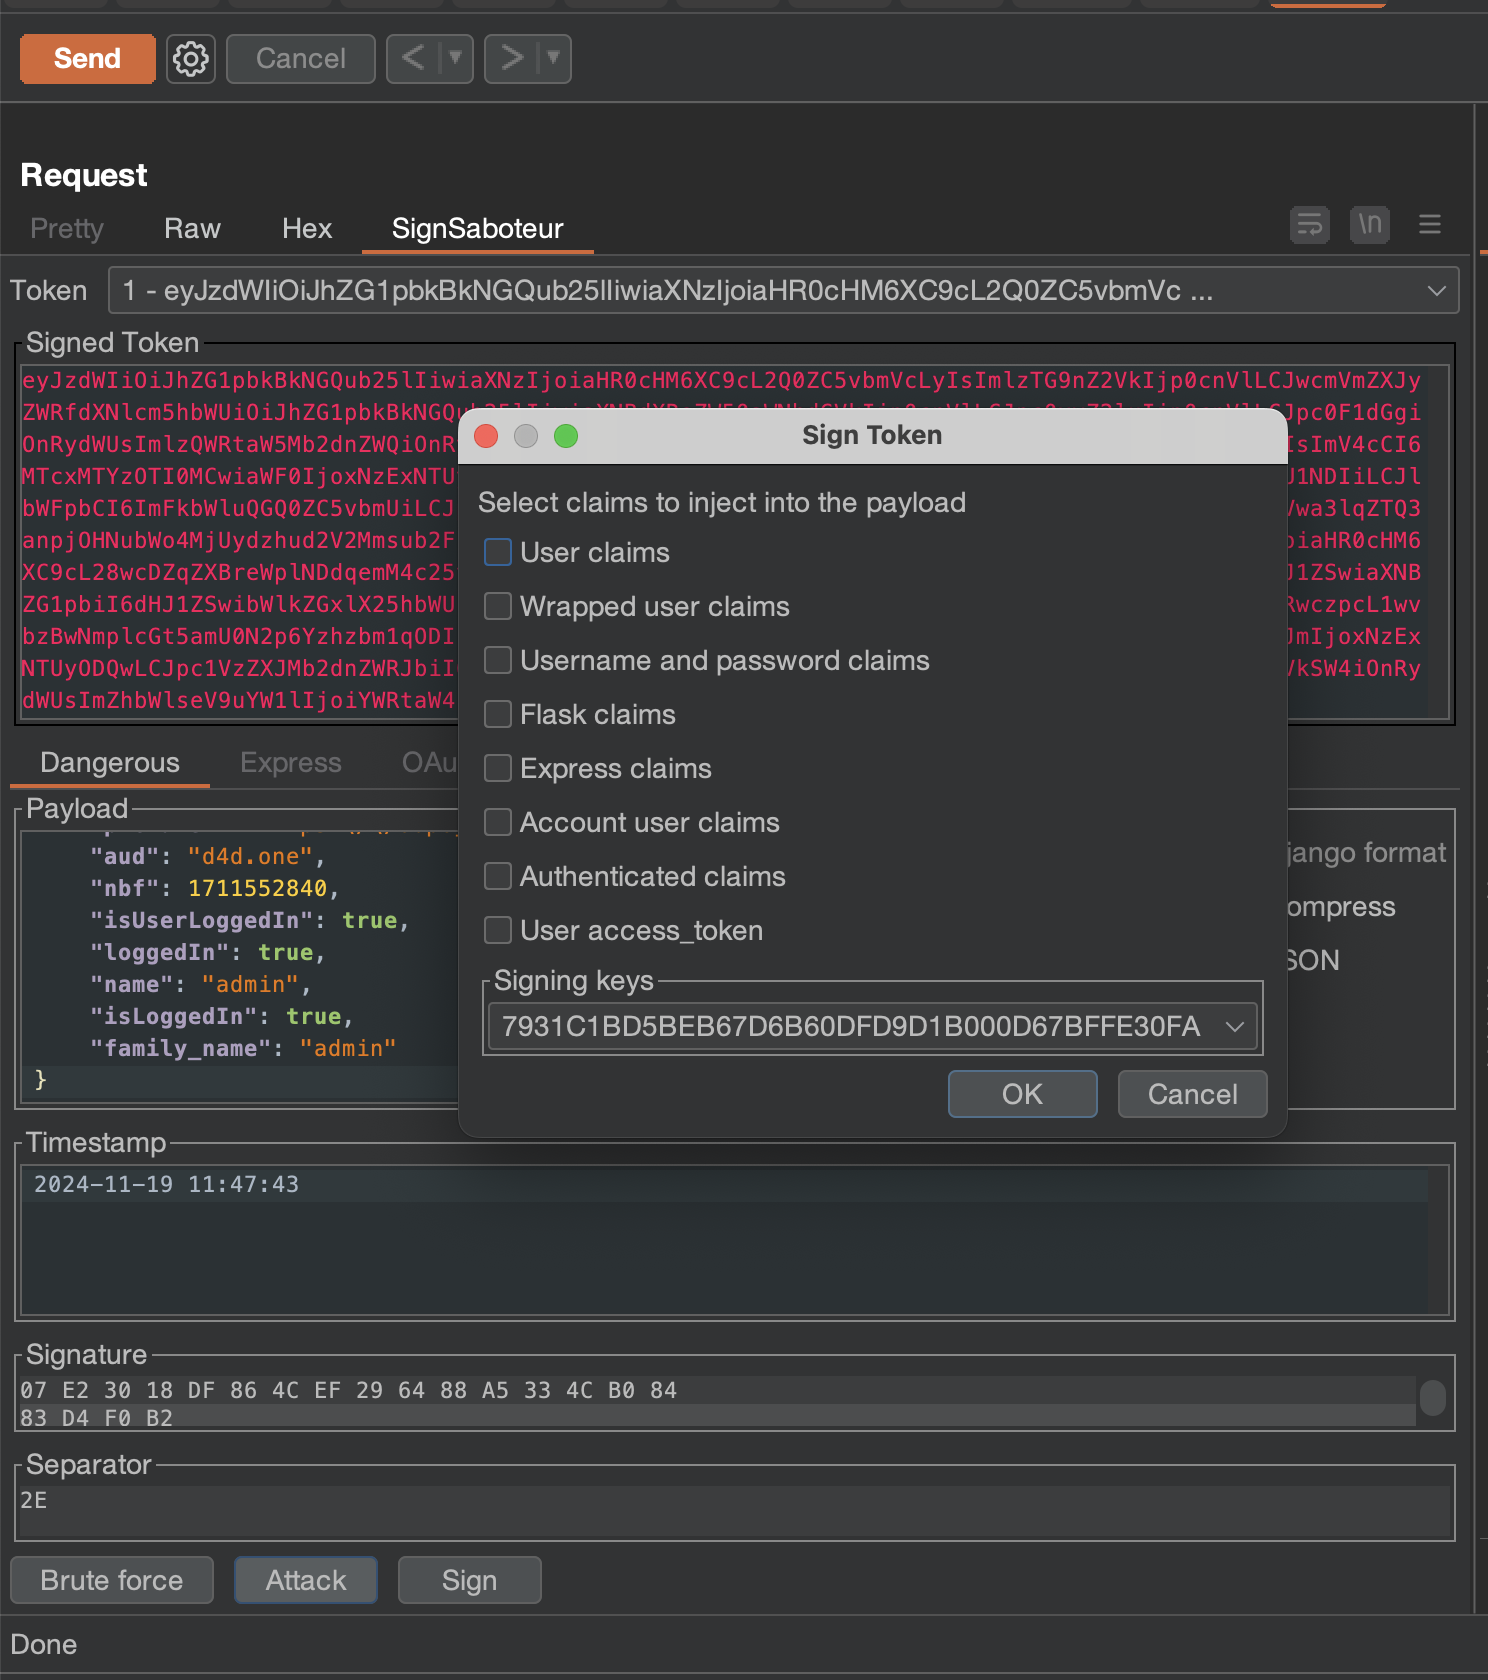 d0ge/sign-saboteur
SignSaboteur is a Burp Suite extension for editing, signing, verifying various signed web tokens
 muraenateam/muraena
Automates phishing and post-phishing activities with an almost-transparent reverse proxy that dynamically mirrors target web apps and interacts with…
 t3l3machus/pentest-pivoting
A compact guide to network pivoting for penetration testings / CTF challenges.
 sensepost/mallet
Mallet is an intercepting proxy for arbitrary protocols
 nccgroup/berserko
Burp Suite extension to perform Kerberos authentication
 xiaolichan/redcaddy
C2 redirector base on caddy
 mr-pmillz/gofireprox
FireProx written in Go
 stolenusername/cowitness
CoWitness is a powerful web application testing tool that enhances the accuracy and efficiency of your testing efforts. It allows you to mimic an…
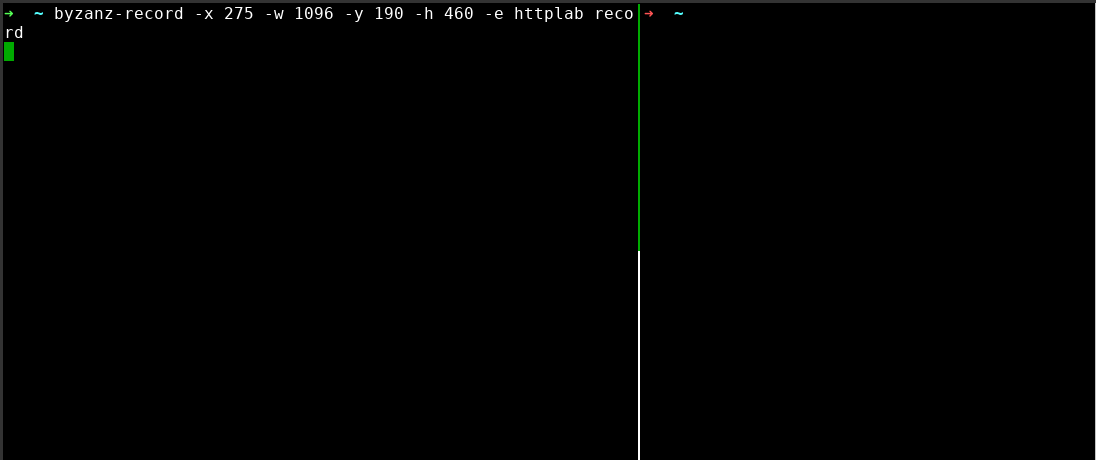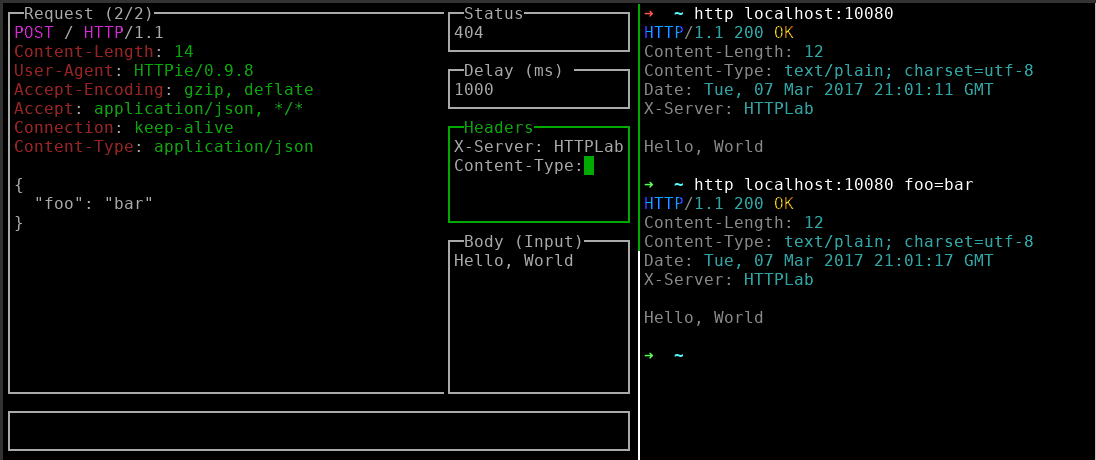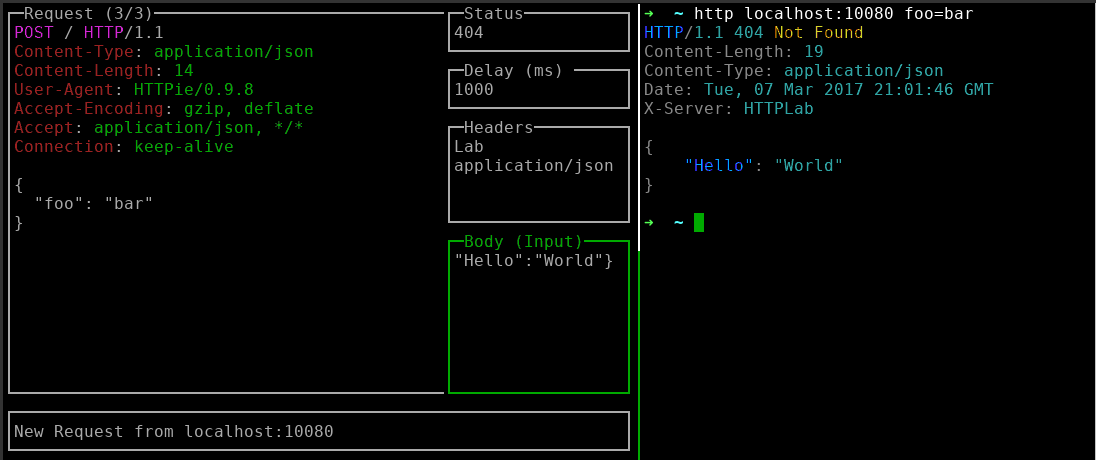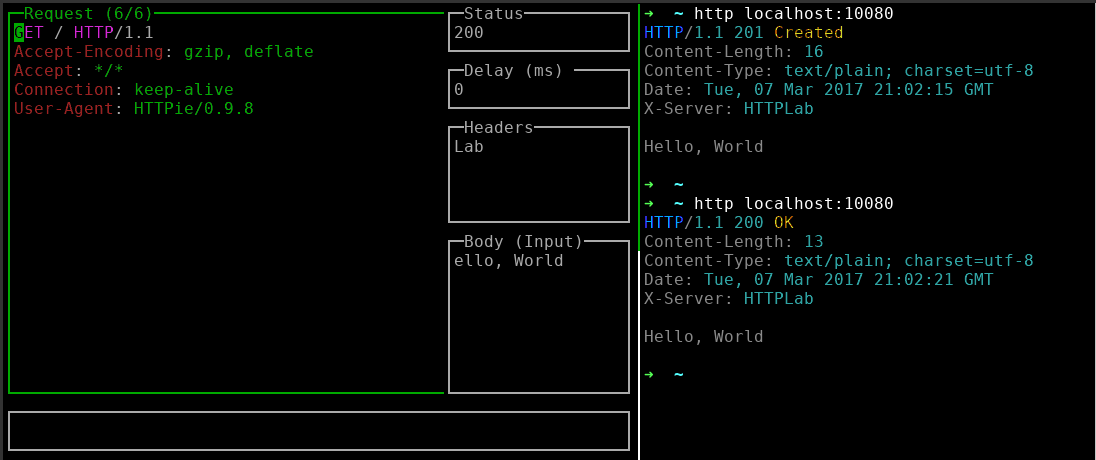 qustavo/httplab
Interactive web server for inspecting HTTP requests and forging responses, with a terminal UI for real-time debugging and API testing.