
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended
 seanwrightsec/cve-2022-42889-poc
Proof of Concept for the Apache commons-text vulnerability CVE-2022-42889.
 pyn3rd/cve-2019-2618
Weblogic Unrestricted File Upload
 doretox/atomicvulns
Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 sinsinology/cve-2024-6670
Proof-of-concept exploit for Progress WhatsUp Gold SQL injection authentication bypass (CVE-2024-6670). Includes root cause analysis and automated…
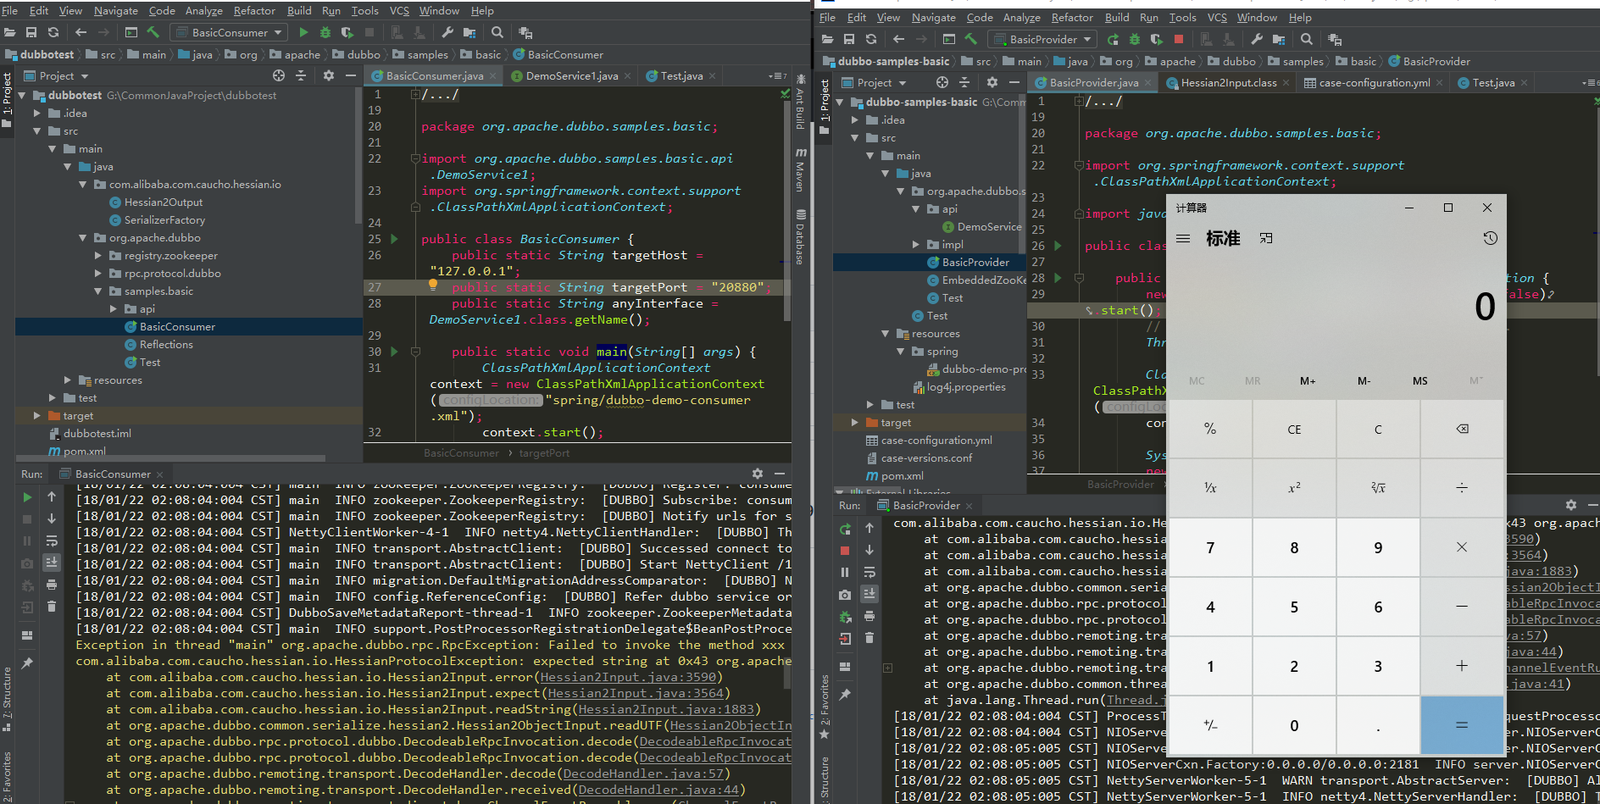 longofo/apache-dubbo-hessian2-cve-2021-43297
Demonstrates a proof-of-concept exploit for CVE-2021-43297, a deserialization vulnerability in Apache Dubbo's Hessian2 protocol, with provider and…
 ls4ss/cve-2021-41773_cve-2021-42013
Apache HTTP Server 2.4.49, 2.4.50 - Path Traversal & RCE
 future-client/cve-2021-44228
Abuse Log4J CVE-2021-44228 to patch CVE-2021-44228 in vulnerable Minecraft game sessions to prevent exploitation in the session :)
 nccgroup/wcfdser-ngng
A Burp Extender plugin, that will make binary soap objects readable and modifiable.
 benjaminhays/cve-2023-28771-poc
PoC for CVE-2023-28771 based on Rapid7's excellent writeup
 yoryio/cve-2024-27198
Exploit for CVE-2024-27198 - TeamCity Server
 momika233/loxs-optimized
Web vulnerability scanner focused on automated XSS/CSP bypass payload testing and batch SQL injection detection, using SQLMap and reporting only…
 p0dalirius/joomla-webshell-plugin
A webshell plugin and interactive shell for pentesting a Joomla website.
 jgoyd/glass-cage-ios18-cve-2025-24085-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, bypassing LockDown mode protection by exploiting ImageIO (CVE-2025-43300), then…
 sourceincite/hekate
Exploit for VMWare Workspace ONE Access chaining five CVEs for unauthenticated remote code execution via JDBC injection and privilege escalation.
 bigb0x/cve-2024-40348
POC for CVE-2024-40348. Will attempt to read /etc/passwd from target
 exploitbox/git-lfs-rce-exploit-cve-2020-27955
Git-lfs RCE exploit CVE-2020-27955 - tested on Windows on: git, gh cli, GitHub Desktop, Visual Studio, SourceTree etc.
 umair-aziz025/dahua-cve-research
Dahua IP camera CVE research toolkit (CVE-2021-33044/33045, CVE-2025-31700/31701)








