
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended
 zz-socmap/cve-2021-35587
Proof-of-concept exploit for CVE-2021-35587, an unauthenticated remote code execution vulnerability in Oracle Access Manager, allowing full takeover…
 bhdresh/cve-2021-33766
ProxyToken (CVE-2021-33766) : An Authentication Bypass in Microsoft Exchange Server POC exploit
 akamai/cve-2025-27636-apache-camel-poc
Proof-of-concept demonstrating remote code execution in Apache Camel by exploiting header and parameter filtering bypasses (CVE-2025-27636,…
 aiex-3/confluence-hack
Exploit for CVE-2023-22515 in Atlassian Confluence that creates a new admin user and deploys a web-based shell plugin for command execution on the…
 roo7break/serialator
Python script to exploit CVE-2015-4852.
 immersive-labs-sec/cve-2025-31161
Proof of Concept for CVE-2025-31161 / CVE-2025-2825
 en0f/cve-2017-7529_poc
Proof-of-concept exploit for CVE-2017-7529, an integer overflow vulnerability in Nginx HTTP server, enabling remote denial-of-service or potential…
 cyberheartmi9/cve-2017-8295
Proof-of-concept exploit for CVE-2017-8295, a WordPress password reset vulnerability allowing attackers to obtain reset links without authentication,…
 blackmathit/2017-11882_generator
CVE-2017-11882 File Generator PoC
 tin-z/cve-2025-27363
Integer overflow in FreeType software, which also affects Chrome
 muhammadwaseem29/cve-2025-53770
Unauthenticated Remote Code Execution via unsafe deserialization in Microsoft SharePoint Server (CVE-2025-53770)
 redrays-io/ws_racecondition_poc
Simple PoC for demonstrating Race Conditions on Websockets
 p0dalirius/cve-2022-45771-pwndoc-lfi-to-rce
Pwndoc local file inclusion to remote code execution of Node.js code on the server
 crowsec-edtech/cve-2022-22947
Spring Cloud Gateway < 3.0.7 & < 3.1.1 Code Injection (RCE)
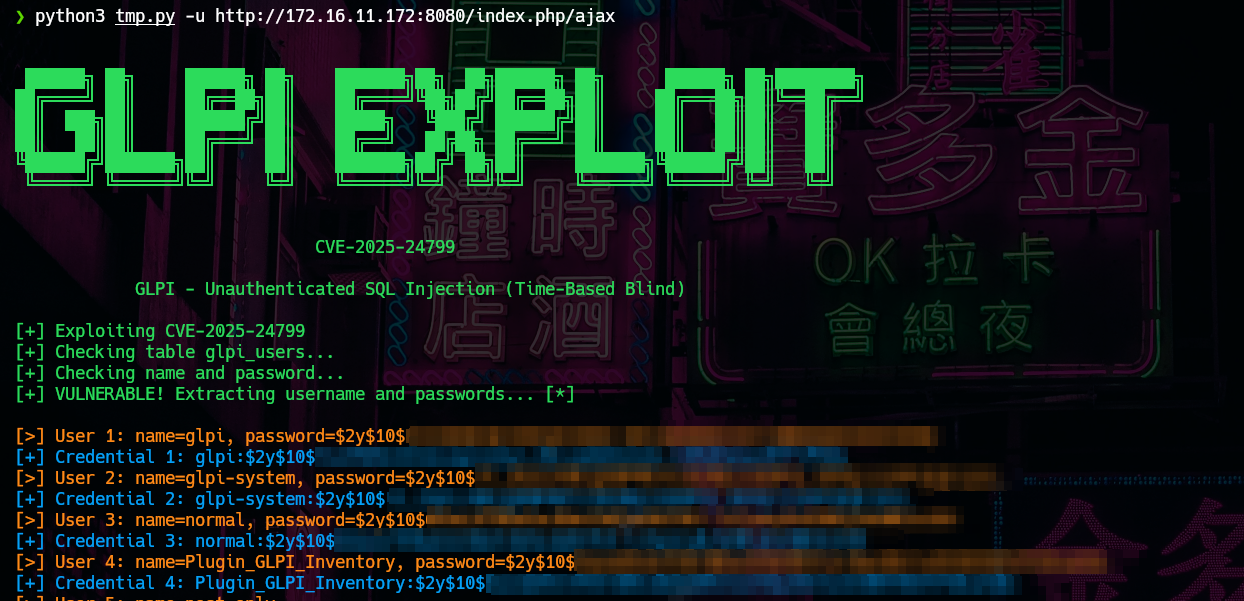 matheuzsecurity/exploit-cve-2025-24799
CVE-2025-24799 Exploit: GLPI - Unauthenticated SQL Injection
 rafabd1/vectorfreed
Documents the VectorFreed librsvg use-after-free RCE chain (CVE-2026-96889) with an SVG generator PoC and remediation guidance for librsvg, Next.js,…
 horizon3ai/cve-2023-34992
Proof-of-concept exploit for CVE-2023-34992 enabling unauthenticated blind command injection as root on vulnerable Fortinet FortiSIEM appliances.
 jpiechowka/zip-shotgun
Utility script to test zip file upload functionality (and possible extraction of zip files) for vulnerabilities (aka Zip Slip)








