
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended
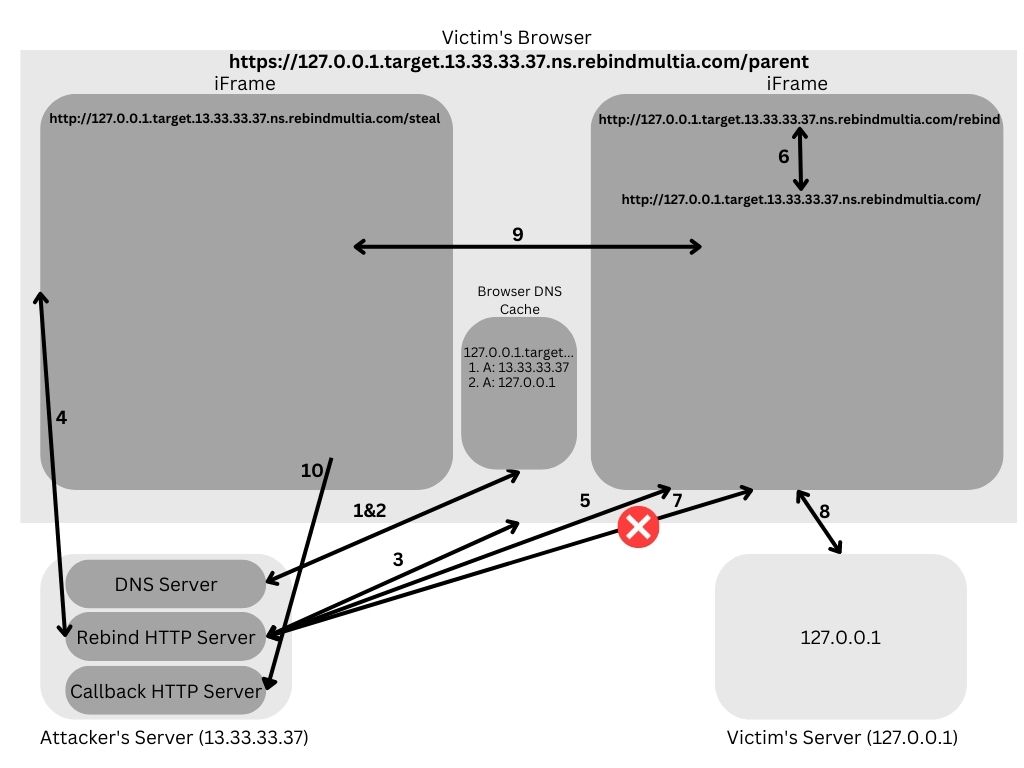
 rhynorater/rebindmultia
DNS rebinding attack tool exploiting multiple A records to bypass same-origin policy and exfiltrate data from internal network services via browser…
 ahisec/geoserver-
geoserver CVE-2024-36401漏洞利用工具
 jas502n/webuploader-0.1.15-demo
webuploader-v-0.1.15未授权-任意文件上传
 randomrobbiebf/cve-2023-7028
CVE-2023-7028

 horizon3ai/cve-2021-44077
Proof-of-concept exploit for PreAuth RCE in ManageEngine ServiceDesk Plus (CVE-2021-44077). Uploads and executes arbitrary Windows executables on…
 c1ph3rx13/cve-2023-42820
Exploit script for JumpServer password reset vulnerability CVE-2023-42820, with automatic verification code calculation and password modification.
 crowsec-edtech/cve-2022-26134
Python PoC exploit for CVE-2022-26134, a pre-authentication remote code execution vulnerability in Atlassian Confluence via OGNL injection. Executes…
 hexsecteam/cve-2025-8088-winrar-tool
A sophisticated GUI tool for creating malicious RAR archives that exploit the WinRAR path traversal vulnerability (CVE-2025-8088) using ADS and RAR5…
 4m3rr0r/cve-2025-47812-poc
Wing FTP Server Remote Code Execution (RCE) Exploit (CVE-2025-47812)
 ibonok/cve-2020-4463
IBM Maximo Asset Management is vulnerable to Information Disclosure via XXE Vulnerability (CVE-2020-4463)
 wuzuowei/cve-2020-17530
S2-061 的payload,以及对应简单的PoC/Exp
 err0r-ica/whatspayloadrce
Whatsapp Automatic Payload Generator [CVE-2019-11932]
 silverplate3/my-cves
CVE's I found. technical writeups, expolitation examples and fuzzing sessions walkthroughs
 pwntester/springbreaker
Exploit PoC for Spring RCE issue (CVE-2011-2894)
 win3zz/cve-2023-43261
CVE-2023-43261 - Credential Leakage Through Unprotected System Logs and Weak Password Encryption
 wjlin0/cve-2024-23897
CVE-2024-23897 - Jenkins 任意文件读取 利用工具
 onlytoxi/cve-2025-8088-winrar-tool
Advanced WinRAR Path Traversal Exploit Tool for CVE-2025-8088








