
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended
 7iosecurity/xss-payloads
Collection of cross-site scripting (XSS) payloads for web application security testing, filter bypass research, and penetration testing engagements.
 sourceincite/dashoverride
This is a pre-authenticated RCE exploit for VMware vRealize Operations Manager
 mzzdtot/cve-2023-28432
MinIO敏感信息泄露漏洞批量扫描poc&exp
 csenox/cve-2021-22911
Pre-Auth Blind NoSQL Injection leading to Remote Code Execution in Rocket Chat 3.12.1
 taroballzchen/cve-2022-41040-metasploit-proxynotshell
the metasploit script(POC) about CVE-2022-41040. Microsoft Exchange are vulnerable to a server-side request forgery (SSRF) attack. An authenticated…
 embedi/amt_auth_bypass_poc
CVE-2017-5689 Proof-of-Concept exploit
 le1a/cve-2023-33246
Apache RocketMQ 远程代码执行漏洞(CVE-2023-33246) Exploit
 pimps/cve-2019-2725
WebLogic Insecure Deserialization - CVE-2019-2725 payload builder & exploit
 iletee/struts2-rce
Exploitable target to CVE-2017-5638
 hrishikesh7665/follina_exploiter_cli
Exploit Microsoft Zero-Day Vulnerability Follina (CVE-2022-30190)
 jas502n/cve-2019-2890
Exploit for CVE-2019-2890 WebLogic deserialization RCE with ysoserial integration, providing step-by-step PoC for remote code execution via T3…
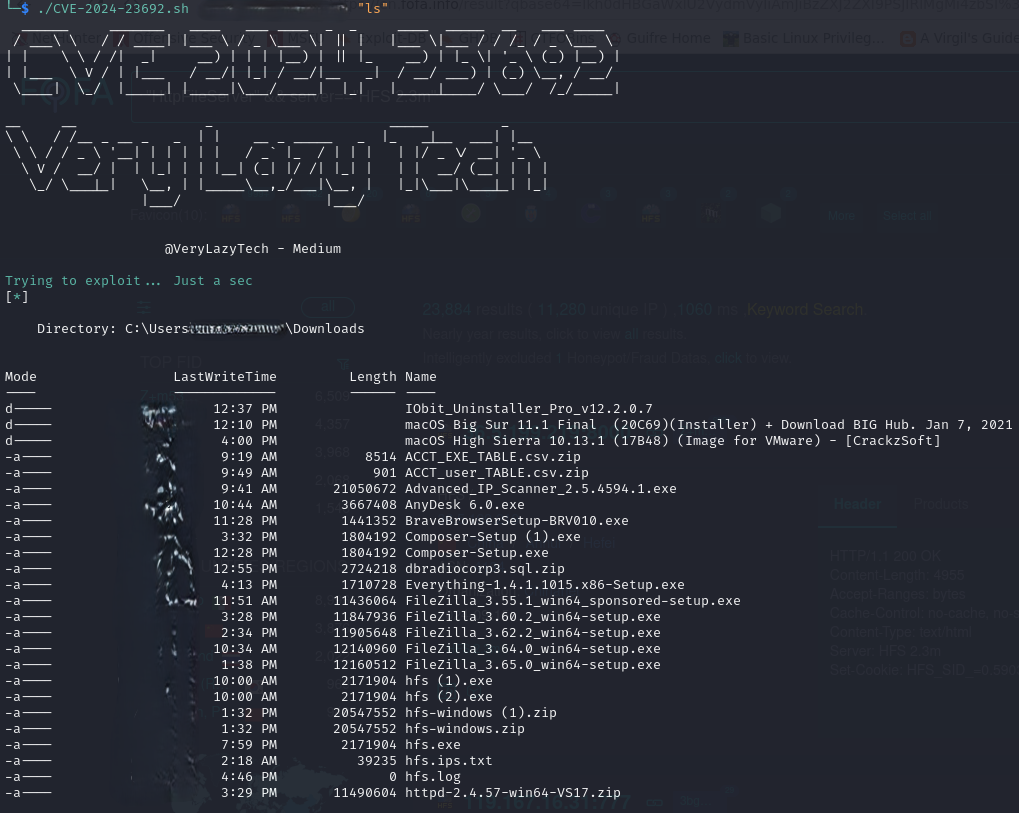 verylazytech/cve-2024-23692
POC - Unauthenticated RCE Flaw in Rejetto HTTP File Server - CVE-2024-23692
 stuub/cve-2024-4040-ssti-lfi-poc
CVE-2024-4040 CrushFTP SSTI LFI & Auth Bypass | Full Server Takeover | Wordlist Support
 tangxiaofeng7/cve-2022-22947-spring-cloud-gateway
CVE-2022-22947批量
 do4choo/cve-2026-3227-tp-link-authenticated-rce
Proof-of-concept for authenticated OS command injection in TP-Link router firmware. Includes decryption, QEMU-based encryption hook, and 15-character…
 sophoslabs/cve-2018-18500
PoC for CVE-2018-18500 - Firefox Use-After-Free
 nuts7/cve-2023-27372
SPIP before 4.2.1 allows Remote Code Execution via form values in the public area because serialization is mishandled. The fixed versions are 3.2.18,…
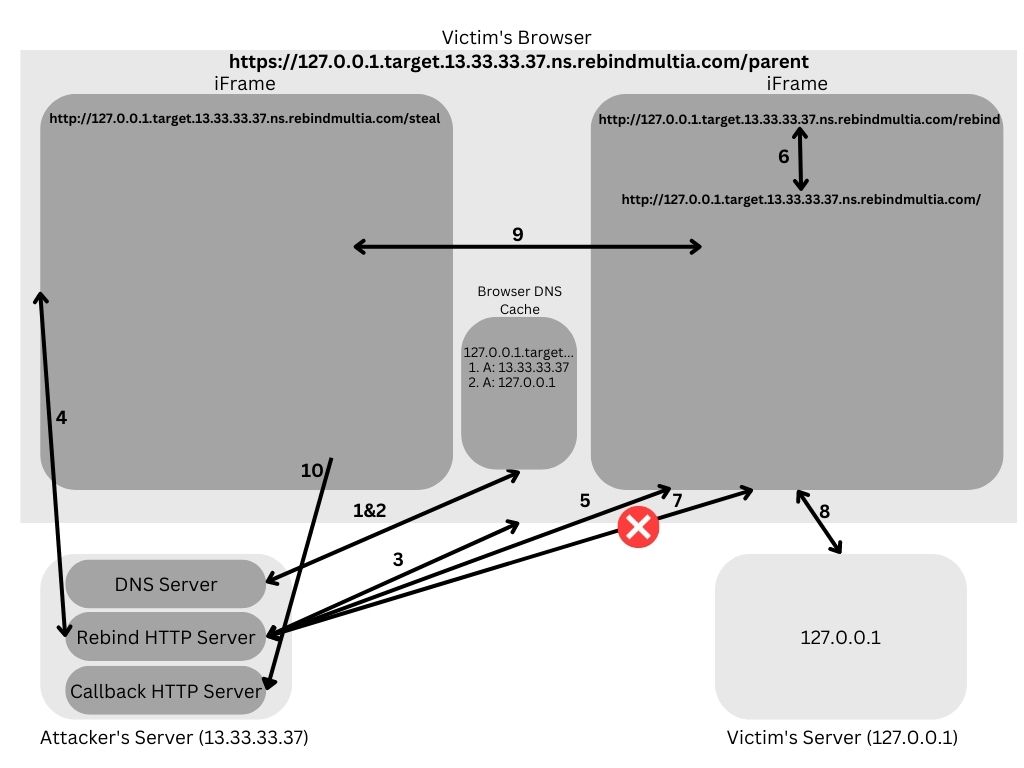 rhynorater/rebindmultia
DNS rebinding attack tool exploiting multiple A records to bypass same-origin policy and exfiltrate data from internal network services via browser…








