
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended

 0xsha/wp2shell
CVE-2026-63030 + CVE-2026-60137 - “wp2shell”: unauthenticated RCE in WordPress core
 deathshotxd/comment2shell
Zero-click pre-auth WordPress CVE-2026-93485 exploit chain: stored XSS in wpautop() escalates to admin-session plugin upload and a self-deleting…
 jas502n/oa-tongda-rce
Office Anywhere网络智能办公系统
 dxask88ma/weblogic-cve-2023-21839
Java-based exploit for CVE-2023-21839 targeting Oracle WebLogic Server versions 12.2.1.3.0 and 12.2.1.4.0 via LDAP injection for remote code…
 koadt/oss-oopssec-store
Security training for the apps you actually ship. Open your browser and start hacking.
 g0rx/cve-2018-7600-drupal-rce
PoC exploit collection for CVE-2018-7600 Drupal RCE with multiple scripts targeting Drupal 7 and 8, including mass exploitation variants.
 dhmosfunk/7-zip-cve-2025-0411-poc
This repository contains POC scenarios as part of CVE-2025-0411 MotW bypass.
 hktalent/cve-2020-2551
how detect CVE-2020-2551 poc exploit python Weblogic RCE with IIOP
 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 puliczek/cve-2021-21123-poc-google-chrome
🐱💻 👍 Google Chrome - File System Access API - vulnerabilities reported by Maciej Pulikowski | Total Bug Bounty Reward: $5.000 | CVE-2021-21123…
 jas502n/cve-2019-11581
Atlassian JIRA Template injection vulnerability RCE
 h4x0r-dz/cve-2024-21762
out-of-bounds write in Fortinet FortiOS CVE-2024-21762 vulnerability
 duc-nt/cve-2020-6287-exploit
PoC for CVE-2020-6287 The PoC in python for add user only, no administrator permission set. Inspired by @zeroSteiner from metasploit. Original…
 cyberxml/log4j-poc
A Docker based LDAP RCE exploit demo for CVE-2021-44228 Log4Shell
 redteampentesting/cve-2020-13935
Exploit for WebSocket Vulnerability in Apache Tomcat
 nxenon/h2spacex
HTTP/2 Last Frame Synchronization (also known as Single Packet Attack) low Level Library / Tool based on Scapy + Exploit Timing Attacks
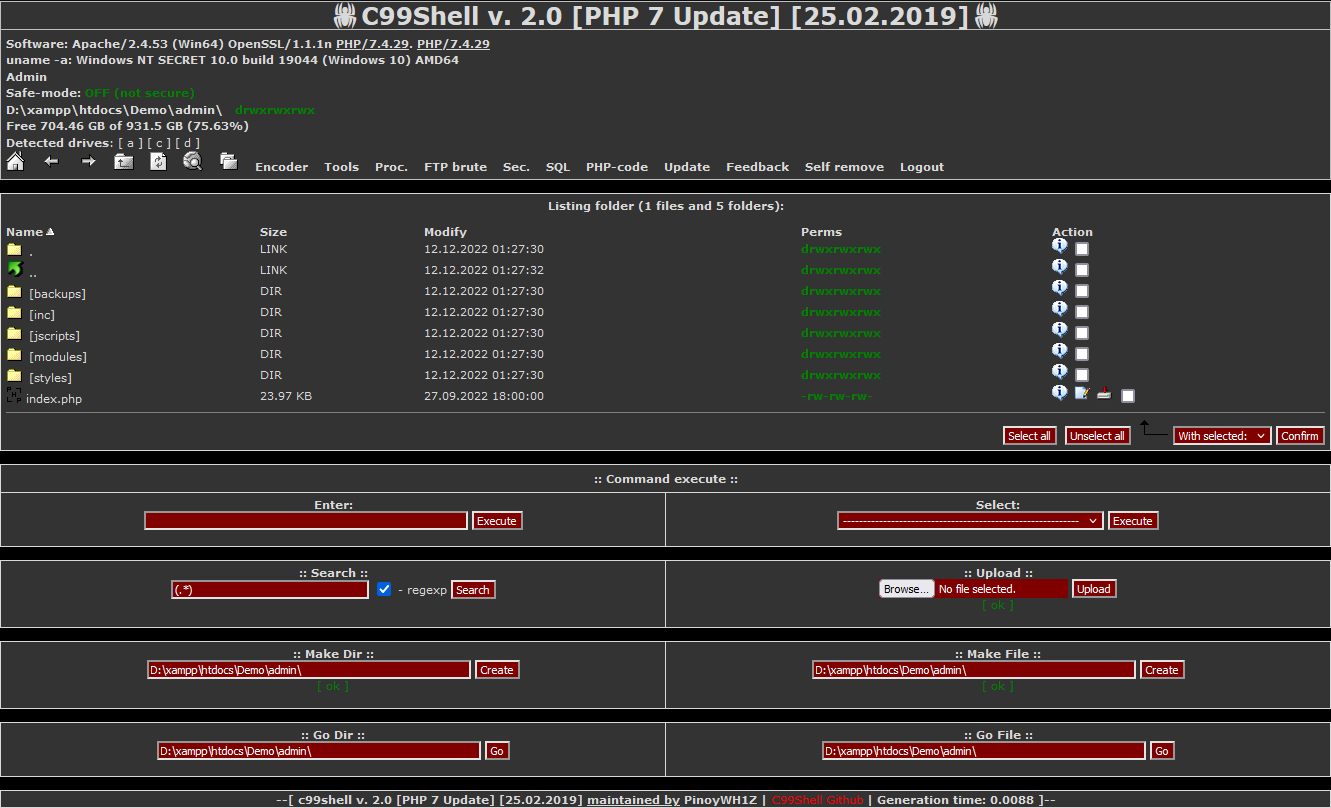 pinoywh1z/c99shell-php7
PHP 7 and safe-build Update of the popular C99 variant of PHP Shell.
 alienwithin/owasp-mth3l3m3nt-framework
OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…








