
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended

 lourc0d3/cve-2024-4367-poc
CVE-2024-4367 & CVE-2024-34342 Proof of Concept
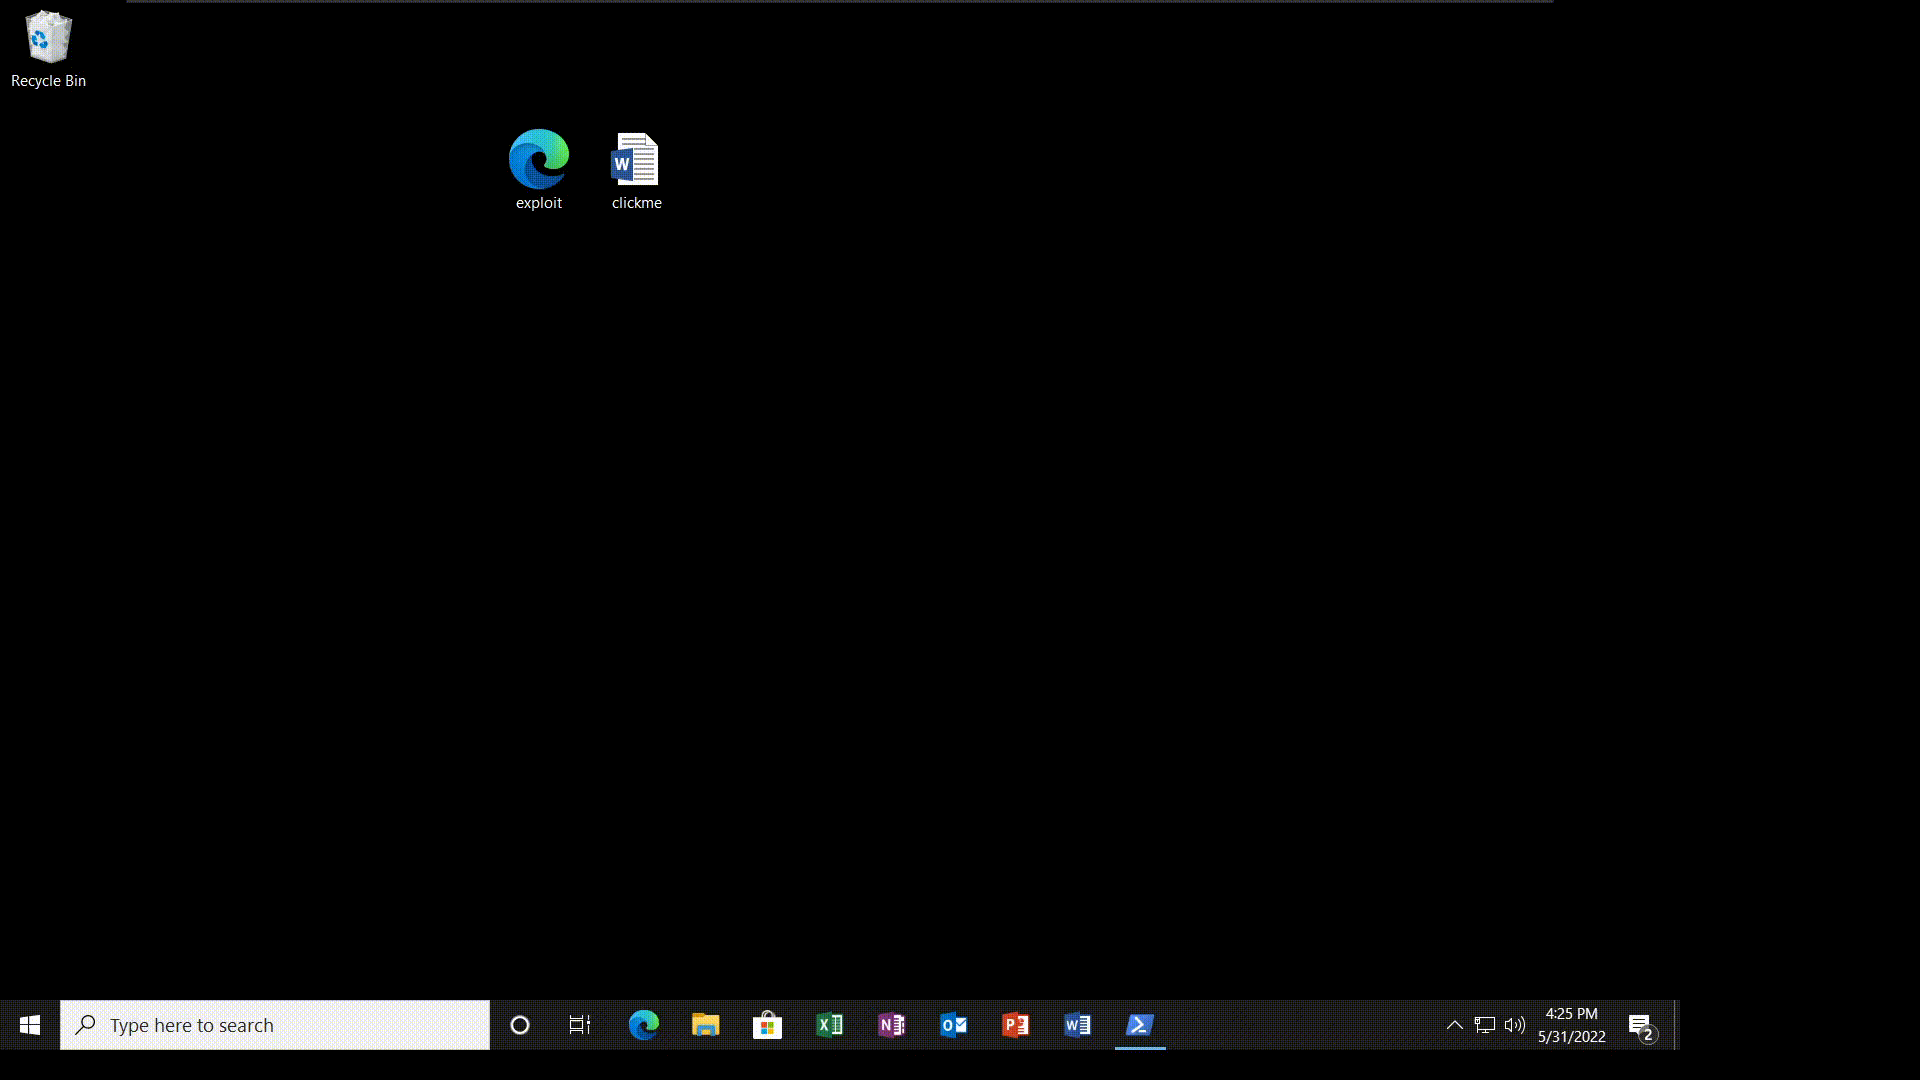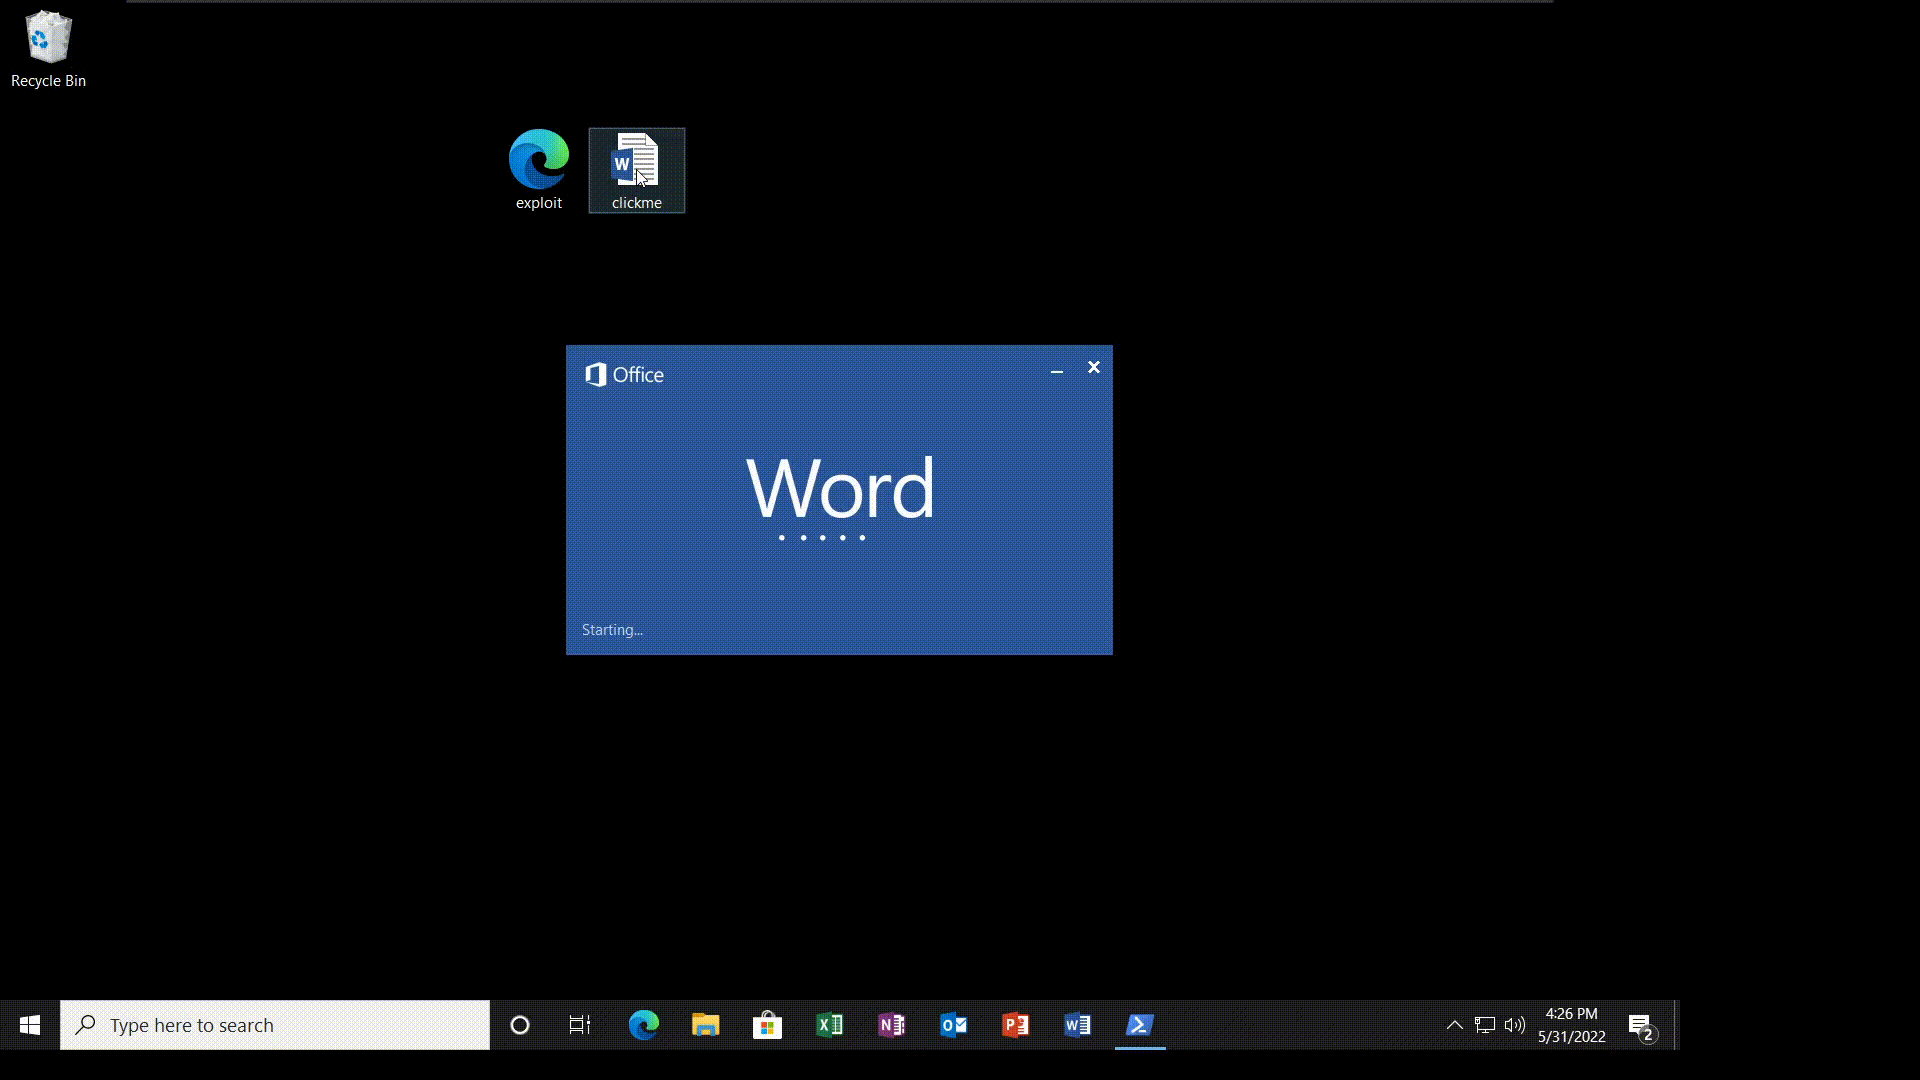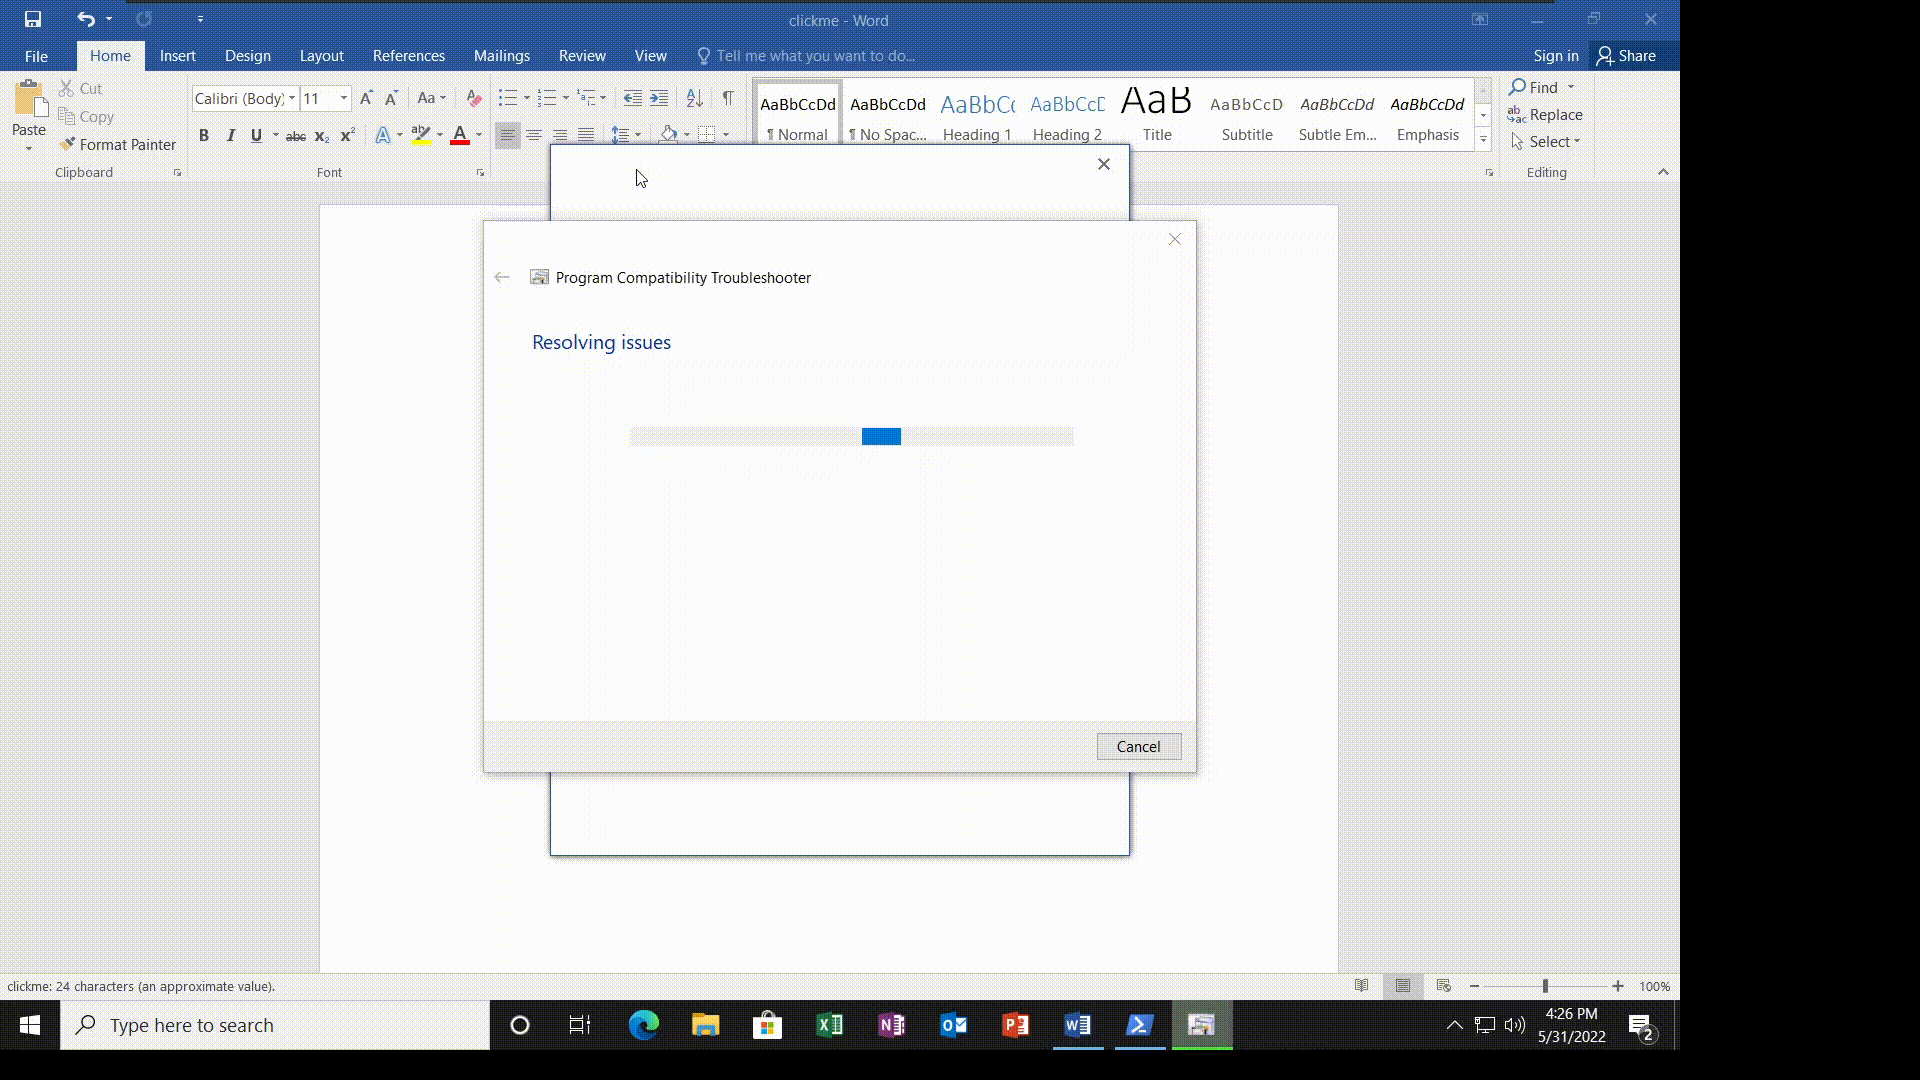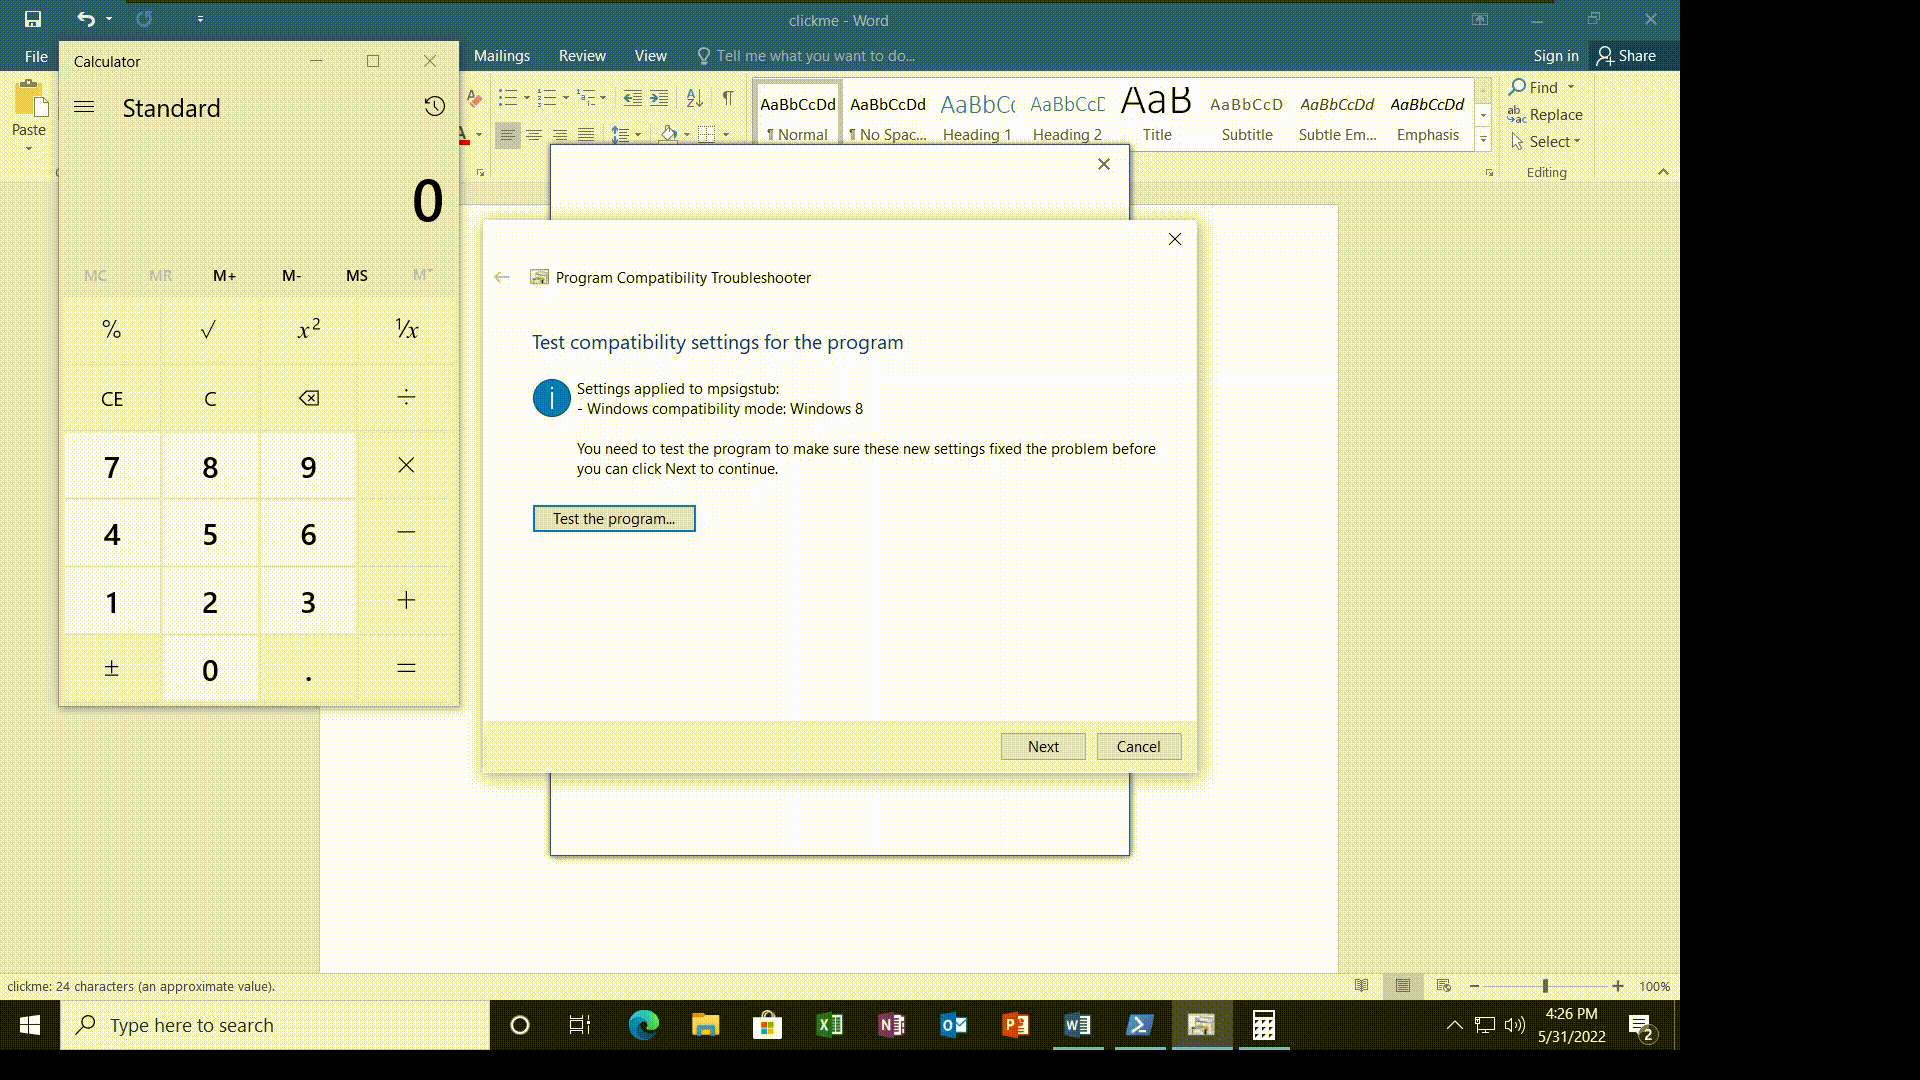 onecloudemoji/cve-2022-30190
CVE-2022-30190 Follina POC
 appsecco/dvcsharp-api
Damn Vulnerable C# Application (API)
 tuhinshubhra/shellstack
A PHP Based Tool That Helps You To Manage All Your Backdoored Websites Efficiently.
 sma11new/poclist
漏洞POC、EXP合集,持续更新。Apache Druid-任意文件读取(CVE-2021-36749)、ConfluenceRCE(CVE-2021-26084)、ZeroShell防火墙RCE(CVE-2019-12725)、ApacheSolr任意文件读取、蓝凌OA任意文件读取、phpStud…
 mrd0x/webview2-cookie-stealer
Injects JavaScript keylogger into WebView2 pages to capture keystrokes and exfiltrate cookies from Microsoft authentication sessions via HTTP GET…
 ethicalhackingplayground/tproxer
A Burp Suite extension made to automate the process of finding reverse proxy path based SSRF.
 milo2012/cve-2018-13382
CVE-2018-13382
 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
 convisolabs/cve-2024-43044-jenkins
Exploit for the vulnerability CVE-2024-43044 in Jenkins
 theori-io/chakra-2016-11
Proof-of-Concept exploit for Edge bugs (CVE-2016-7200 & CVE-2016-7201)
 mr-r3bot/gitlab-cve-2021-22205
Unauthenticated remote code execution exploit for GitLab versions < 13.10.3, leveraging ExifTool DjVu annotation parsing to execute arbitrary…
 esmog/nodexp
NodeXP - A Server Side Javascript Injection tool capable of detecting and exploiting Node.js vulnerabilities
 hosch3n/proxyvulns
[ProxyLogon] CVE-2021-26855 & CVE-2021-27065 Fixed RawIdentity Bug Exploit. [ProxyOracle] CVE-2021-31195 & CVE-2021-31196 Exploit Chains.…
 offxec/thedoc
Automates SQL injection exploitation with SQLMAP, crawls for vulnerabilities, extracts database credentials, finds admin login pages, and cracks…
 jmousqueton/poc-cve-2022-30190
POC CVE-2022-30190 : CVE 0-day MS Offic RCE aka msdt follina
 watchtowrlabs/citrix-virtual-apps-xen-exploit
Citrix Virtual Apps and Desktops (XEN) Unauthenticated RCE
 bishopfox/json-interop-vuln-labs
Companion labs to "An Exploration of JSON Interoperability Vulnerabilities"








