
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended
 exodusintel/cve-2019-5786
FileReader Exploit
 dinosn/fastjson-jsontype-rce-lab
Docker labs + defensive scanner for fastjson remote-class-load RCE. fastjson 1.2.66-1.2.83: @JSONType resource probe (CVE-2026-16723). fastjson2…
 paradoxis/flask-unsign
Command line tool to fetch, decode, brute-force and craft session cookies of a Flask application by guessing secret keys.
 al1ex/cve-2021-22205
CVE-2021-22205& GitLab CE/EE RCE
 weev3/lkwa
Lesser Known Web Attack Lab
 bobtheshoplifter/spring4shell-poc
Spring4Shell Proof Of Concept/And vulnerable application CVE-2022-22965

 jas502n/cnvd-c-2019-48814
WebLogic wls9-async反序列化远程命令执行漏洞
 milo2012/cve-2018-13379
CVE-2018-13379
 jas502n/cve-2020-14882
Weblogic CVE-2020-14882 unauthorized RCE exploit with patch bypass, command execution, and webshell deployment for penetration testing.
 appsecco/vulnerable-mcp-servers-lab
A collection of servers which are deliberately vulnerable to learn Pentesting MCP Servers.
 horizon3ai/cve-2021-21972
Proof of Concept Exploit for vCenter CVE-2021-21972
 ynsmroztas/nextrce
React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)
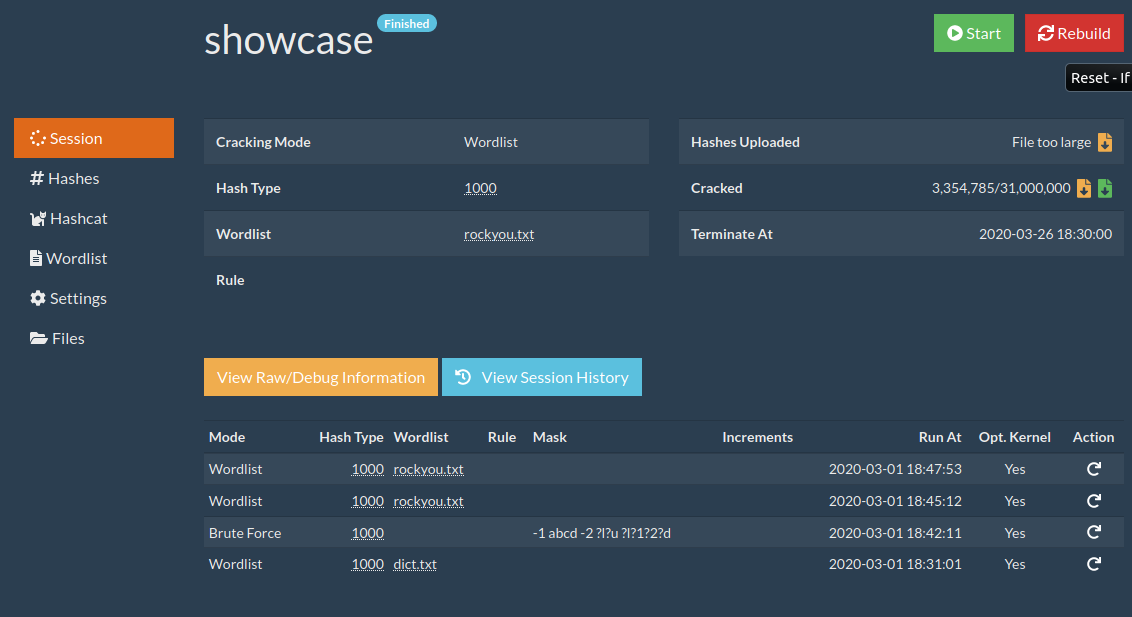 ctxis/crackerjack
CrackerJack / Hashcat Web Interface / Context Information Security
 bdblackhat/admin-panel-finder
Python script to discover admin panel URLs of websites, aiding in security reconnaissance and penetration testing.
 paralelo14/google_explorer
Mass exploitation tool in python
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 yt1g3r/cve-2020-0688_exp
CVE-2020-0688_EXP Auto trigger payload & encrypt method








