
 #1
Tools for identifying, assessing, and prioritizing security weaknesses in systems and applications.
Kitploit recommended
 r1is/cve-2022-0847
CVE-2022-0847-DirtyPipe-Exploit CVE-2022-0847 是存在于 Linux内核 5.8 及之后版本中的本地提权漏洞。攻击者通过利用此漏洞,可覆盖重写任意可读文件中的数据,从而可将普通权限的用户提升到特权 root。 CVE-2022-0847…
 appsecco/vulnerable-mcp-servers-lab
A collection of servers which are deliberately vulnerable to learn Pentesting MCP Servers.
 milo2012/cve-2018-13379
CVE-2018-13379
 solomonsklash/chomp-scan
A scripted pipeline of tools to streamline the bug bounty/penetration test reconnaissance phase, so you can focus on chomping bugs.
 ynsmroztas/nextrce
React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)
 opennetworkingfoundation/delta
PROJECT DELTA: SDN SECURITY EVALUATION FRAMEWORK
 wish-i-was/femida
Automated blind-xss search for Burp Suite
 tykawaii98/cve-2024-30088
Proof-of-concept exploit for CVE-2024-30088, a Windows kernel TOCTOU vulnerability in AuthzBasepCopyoutInternalSecurityAttributes enabling arbitrary…
 darrenmartyn/visualdoor
SonicWall SSL-VPN Exploit
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
 hubblestack/hubble
Hubble is a modular, open-source security compliance framework. The project provides on-demand profile-based auditing, real-time security event…
 paralelo14/google_explorer
Mass exploitation tool in python
 w-digital-scanner/w12scan-client
Network asset discovery and scanning client that integrates nmap and masscan for large-scale asset identification, port scanning, and vulnerability…
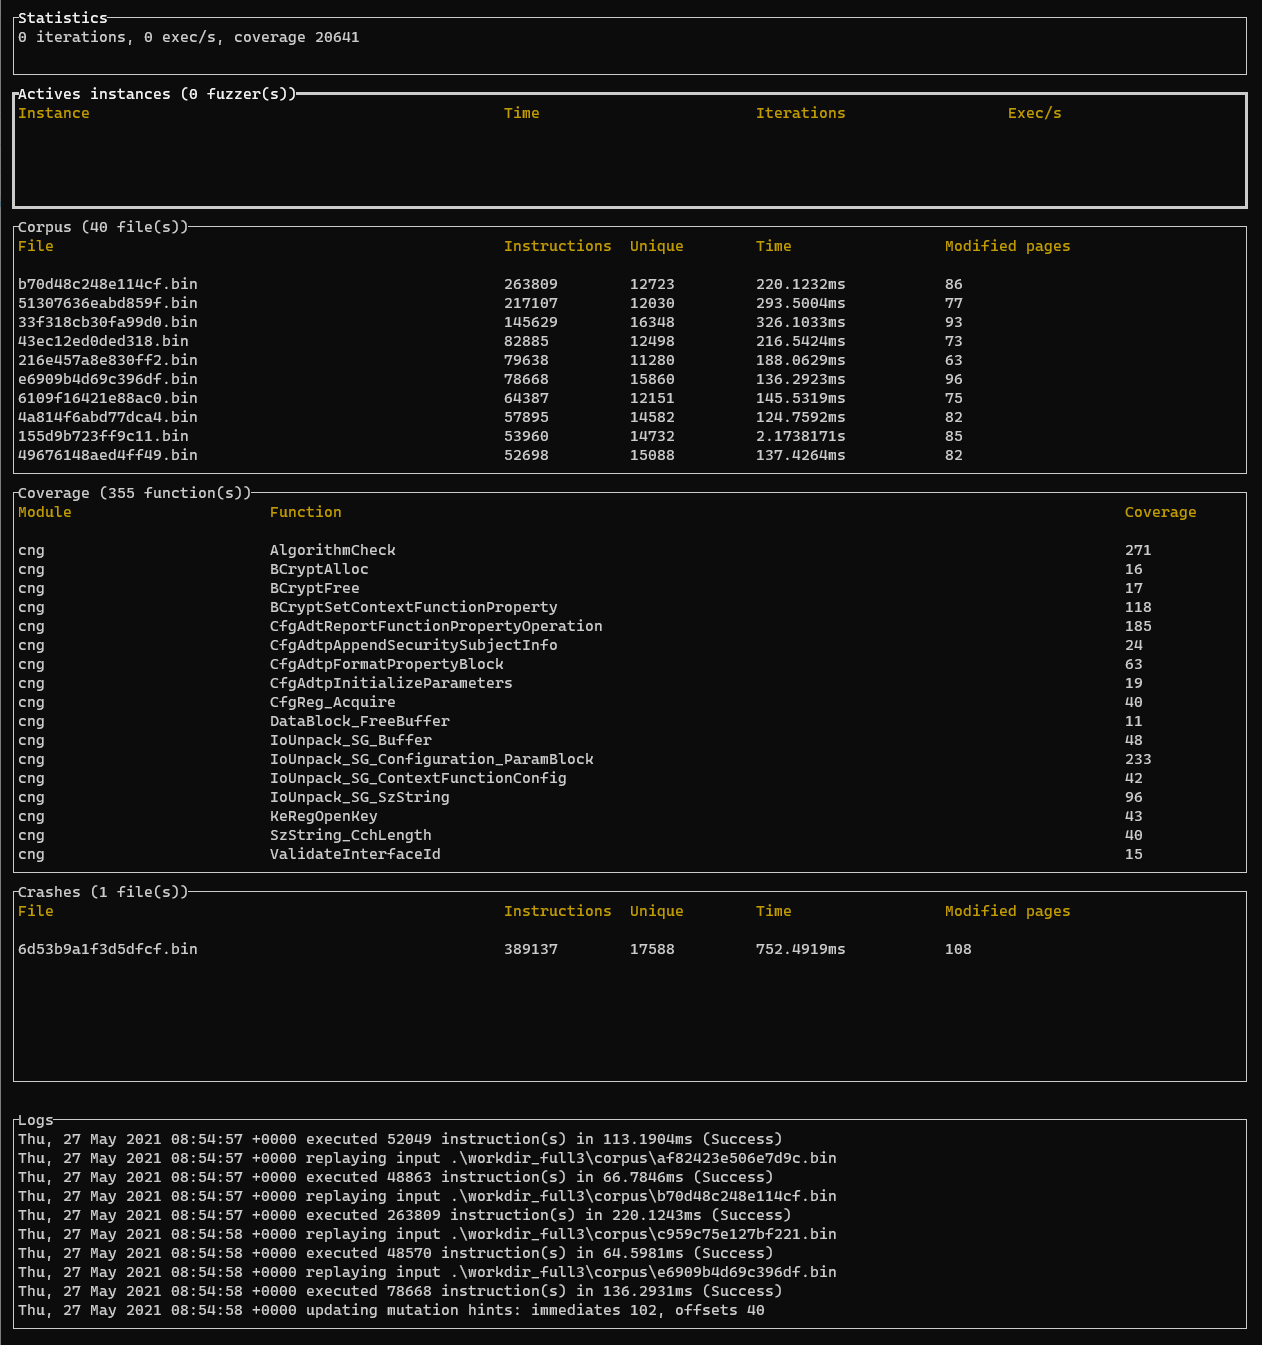 quarkslab/rewind
Snapshot-based coverage-guided windows kernel fuzzer
 zhuowei/cheese
CVE-2025-21479 proof-of-concept, I think
 evilsocket/dirsearch
Concurrent web directory and file brute-forcing tool that performs HEAD requests against a target URL using a wordlist, with support for custom…
 4shadoww/hakkuframework
Hakku Framework penetration testing
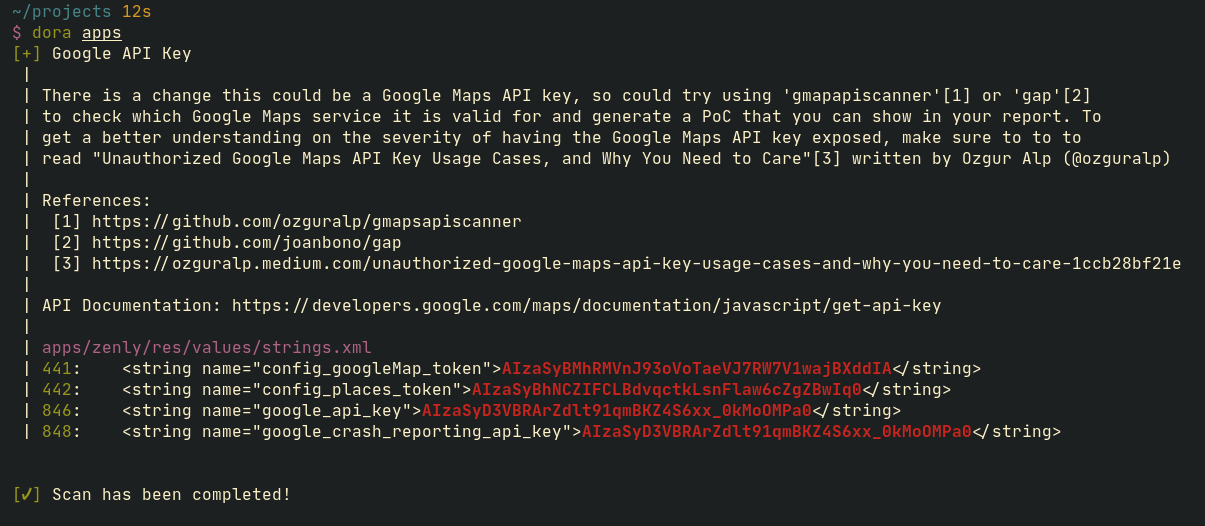 sdushantha/dora
Find exposed API keys based on RegEx and get exploitation methods for some of keys that are found








