
 #1
Tools for identifying, assessing, and prioritizing security weaknesses in systems and applications.
Kitploit recommended
 soltanali0/cve-2025-53770-exploit
SharePoint WebPart Injection Exploit Tool
 genai-security-project/genai-llm-top10
OWASP Top 10 for Large Language Model Applications
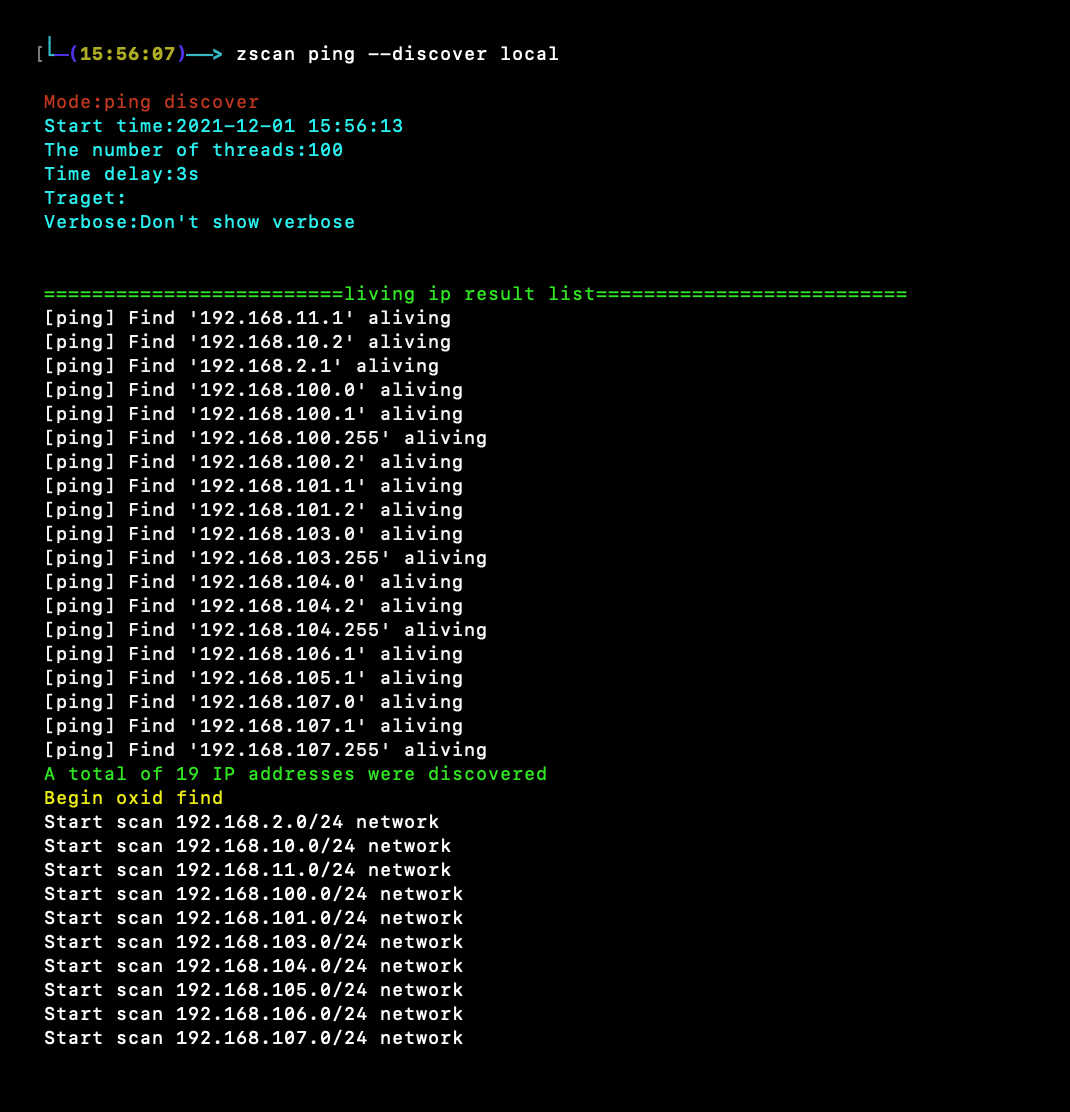 zyylhn/zscan
Zscan a scan blasting tool set
 cisagov/kev-data
Mirrors CISA's Known Exploited Vulnerabilities (KEV) catalog as CSV and JSON with a JSON schema, enabling programmatic access and commit-history…
 flipkart-incubator/rta
Red team Arsenal - An intelligent scanner to detect security vulnerabilities in company's layer 7 assets.
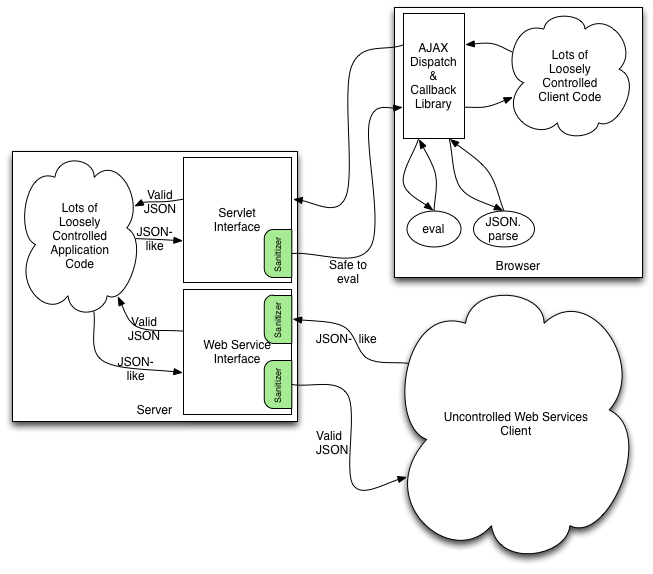 owasp/json-sanitizer
Given JSON-like content, The JSON Sanitizer converts it to valid JSON.
 dmontgomery40/pentest-mcp
NOT for educational purposes: An MCP server for professional penetration testers including STDIO/HTTP/SSE support, nmap, go/dirbuster, nikto, JtR,…
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
 garatc/bitunlocker
Downgrade attack for CVE-2025-48804
 ethicalhackingplayground/ssrf-king
SSRF plugin for burp Automates SSRF Detection in all of the Request
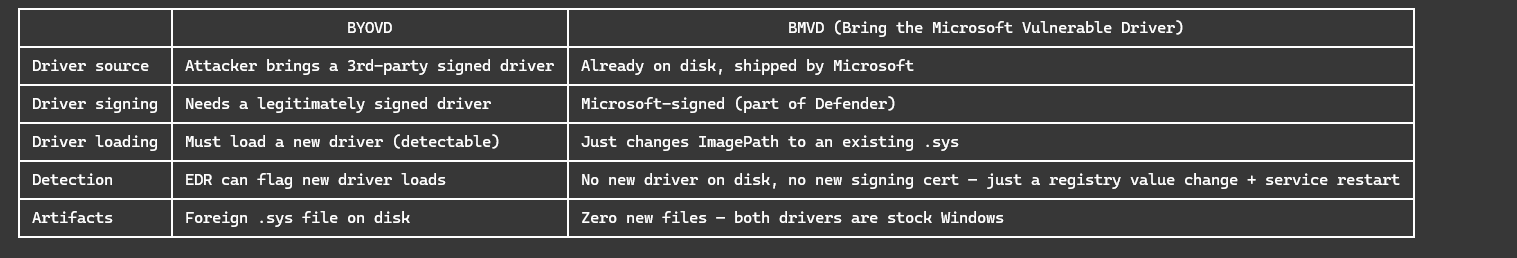 andreisss/ksldump
KslDump — Why bring your own knife when Defender already left one in the kitchen?
 evict/poc_cve-2018-1002105
Proof-of-concept exploit for CVE-2018-1002105 targeting Kubernetes API server. Supports authenticated and unauthenticated privilege escalation to…
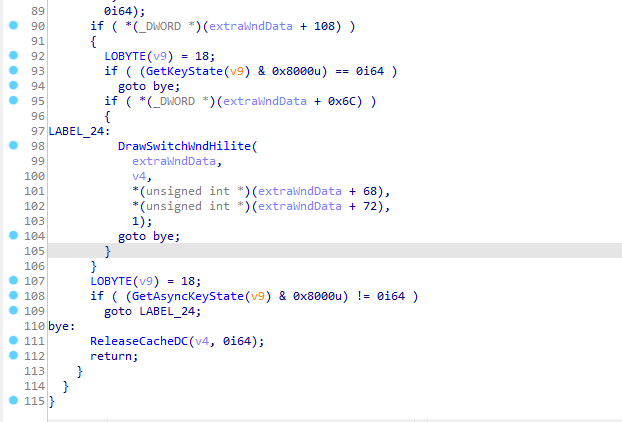 piotrflorczyk/cve-2019-1458_poc
POC for cve-2019-1458

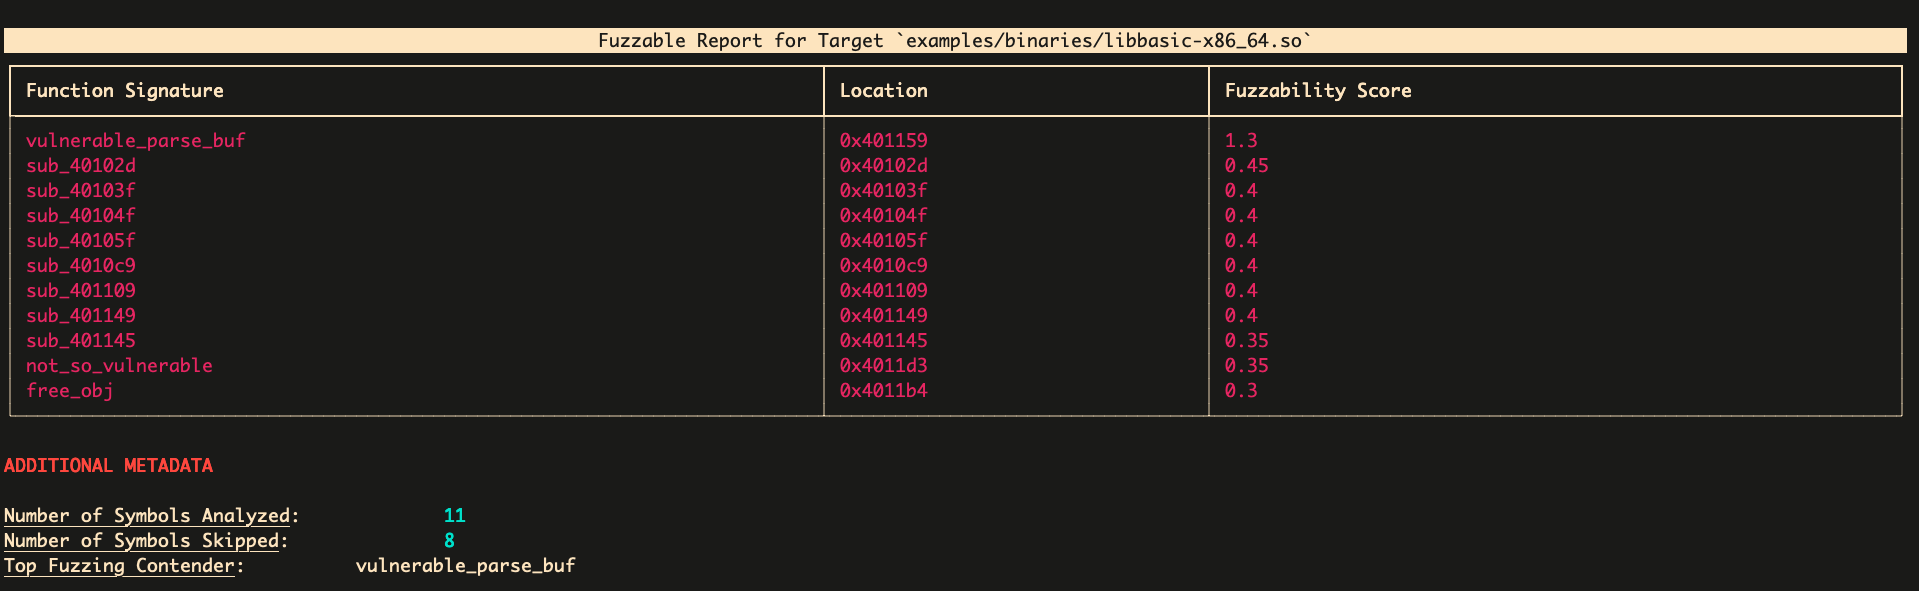 ex0dus-0x/fuzzable
Static analysis framework that identifies fuzzable function targets in source code and binaries, generates harness templates, and integrates with…
 zblurx/certsync
Dump NTDS with golden certificates and UnPAC the hash
 cyberark/blobhunter
Find exposed data in Azure with this public blob scanner








