
 #1
Tools for identifying, assessing, and prioritizing security weaknesses in systems and applications.
Kitploit recommended
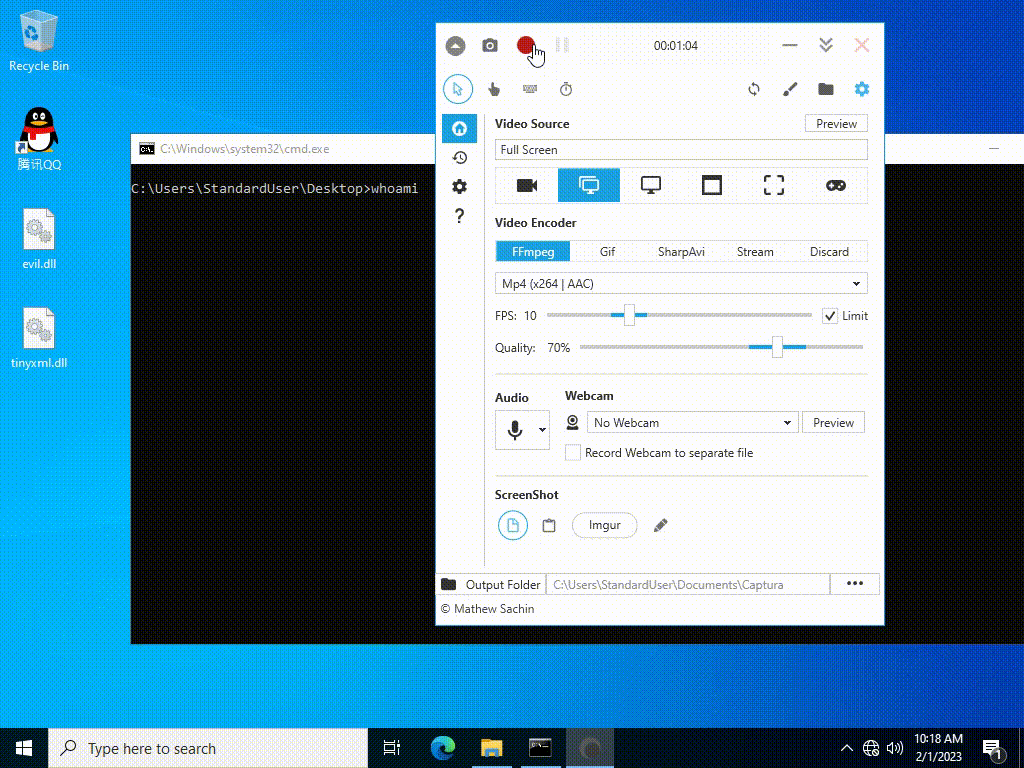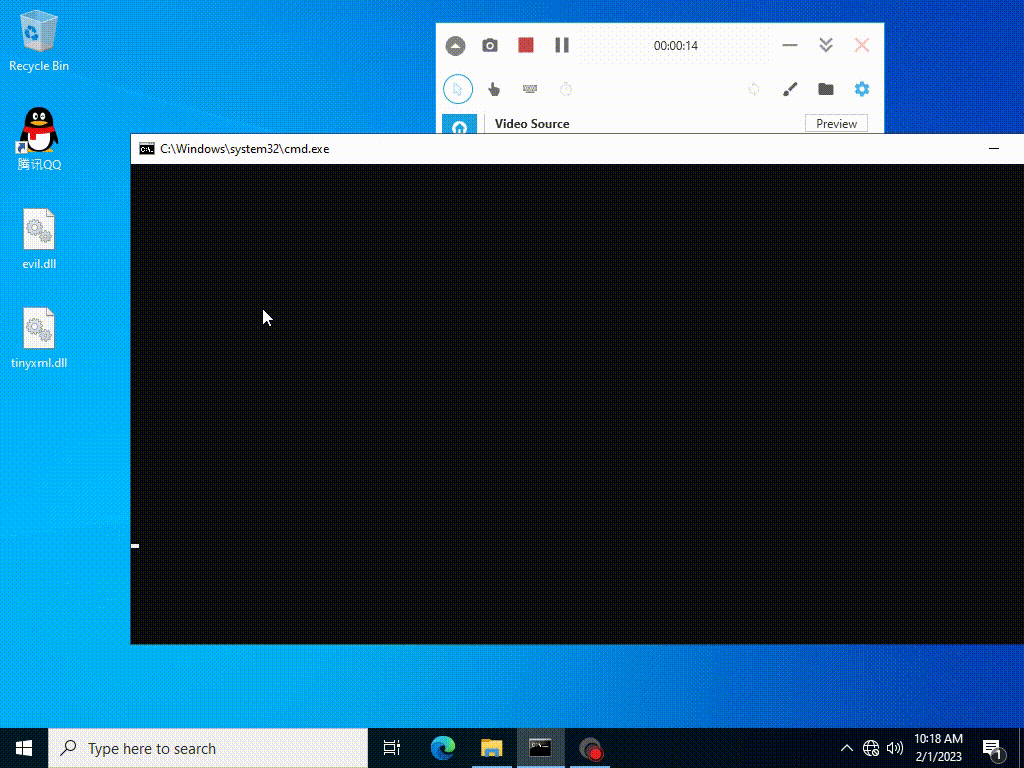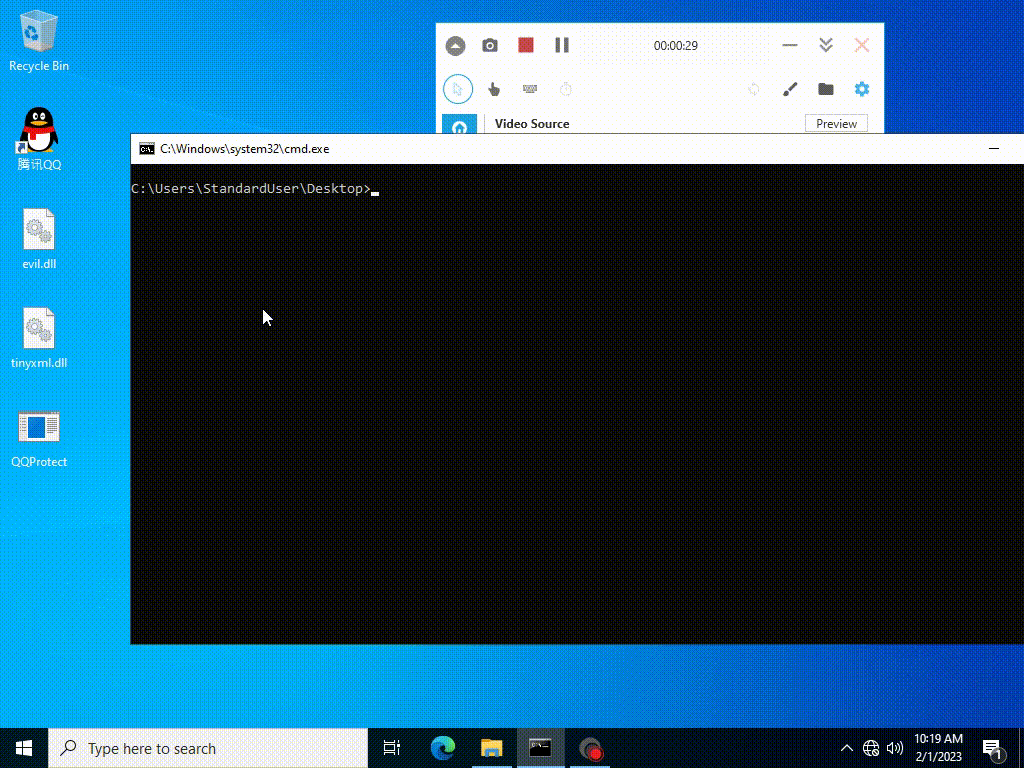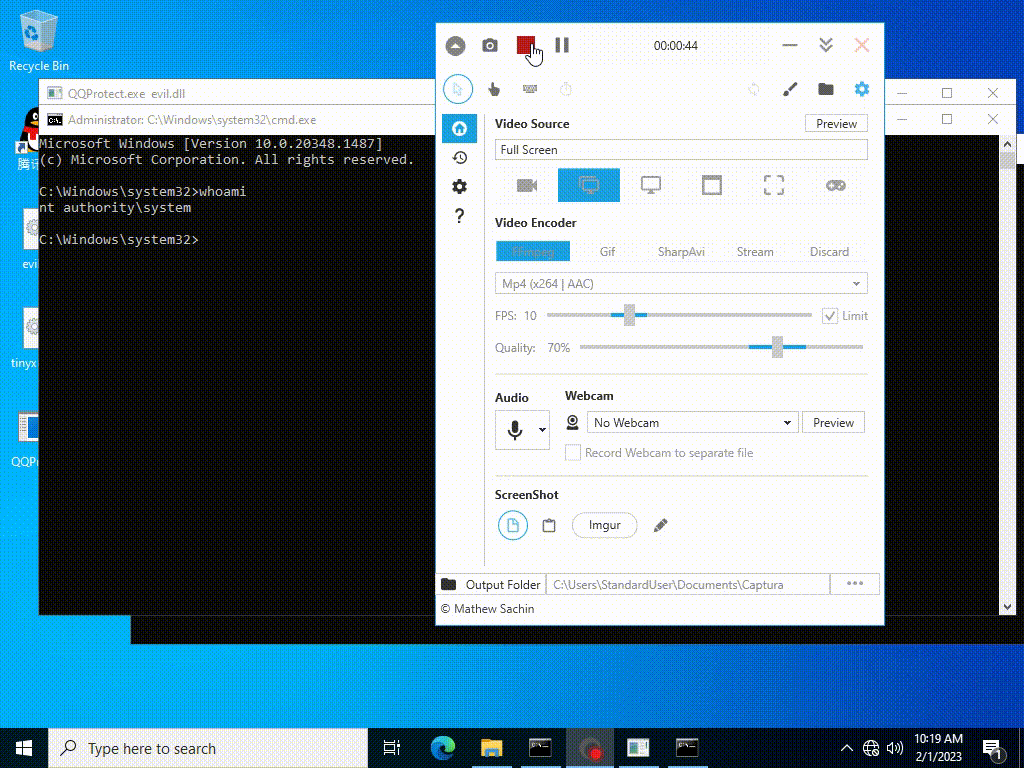
 vi3t1/qq-tim-elevation
CVE-2023-34312
 0x6rss/cve-2025-24071_poc
CVE-2025-24071: NTLM Hash Leak via RAR/ZIP Extraction and .library-ms File
 horizon3ai/cve-2022-40684
A proof of concept exploit for CVE-2022-40684 affecting Fortinet FortiOS, FortiProxy, and FortiSwitchManager
 dzonerzy/gowapt
Go Web Application Penetration Test
 its-arun/cve-2022-39197
Proof-of-concept exploit for CVE-2022-39197, enabling remote code execution against CobaltStrike <= 4.7.1 via malicious SVG payload served over HTTP.
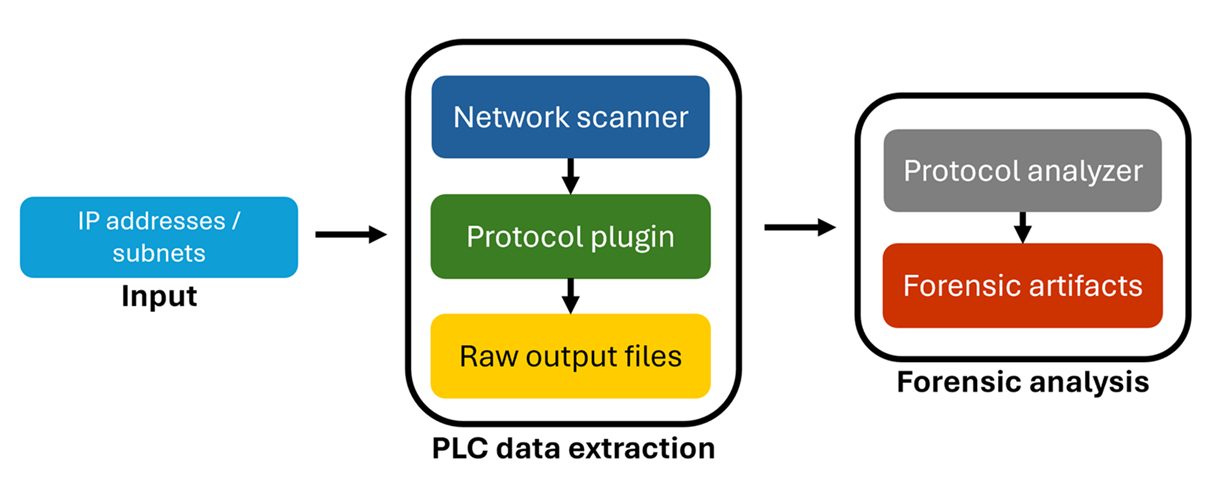 microsoft/ics-forensics-tools
Open-source forensics framework for analyzing Industrial PLC metadata and project files. Scans for suspicious artifacts in ICS environments to…
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 trustedsec/spoonmap
Python wrapper around masscan and nmap for large-scale port discovery, host discovery, banner grabbing, and NSE-based vulnerability scanning across…
 thomastjdev/wmd
Python framework for IT security tools
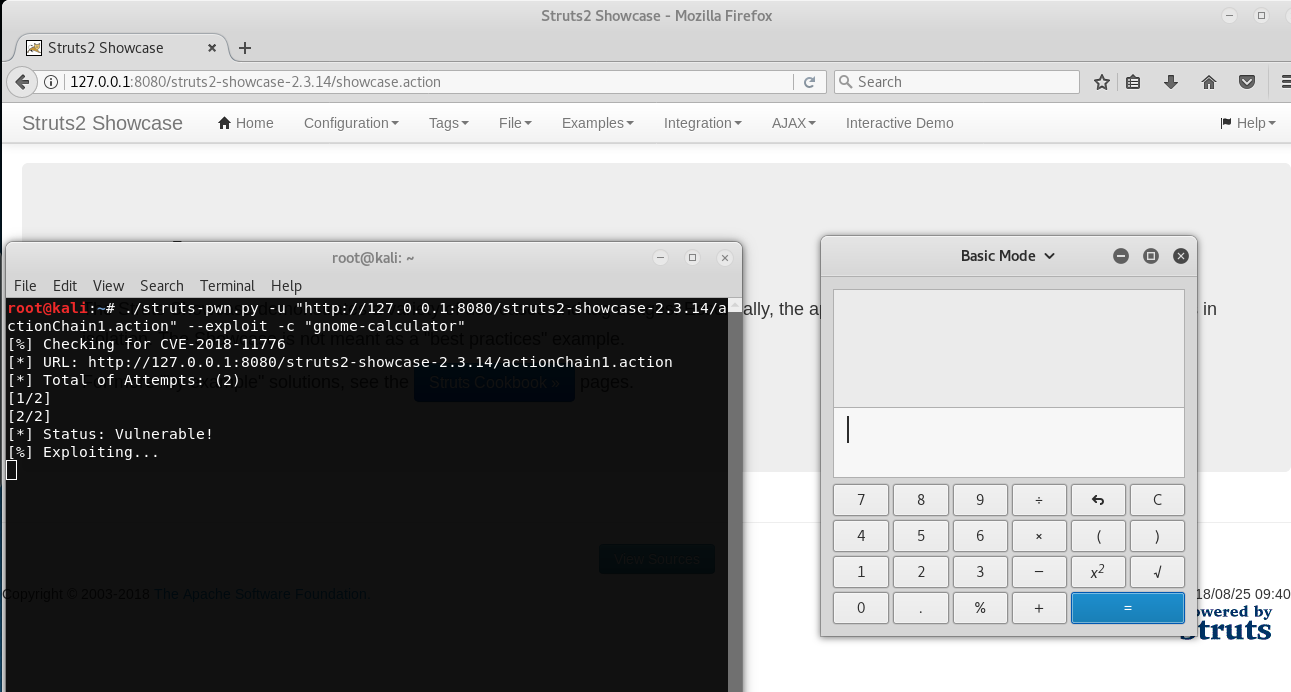 mazen160/struts-pwn_cve-2018-11776
An exploit for Apache Struts CVE-2018-11776
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
 opaxial/cve-2026-9830
CVE-2026-9830 Proof of Concept
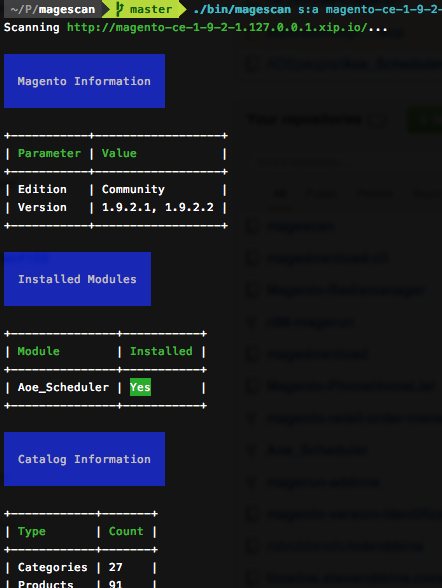 steverobbins/magescan
Scan a Magento site for information
 mrash/psad
psad: Intrusion Detection and Log Analysis with iptables
 johackim/docker-hacklab
My personal hacklab, create your own.
 s0md3v/parth
Heuristic Vulnerable Parameter Scanner
 liuk3r/cve-2023-32233
CVE-2023-32233: Linux内核中的安全漏洞
 teknogeek/ssrf-sheriff
A simple SSRF-testing sheriff written in Go








