
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
magescan — Scan a Magento site for information | Kitploit
Tools/GitHubGitHub/steverobbins/magescan
ReconnaissanceVulnerability ScannersInformation GatheringWeb Security
GitHubsteverobbins/magescan

magescan

Scan a Magento site for information

View Repository
459110377 years agoReviewed by Kitploit
Share

Mage Scan

Join the chat at https://gitter.im/steverobbins/magescan

Master Build Status Master Code Quality Master Code Coverage Latest Stable Version Master Dependancies

The idea behind this is to evaluate the quality and security of a Magento site you don't have access to. The scenario when you're interviewing a potential developer or vetting a new client and want to have an idea of what you're getting into.

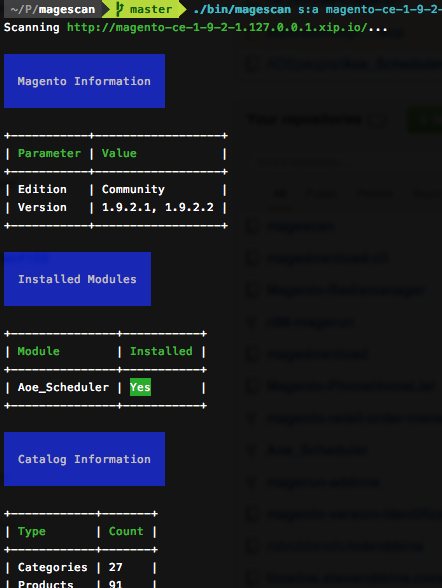
Screenshot

Installation

.phar

  • Download the magescan.phar file from the releases page
  • Run in command line with the php command
php magescan.phar scan:all www.example.com

Source

  • Clone this repository
  • Install with composer
git clone https://github.com/steverobbins/magescan magescan
cd magescan
curl -sS https://getcomposer.org/installer | php
php composer.phar install
bin/magescan scan:all www.example.com

n98-magerun

Clone into your ~/.n98-magerun/modules directory

mkdir -p ~/.n98-magerun/modules
git clone https://github.com/steverobbins/magescan ~/.n98-magerun/modules/magescan
magerun magescan:scan store.example.com

Composer

composer require steverobbins/magescan --dev

Include in your project

Add the following to your composer.json

"require": {
    "steverobbins/magescan": "dev-master"
}

Usage

$ magescan.phar scan:all store.example.com

Commands

scan:all

$ magescan.phar scan:all [--insecure|-k] [--show-modules] <url>

Run all scans on the given <url>.

Options

--format=FORMAT

Specify a different output format. Possible values:

  • default
  • json
--insecure, -k

If set, SSL certificates won't be validated

--show-modules

Lists all modules searched for, not just those found

scan:catalog

$ magescan.phar scan:catalog [--insecure|-k] <url>

Get catalog information

scan:modules

$ magescan.phar scan:modules [--insecure|-k] [--show-modules] <url>

Get installed modules

scan:patch

$ magescan.phar scan:patch [--insecure|-k] <url>

Get patch information

scan:server

$ magescan.phar scan:server [--insecure|-k] <url>

Check server technology

scan:sitemap

$ magescan.phar scan:sitemap [--insecure|-k] <url>

Check sitemap

scan:unreachable

$ magescan.phar scan:unreachable [--insecure|-k] <url>

Check unreachable paths

scan:version

$ magescan.phar scan:version [--insecure|-k] <url>

Get the version of a Magento installation

Show all modules that we tried to detect, not just those that were found

Disclaimer

Since we can't see the code base, this tool makes assumptions and takes guesses. Information reported isn't guaranteed to be correct.

For in depth analyses, consider:

  • mageaudit
  • Magento Project Mess Detector (for n98-magerun)
  • magniffer
  • Magento Coding Standard
  • magecheck
  • magento-check

Support

Please create an issue for all bugs and feature requests

Contributing

Fork this repository and send a pull request to the dev branch

License

Creative Commons Attribution 4.0 International

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →





