
 #1
Tools for identifying, assessing, and prioritizing security weaknesses in systems and applications.
Kitploit recommended

 datasploit/datasploit
An #OSINT Framework to perform various recon techniques on Companies, People, Phone Number, Bitcoin Addresses, etc., aggregate all the raw data, and…
 xoreaxeaxeax/skitter-creek-bath-salts
Unlocking _everything_ on the CPU with DRAM scrambling
 wgpsec/aboutsecurity
Everything for pentest. | 渗透测试知识库,以 AI Agent 可执行的格式沉淀安全方法论。
 danmcinerney/xsscrapy
XSS spider - 66/66 wavsep XSS detected
 lmacken/pyrasite
Inject code into running Python processes
 mandatoryprogrammer/xsshunter-express
An easy-to-setup version of XSS Hunter. Sets up in five minutes and requires no maintenance!
 sheeki03/tirith
Terminal security for developers and AI agents. Intercepts homograph URLs, pipe-to-shell, ANSI injection, obfuscated payloads, data exfiltration, and…
 moham3driahi/xattacker
X Attacker Tool ☣ Website Vulnerability Scanner & Auto Exploiter
 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
 ajinabraham/nodejsscan
nodejsscan is a static security code scanner for Node.js applications.
 cr0hn/dockerscan
The Most Comprehensive Docker Security Scanner
 diego-treitos/linux-smart-enumeration
Linux enumeration tool for pentesting and CTFs with verbosity levels
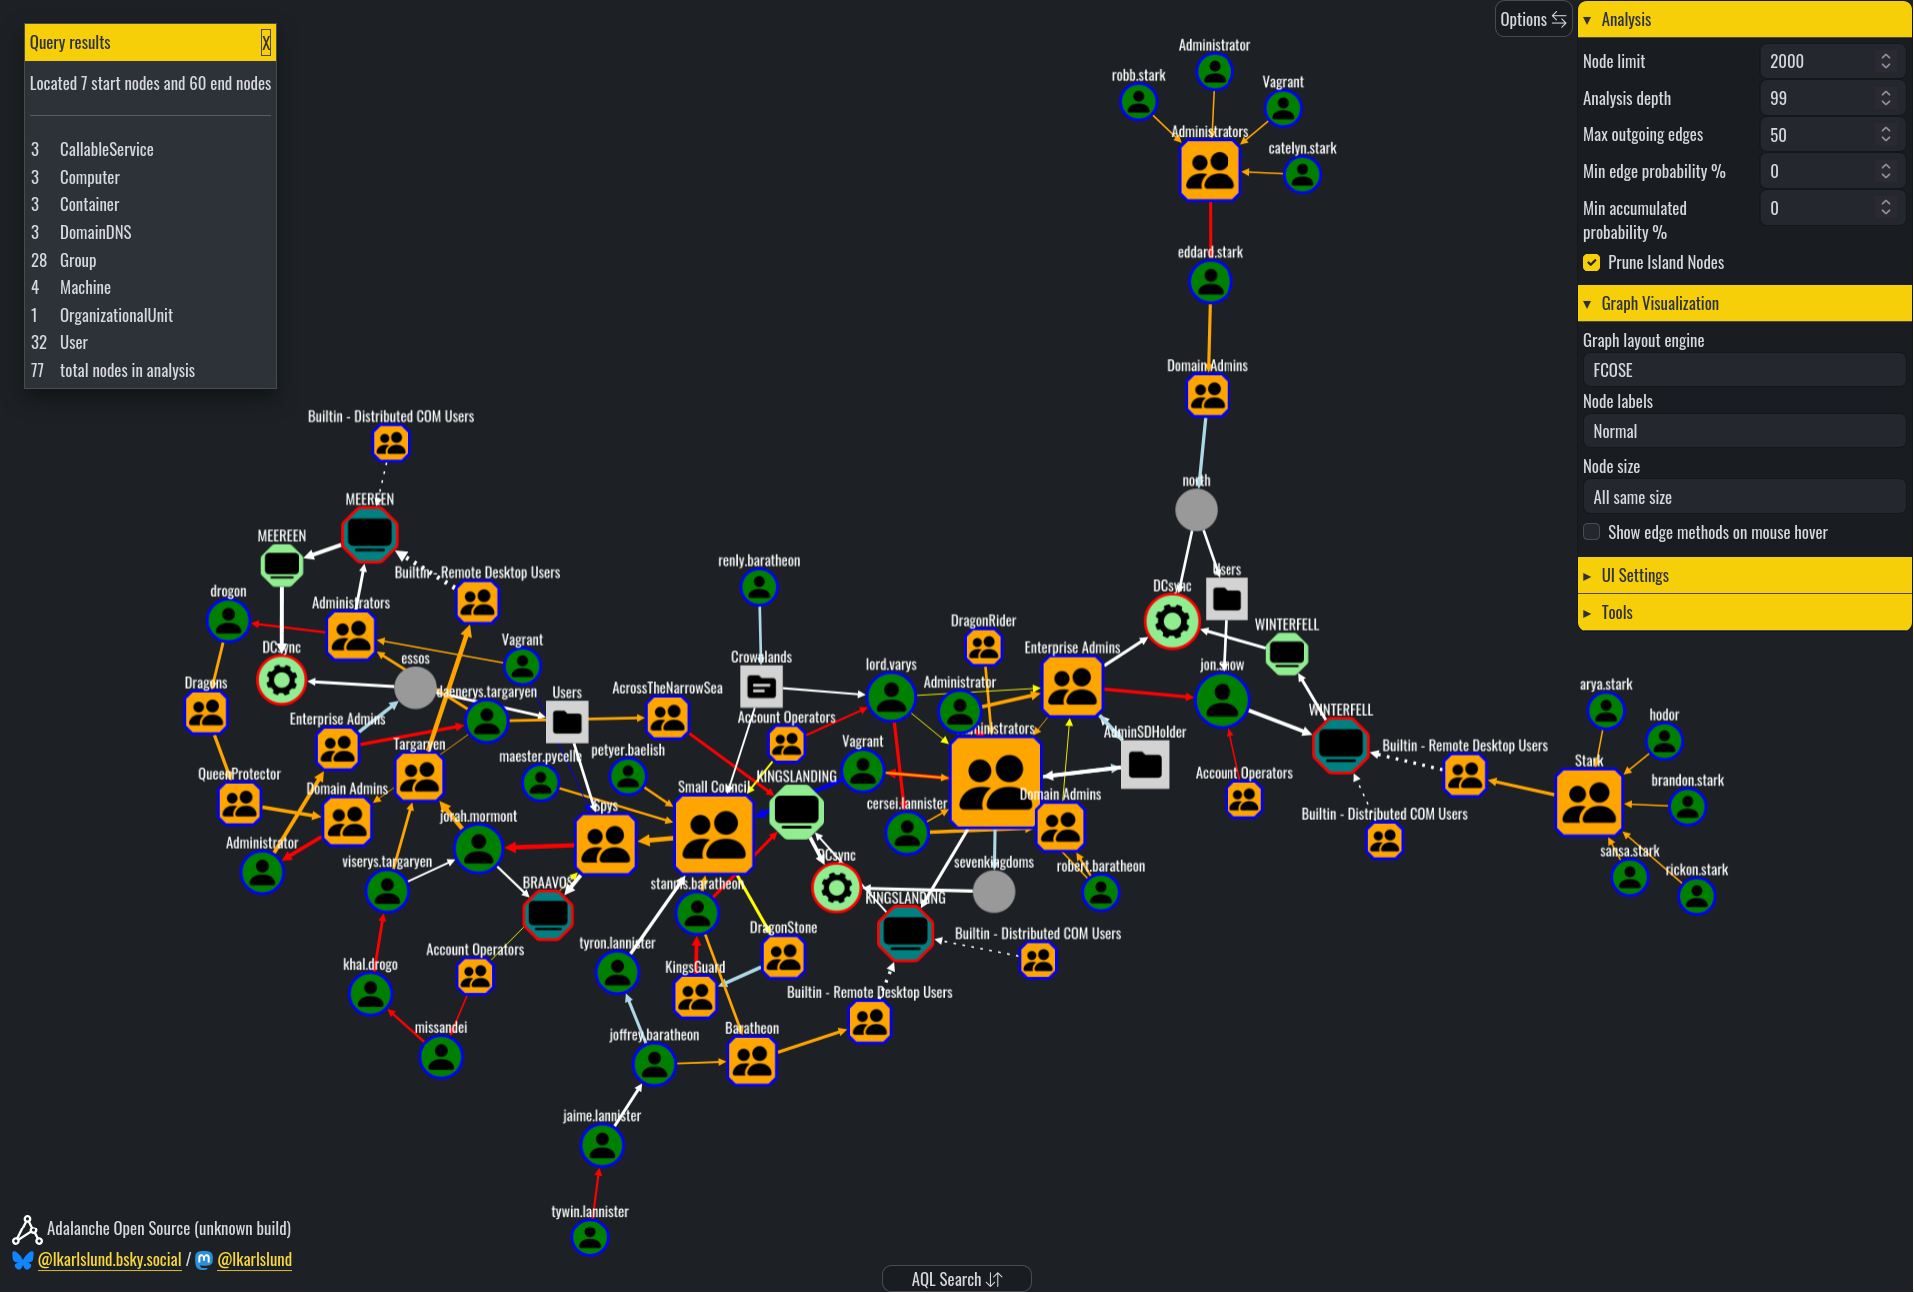 lkarlslund/adalanche
Attack Graph Visualizer and Explorer (Active Directory) ...Who's *really* Domain Admin?
 epinna/weevely3
Weaponized web shell
 aress31/burpgpt
A Burp Suite extension that integrates OpenAI's GPT to perform an additional passive scan for discovering highly bespoke vulnerabilities and enables…
 salesforce/policy_sentry
Generates least-privilege AWS IAM policies based on resource ARNs and access levels, automating secure policy creation for cloud infrastructure.
 xiphosresearch/exploits
Miscellaneous exploit code
 sap/macos-enterprise-privileges
This application gives Mac users in enterprise environments control over the administration of their machines by elevating their access level to…








