
 #1
Tools for identifying, assessing, and prioritizing security weaknesses in systems and applications.
Kitploit recommended

 bugcrowd/hunt
Flags parameters commonly associated with injection, SSRF, path traversal, IDOR, and SSTI, via passive Burp/ZAP scanning; also organizes manual…
 owasp/nodegoat
The OWASP NodeGoat project provides an environment to learn how OWASP Top 10 security risks apply to web applications developed using Node.js and how…
 vanhoefm/krackattacks-scripts
Scripts to verify WPA2 clients and APs for KRACK key reinstallation vulnerabilities using modified hostapd and monitor-mode frame replay.
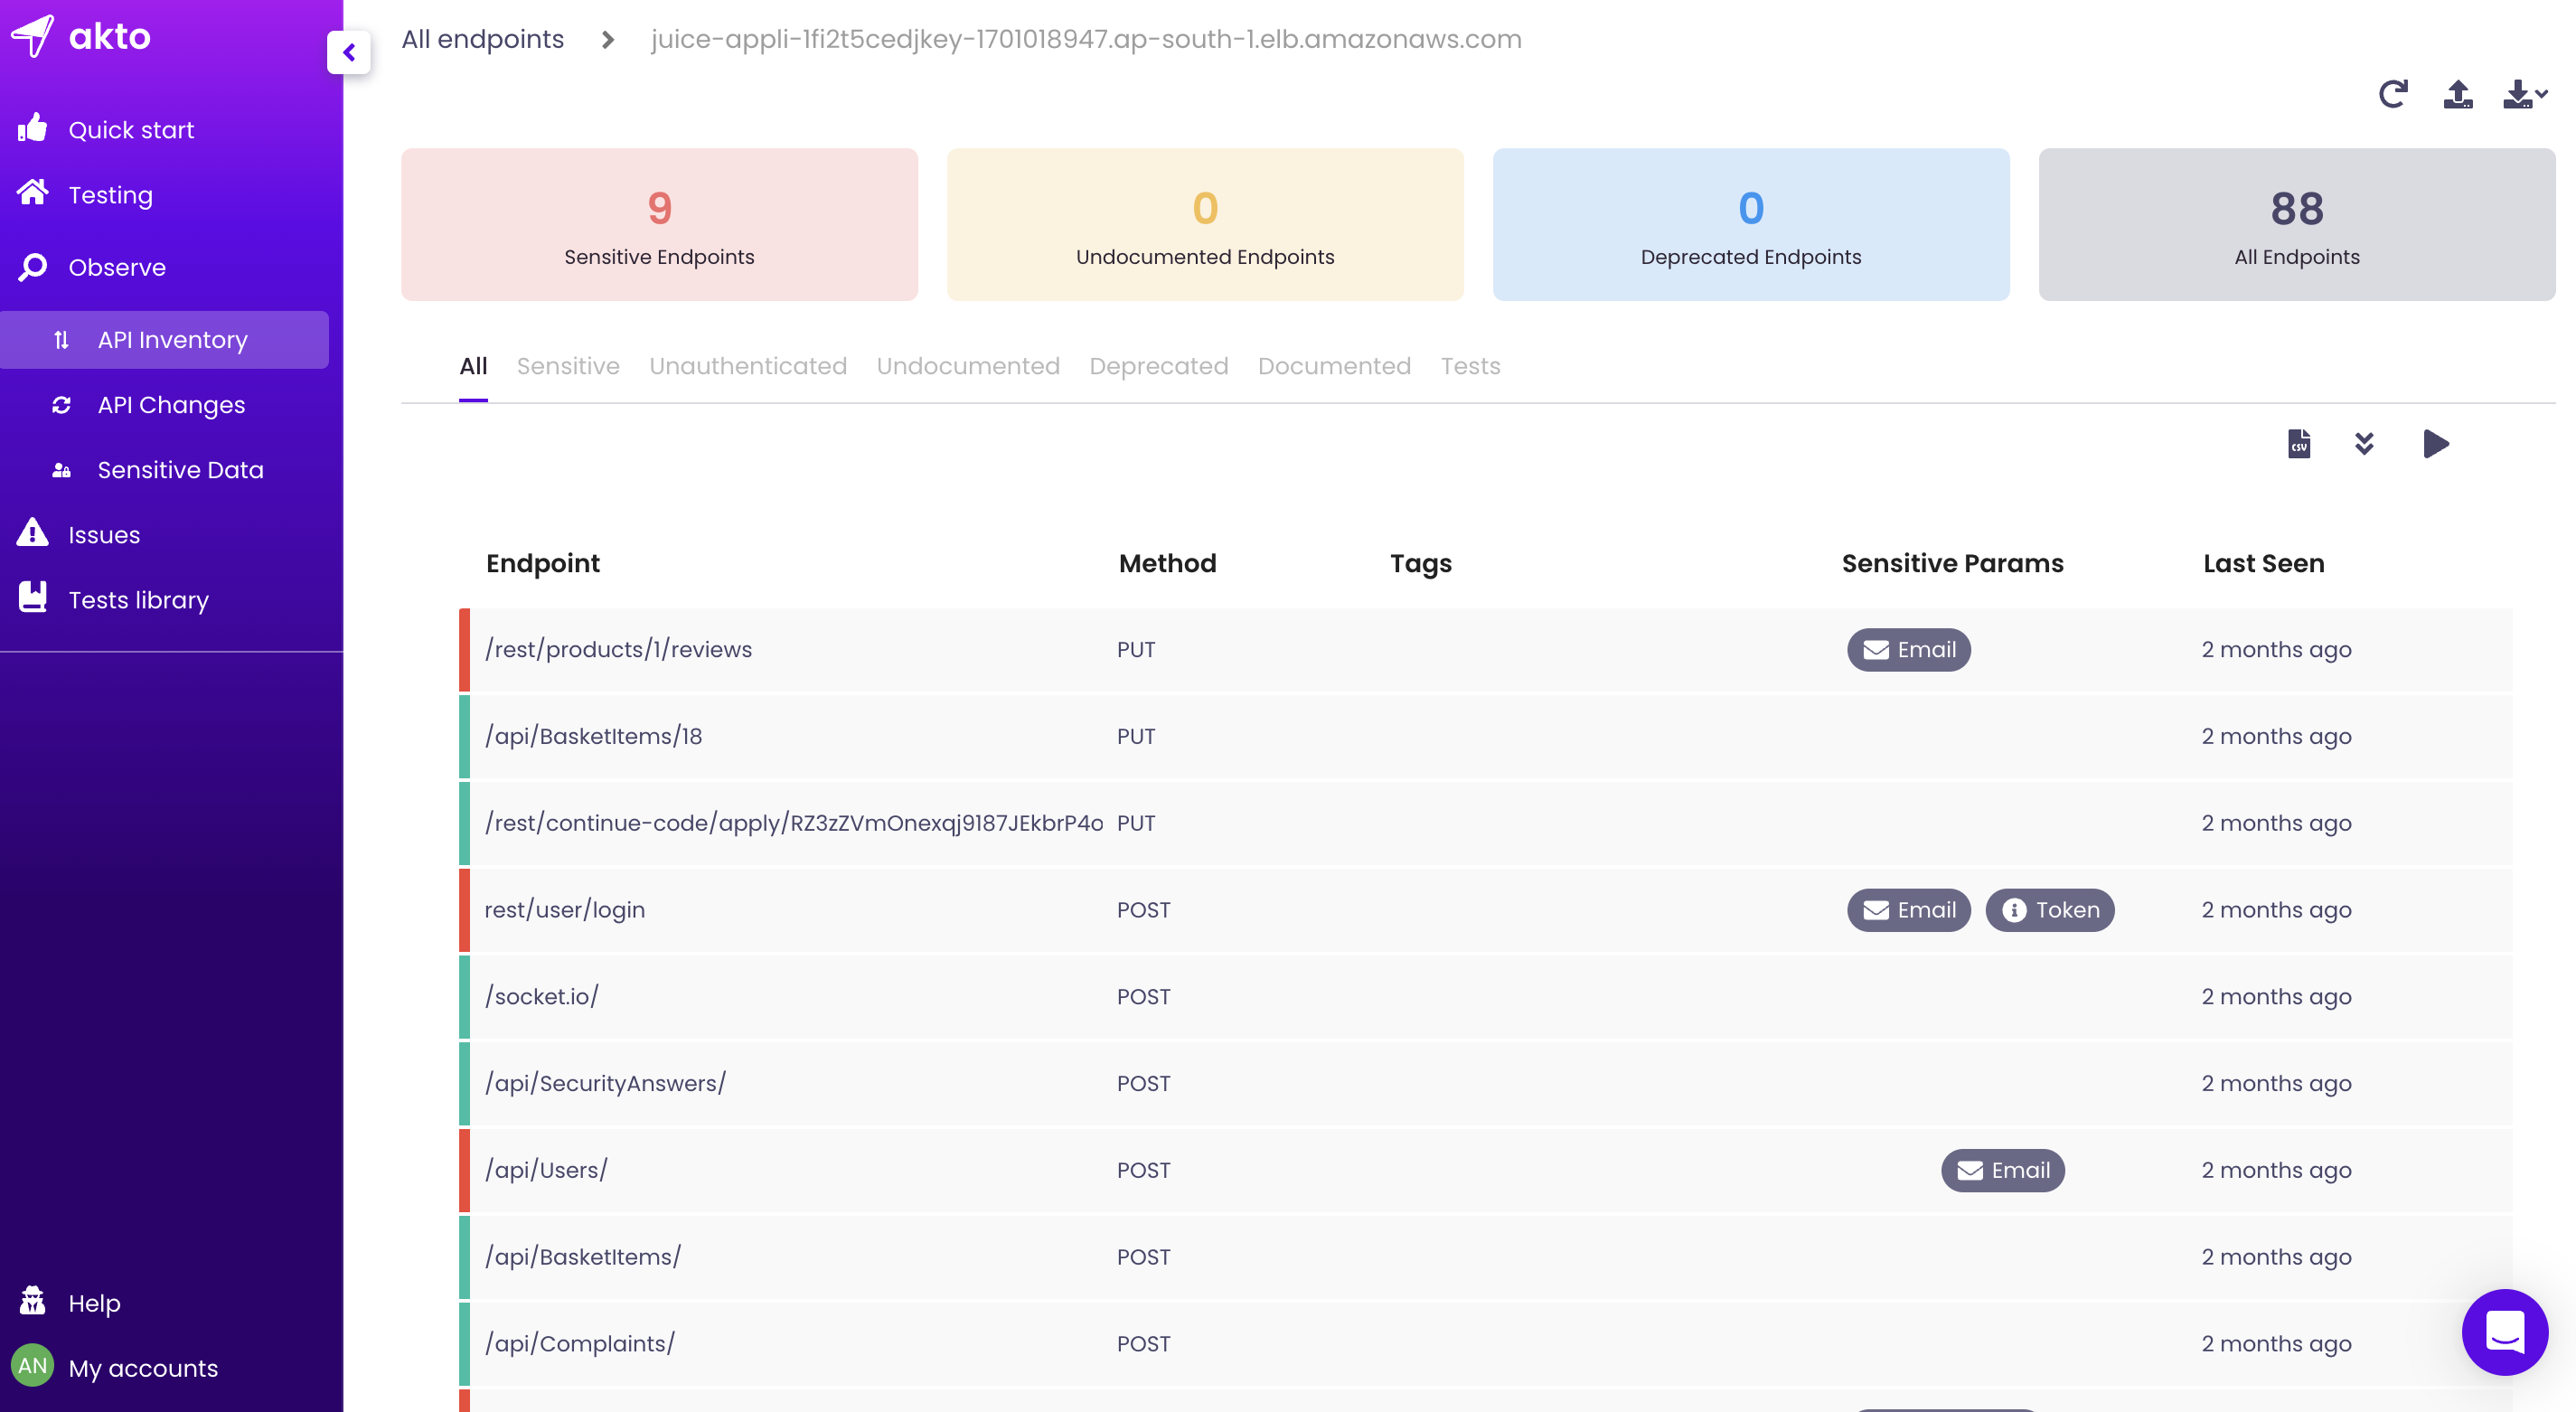 akto-api-security/akto
Open-source API security platform for continuous API discovery, vulnerability testing, and runtime threat detection. Integrates with CI/CD pipelines…
 hengyoush/kyanos
Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…
 comodosecurity/openedr
Open EDR public repository
 attify/firmware-analysis-toolkit
Firmware security research platform combining binary analysis, taint tracing, and emulation across IoT, edge AI, mobile devices, and robotics.
 tom0li/collection-document
Collection of quality safety articles. Awesome articles.
 bittentech/bug-bounty-beginner-roadmap
This is a resource factory for anyone looking forward to starting bug hunting and would require guidance as a beginner.
 lcvvvv/kscan
Multi-protocol port scanner with fingerprint recognition, service detection, and brute-force authentication testing. Supports 1200+ protocols, 10000+…
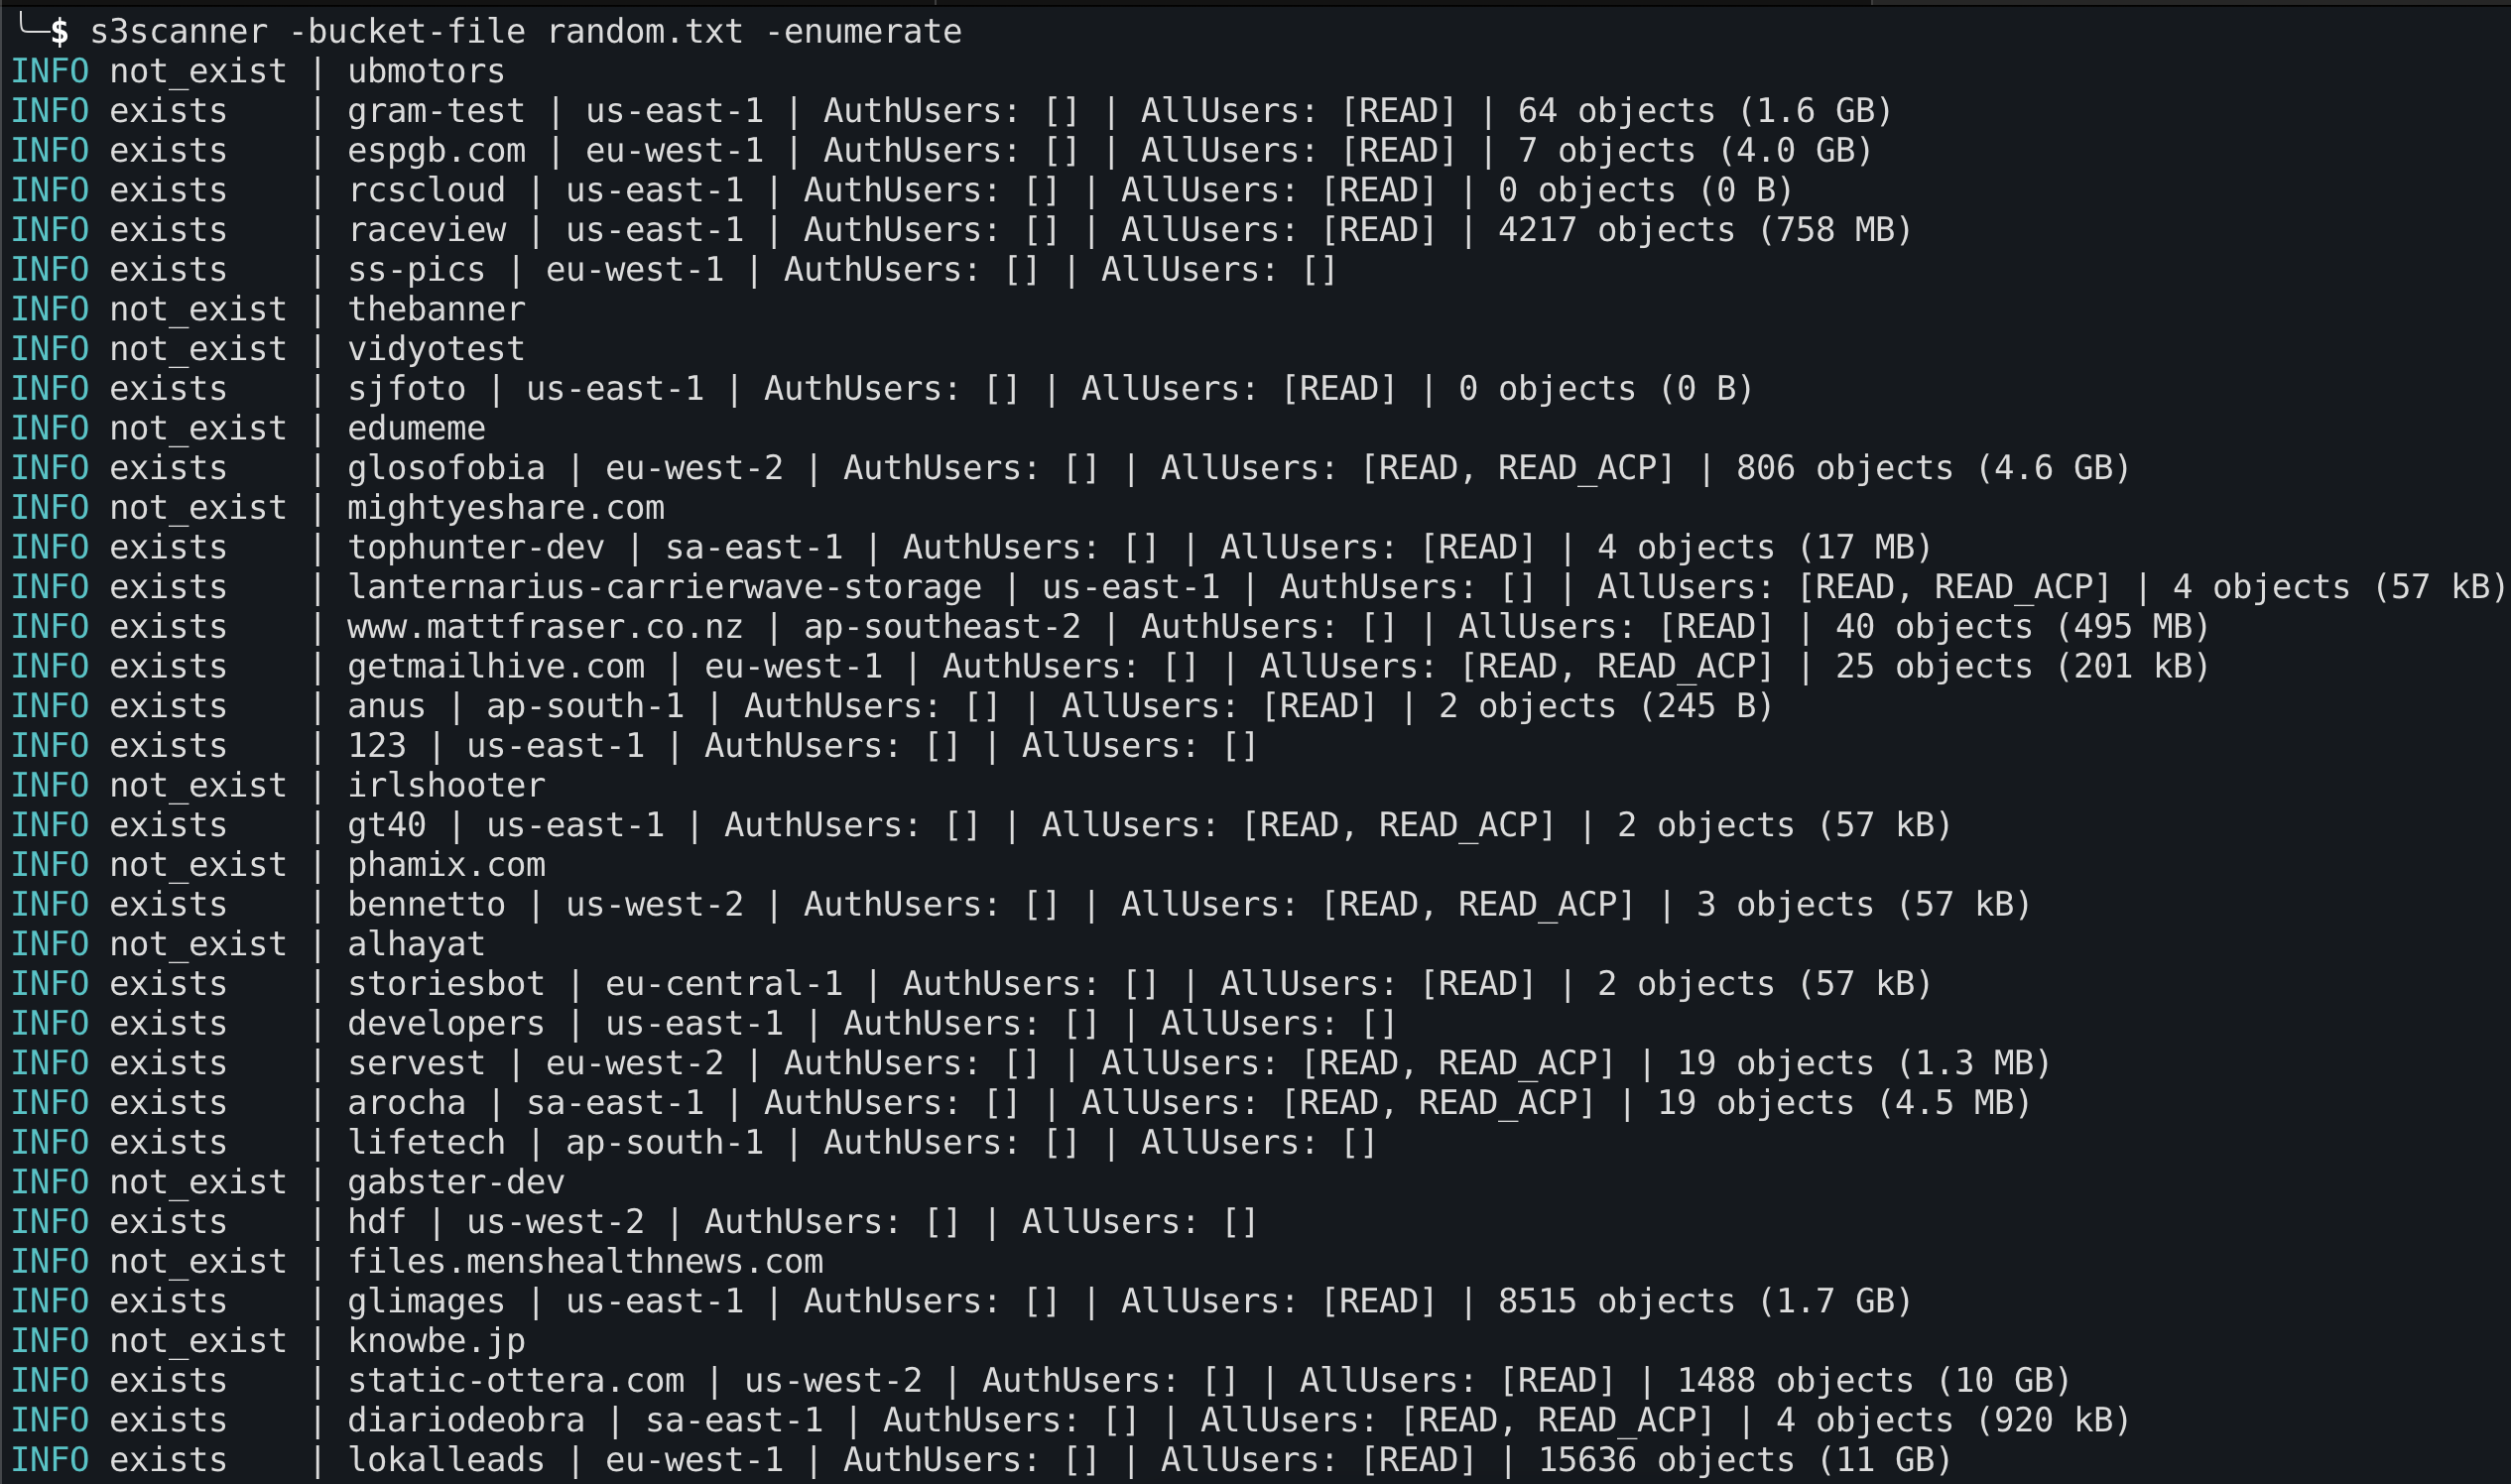 sa7mon/s3scanner
Scan for misconfigured S3 buckets across S3-compatible APIs!
 0xsteph/pentest-ai
Open-source AI pentester that proves every finding. Machine oracles re-run each exploit; verified bugs ship a proof capsule you can replay yourself.
 portswigger/turbo-intruder
High-speed Burp Suite extension for sending large volumes of HTTP requests with a custom stack, Python-based attack configuration, and advanced…
 sw33tlie/bbscope
Scope aggregation tool for HackerOne, Bugcrowd, Intigriti, YesWeHack, and Immunefi!
 s-rah/onionscan
OnionScan is a free and open source tool for investigating the Dark Web.
 openai/php2shell-checker
CLI that checks a website's PHP version or a local PHP binary against embedded patch cutoffs to determine php2shell vulnerability status, with JSON…
 rabbitmask/weblogicscan
Automated vulnerability scanner for Oracle WebLogic Server, detecting historical CVEs including deserialization, SSRF, and arbitrary file upload with…
 linkedin/qark
Tool to look for several security related Android application vulnerabilities








