
 #1
Tools for identifying, assessing, and prioritizing security weaknesses in systems and applications.
Kitploit recommended
 mbechler/marshalsec
Java deserialization vulnerability exploitation tool with payload generators for multiple marshallers (Jackson, XStream, SnakeYAML) and JNDI…
 hasherezade/pe-bear
Portable Executable reversing tool with a friendly GUI
 13o-bbr-bbq/machine_learning_security
Source code about machine learning and security.
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 deepfence/threatmapper
Open Source Cloud Native Application Protection Platform (CNAPP)
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
 9bie/php2shell-bypass-aslr-exp
Pure-HTTP exploit achieving RCE on PHP 8.4.26 + Apache mod_php via session upload_progress heap leak, dangling pointer reuse, and ASLR bypass to call…
 niklasb/libc-database
Build a database of libc offsets to simplify exploitation
 opengrep/opengrep
🔎 Static code analysis engine to find security issues in code.
 yandex/gixy
Nginx configuration static analyzer
 opencve/opencve
Aggregate, filter, and track CVEs from multiple sources with team collaboration, custom dashboards, alerts, and AI-powered analysis for vulnerability…
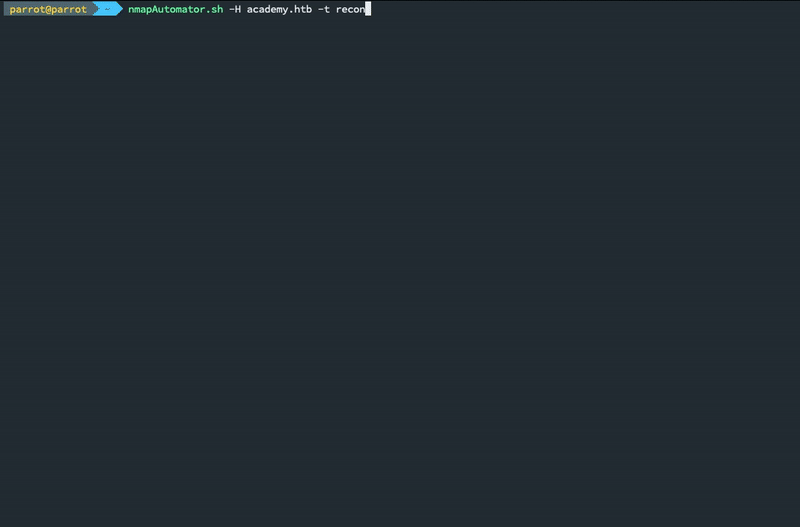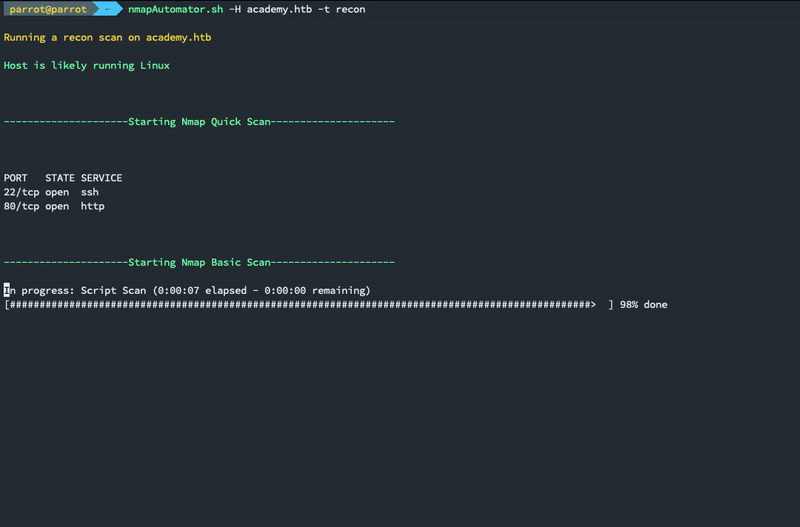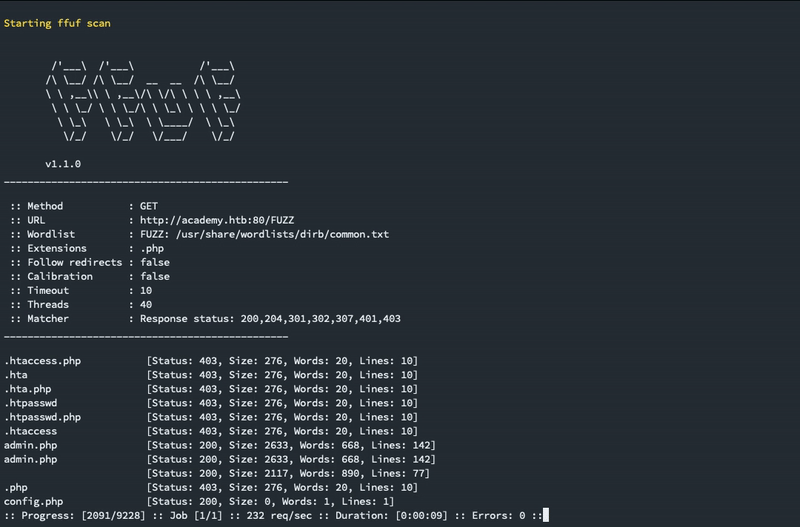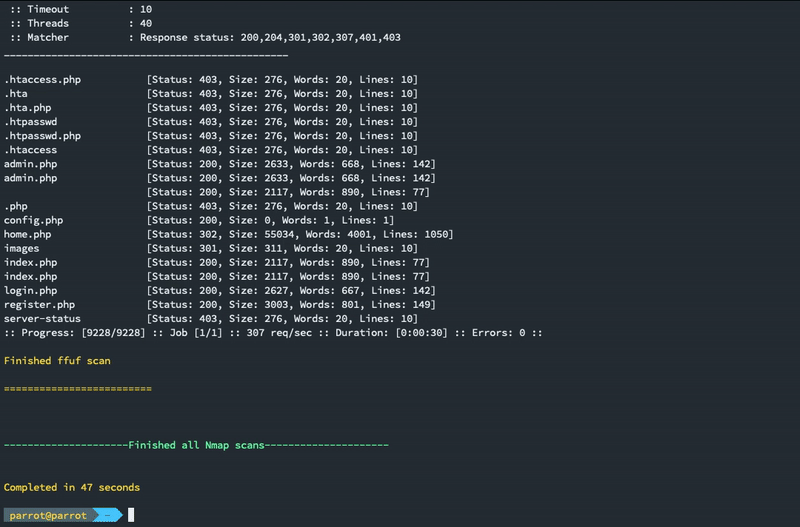 21y4d/nmapautomator
A script that you can run in the background!
 liamg/traitor
:arrow_up: :skull_and_crossbones: :fire: Automatic Linux privesc via exploitation of low-hanging fruit e.g. gtfobins, pwnkit, dirty pipe, +w…
 duo-labs/cloudmapper
CloudMapper helps you analyze your Amazon Web Services (AWS) environments.
 ticarpi/jwt_tool
:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens
 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…
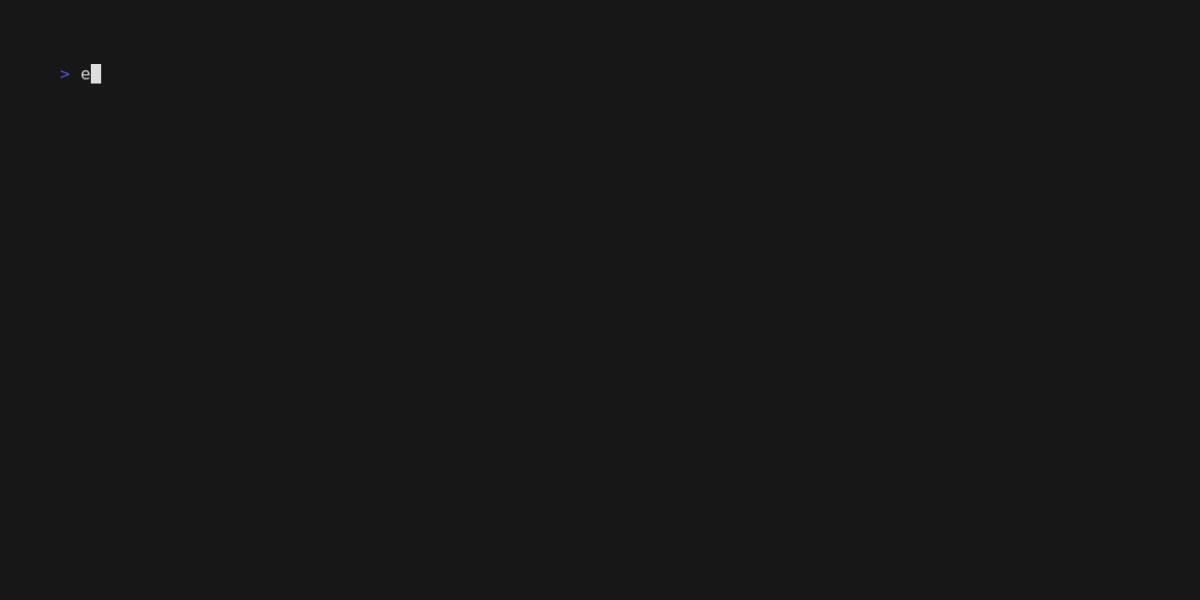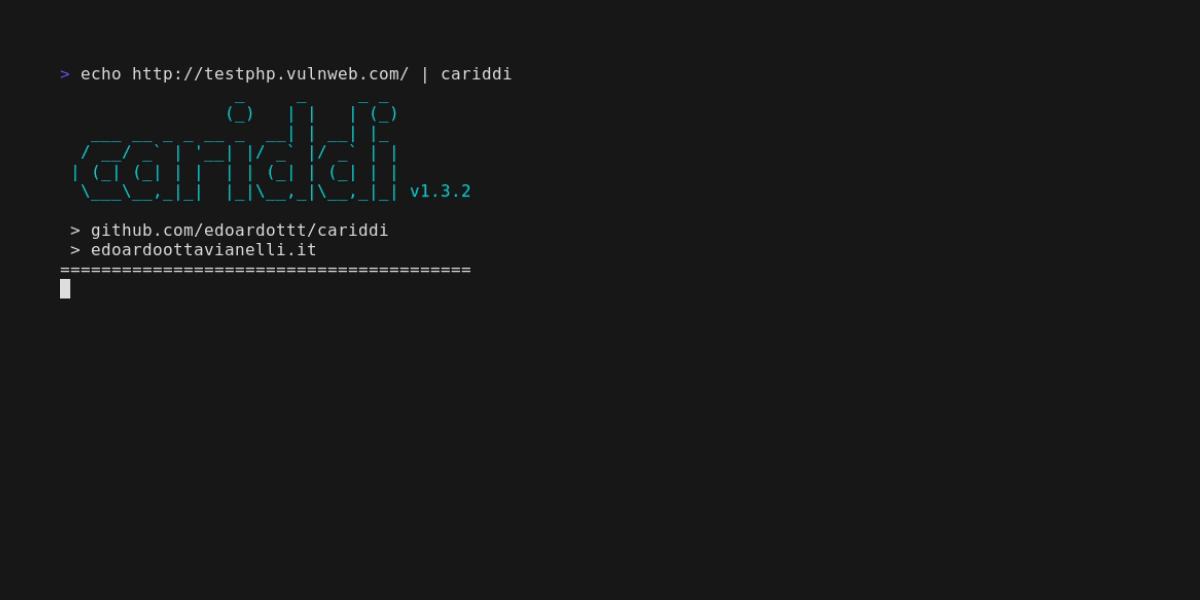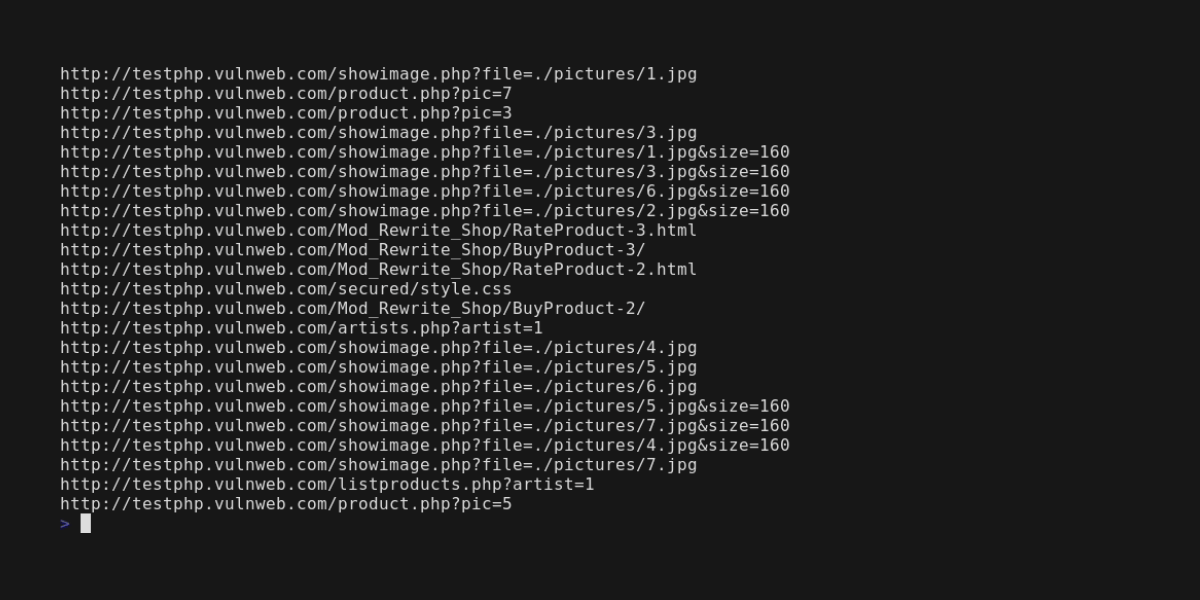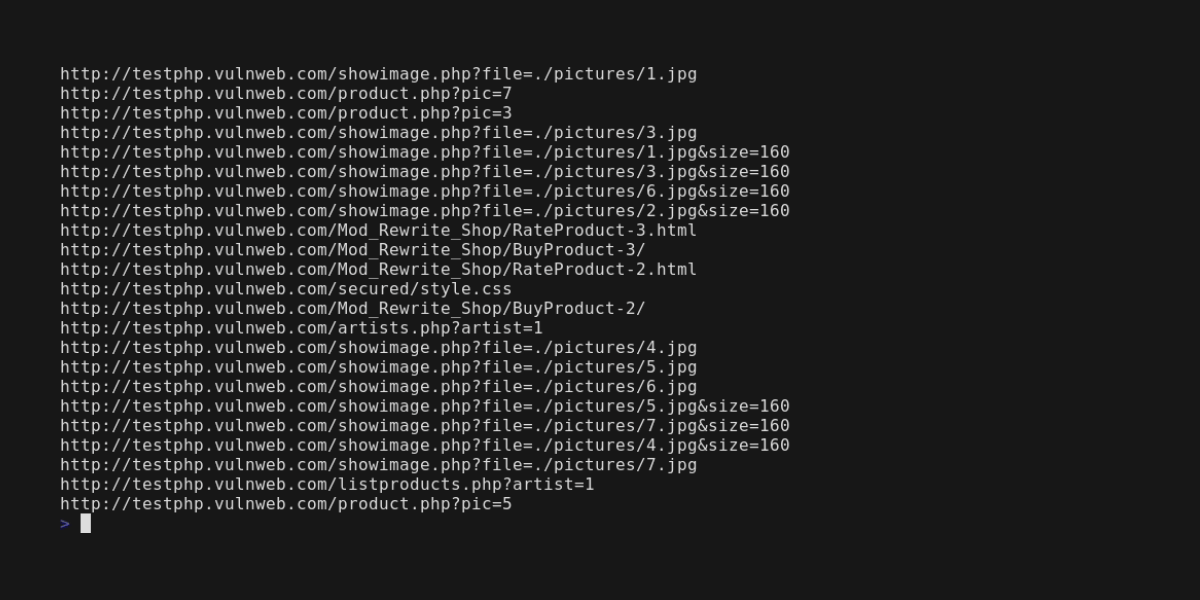 edoardottt/cariddi
Take a list of domains, crawl urls and scan for endpoints, secrets, api keys, file extensions, tokens and more
 projectdiscovery/public-bugbounty-programs
Community curated list of public bug bounty and responsible disclosure programs.








