
 #1
General-purpose tools, frameworks, and environments supporting various cybersecurity workflows and tasks.
Kitploit recommended

 shoucheng3/xwiki__xwiki-commons_cve-2023-29201_14-5
Technical libraries for XWiki projects, providing reusable components for vulnerability analysis, code analysis, and static analysis across…
 shoucheng3/xwiki__xwiki-commons_cve-2023-29528_14-9-rc-1
Generic Java utility libraries providing common technical components for the XWiki ecosystem, designed for reuse across various projects.
 shoucheng3/xwiki__xwiki-commons_cve-2023-31126_14-10-3
Java library providing technical commons for XWiki projects, with a focus on vulnerability analysis and static code inspection for security testing.
 shoucheng3/xwiki__xwiki-commons_cve-2023-36471_14-10-5
Technical Java libraries providing common utilities and components for the XWiki platform, including security vulnerability fixes and code analysis…
 shoucheng3/xwiki__xwiki-rendering_cve-2023-32070_14-5
Generic rendering system converting wiki syntax, HTML, and other formats into XHTML. Part of the XWiki platform, providing a flexible and extensible…
 shoucheng3/xwiki__xwiki-rendering_cve-2023-37908_14-10-3
Generic wiki/HTML rendering system that converts textual input between syntaxes (wiki, HTML, XHTML). This repository contains a patched version…
 shoucheng3/zeroturnaround__zt-zip_cve-2018-1002201_1-12
Java library providing convenience methods for ZIP archive manipulation, including packing, unpacking, entry iteration, transformation, and…
 skyshell20082008/cve-2019-0708-poc-hitting-path
It's only hitting vulnerable path in termdd.sys!!! NOT DOS
 spamscanner/url-regex-safe
Regular expression matching for URL's. Maintained, safe, and browser-friendly version of url-regex. Resolves CVE-2020-7661 for Node.js servers.
 tazxtazxedu/winre-fix
PowerShell script to fix WinRE/Recovery partition issues - KB5034441, KB5028997, CVE-2024-20666 Windows Update failures
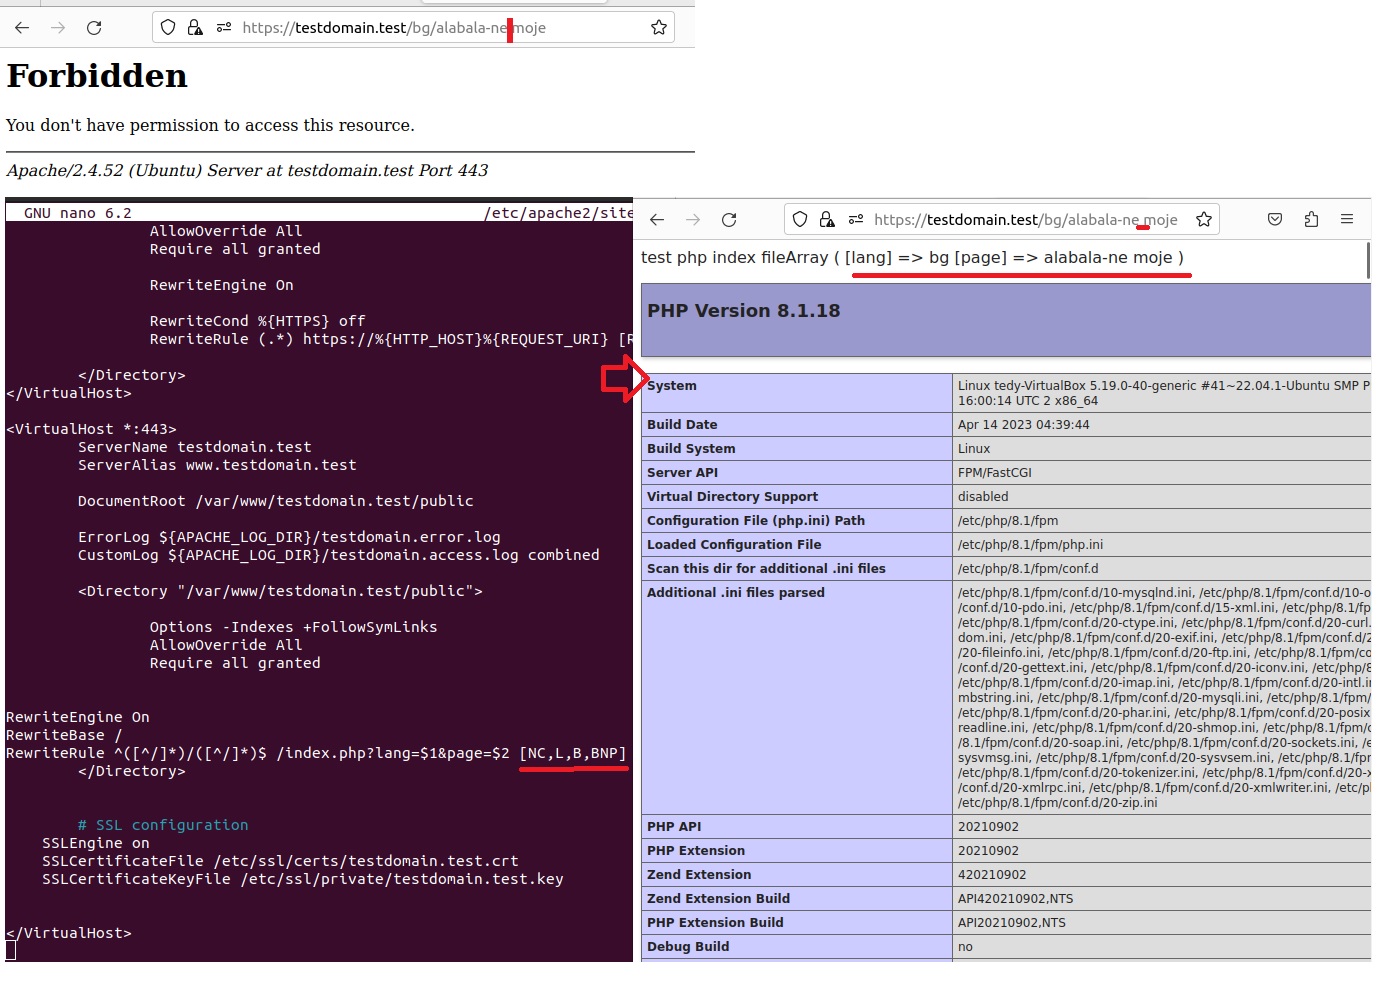 tbachvarova/linux-apache-fix-mod_rewrite-spaceinurl
Fix URL containing SPACES after Apache upgrade CVE-2023-25690
 tdawg506/mailenable-cve-2022-36934
Metasploit module for MailEnable CVE-2022-36934 authentication bypass RCE
 themmokhtar/cve-2020-0022
A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)
 tiagob0b/cve-2021-22005
Metasploit module for CVE-2021-22005 VMware vCenter arbitrary file upload vulnerability with proof-of-concept and remote code execution exploit.
 zoemurmure/cve-2023-21768-afd-for-winsock-eop-exploit
Local privilege escalation exploit for Windows Ancillary Function Driver (afd.sys) targeting CVE-2023-21768, with post-exploitation cleanup code.…
 uziii2208/cve-2025-33073
Universal exploitation tool for CVE-2025-33073 targeting Windows Domain Controllers with DNSAdmins privileges and WinRM enabled.
 vercel-labs/fix-react2shell-next
One command to fix CVE-2025-66478 (React 2 Shell RCE) in your Next.js / React RSC app.
 victor0013/cve-2019-0708
Scanner PoC for CVE-2019-0708 RDP RCE vuln








