
 #1
Tools for collecting, analyzing, and operationalizing threat feeds, indicators of compromise (IOCs), and attack trends.
Kitploit recommended
 browserbox/browserbox
💚🇺🇸🗽Secure remote browsing anywhere, any way you like it.
 opencve/opencve
Aggregate, filter, and track CVEs from multiple sources with team collaboration, custom dashboards, alerts, and AI-powered analysis for vulnerability…
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 elceef/dnstwist
Domain name permutation engine for detecting homograph phishing attacks, typo squatting, and brand impersonation
 jpcertcc/logontracer
Investigate malicious Windows logon by visualizing and analyzing Windows event log
 datadog/stratus-red-team
:cloud: :zap: Granular, Actionable Adversary Emulation for the Cloud
 elastic/protections-artifacts
Elastic Security detection content for Endpoint
 yeti-platform/yeti
Your Everyday Threat Intelligence
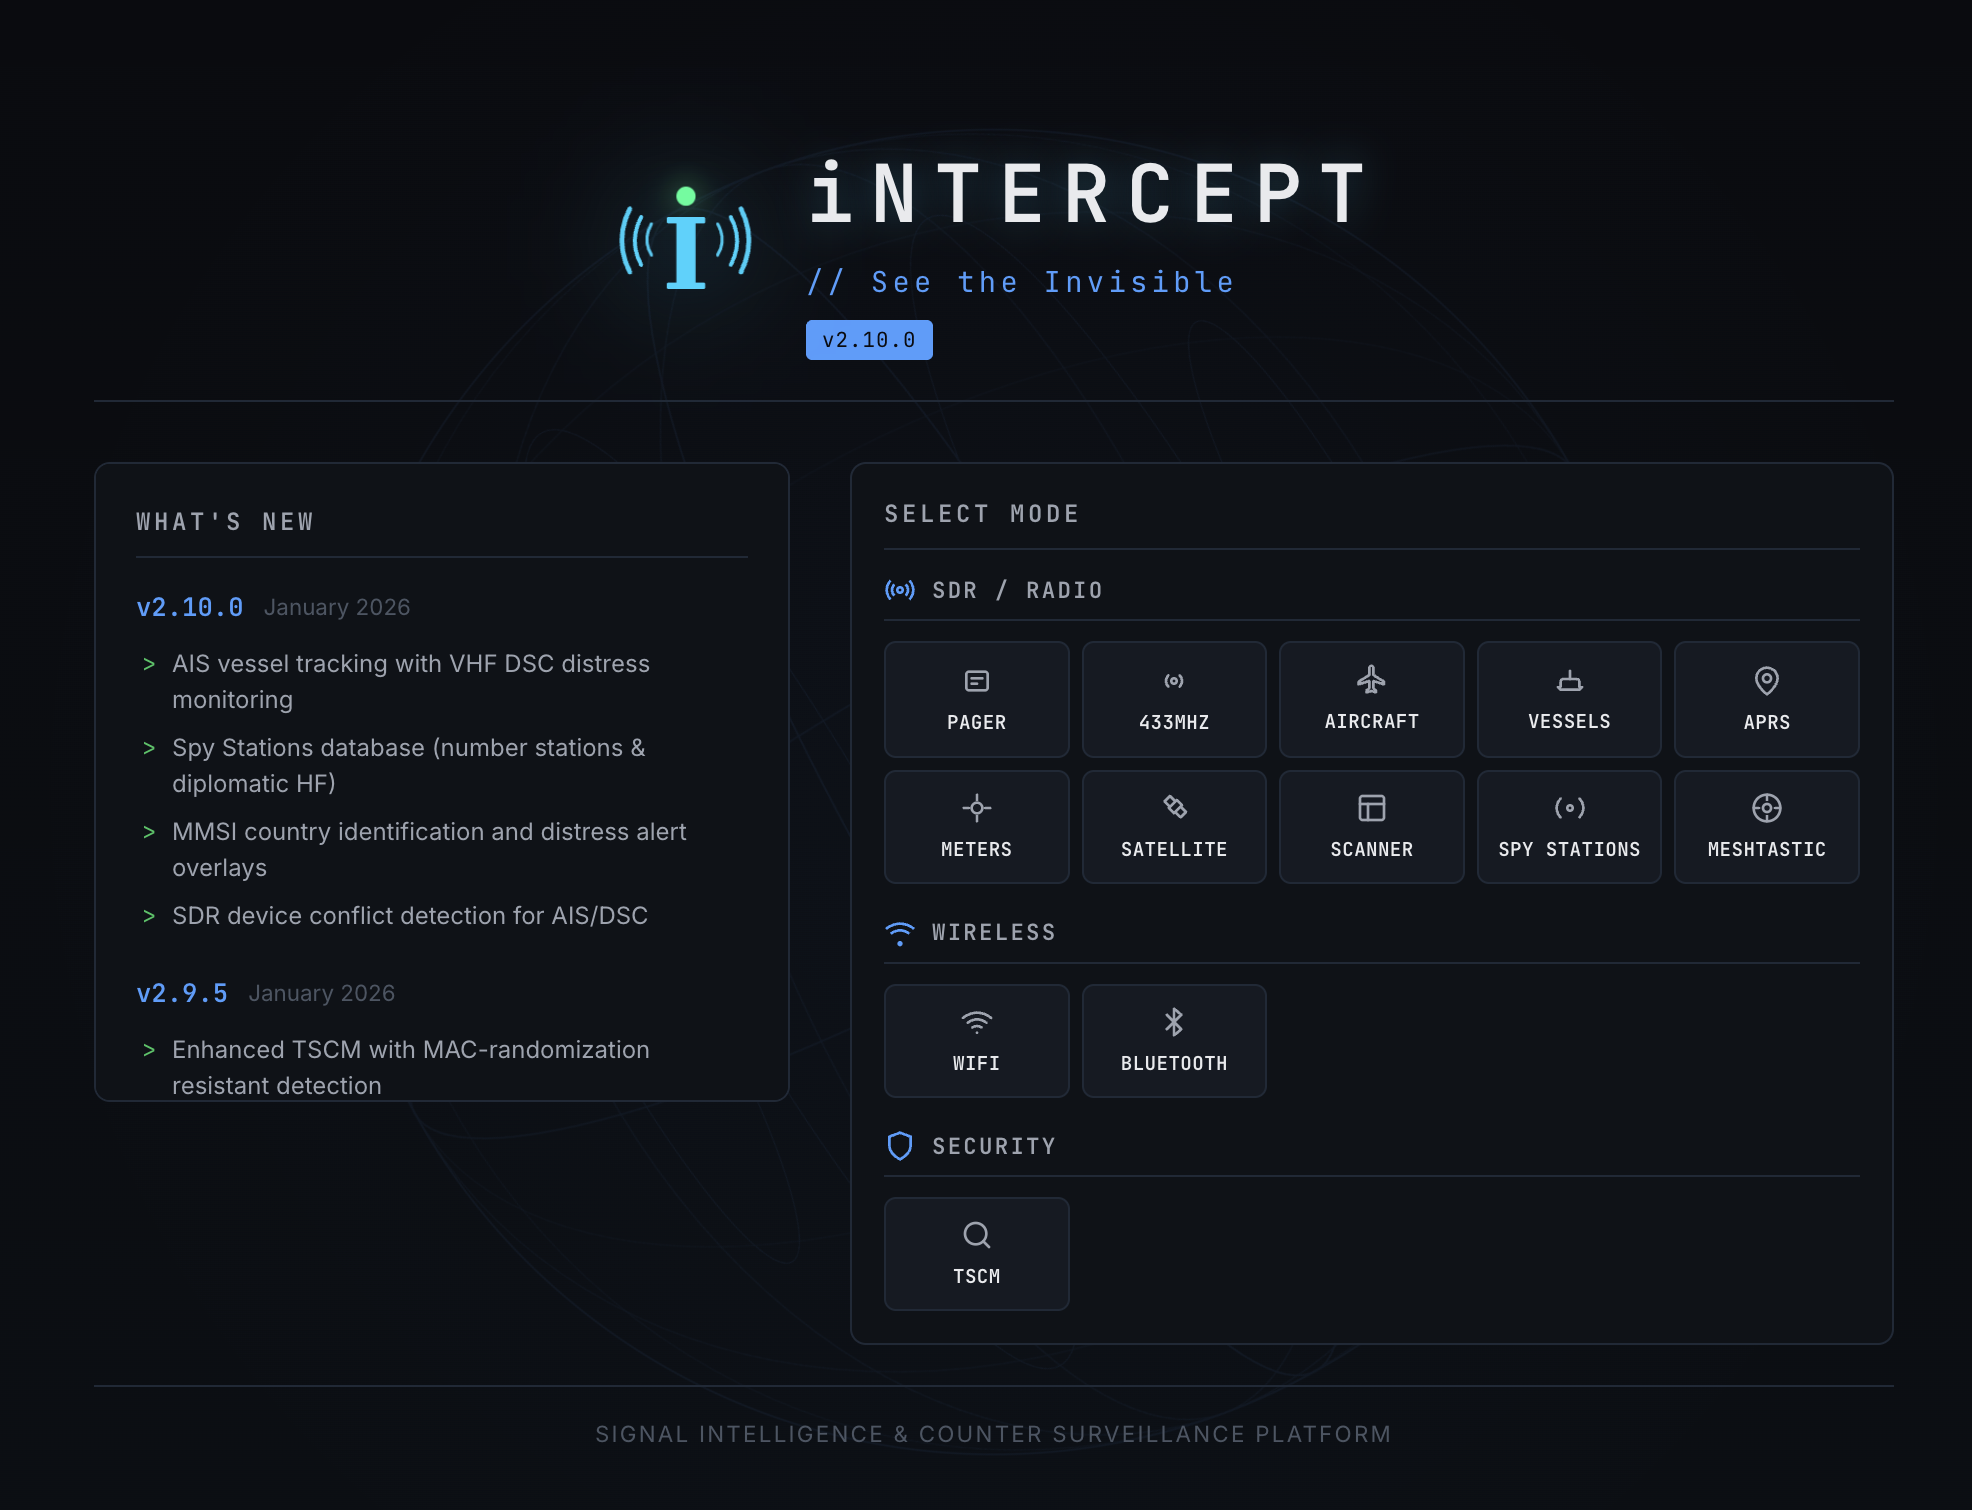 smittix/intercept
iNTERCEPT, a free and open-source platform that unites the best signal intelligence tools into a single, accessible interface.
 rabbitstack/fibratus
Security sensor for realtime threat detection and protection
 rabobank-cdc/dettect
Detect Tactics, Techniques & Combat Threats
 khast3x/h8mail
Email OSINT & Password breach hunting tool, locally or using premium services. Supports chasing down related email
 0xmarcio/pocindex
Search public CVE proof-of-concept exploits from GitHub, Nuclei, ExploitDB, Metasploit and Vulhub, with CVSS, EPSS and CISA KEV context.
 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
 beenuar/aisoc
Self-hostable AI SOC that fuses security alerts, auto-triages via agentic AI, runs MITRE ATT&CK investigations, and logs every agent decision in a…
 mikeroyal/digital-forensics-guide
Digital Forensics Guide. Learn all about Digital Forensics, Computer Forensics, Mobile device Forensics, Network Forensics, and Database Forensics.
 timb-machine/linux-malware
Tracking interesting Linux (and UNIX) malware. Send PRs
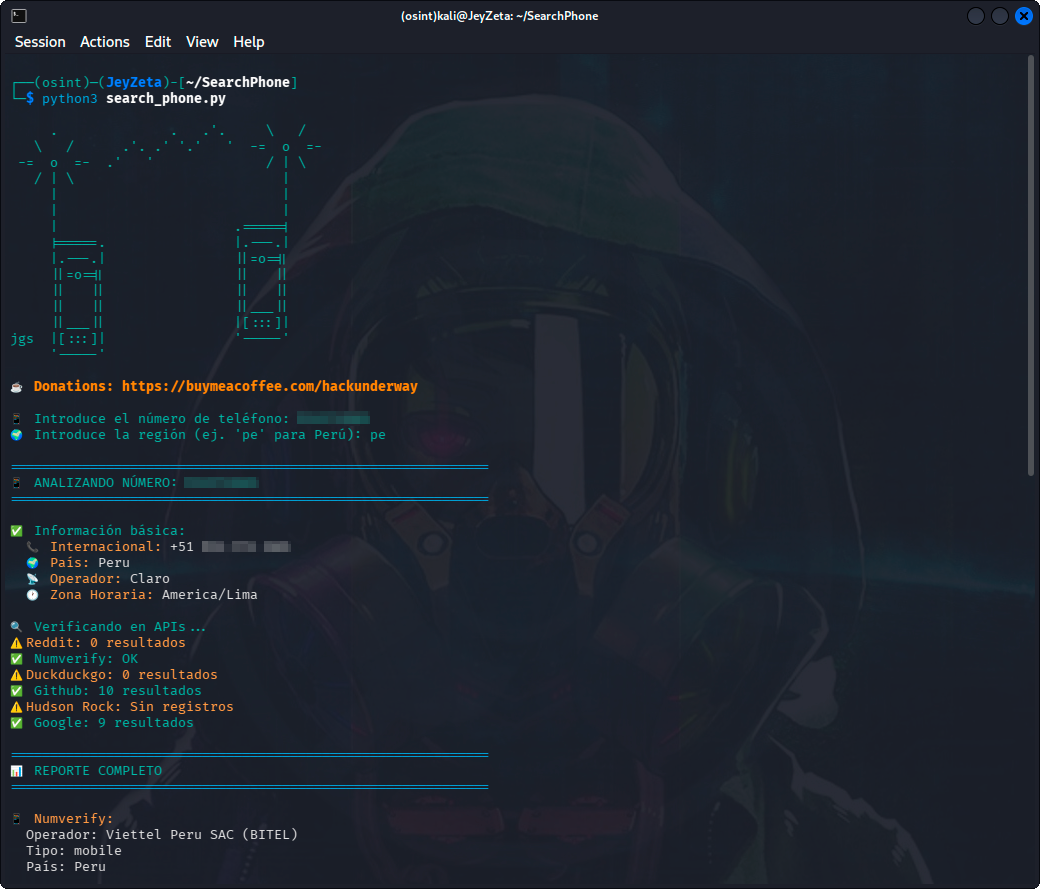 hackunderway/searchphone
Phone number OSINT toolkit with multi-API search (Google, GitHub, Numverify, Reddit, DuckDuckGo), Hudson Rock infostealer intelligence, and automatic…







