
 #1
Tools for collecting, analyzing, and operationalizing threat feeds, indicators of compromise (IOCs), and attack trends.
Kitploit recommended
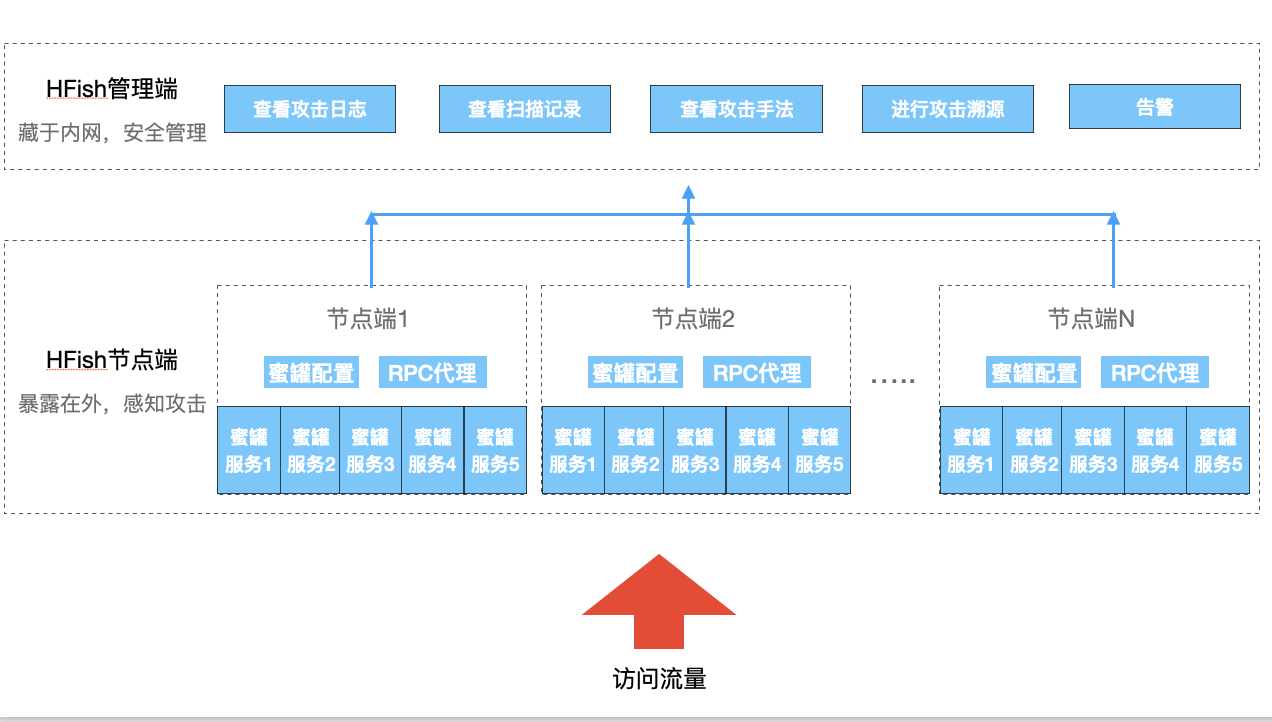
 hacklcx/hfish
Enterprise-grade honeypot system for detecting internal network breaches, external threats, and producing threat intelligence with 90+ service…
 nolabs-ai/nono
agent runtime security - zero trust, zero setup, zero latency agent sandboxing
 cveproject/cvelistv5
CVE cache of the official CVE List in CVE JSON 5 format
 divinelabio/argus
The Ultimate Information Gathering Toolkit
 cyb3rxp/awesome-soc
A curated knowledge base to build, run and mature a SOC (including CSIRT).
 jasonxtn/argus
The Ultimate Information Gathering Toolkit
 domcyrus/rustnet
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
 pavel-odintsov/fastnetmon
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support
 rspamd/rspamd
Spam filtering and email processing framework with regex rules, statistical analysis, custom Lua plugins, and external blocklists for MTA integration.
 google/osv.dev
Open source vulnerability DB and triage service.
 apurvsinghgautam/dark-web-osint-tools
OSINT Tools for the Dark Web
 withsecureopensource/chainsaw
Rapidly Search and Hunt through Windows Forensic Artefacts
 yamato-security/hayabusa
Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…
 cipher387/api-s-for-osint
List of API's for gathering information about phone numbers, addresses, domains etc
 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
 deepfence/threatmapper
Open Source Cloud Native Application Protection Platform (CNAPP)
 thinkst/opencanary
Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
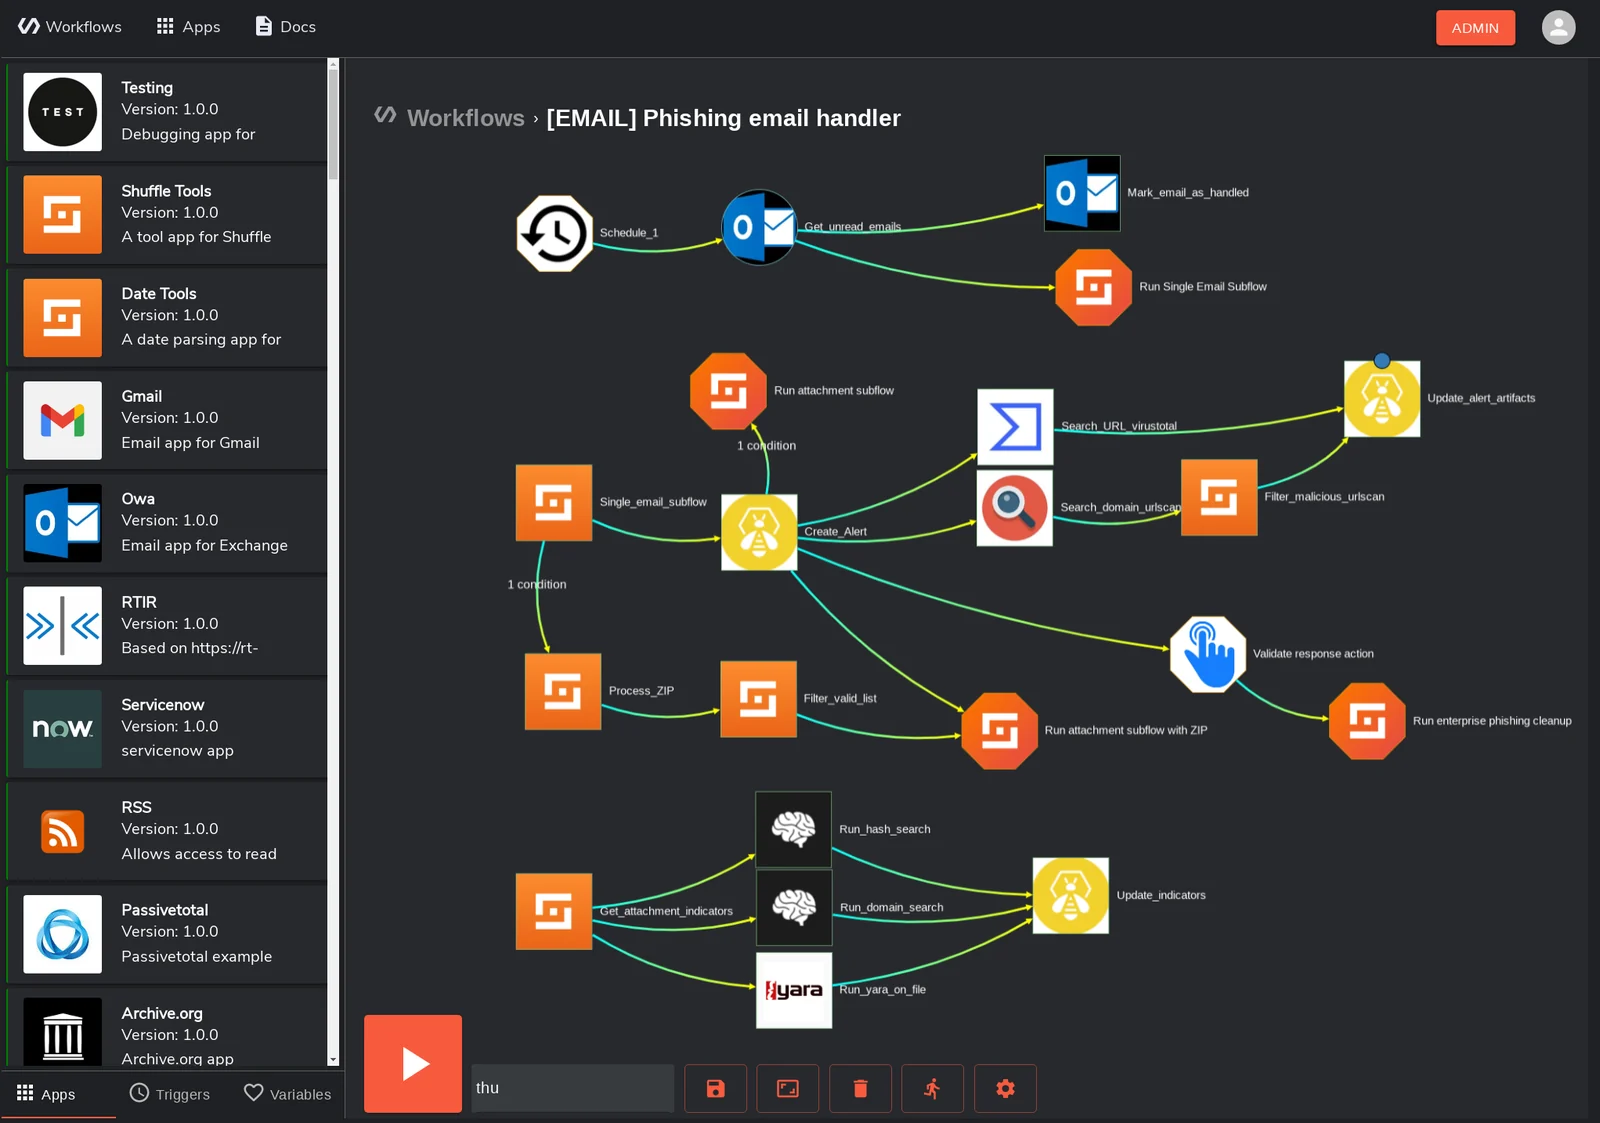 shuffle/shuffle
Open-source security orchestration, automation, and response (SOAR) platform with a visual workflow editor, prebuilt security app integrations, and…








