
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended
 8b-is/smart-tree
Smart Tree: not just a tree, a philosophy. A context-aware, AI-crafted replacement for 20+ tools with MEM8 quantum compression, semantic search,…
 arnica/depsguard
Harden your package manager configs against supply chain attacks.
 0sec-labs/foxguard
A fast universal code security scanner, written in Rust. Batteries included: supports 14 languages, TUI for triage, secrets, post-quantum audits,…
 appsecco/vulnerable-mcp-servers-lab
A collection of servers which are deliberately vulnerable to learn Pentesting MCP Servers.
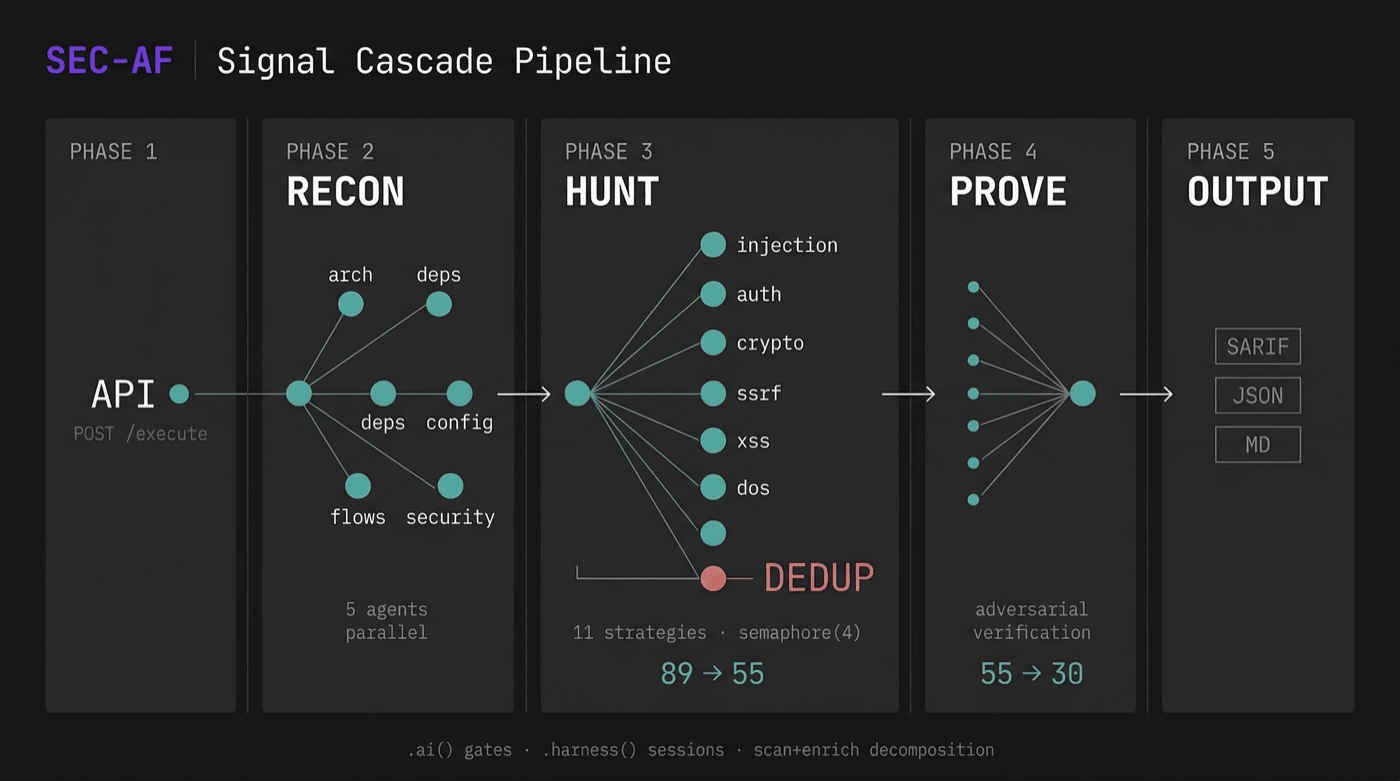 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
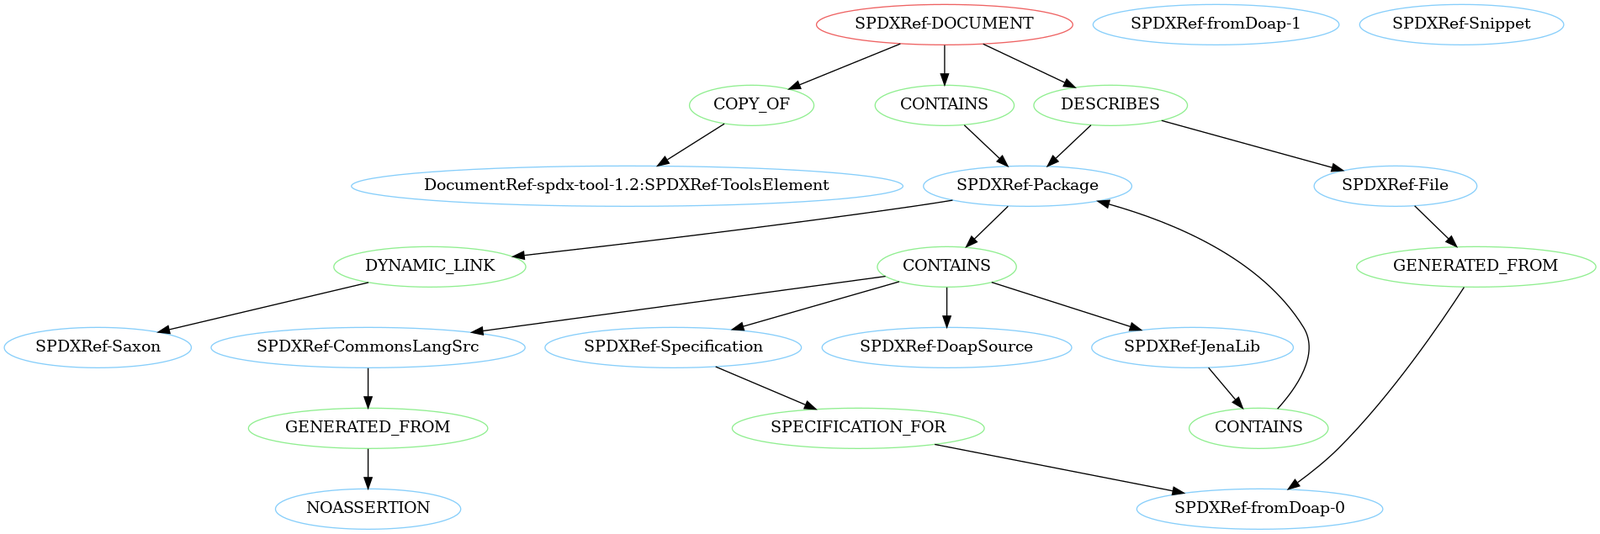 spdx/tools-python
A Python library to parse, validate and create SPDX documents.
 binarly-io/supplychainattacks
Curated repository of documented firmware supply chain attacks, featuring IoCs, detection tools, and references to help defenders understand and…
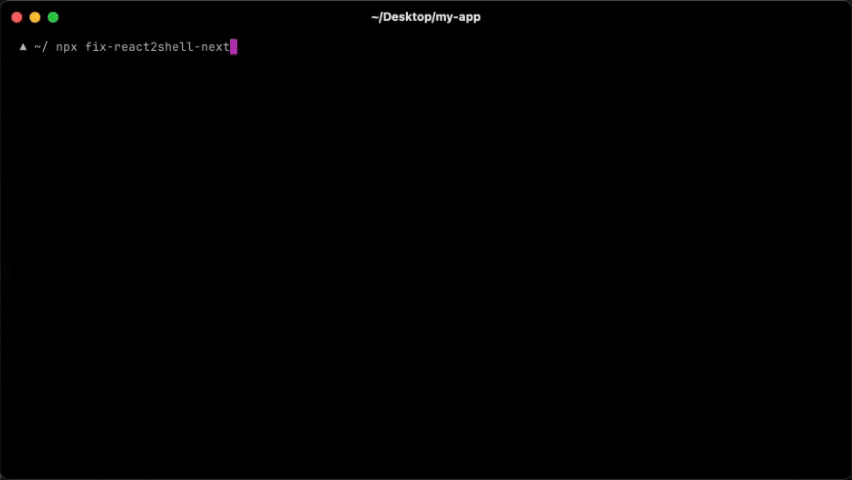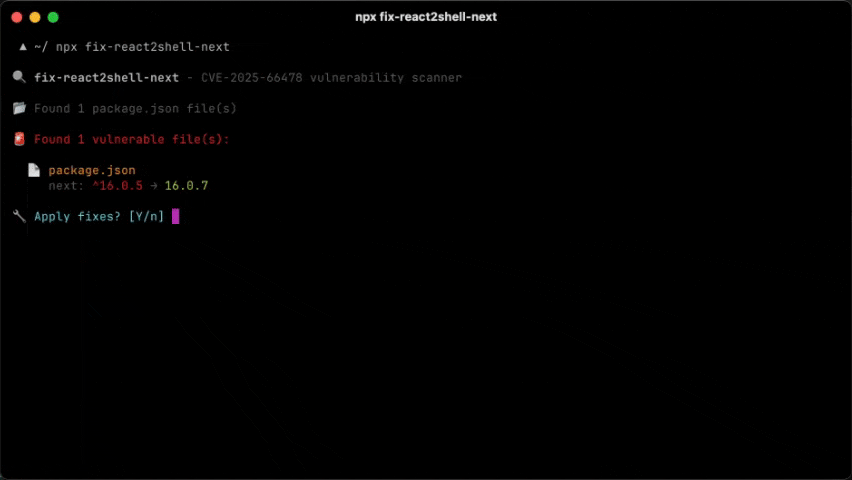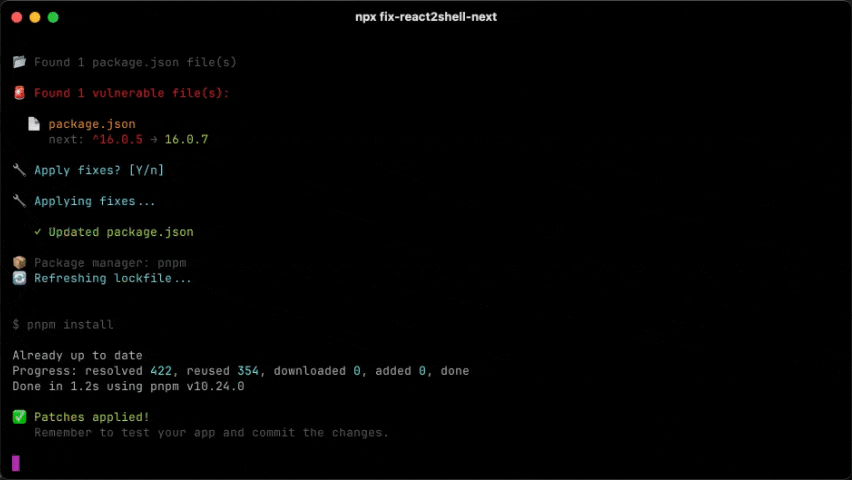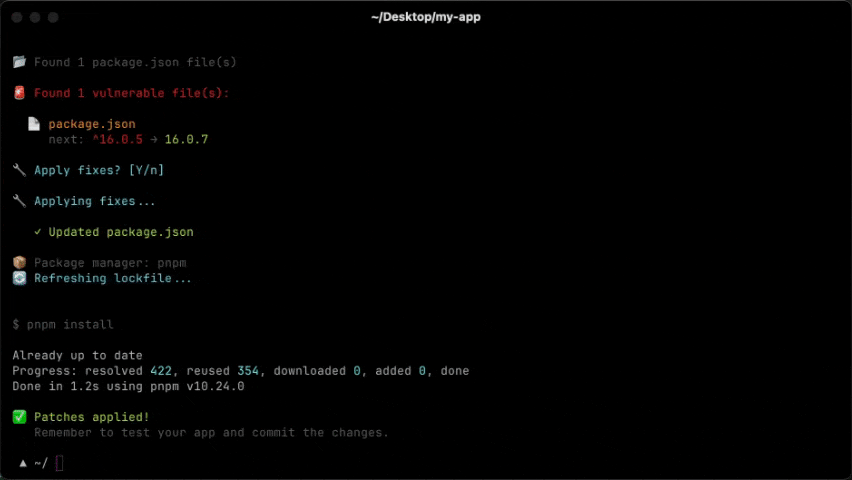 vercel-labs/fix-react2shell-next
One command to fix CVE-2025-66478 (React 2 Shell RCE) in your Next.js / React RSC app.
 projectdiscovery/depx
Malicious package & supply-chain intelligence
 node9-ai/node9-proxy
IAM for your AI agents. Set what Claude Code, Codex, Gemini, Cursor and any MCP server are allowed to do, review risky actions before they run, and…
 justinsteven/advisories
Personal repository of security advisory disclosures covering vulnerabilities in web, cloud, infrastructure, and open-source software.
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
 nccgroup/tpmgenie
TPM Genie is an I2C bus interposer for discrete Trusted Platform Modules
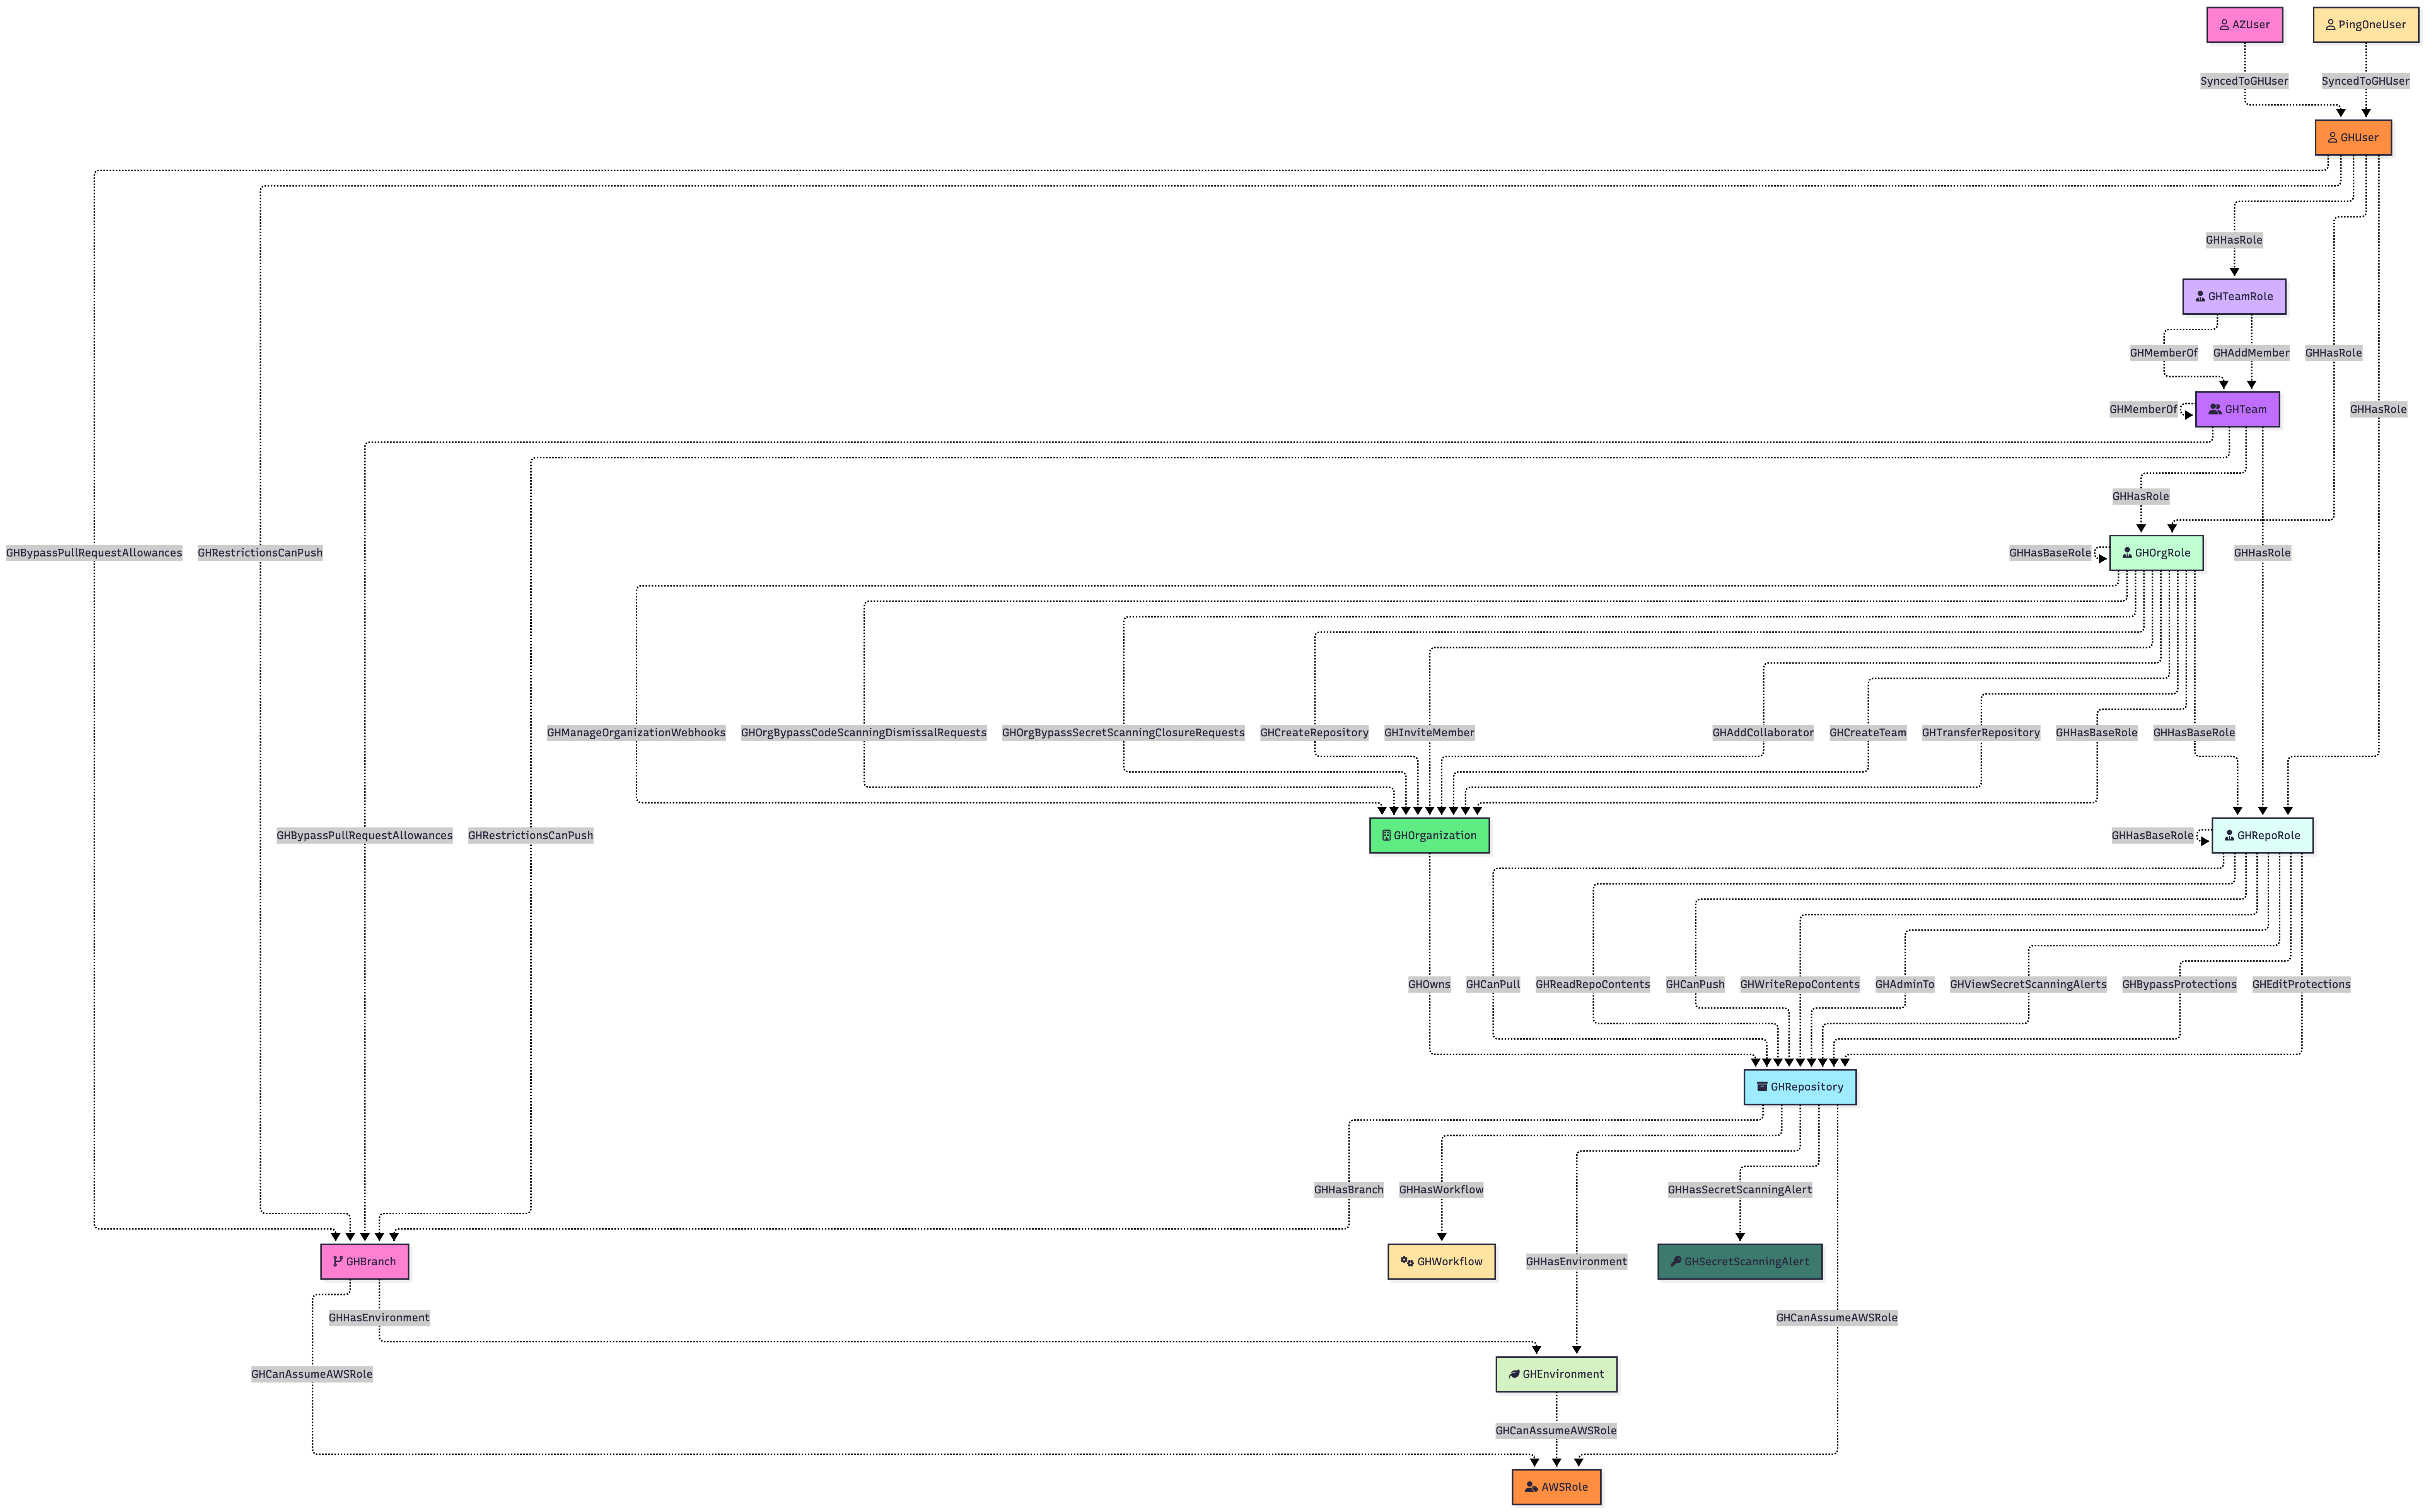 specterops/githound
BloodHound OpenGraph collector for GitHub that maps organization structure, permissions, and cross-cloud attack paths into a navigable graph for…
 kevinslin/safe-npm
Safely install NPM packages
 greatscott/enject
enject: Hide .env secrets from prAIng eyes: secrets live in local encrypted stores (per project) and are injected directly into apps at runtime,…
 wiz-sec-public/cloud-middleware-dataset
Curated dataset of cloud middleware agents installed by AWS, Azure, and GCP, documenting past vulnerabilities, privileges, and attack-surface risks…








