
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended
 aikidosec/safe-chain
Protect against malicious code installed via npm, yarn, pnpm, npx, pnpx, pip, uv and poetry with Aikido Safe Chain. Free to use, no tokens required.
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 dependencytrack/dependency-track
Intelligent Component Analysis platform that leverages SBOMs to identify and reduce software supply chain risk through continuous vulnerability…
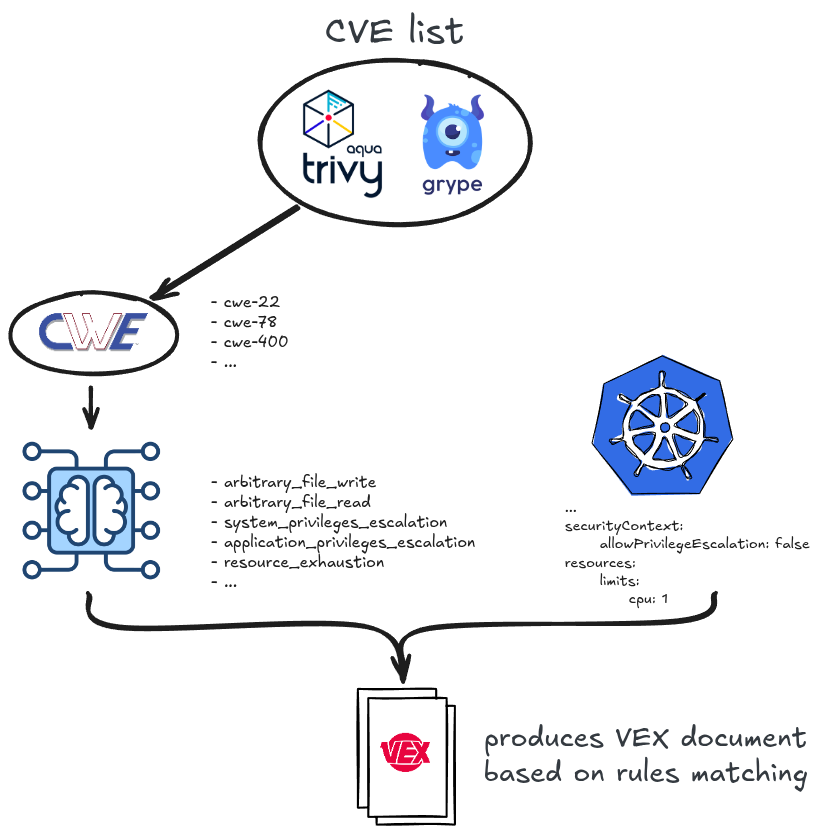 alegrey91/vex8s
Suppress vulnerabilities applying Kubernetes context to scans
 dependency-check/dependencycheck
OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.
 hotcakex/harden-windows-security
Harden Windows Safely, Securely using Official Supported Microsoft methods and proper explanation | Always up-to-date and works with the latest build…
 nationwide-group-oss/cryptoptic
CodeQL-based scanner that inventories cryptographic function calls across repositories and GitHub organizations, producing a Cryptographic Bill of…

 vpierre/ndaal_public_sbom_auditor
Offline single-binary web app that ingests CycloneDX, SPDX and syft SBOMs, runs an ensemble of CVE scanners, enriches findings with EPSS, CISA-KEV…
 theupdateframework/python-tuf
Python reference implementation of The Update Framework (TUF)
 secure-systems-lab/securesystemslib
Cryptographic and general-purpose routines for Secure Systems Lab projects at NYU
 google/capslock
CLI tool for analyzing Go package capabilities by tracing transitive calls to privileged standard library operations, enabling supply chain risk…
 cisco-ai-defense/skill-scanner
Security Scanner for Agent Skills
 cosai-oasis/ws4-secure-design-agentic-systems
Repository for CoSAI Workstream 4, Secure Design Patterns for Agentic Systems
 guacsec/guac
Aggregates software supply chain security metadata (SBOMs, attestations, vulnerabilities) into a queryable graph database for audit, policy, and risk…
 trailofbits/skills
Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows
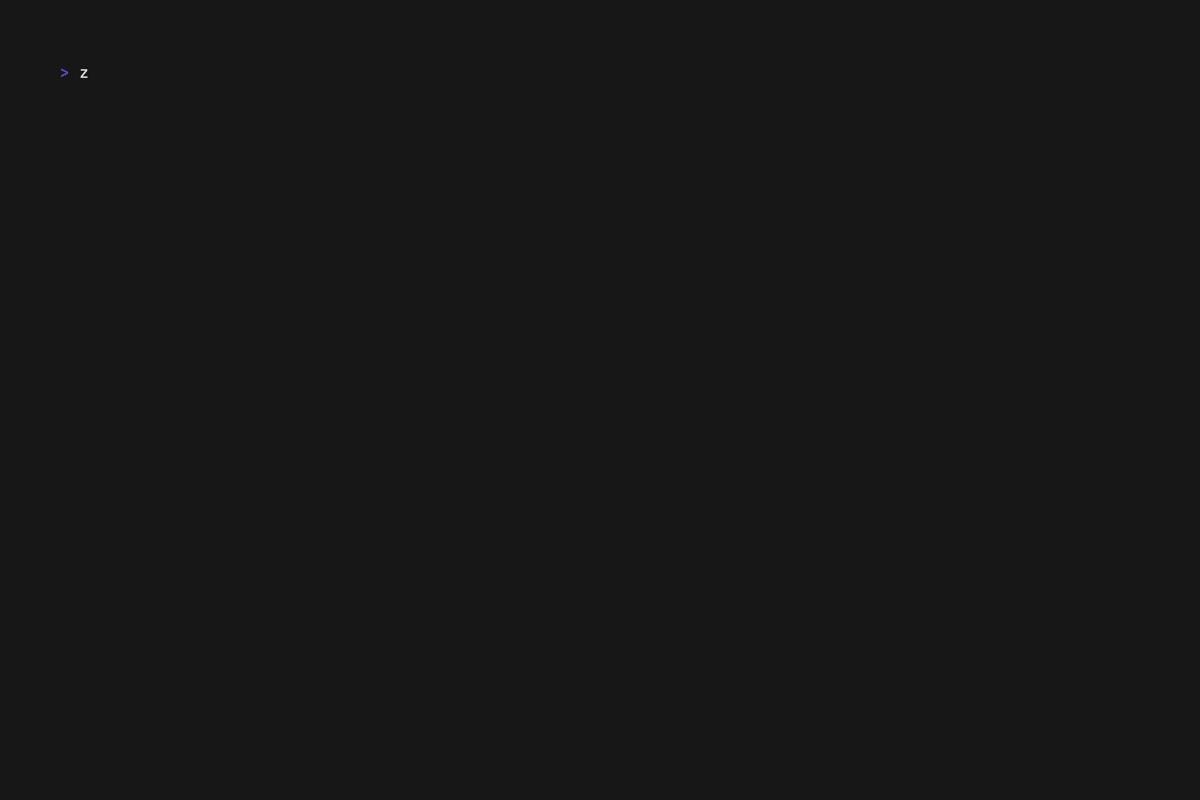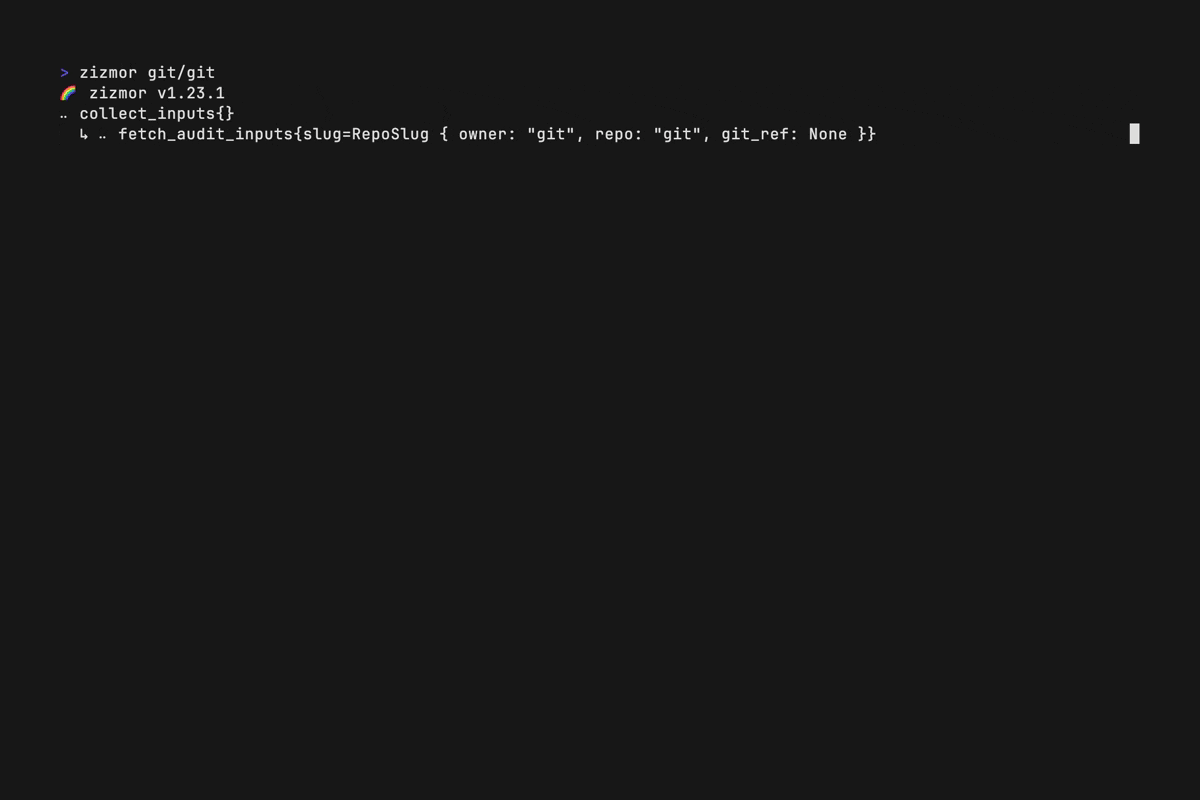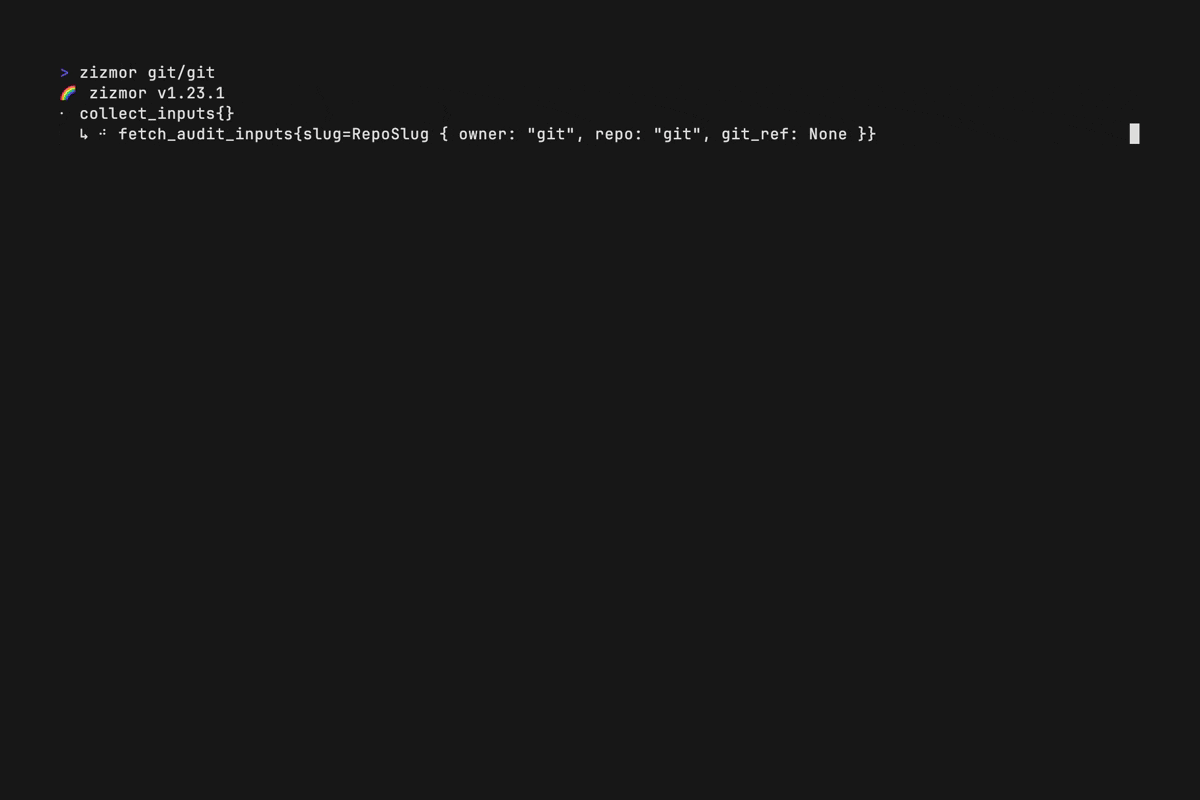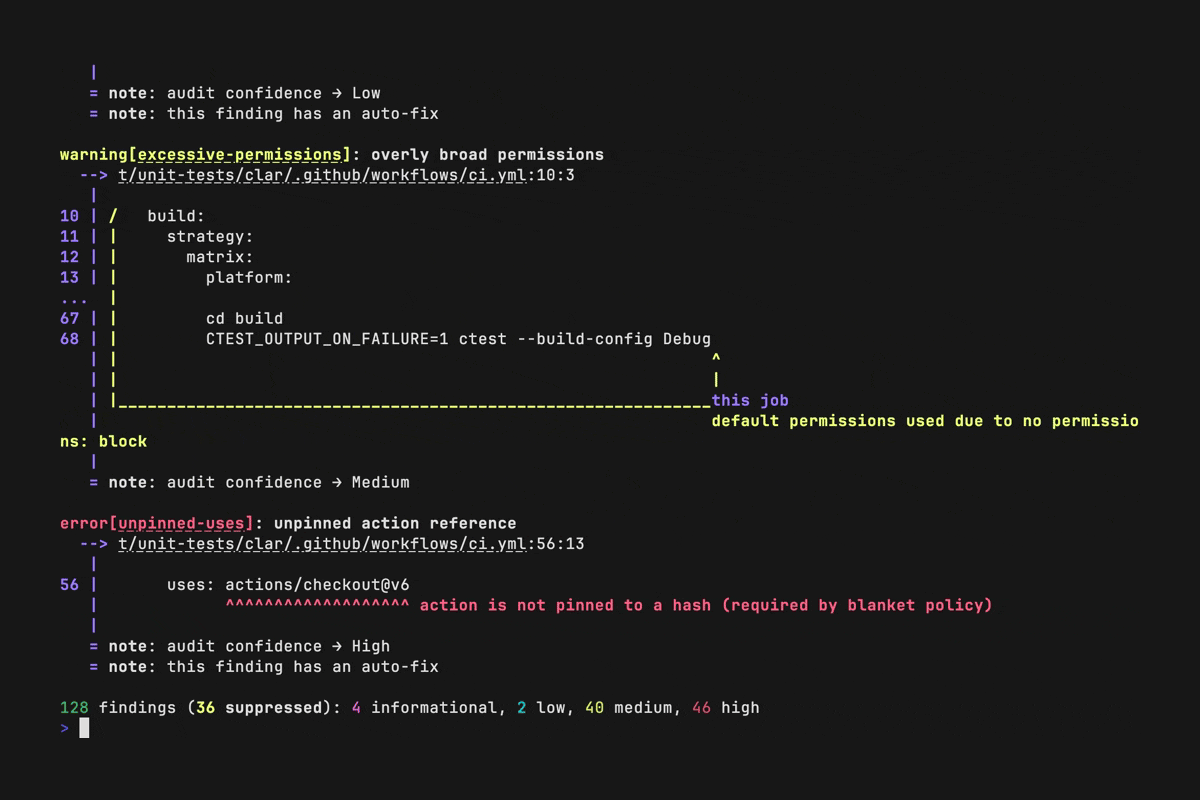 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
 owasp-dep-scan/dep-scan
Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD…
 knostic/openant
OpenAnt from Knostic is the leading open source LLM-based vulnerability discovery product, helping defenders proactively find verified security flaws…





