
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended
 barrersoftware/opencode-secure
Security-hardened fork of OpenCode - Fixes CVE-2026-22812 (CVSS 8.8 RCE) that upstream refuses to patch
 atiilla/cve-2026-21852-poc
Educational demo of three Claude Code vulnerabilities (hooks bypass, MCP injection, API key exfiltration) with attacker server, MITM proxy, and…
 simoesctt/sovereign-echo-33017
Exploit for CVE-2026-33017, an unauthenticated RCE in Langflow 1.8.1 via the build_public_tmp endpoint, enabling Python code injection through…
 rohitberiwala/nodejs-tar-symlink-exploit-cve-2026-29786
Technical analysis and Proof-of-Concept (PoC) for a critical Path Traversal vulnerability via Symlink manipulation in the Node.js 'tar' package…
 jvr2022/cve-2026-31802
Proof of concept and technical write-up for CVE-2026-31802, a symlink path traversal in npm tar allowing arbitrary file overwrite outside extraction…
 jvr2022/cve-2026-29786
Proof-of-concept demonstrating a hardlink path traversal in the tar npm package, allowing overwrite of files outside the extraction directory via…
 otakuliu/cve-2026-22807_range
Educational Python target range simulating CVE-2026-22807, an AI supply chain RCE via TOCTOU in model loading. Includes vulnerable library, PoC…
 osmancanvural/cve-2026-21436
Proof-of-concept exploit for CVE-2026-21436, demonstrating path traversal in Solus OS eopkg package manager allowing arbitrary file write during…
 openexecution-coder/demo-cve-2026-4821
Demonstrates AI agent-driven CVE remediation with cryptographic provenance tracking, showcasing detection, analysis, human approval, and verification…
 fevar54/cve-2026-33634-scanner
Scanner de IOCs del ataque de cadena de suministro TeamPCP (CVE-2026-33634).
 belazy167/next-picomatch-cve-repro
Minimal repro for Next.js 16.2.4 bundling picomatch 4.0.3 (CVE-2026-33671)
 batosay1337lab/cve-2026-31900-lab
CVE-2026-31900 Vulnerable Lab - psf/black GitHub Action RCE
 ashleyt3/docker-socket-risk-demos
Companion source for YouTube video "Stop Mounting docker.sock — Run Trivy Without Giving Away Root Access — (inspired by CVE-2026-33634)"
 3pplus/loguccino
Scan and patch tool for CVE-2021-44228 and related log4j concerns.
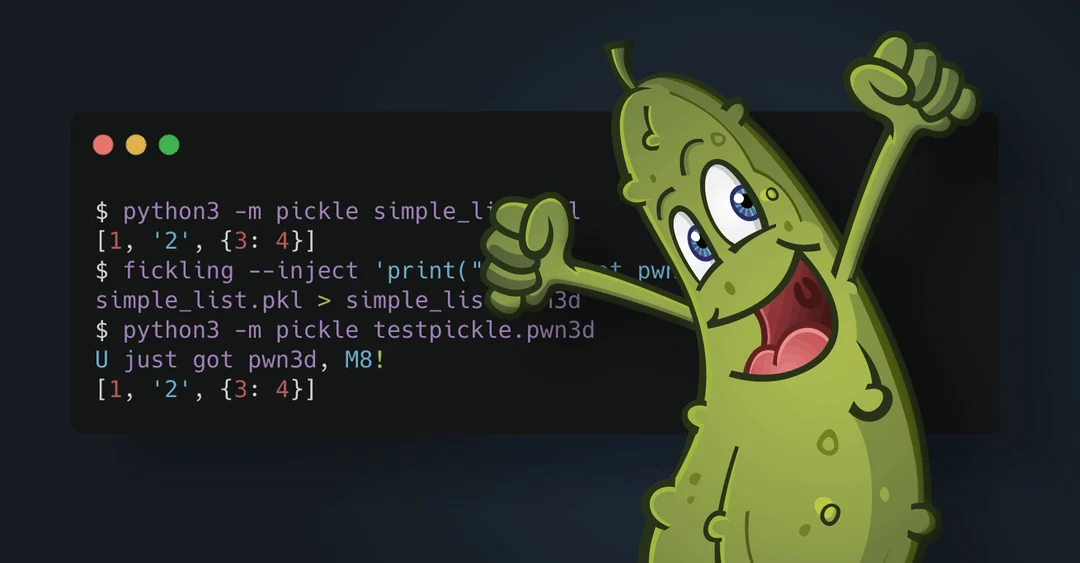 trailofbits/fickling
A Python pickling decompiler and static analyzer
 platanor/hardware-compliance-handbook
AI-ready knowledge base of security & compliance regulations for hardware and connected-device manufacturers - structured, indexed, and…
 s1ko/cve-2026-52617
Advisory and proof-of-concept for OS command injection in an MCP ffmpeg helper, with root-cause analysis, detector guidance, and mitigations for an…
 protectai/modelscan
Protection against Model Serialization Attacks








