
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended

 airineiandrei/tarmageddon-cve-2025-62518-
PoC for CVE-2025-62518 demonstrating tar archive smuggling via tokio-tar PAX header parsing, creating malicious payloads and a vulnerable extractor…
 7whyex/cve-2026-45321-tanstack
Educational lab simulating an npm supply chain attack (CVE-2026-45321) with malicious packages, postinstall payload execution, and CI/CD abuse…
 431m/rcetest
CVE-2024-32002 poc test
 1lann/log4shelldetect
Rapidly scan filesystems for Java programs potentially vulnerable to Log4Shell (CVE-2021-44228) or "that Log4j JNDI exploit" by inspecting the class…
 0x3a/cve-2014-4936
Repository for CVE-2014-4936 POC code.
 checkmarx/checkmarx-cve-2025-30066-detection-tool
Scans GitHub workflows and logs for indicators of CVE-2025-30066, detecting malicious actions and exposed secrets using Checkmarx 2ms integration.
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
 momenbasel/malware-check
Static and dynamic analysis tool for detecting malicious code, suspicious binaries, and privacy violations
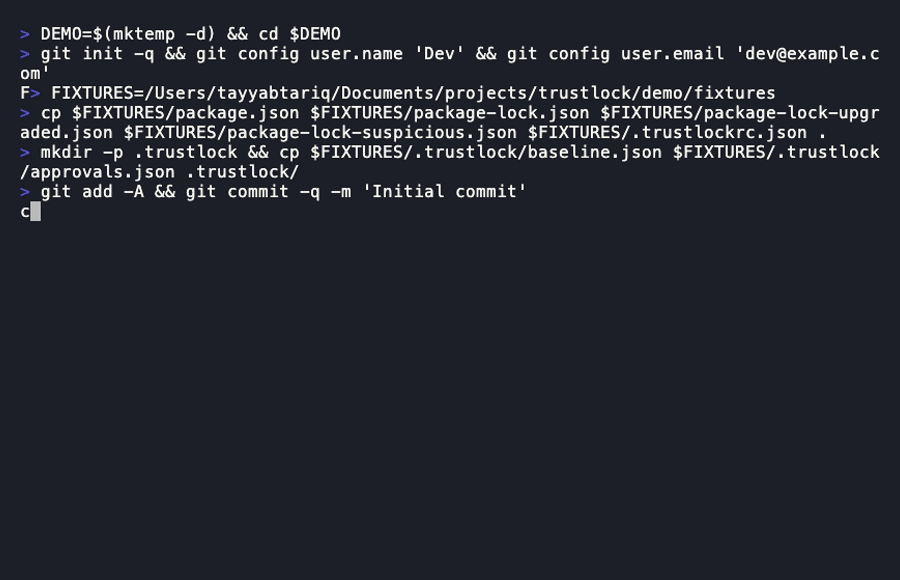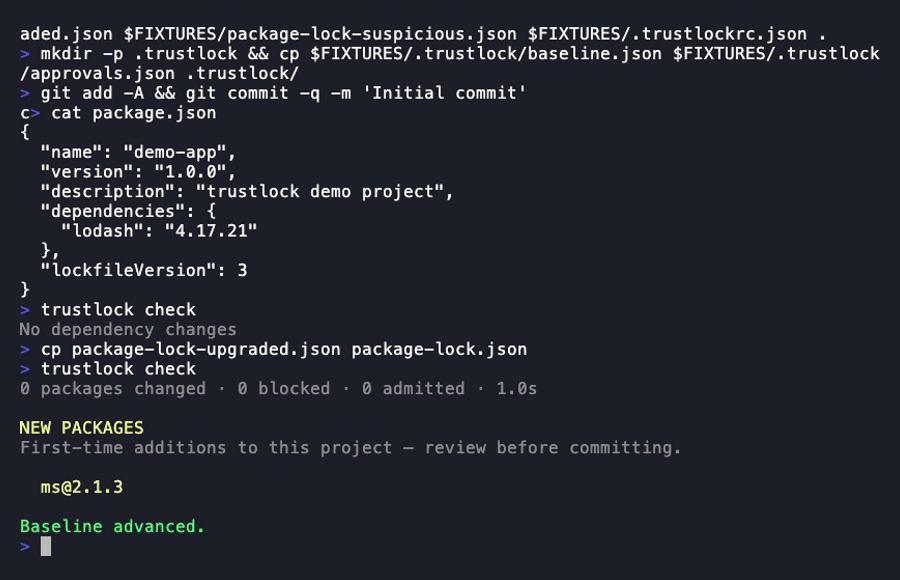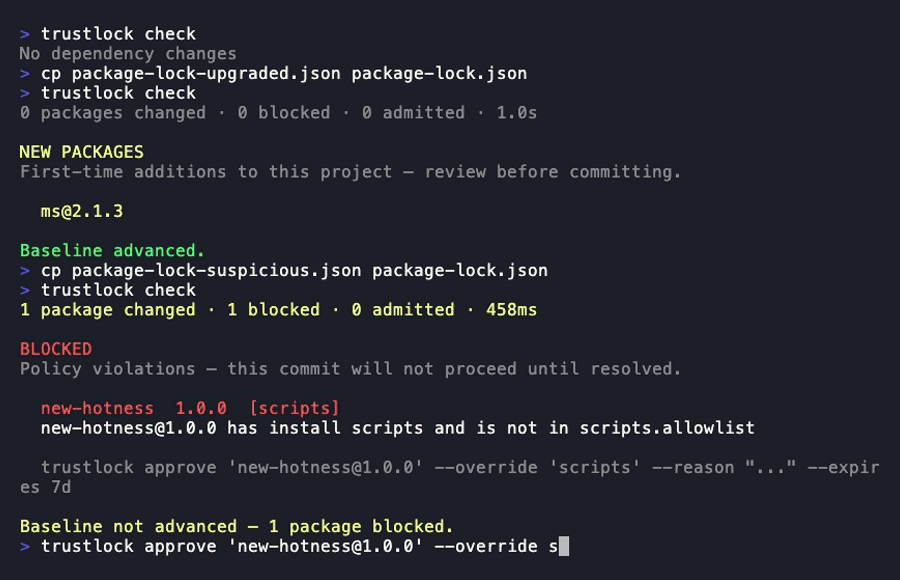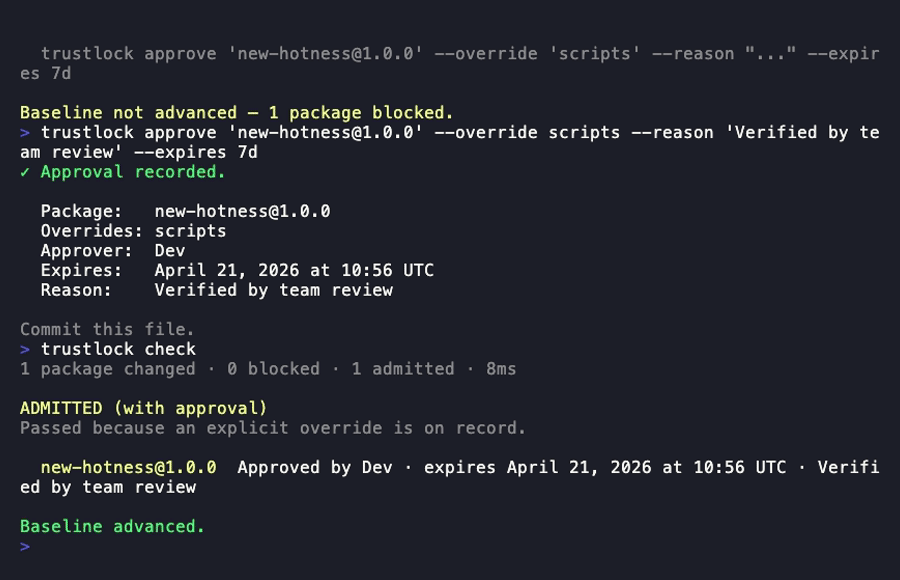 tayyabt/trustlock
A Git-native dependency admission controller. Evaluates trust signals on every dependency change and blocks commits or builds when packages fail your…
 dshapi/ai-spm
This opensource project dedicated to implementing Enterprise level AI-SPM. By doing so organizations can proactively protect their AI systems from…
 boostsecurityio/smokedmeat
A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
 pathakabhi24/llm-mcp-security-field-guide
The most comprehensive LLM + MCP security guide i.e. OWASP aligned, real CVEs, actionable checklists
 find-lab/agentward
Full-stack security OS for AI agents with five-layer defense-in-depth architecture covering foundation scan, input sanitization, cognition…
 opensourcemalware/vercel-april2026-incident-response
This is an incident response playbook we created for the Vercel April 2026 compromise
 msaad00/agent-bom
AI supply-chain BOM: every agent, MCP server and AI package, and what each one can reach. Open-source scanner and self-hosted control plane for code,…
 owasp/apts
OWASP Autonomous Penetration Testing Standard
 gautamvarmadatla/mcpsafetywarden
Proxy server that wraps MCP servers with behavioral profiling, security scanning, risk gating, and safe execution. Detects prompt injection,…
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.








