
 #1
Tools for examining source code without execution to find security flaws.
Kitploit recommended

 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 bearer/bearer
Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.
 kadenzipfel/smart-contract-vulnerabilities
A collection of smart contract vulnerabilities along with prevention methods
 ajinabraham/nodejsscan
nodejsscan is a static security code scanner for Node.js applications.
 wireghoul/graudit
grep rough audit - source code auditing tool
 knostic/openant
OpenAnt from Knostic is the leading open source LLM-based vulnerability discovery product, helping defenders proactively find verified security flaws…
 zegl/kube-score
Kubernetes object analysis with recommendations for improved reliability and security. kube-score actively prevents downtime and bugs in your…
 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
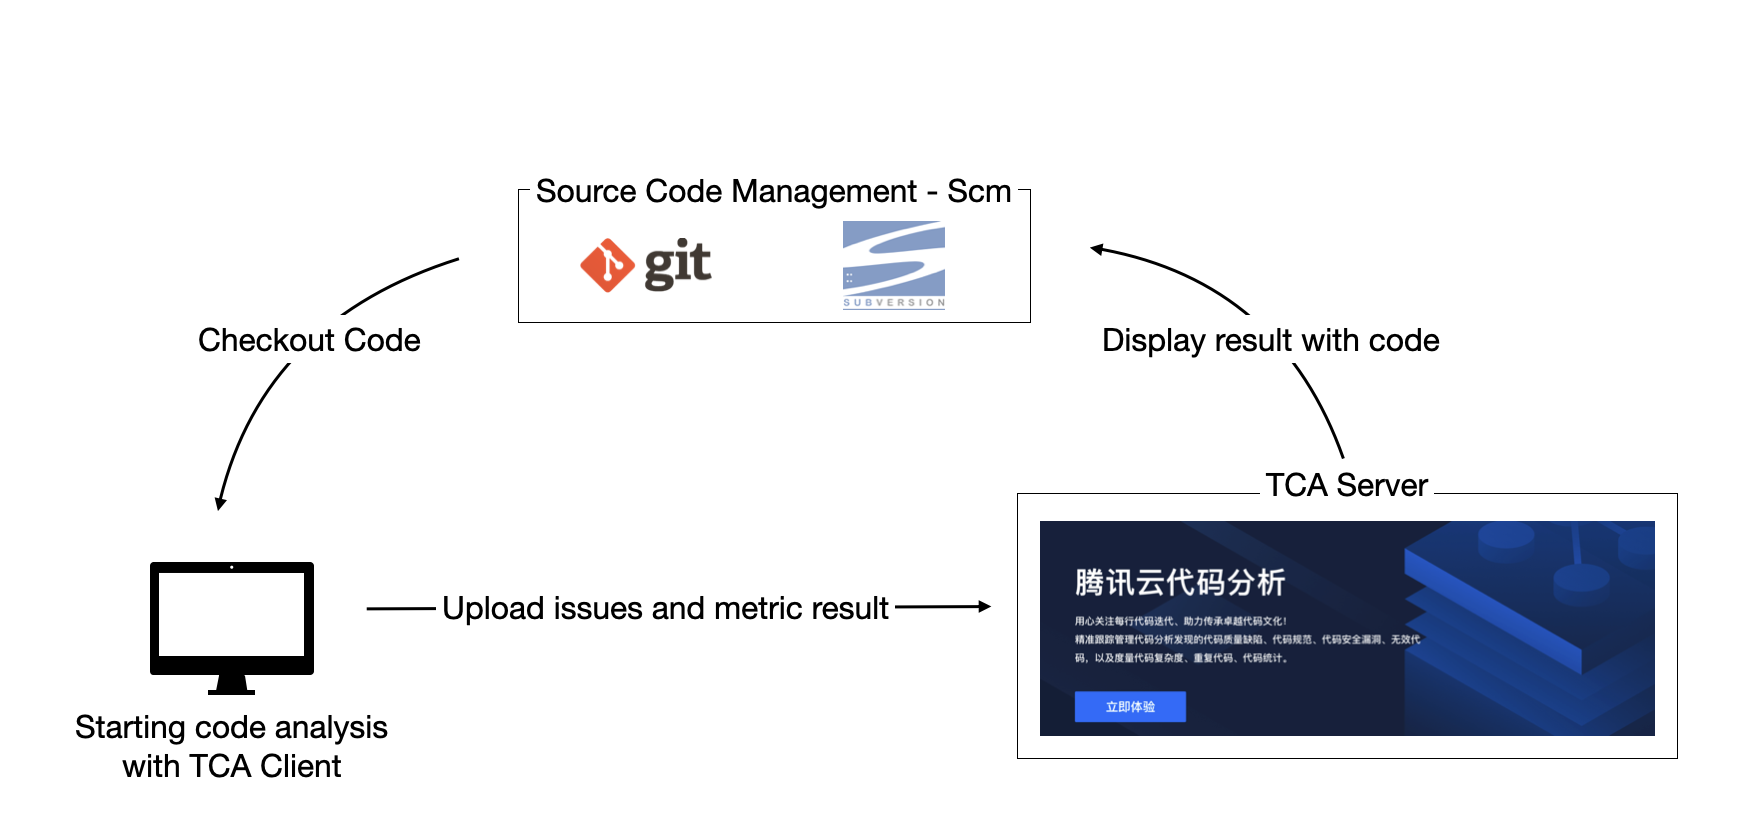 tencent/codeanalysis
Enterprise-grade static code analysis platform with multi-language support, security vulnerability detection, code quality metrics, and DevOps…
 python-security/pyt
A Static Analysis Tool for Detecting Security Vulnerabilities in Python Web Applications
 behisecc/vibesec-skill
This skill helps Claude write secure code and prevent common vulnerabilities.
 0xdea/semgrep-rules
A collection of my Semgrep rules to facilitate vulnerability research.
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 nealbridges/vulnhunter
Agentic AI security scanner that reasons like an attacker over source code, confirms exploitable flaws with executable PoCs, and drives test-first…
 stelligent/cfn_nag
Linting tool for CloudFormation templates
 pantheon-security/medusa
AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…





