#1
Tools for examining source code without execution to find security flaws.
Kitploit recommended

 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…
 aftermathlabs/vmp2
Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…
 mandiant/route-sixty-sink
Link sources to sinks in C# applications.
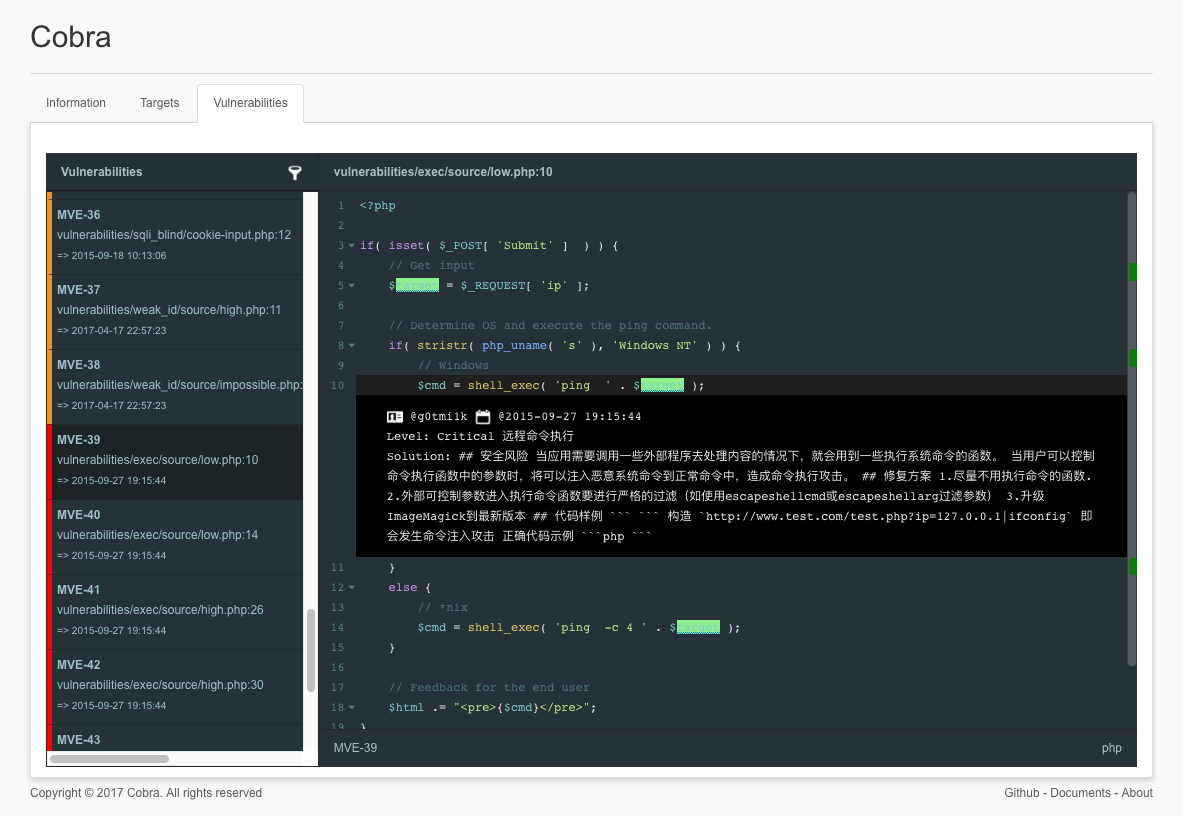 feeicn/cobra
Source Code Security Audit (源代码安全审计)
 tenable/terrascan
Detect compliance and security violations across Infrastructure as Code to mitigate risk before provisioning cloud native infrastructure.
 novoda/gradle-static-analysis-plugin
Easy setup of static analysis tools for Android and Java projects.
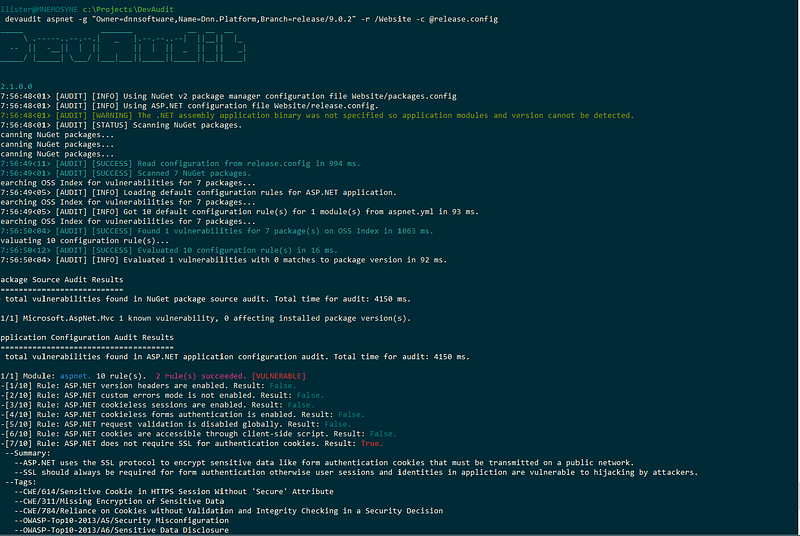 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 skyscanner/lambdaguard
AWS Serverless Security
 praetorian-inc/gokart
A static analysis tool for securing Go code
 iqtlabs/auraborealisapp
Do You Know What's In Your Python Packages? A Tool for Visualizing Python Package Registry Security Audit Data
 owasp/riskassessmentframework
The Secure Coding Framework
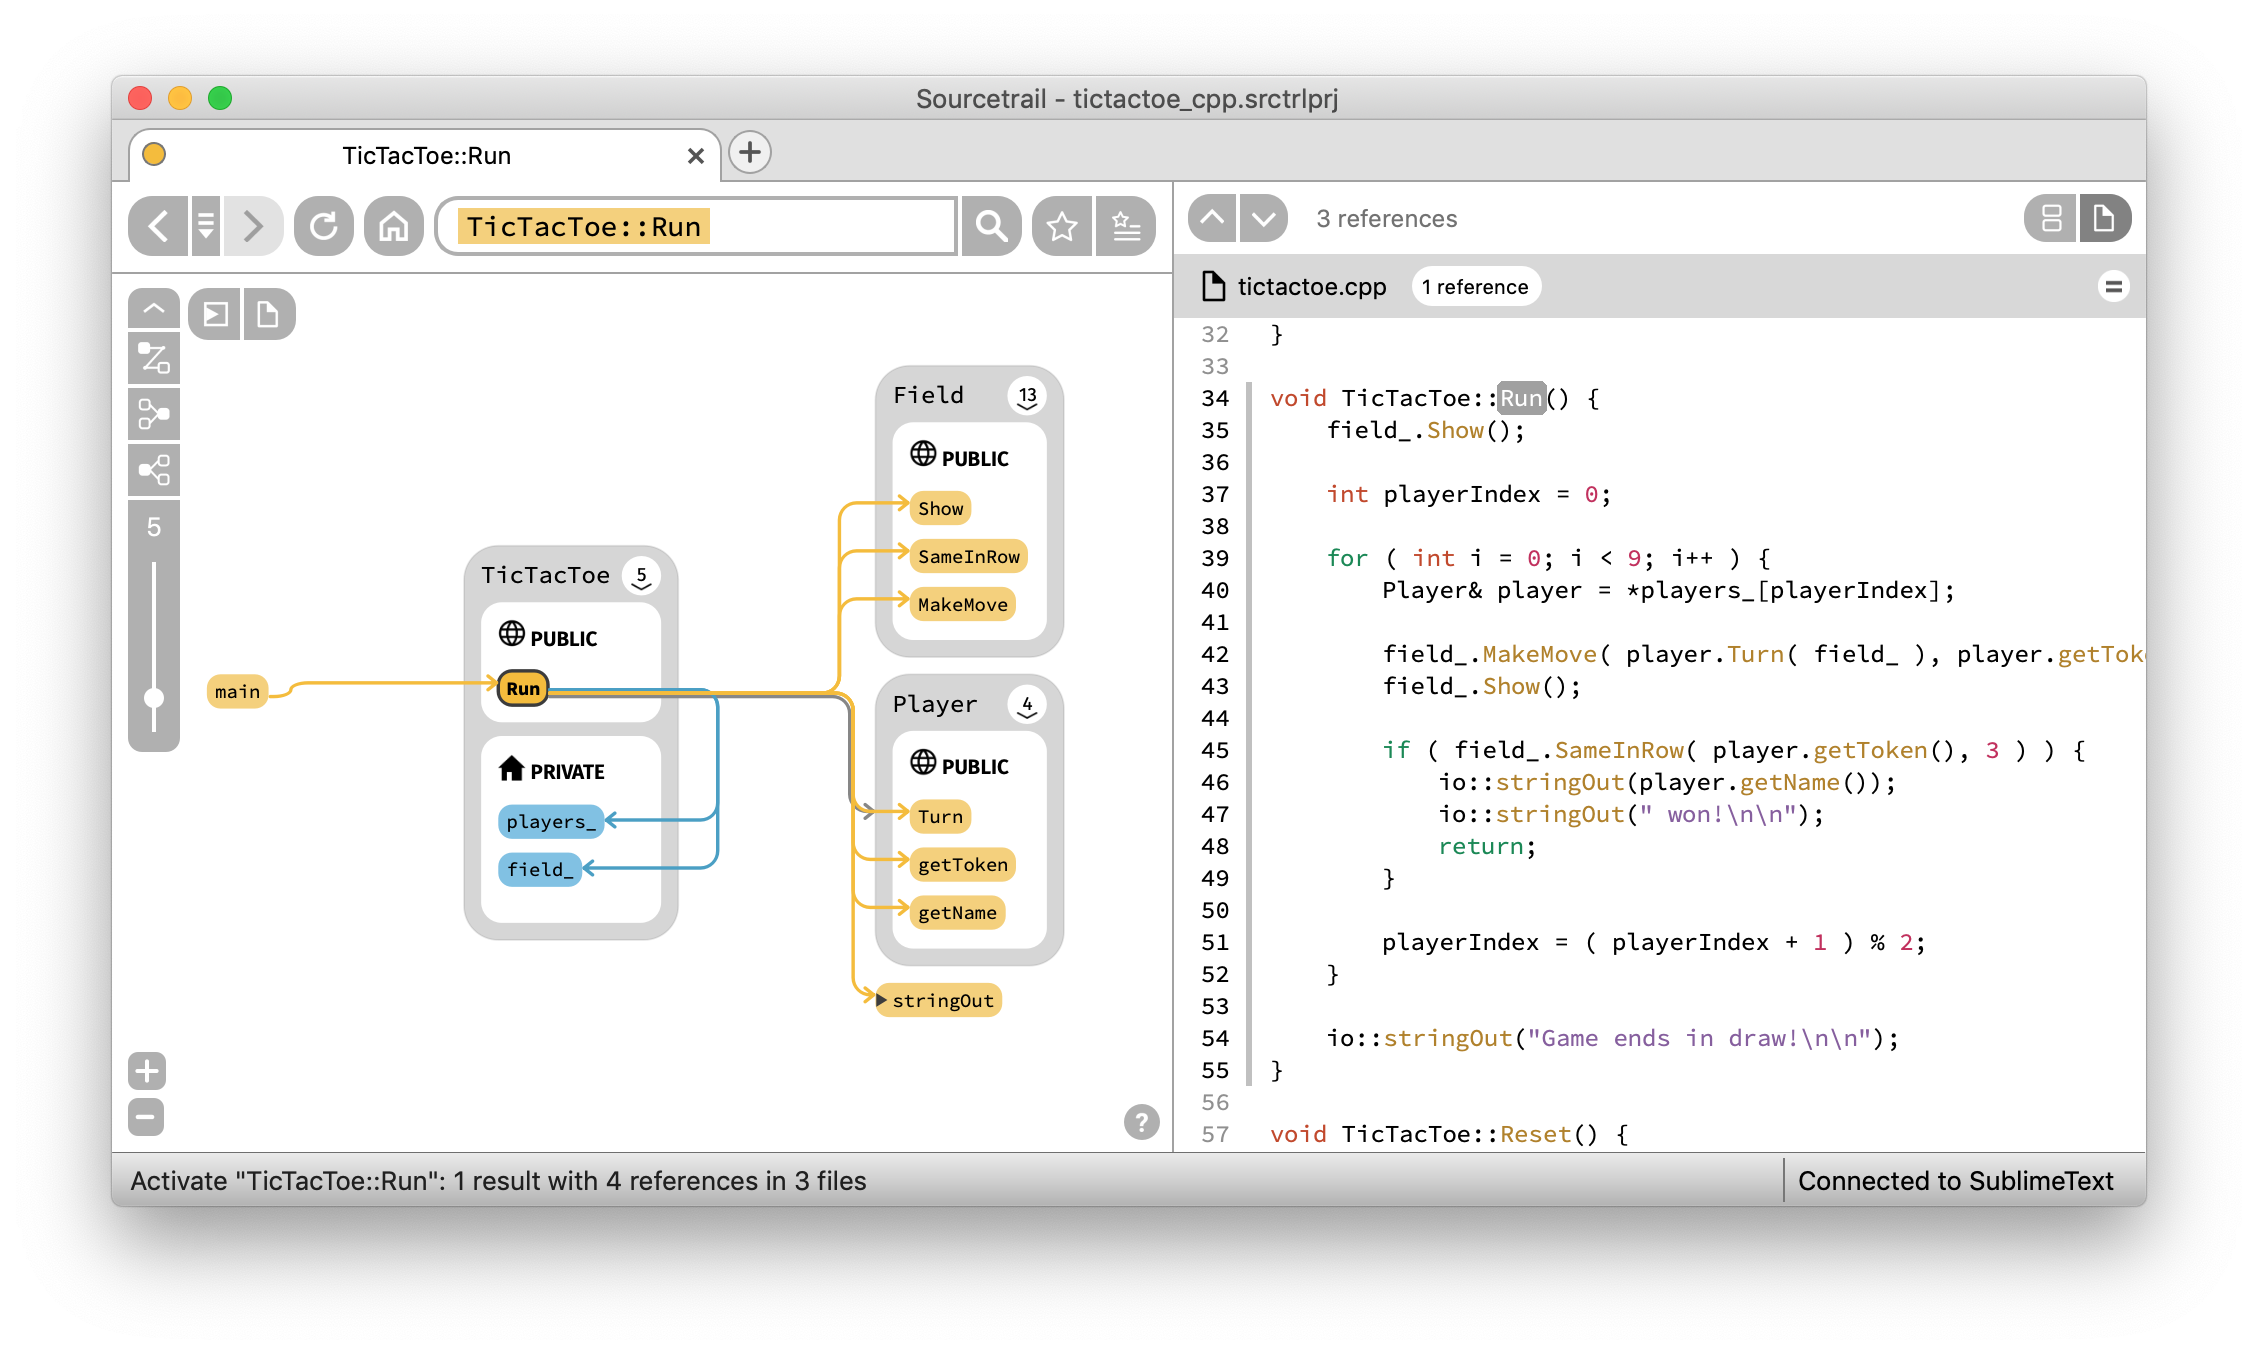 coatisoftware/sourcetrail
Sourcetrail - free and open-source interactive source explorer