
 #1
Tools for examining malware binaries and code without executing them (e.g., disassemblers, unpackers).
Kitploit recommended

 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 lkimuk/reark
An intelligent reverse engineering and AI-assisted analysis tool for HarmonyOS NEXT (HAP/APP/ABC), Android (APK/AAB), iOS (IPA), and native…
 rocky/python-decompile3
Python decompiler for 3.7-3.8 Stripped down from uncompyle6 so we can refactor and start to fix up some long-standing problems
 nccgroup/sobelow
Security-focused static analysis for the Phoenix Framework
 1n3/reverseapk
Quickly analyze and reverse engineer Android packages
 symgraph/ghidrassist
An LLM extension for Ghidra to enable AI assistance in RE.
 programa-stic/barf-project
BARF : A multiplatform open source Binary Analysis and Reverse engineering Framework
 owasp/owasp-java-encoder
The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…
 praetorian-inc/titus
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
 client9/libinjection
SQL / SQLI tokenizer parser analyzer
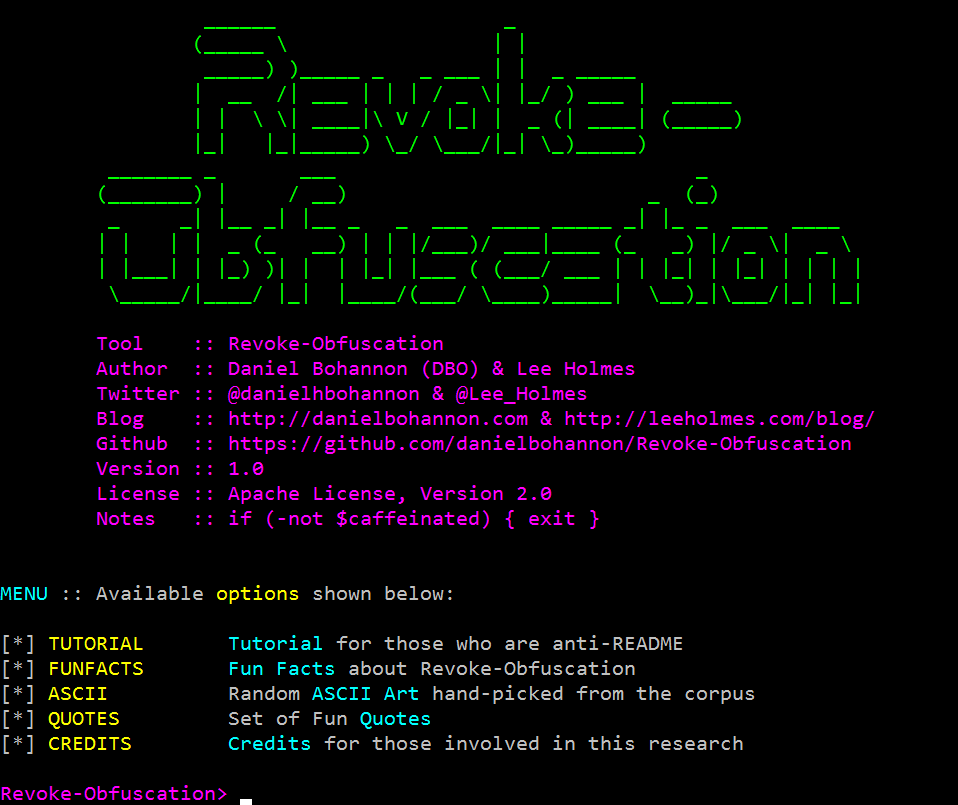 danielbohannon/revoke-obfuscation
PowerShell Obfuscation Detection Framework
 hellman/xortool
A tool to analyze multi-byte xor cipher
 appvia/krane
Kubernetes RBAC static analysis & visualisation tool
 fadi002/de4py
The ultimate AI-powered toolkit for python reverse engineering
 x86rc/vmp-lazy-unpack
Emulation-based unpacker and import resolver for Windows x86/x64 VMProtect 3.x binaries, using Unicorn to emulate syscalls and rebuild the IAT…
 xtiankisutsa/mara_framework
MARA is a Mobile Application Reverse engineering and Analysis Framework. It is a toolkit that puts together commonly used mobile application reverse…
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…








