
 #1
API key scanning, credential leak detection, and secret management tools.
Kitploit recommended
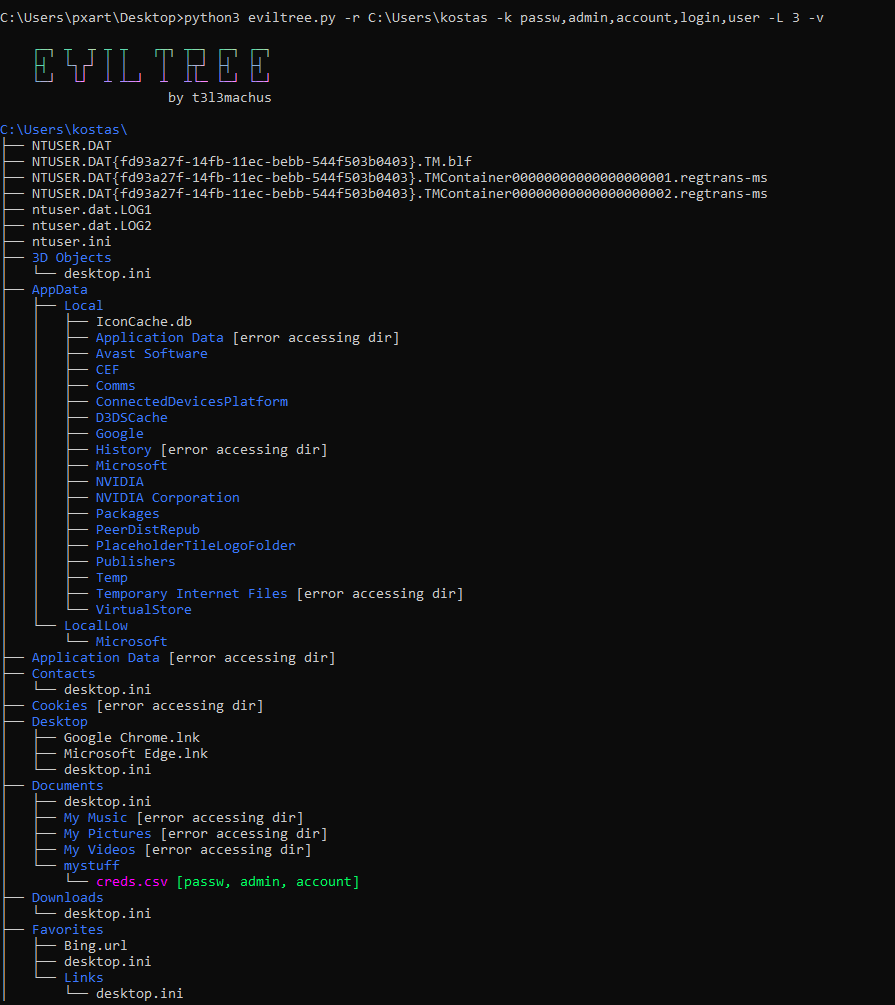
 t3l3machus/eviltree
A python3 remake of the classic "tree" command with the additional feature of searching for user provided keywords/regex in files, highlighting those…
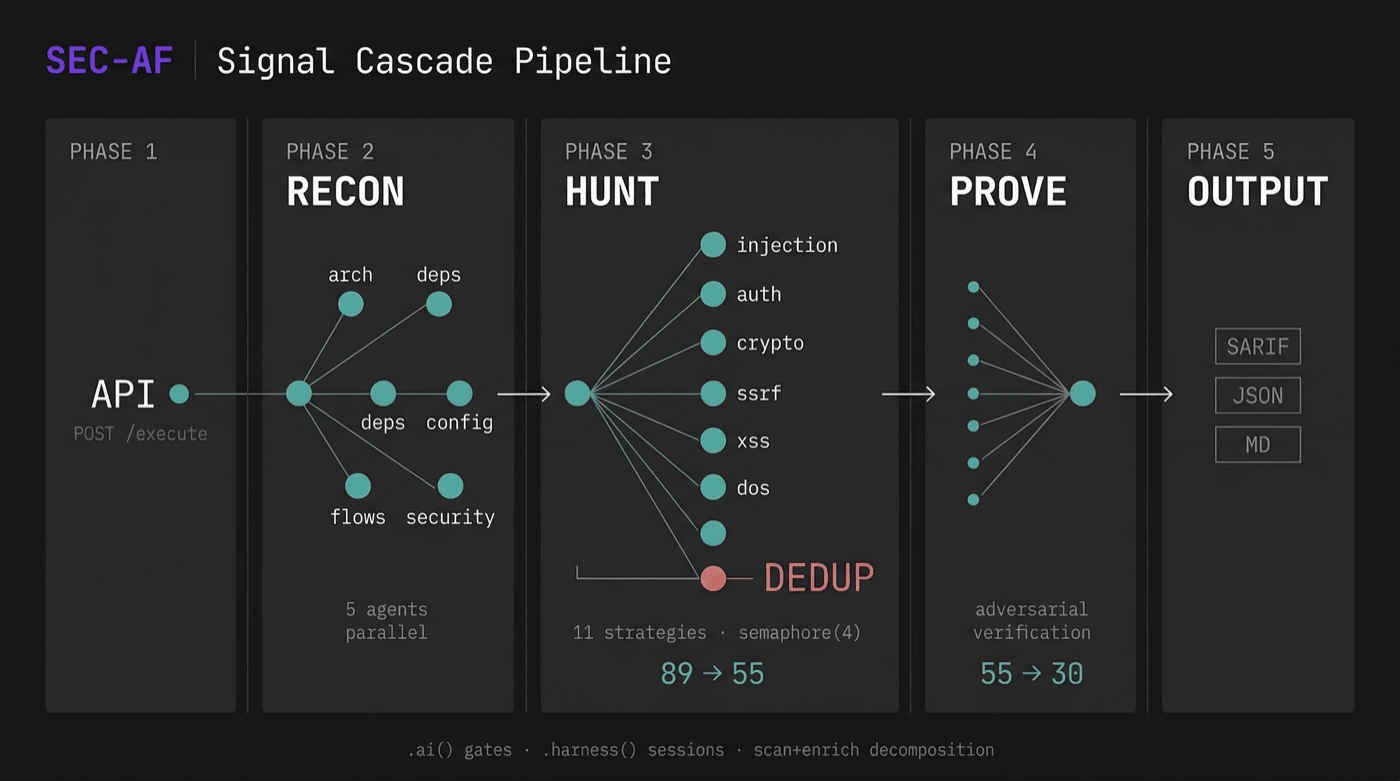 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
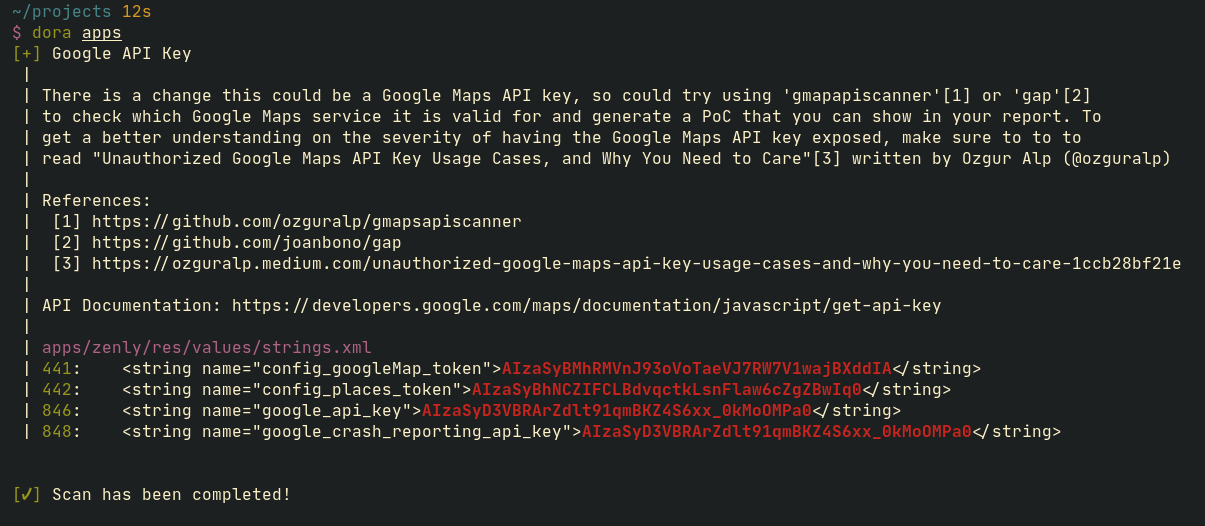 sdushantha/dora
Find exposed API keys based on RegEx and get exploitation methods for some of keys that are found
 josehelps/git-wild-hunt
A tool to hunt for credentials in github wild AKA git*hunt
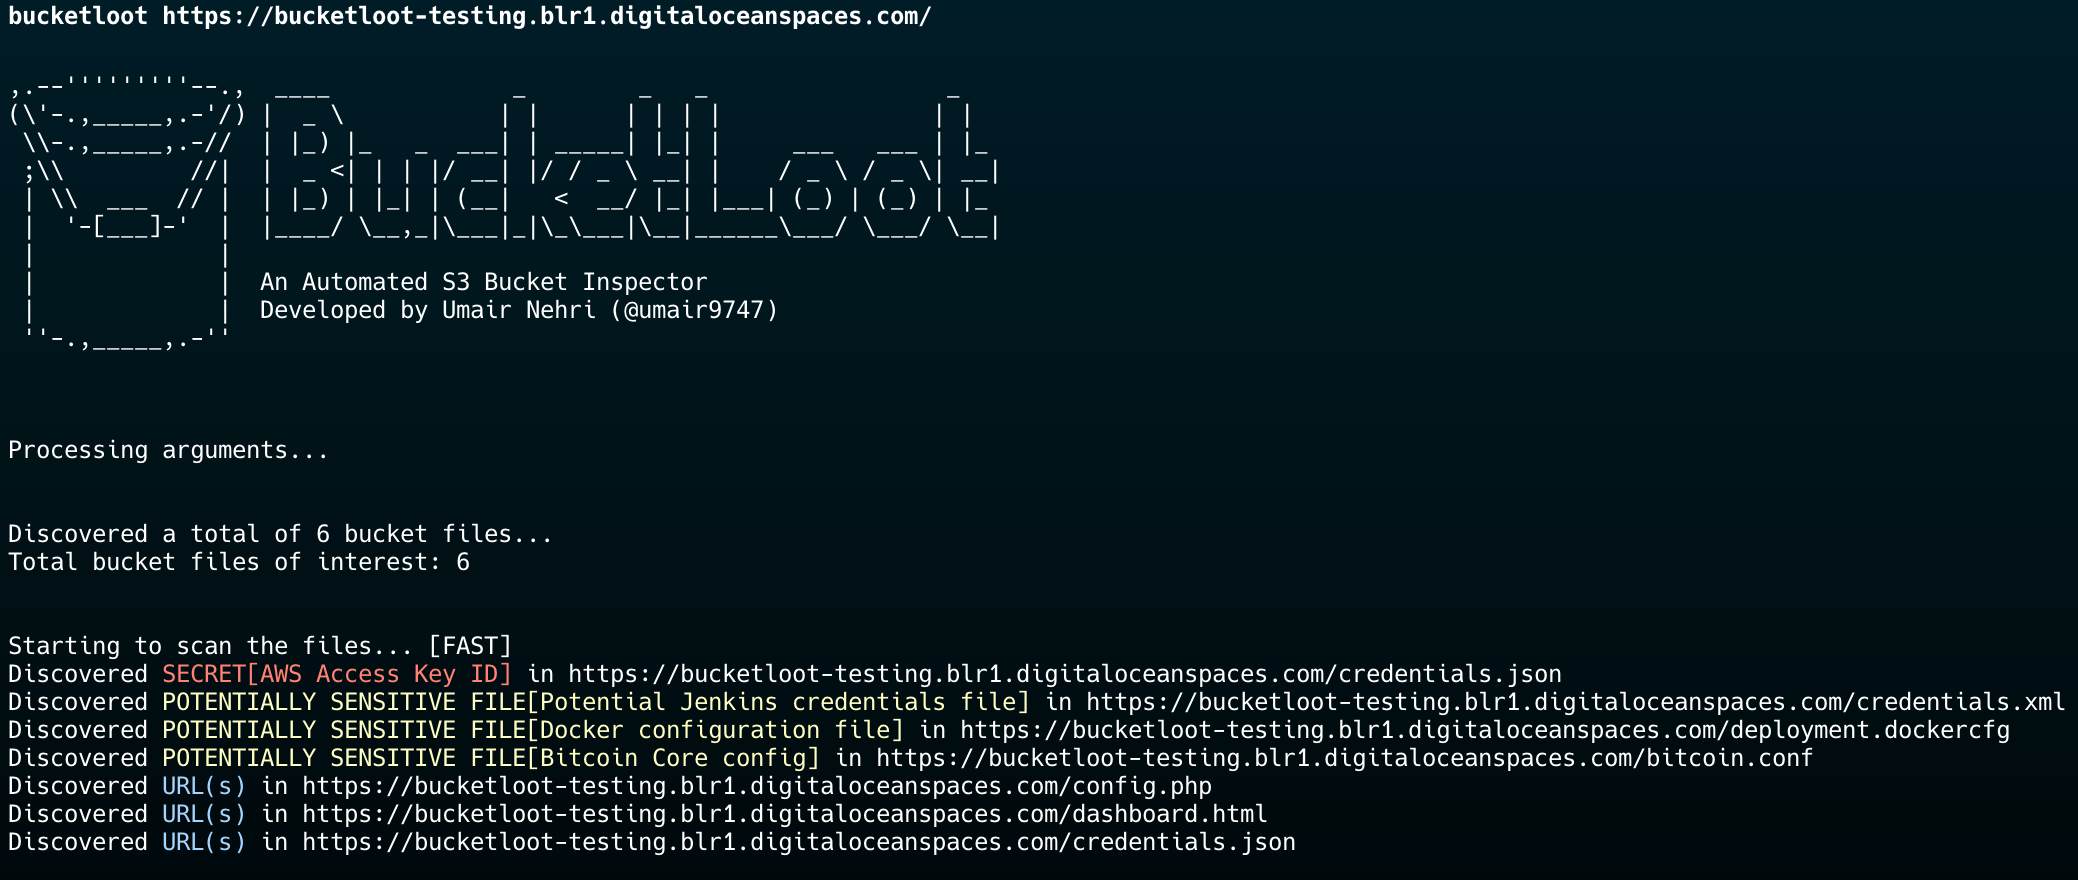 redhuntlabs/bucketloot
BucketLoot is an automated S3-compatible bucket inspector that can help users extract assets, flag secret exposures and even search for custom…
 dark-warlord14/jsscanner
You can read the writeup on this script here
 sourcecode-ai/aura
Python source code auditing and static analysis on a large scale
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project
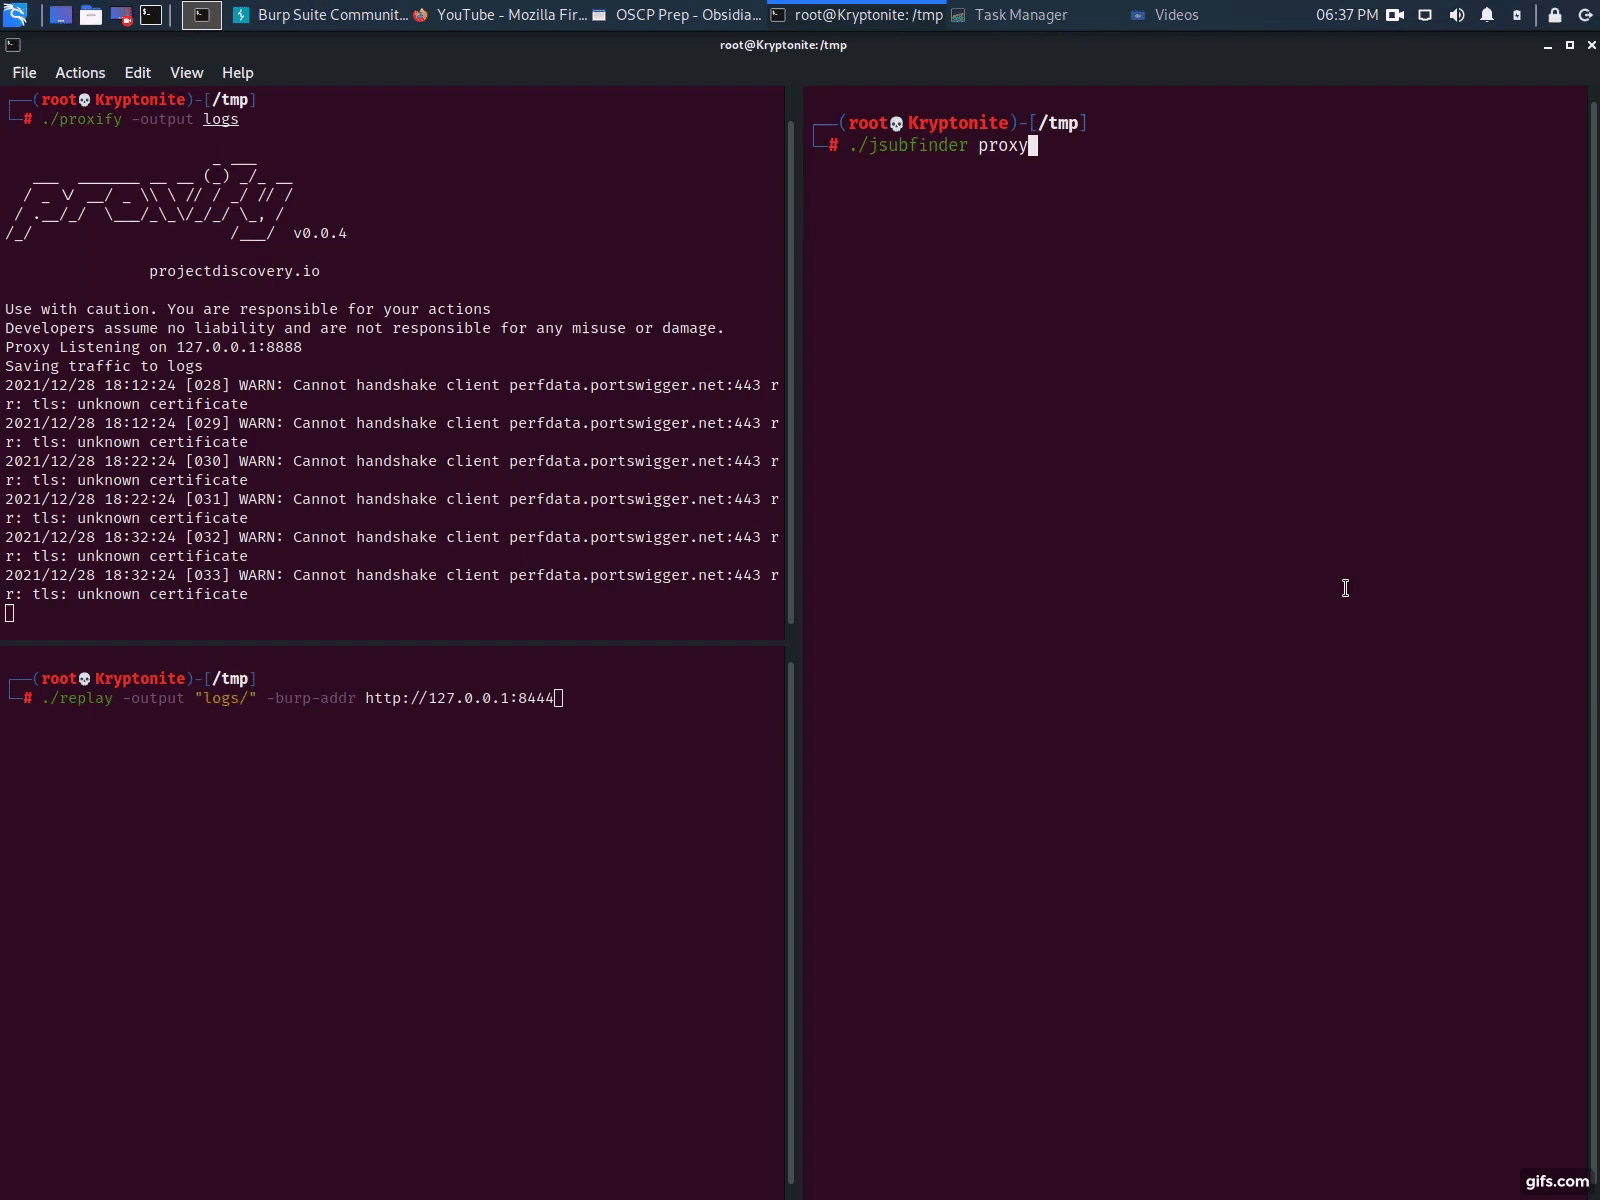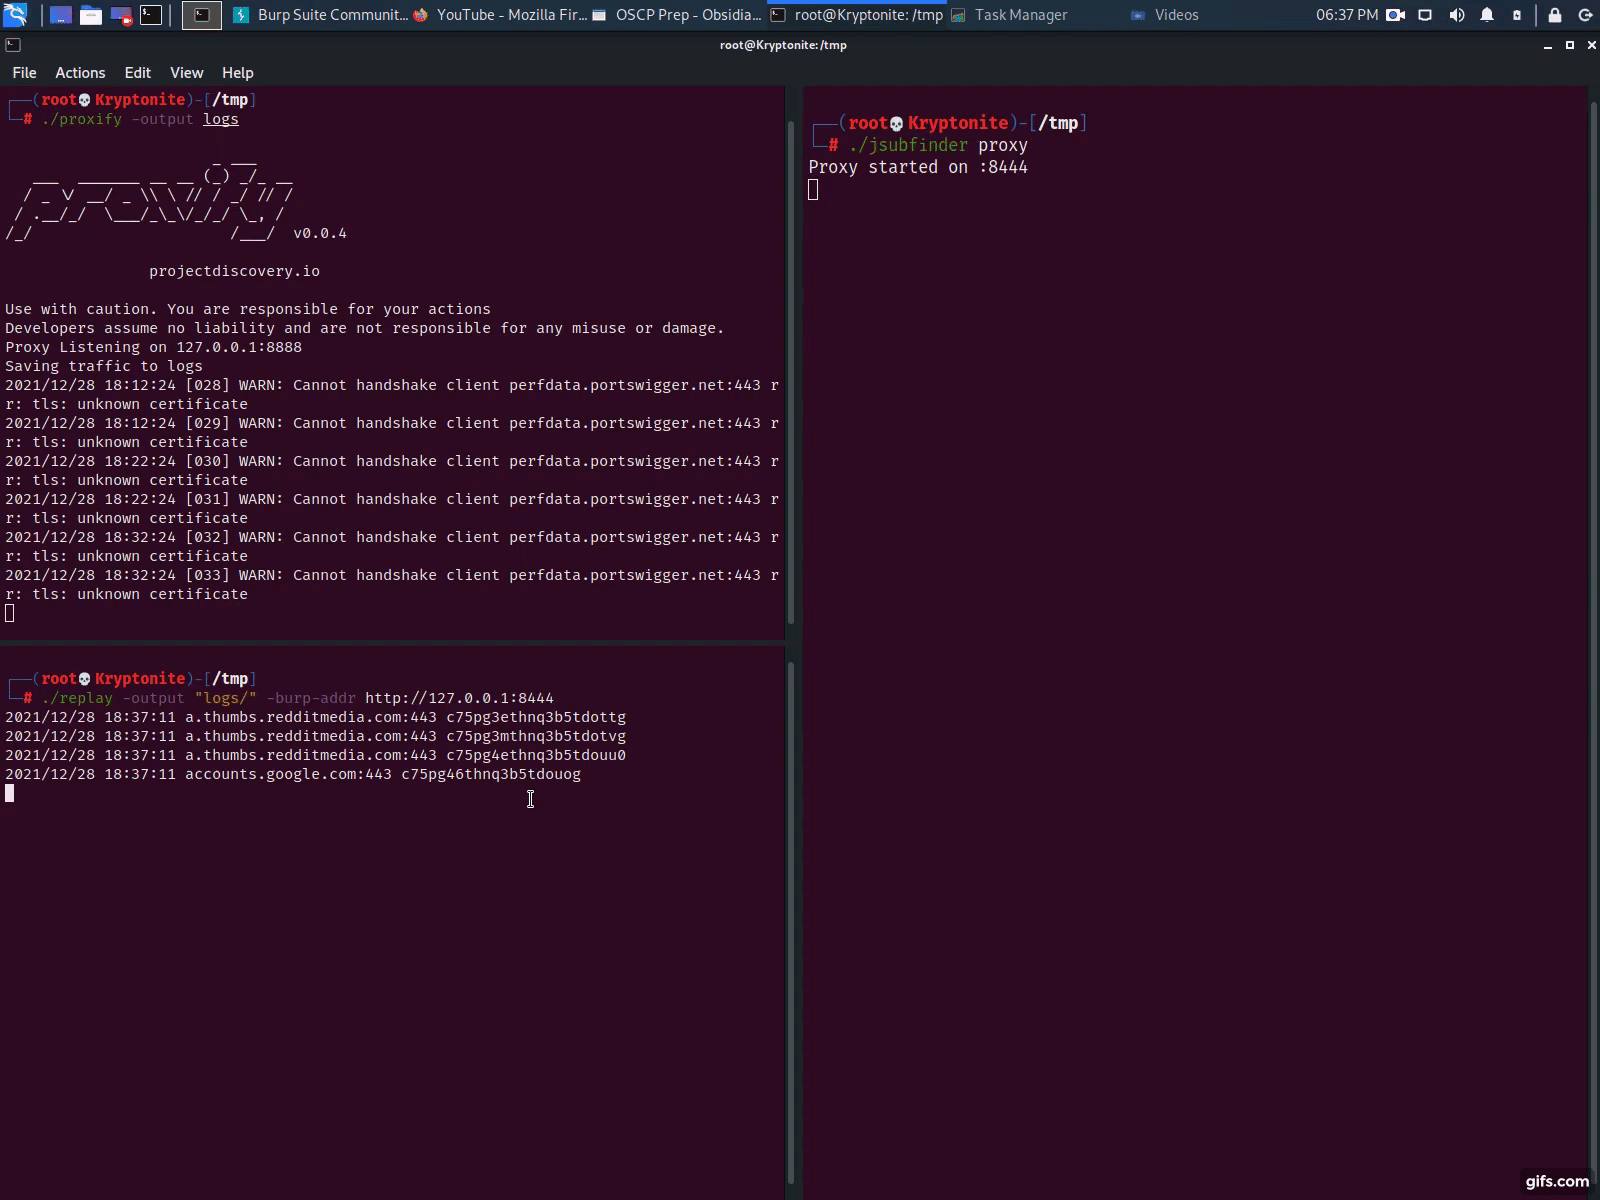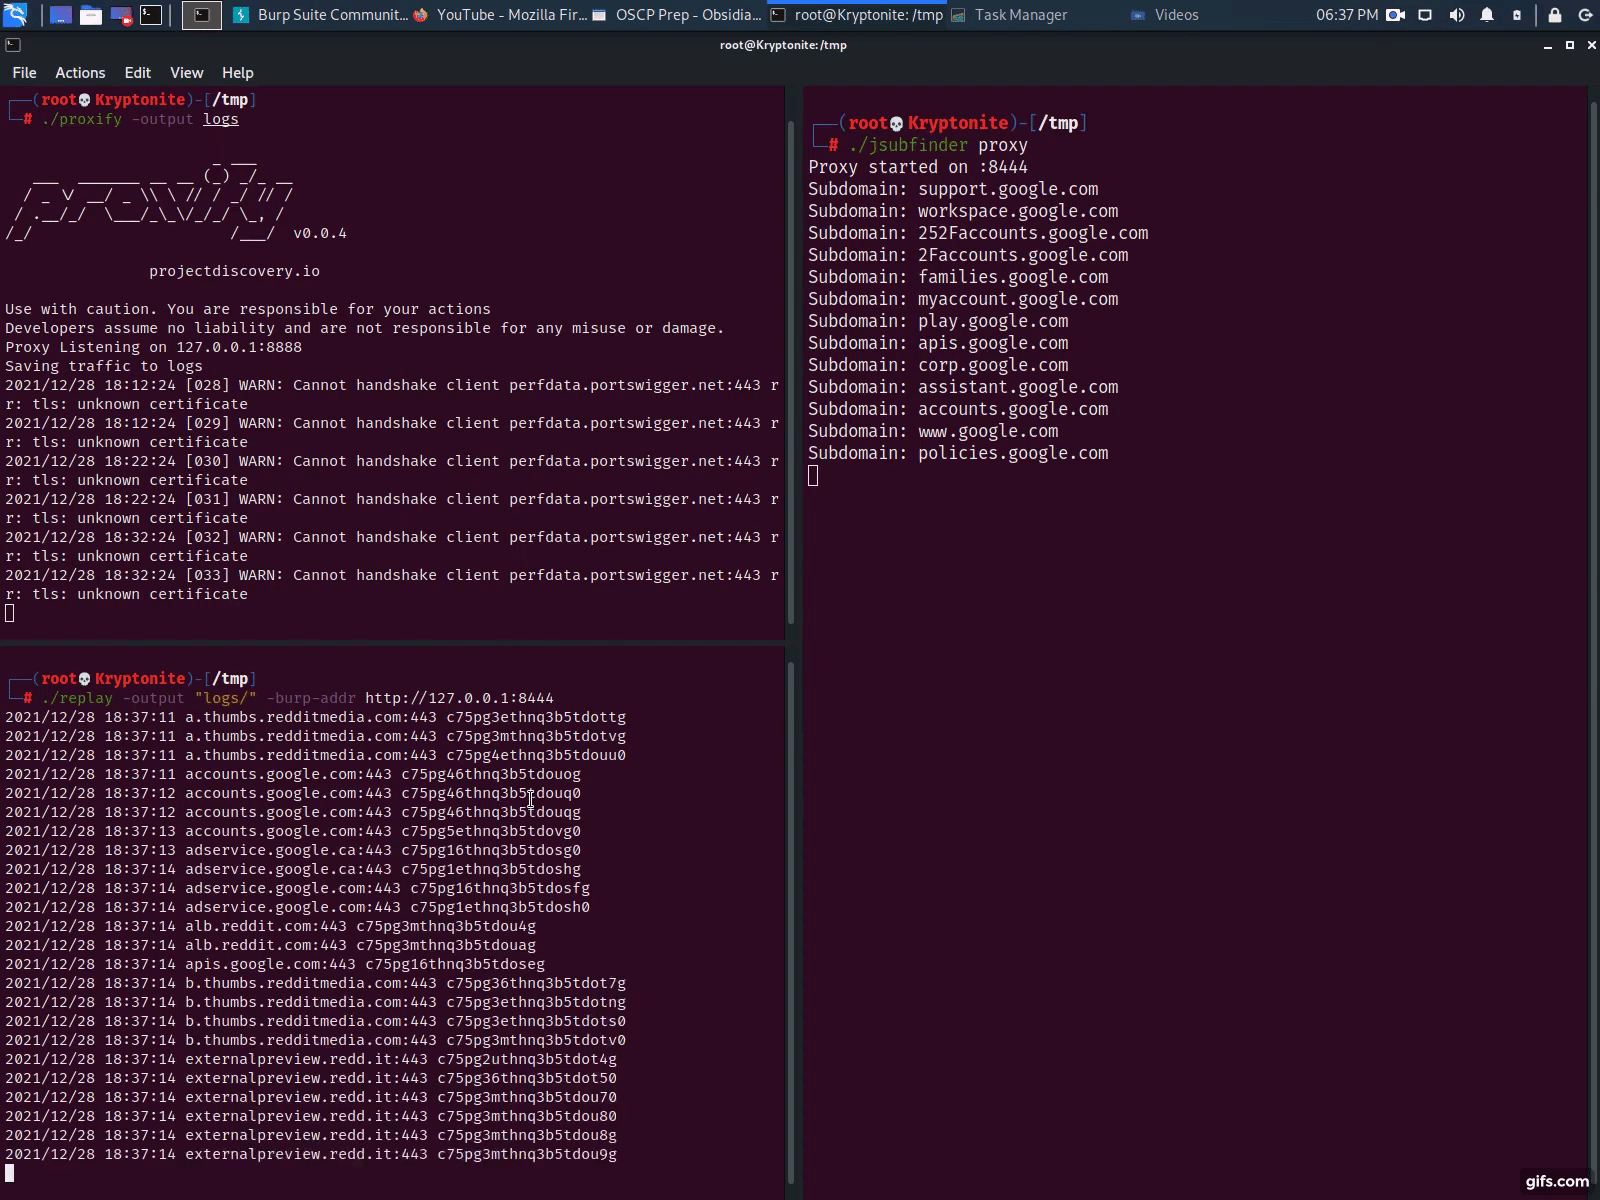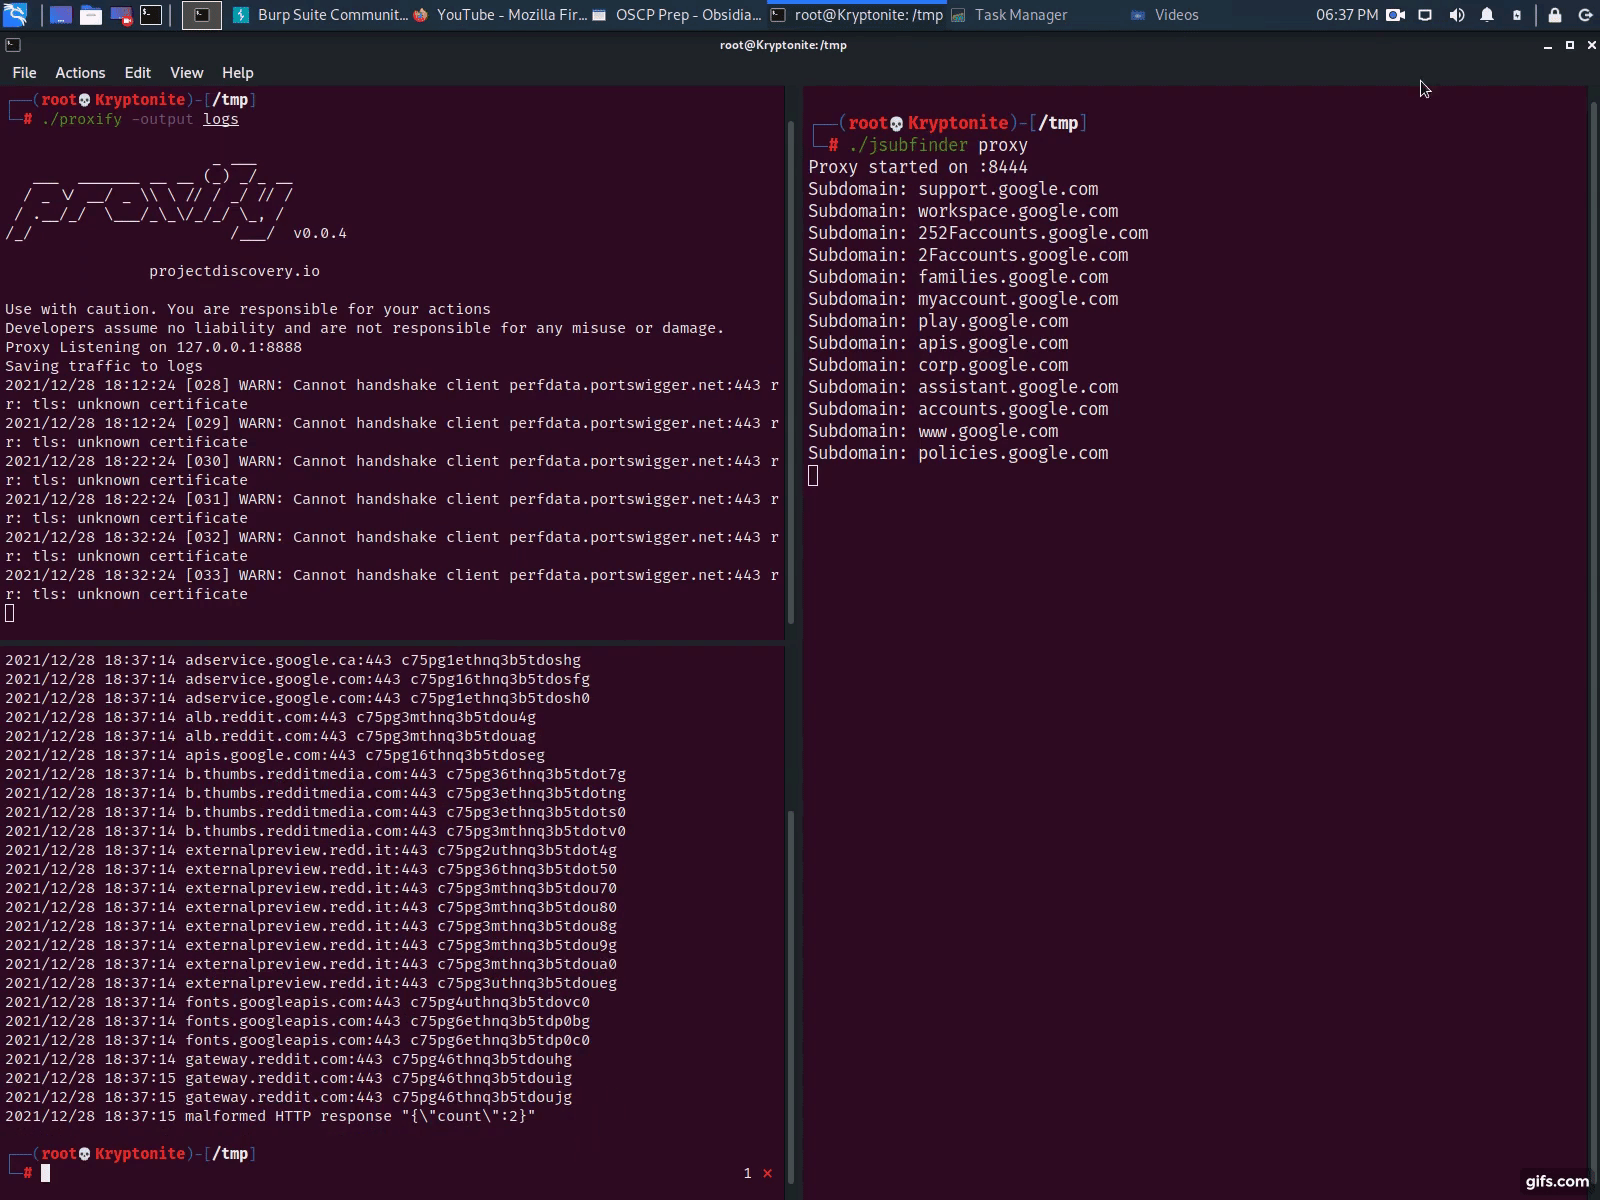 threatunknown/jsubfinder
Go-based tool that scans webpages and JavaScript files to discover hidden subdomains and secrets, with optional crawling and real-time proxy analysis…
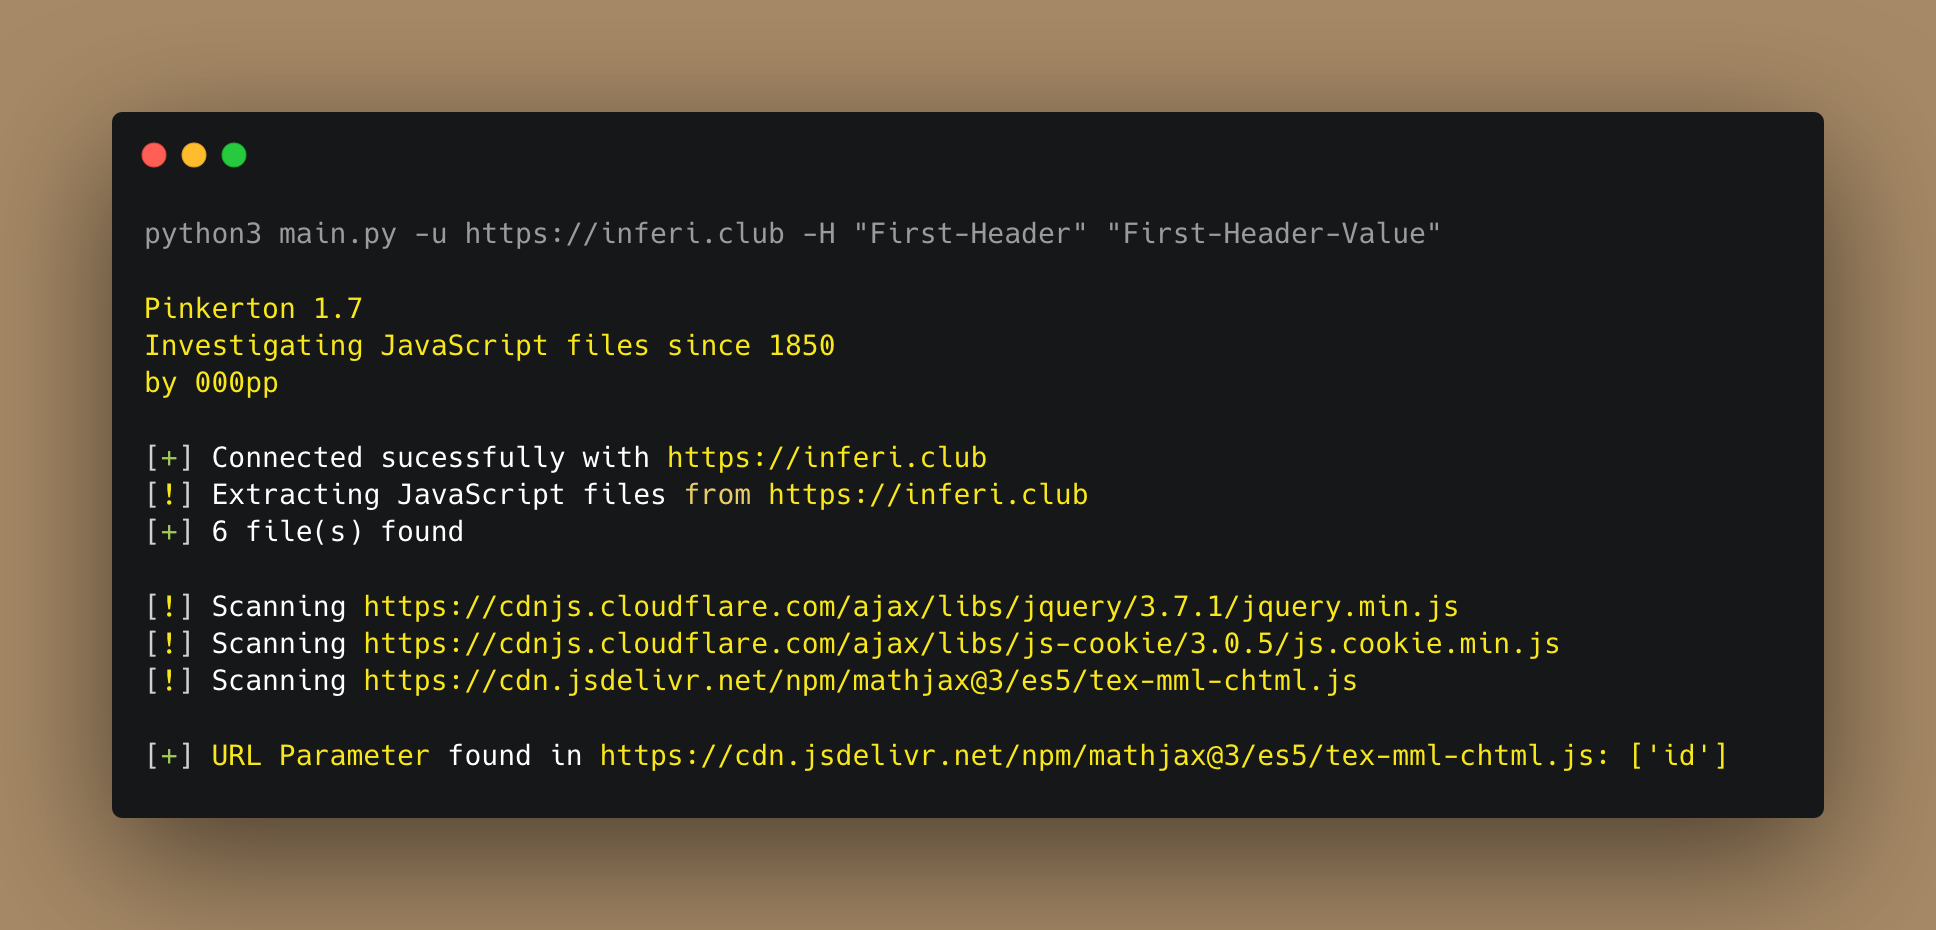 0xdsm/pinkerton
🕵️ Python project to crawl for JavaScript files and search for secrets like API keys, authorization tokens, hardcoded credentials, etc.
 projectdiscovery/depx
Malicious package & supply-chain intelligence
 safedep/gryph
Security layer for AI coding agents. Works with Claude Code, Cursor, Windsurf, Gemini CLI, OpenCode, Pi Agent and more.
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
 node9-ai/node9-proxy
Access control for AI agents. Set what Claude Code, Codex, Gemini, Cursor and any MCP server are allowed to do, review risky actions before they run,…
 shipsecai/studio
Workflow automation for Security Teams
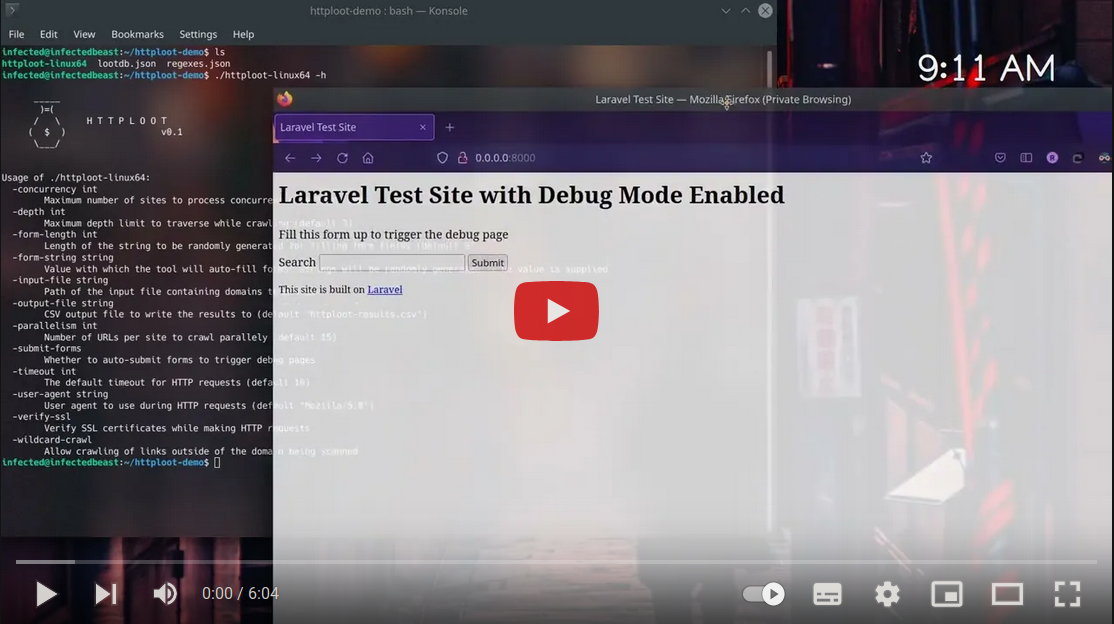 redhuntlabs/httploot
An automated tool which can simultaneously crawl, fill forms, trigger error/debug pages and "loot" secrets out of the client-facing code of sites.
 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 arnica/depsguard
Harden your package manager configs against supply chain attacks.








