
 #1
API key scanning, credential leak detection, and secret management tools.
Kitploit recommended

 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
 rootsecdev/microburstsecretshunter
Scans exported Azure domain dumps for plaintext passwords, connection strings, storage keys, and other secrets; generates redacted CSV/HTML reports…
 jenish-sojitra/jsanalyzer
Burp Suite extension for JavaScript static analysis: extracts API endpoints, URLs, secrets, and emails with noise filtering for web security testing.
 coffinxp/gemini-api-key-hunter
Scans websites and JS files for exposed Gemini API keys, verifies them live, enumerates accessible services, and provides a browser client for direct…
 hackspeak/cve-2026-66066
CVE-2026-66066 (KindaRails2Shell) PoC - Rails Active Storage/libvips arbitrary file read to RCE; for authorized security testing
 pantheon-security/medusa
AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…
 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 gal-nagli/shockwave-oss
Curated collection of bug bounty tips, one-liners, and automation workflows for recon, fuzzing, and web exploitation, with private nuclei templates…
 mohamed--abdel-maksoud/pisiguard
Browser extension that detects PII and sensitive data in AI chats, masks it with placeholders before sending, and restores originals in replies—all…
 iamlucif3r/aws-key-hunter
[Just for fun] Find exposed AWS keys (VALID KEYS ONLY) on github
 randomrobbiebf/static-file-checker
Checks Djangos /static/staticfiles.json for exposed creds using nuclei
 randomrobbiebf/super-secret-finder
Burp Plugin for Secret Matching
 nccgroup/secretscrub
Processes SARIF output from static analysis tools to detect and redact hard-coded secrets in source code, creating a clean copy without the original…
 cappricio-securities/appspec-yaml-leaks
Appspec YML and YAML leaks
 cappricio-securities/behat-config-leaks
BeHat Configuration file leaking
 bishopfox/jsluice
Extract URLs, paths, secrets, and other interesting bits from JavaScript
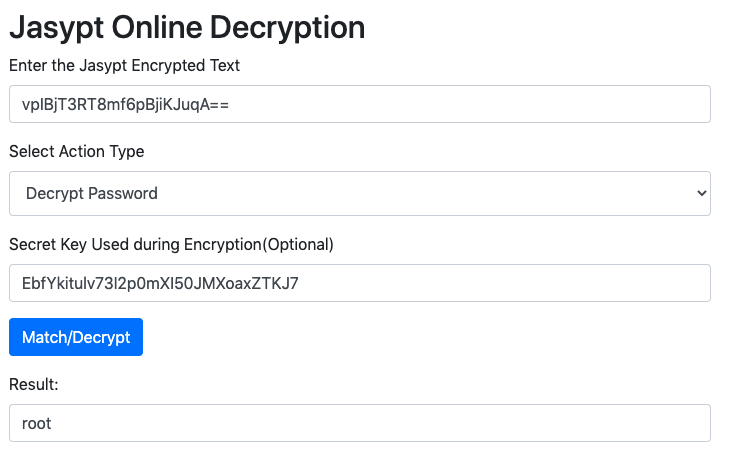 jas502n/database-spring-enc
sprint encode (plan text) get enc password








