
 #1
Tools for decompiling, disassembling, and understanding malware internals and complex binaries.
Kitploit recommended
 humoud/hooketh
A set of scripts that ease working with frida
 ugvxb/cve-2026-9490
The ACCSvc service creates a Named Pipe with a weak Security Descriptor that allows any authenticated user to connect and send messages. When a…
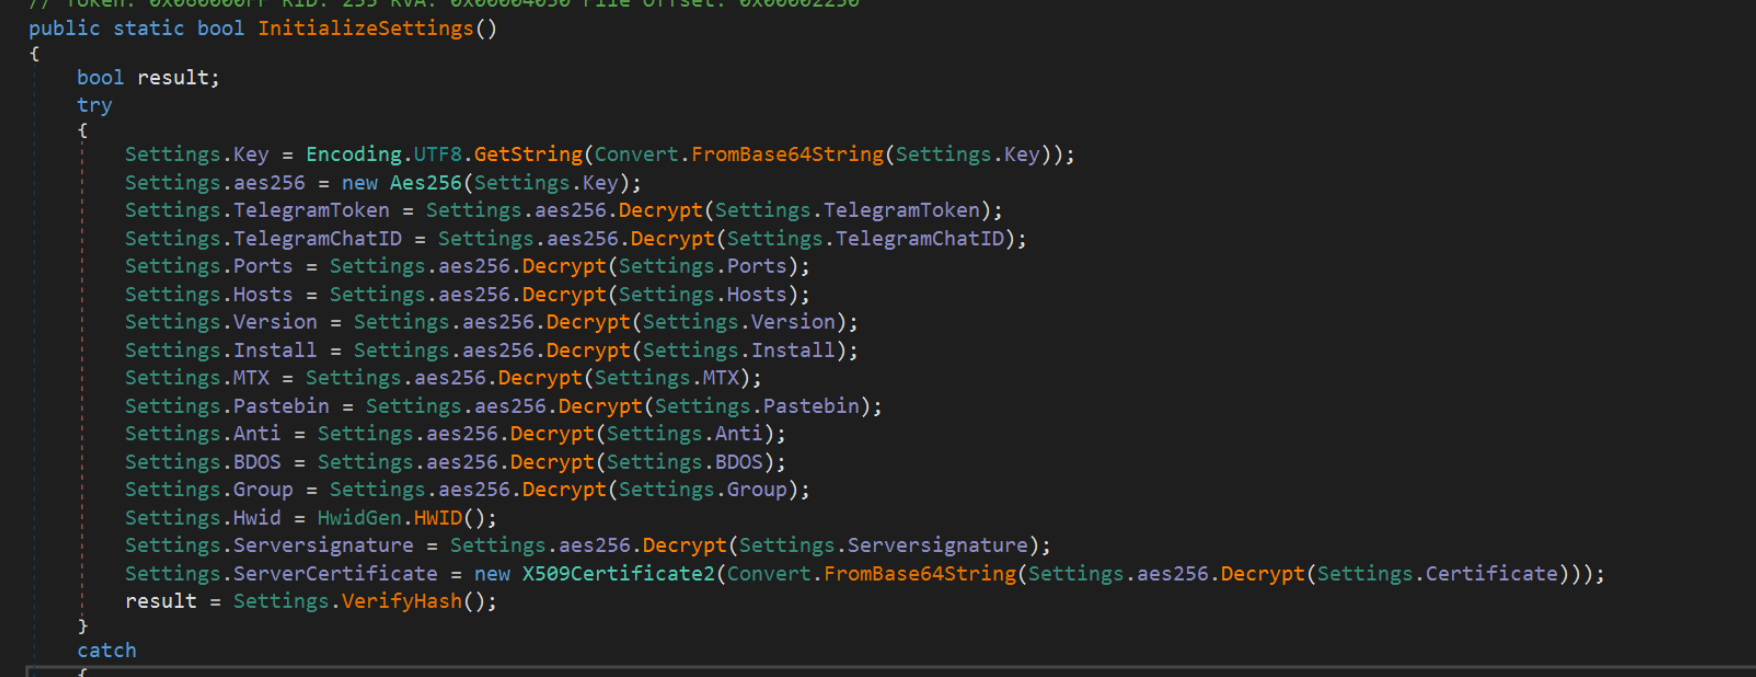 embee-research/asyncrat-venom-dcrat-config-extractor
Config Extractor for Asyncrat/Dcrat/VenomRat
 harbingerse7en/cve-2024-20154
Technical writeup analyzing CVE-2024-20154, a stack-based buffer overflow in MediaTek MT6769 NB-IoT baseband firmware, covering reverse engineering…
 sita-technologies/cve-2025-39247
HikCentral Professional - Pre-Auth License ActiveCode Leak
 ugvxb/cve-2026-9789
A critical local privilege escalation vulnerability has been discovered in Acer NitroSense software (PSAdminAgent.exe). The vulnerability allows any…
 dinosn/cve-2019-13132-lab
CVE-2019-13132 — libzmq CURVE INITIATE stack overflow → RCE. Working exploit + Docker lab.
 gartonchan/redis-cve-2025-62507
Exploit scripts for CVE-2025-62507, a stack buffer overflow in Redis 8.2.0. Provides x86-64 and ARM64 ROP chain exploits with shellcode generation…
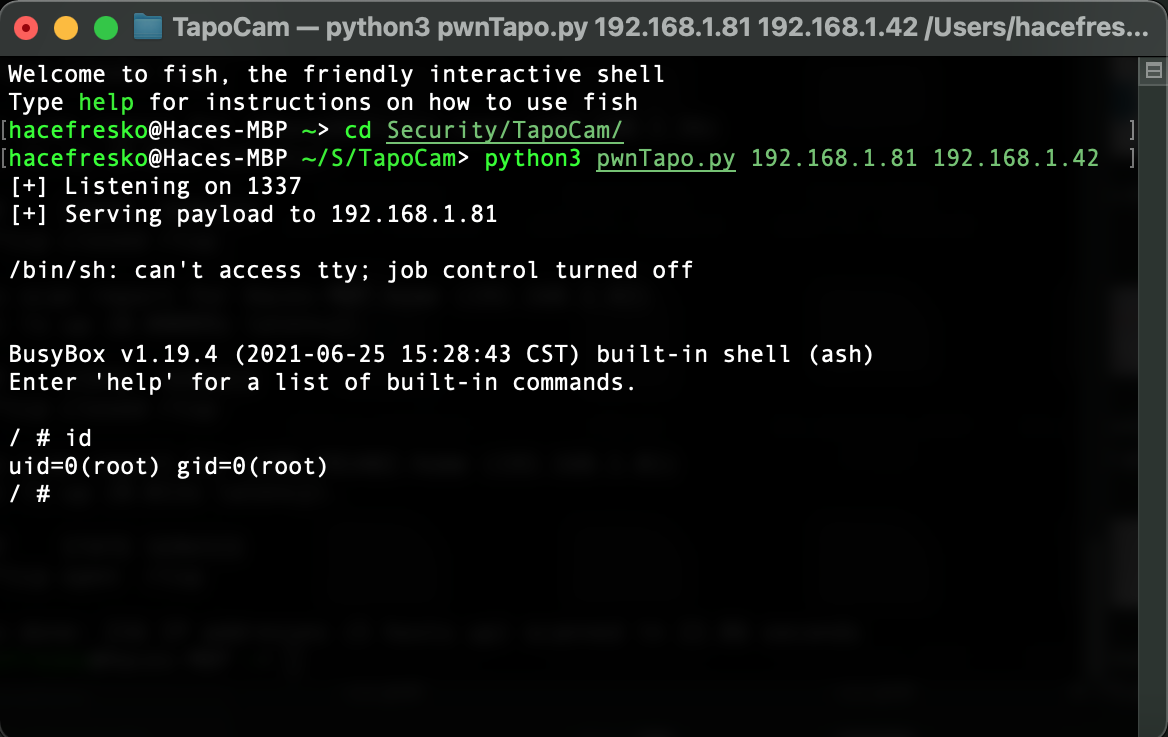 kaleth4/cve-2021-4045
Command injection exploit for TP-Link Tapo C200 camera (CVE-2021-4045) providing root shell access via UART and reverse-engineered uhttpd binary…
 fkshield/cve-2025-5548
End-to-end exploitation lab for CVE-2025-5548 (FreeFloat FTP Server stack buffer overflow). Includes static analysis with IDA/Ghidra, binary fuzzing,…
 gmh5225/ida-sdk
Official IDA Pro SDK headers and libraries for building plugins that disassemble, decompile, and analyze binaries within the IDA reverse engineering…
 idanshechter/cve-2017-13208-scanner
Python script using r2pipe to detect CVE-2017-13208 in Android libnetutils.so by checking for missing dhcp_size validation via static binary analysis.
 flamelu/cve-2020-17035-patch-analysis
Analysis of the patch for CVE-2020-17035, detailing the vulnerability and exploitation mechanism in the affected binary component.
 acloudinthebluesky/cve-2019-6447-es-file-explorer
Technical analysis and safety-conscious research harness for CVE-2019-6447 in ES File Explorer for Android
 kaleth4/cve-2025-60751
Technical analysis and professional exploit for CVE-2025-60751, a stack-based buffer overflow in GeographicLib. Includes a pwntools-based Ret2Libc…
 gmh5225/lithium-kernel
Windows kernel-mode driver with user-mode client exposing IOCTL-based physical and virtual memory read/write, page table walking, pattern scanning,…
 pealeap/cve-2026-21018
Minimal PoC for a Samsung SveService buffer overflow, demonstrating an out-of-bounds write via Binder to crash the Android system service without…








