
 #3
RAT analysis, detection signatures, behavioral analysis, and research frameworks.
Kitploit recommended

 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 kamalx06/tornadoc2
Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
jm33-m0/emp3r0rSelf‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.
 sshuttle/sshuttle
Transparent proxy server that works as a poor man's VPN. Forwards over ssh. Doesn't require admin. Works with Linux and MacOS. Supports DNS…
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 abraxas/pfsense-sshguard-crlf
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - RCE - sshguard THRESHOLD CRLF
 ne0nd0g/merlin
Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.
 horizon3ai/ahsaycbs-auth-bypass-rce
A proof of concept exploit for CVE-2026-105133 and CVE-2026-105134 affecting AhsayCBS
 bishopfox/sliver
Adversary Emulation Framework
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 its-a-feature/mythic
A collaborative, multi-platform, red teaming framework
 jpillora/chisel
Fast TCP/UDP tunnel over HTTP with SSH encryption, supporting reverse port forwarding, SOCKS5 proxy, and client authentication for secure network…
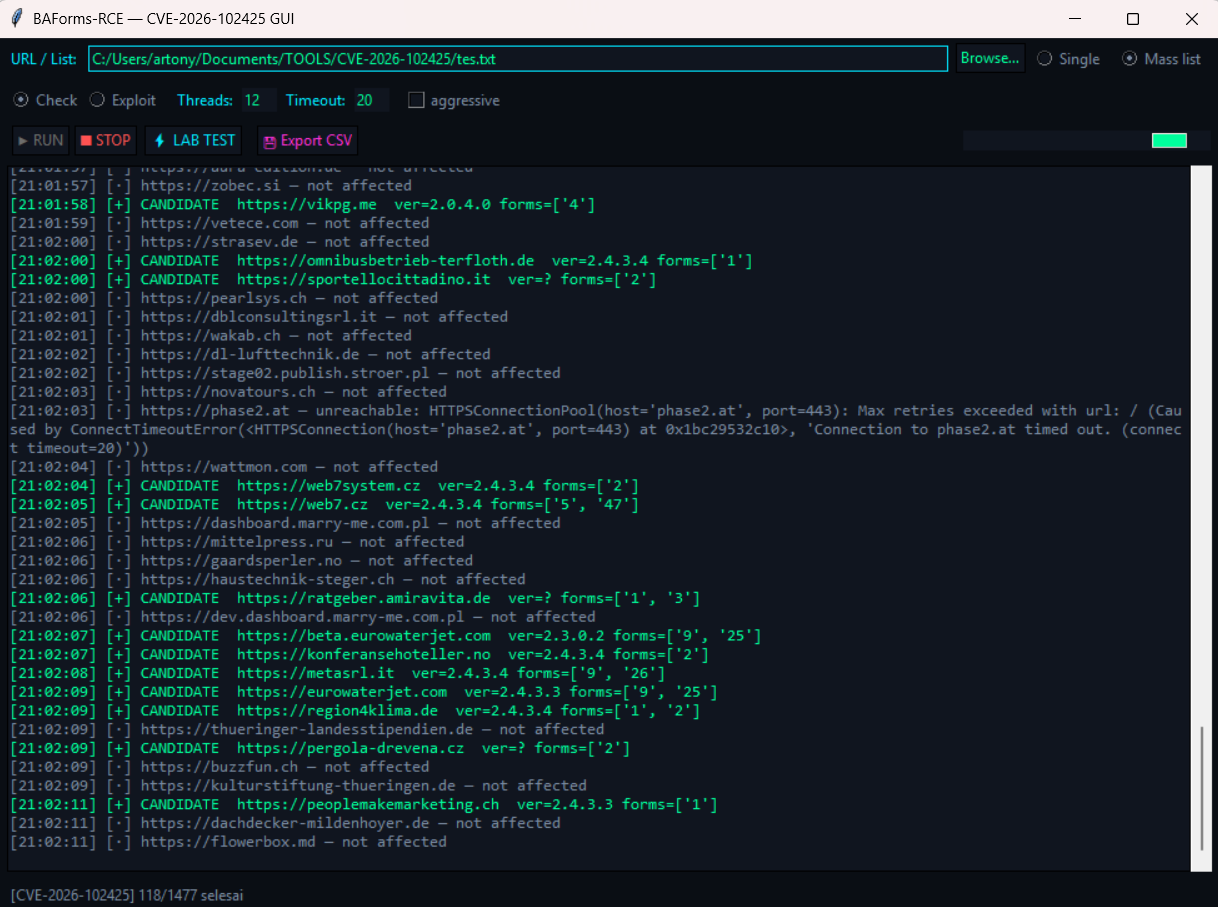 tonydelouvre/cve-2026-102425
GUI scanner and exploit for CVE-2026-102425, an unauthenticated RCE in Balbooa Forms (com_baforms) via PHP shortcode injection, with mass scanning…
 g13net/lockjaw
Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
 cyberuser-hash/cve-2026-44011-craft-rce-poc
Python proof-of-concept for CVE-2026-44011 in Craft CMS, exploiting authenticated remote code execution with command execution and base64-wrapped…



