
 #1
Adversary simulation, red team infrastructure, C2 frameworks, and operational security tools.
Kitploit recommended
 p0dalirius/mssql-analysis-coerce
A technique to coerce a Windows SQL Server to authenticate on an arbitrary machine.
 bytecode77/slui-file-handler-hijack-privilege-escalation
Slui File Handler Hijack UAC Bypass Local Privilege Escalation
 cr4ckc4t/cve-2022-41352-zimbra-rce
Zimbra <9.0.0.p27 RCE
 mirchr/security-research
Security Research
 vnhacker1337/cve-2022-27925-poc
Zimbra RCE simple poc
 hyd3sec/azur3alph4
PowerShell module for post-breach Azure red teaming, automating token extraction, resource enumeration, and lateral movement within managed identity…
 1n3/powerexfil
A collection of data exfiltration scripts for Red Team assessments.
 ahhh/reverse_https_bot
A python based https remote access trojan for penetration testing
 thiagopeixoto/winsos-poc
A PoC demonstrating code execution via DLL Side-Loading in WinSxS binaries.
 3nailsinfosec/dcvc2
Discord voice channel C2 framework for covert command and control operations. Transmits all data via RTP packets over voice channels, leaving no…
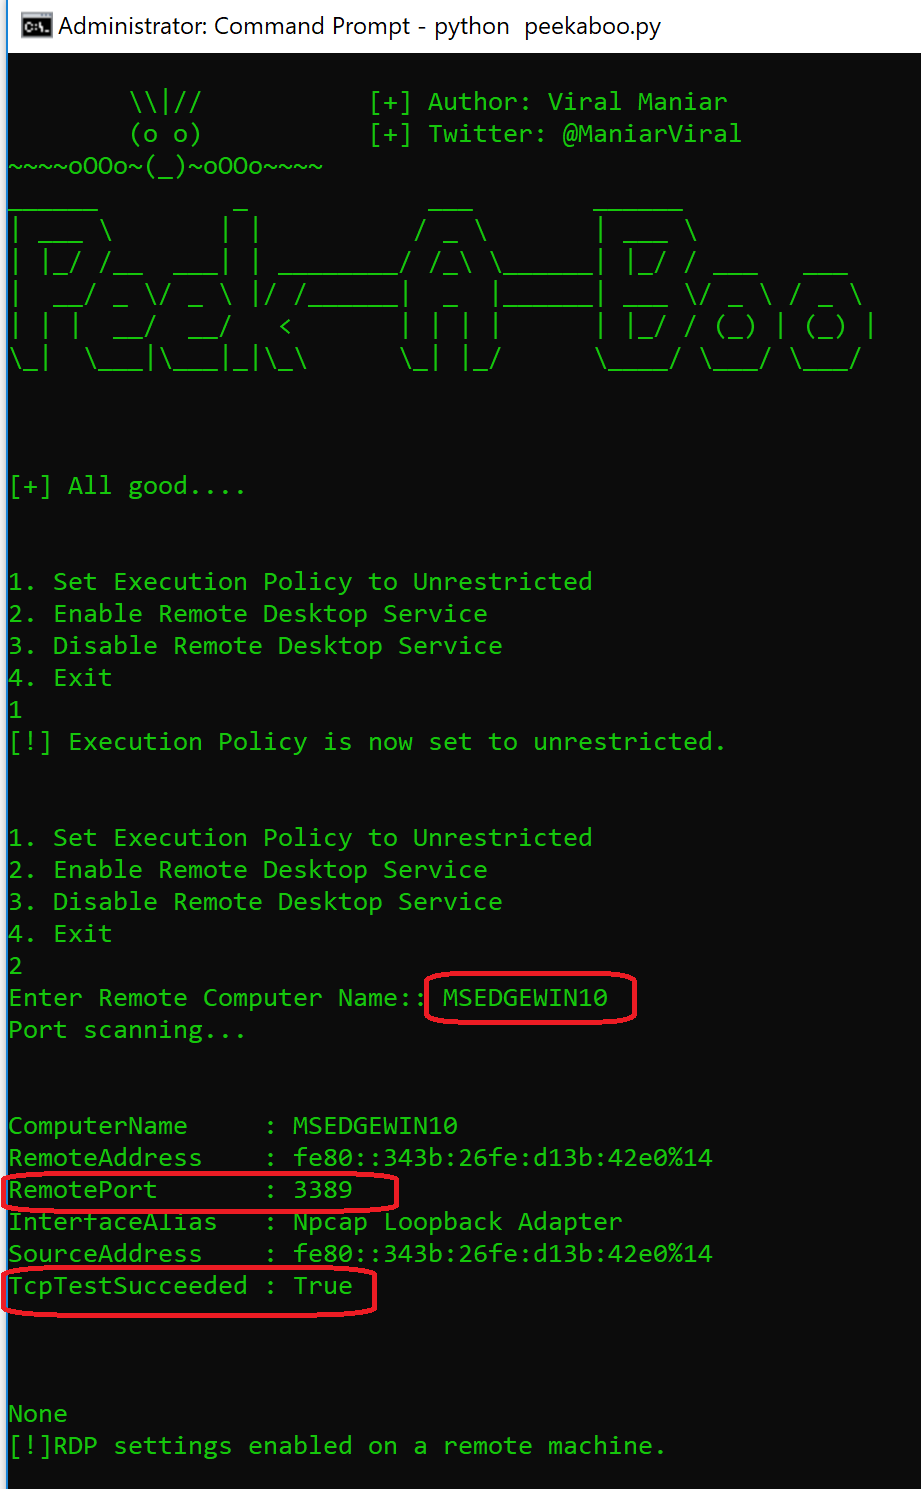 viralmaniar/peekaboo
PeekABoo tool can be used during internal penetration testing when a user needs to enable Remote Desktop on the targeted machine. It uses PowerShell…
 mister-iks/pcybox-attackgraph
Open source browser lab to build a simulated infrastructure, watch an attack move through it, and check whether your defense works.
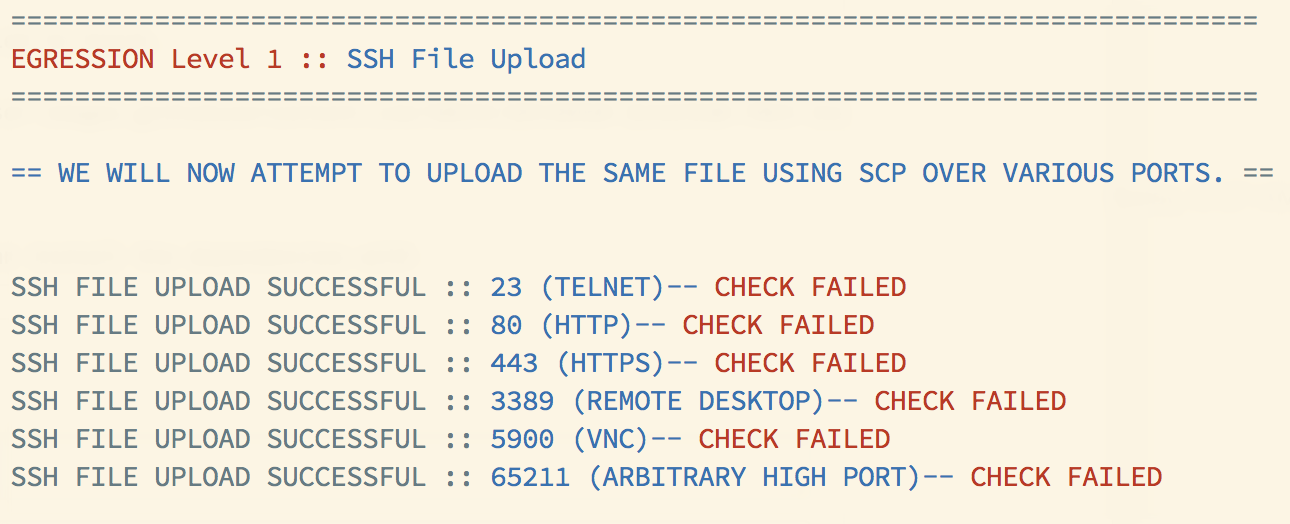 danielmiessler/egression
Test a network's egress controls with various levels of success and failure.
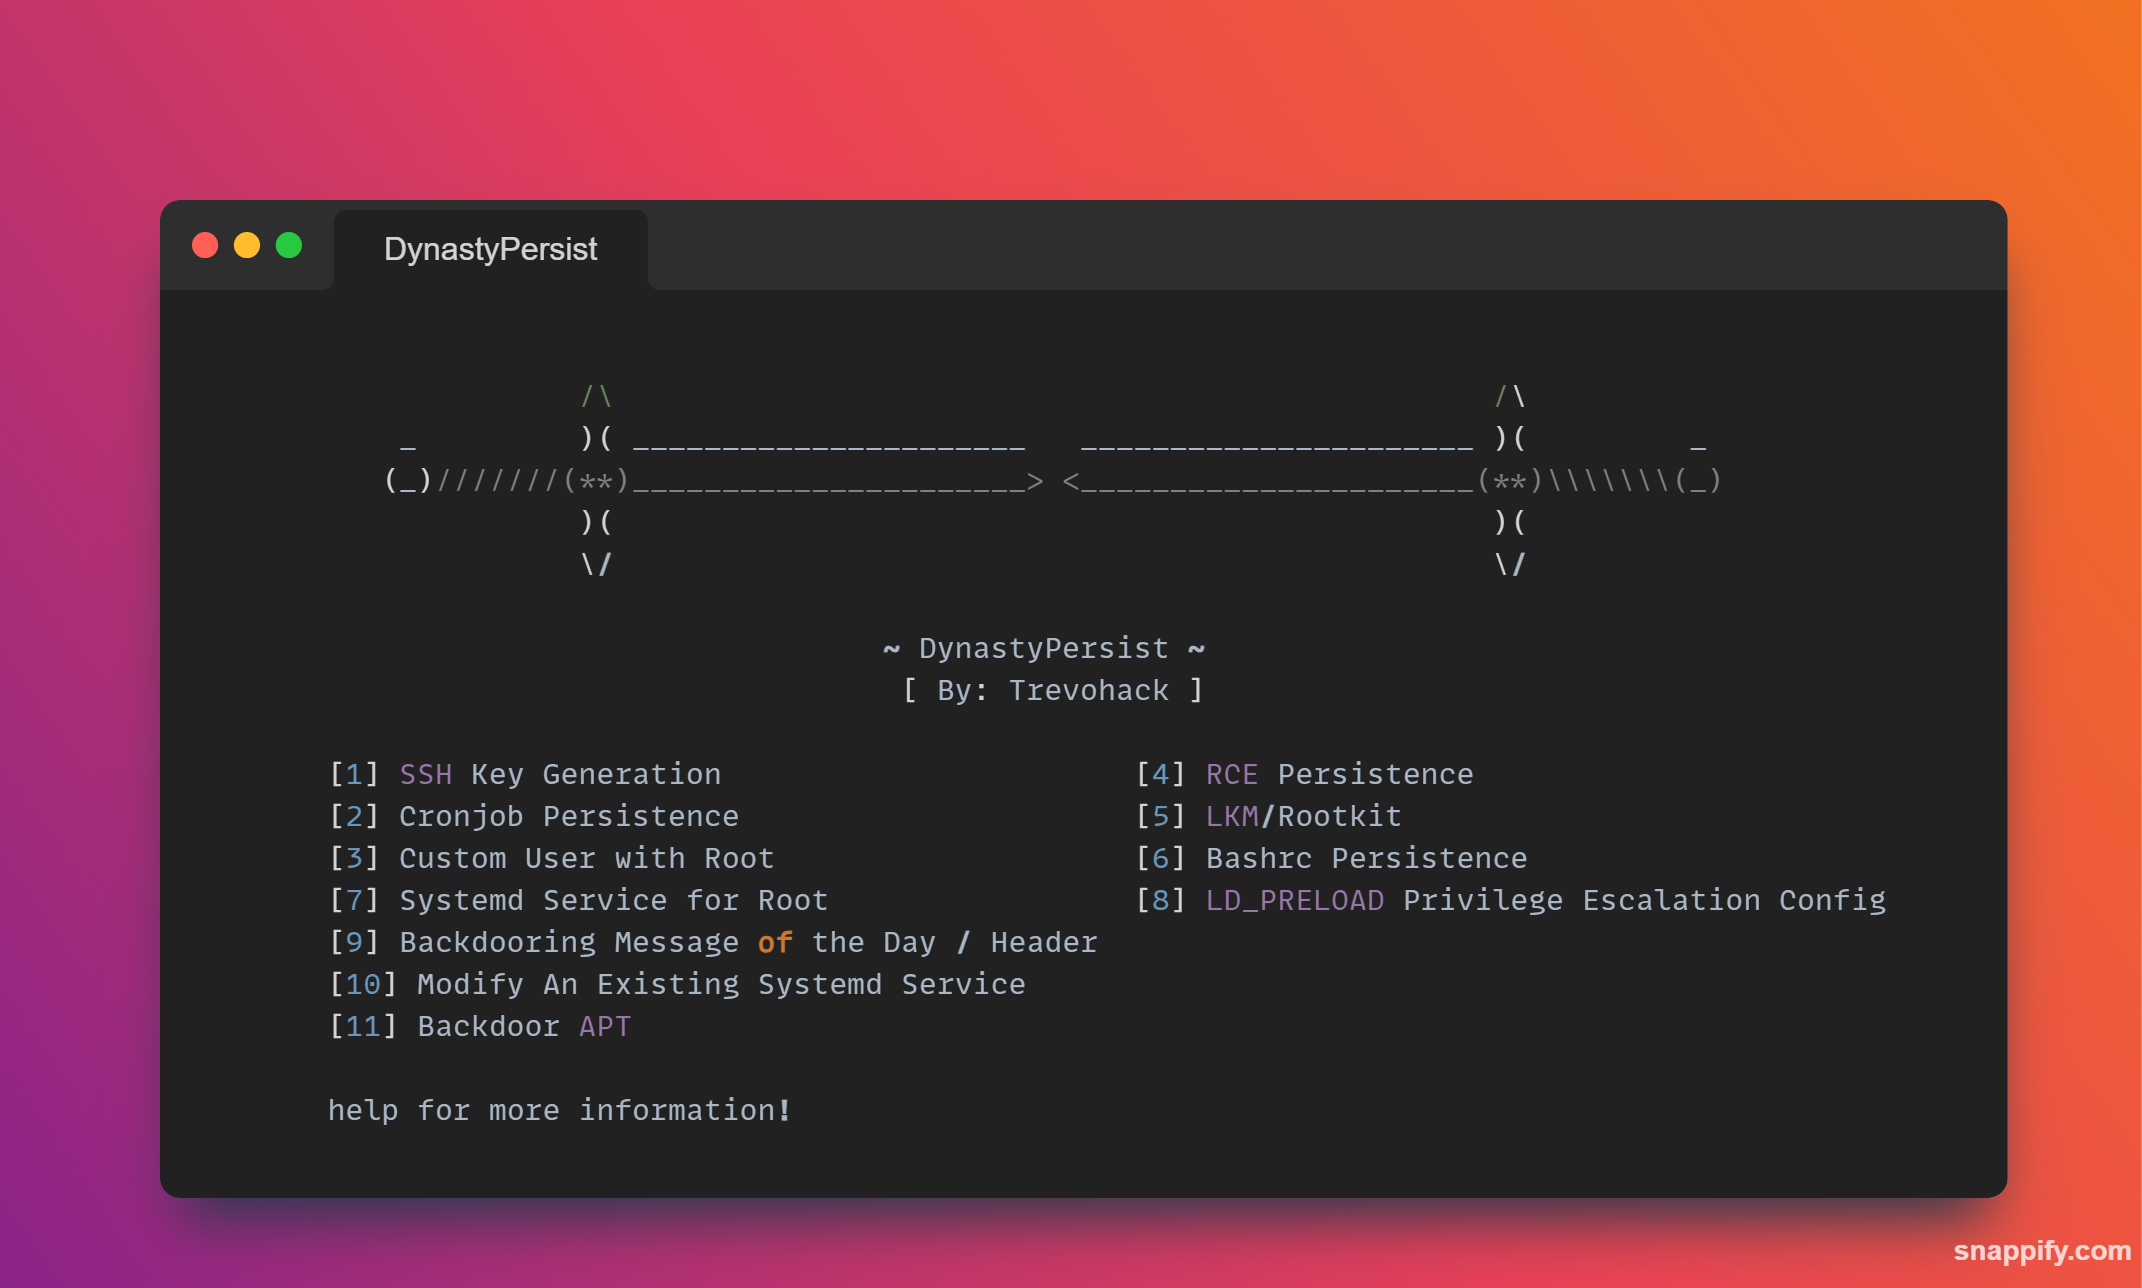 trevohack/dynastypersist
Linux persistence toolkit with 11 modules for SSH key backdoors, cronjobs, systemd services, LKM rootkits, and LD_PRELOAD privilege escalation.…
 secforce/sharpwhispers
C# porting of SysWhispers2. It uses SharpASM to find the code caves for executing the system call stub.
 tam-k592/cve-2024-53677-s2-067
A critical vulnerability, CVE-2024-53677, has been identified in the popular Apache Struts framework, potentially allowing attackers to execute…
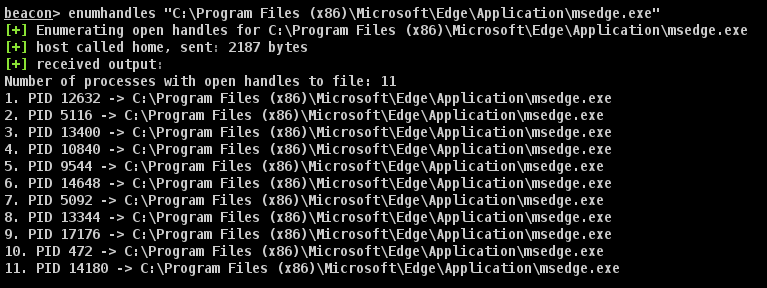 octoberfest7/enumhandles_bof
Cobalt Strike BOF for live Windows enumeration of open file handles, revealing which process has locked a target file on disk during…
 zblurx/impersonate-rs
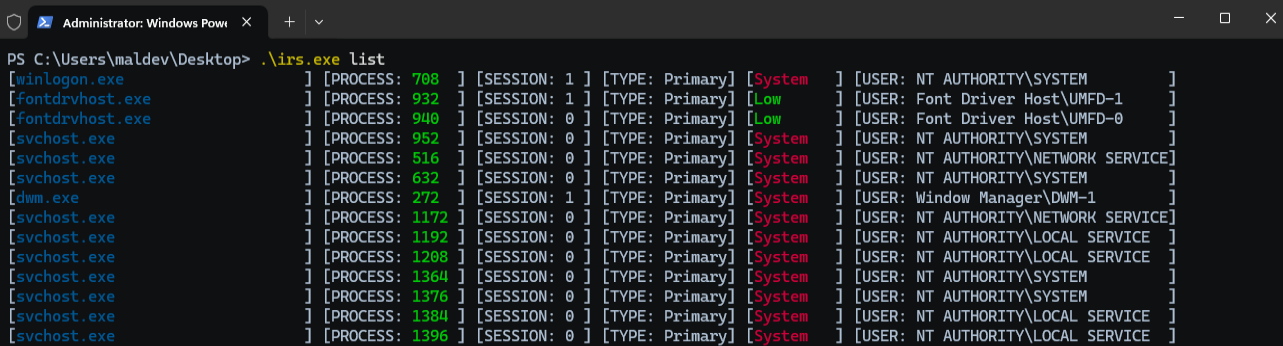
Rusty Impersonate








